
BLEBoy
 nccgroup/bleboy
BLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…
bluetooth-securityeducationembedded-systems-security+3
49
nccgroup/bleboyBLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…
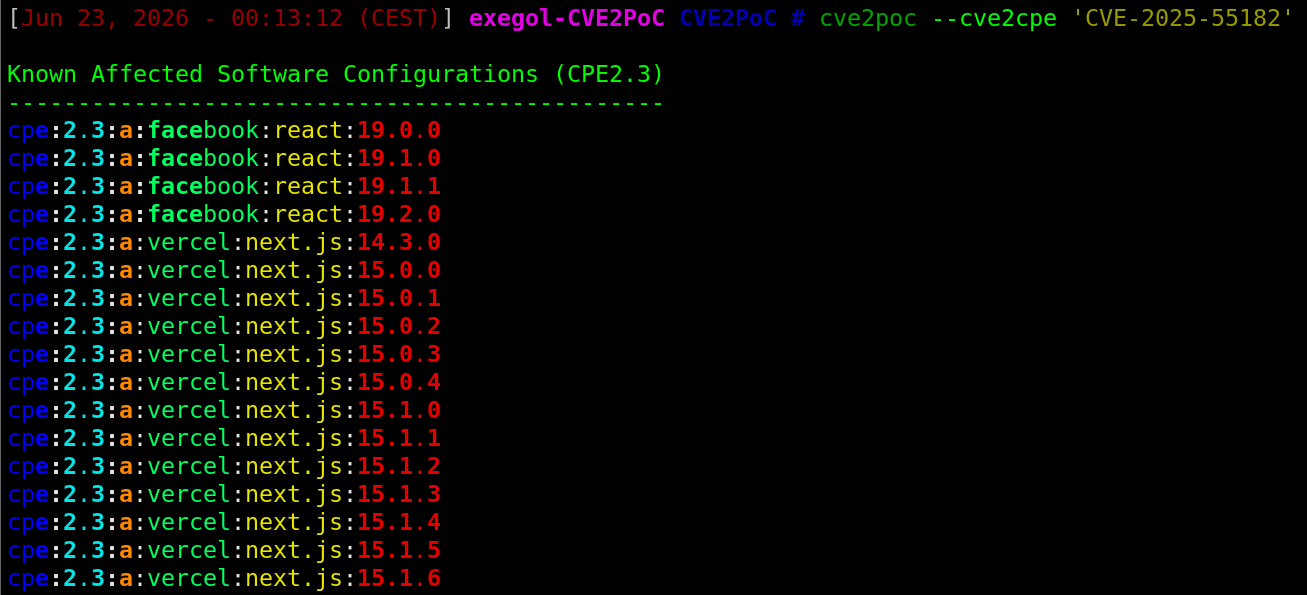 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)
 ricsirigu/cve-2025-29927
A deliberately Next.js app, vulnerable to CVE-2025-29927, Authorization Bypass
 ne0zer01/cve-2024-27198_lab
Docker-based lab for CVE-2024-27198 TeamCity authentication bypass. Includes exploit reproduction, IoC hunting with Sigma/Suricata rules, and…
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 hexsecteam/cve-2025-8088-winrar-tool
A sophisticated GUI tool for creating malicious RAR archives that exploit the WinRAR path traversal vulnerability (CVE-2025-8088) using ADS and RAR5…
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 badsectorlabs/ludus_xz_backdoor
An Ansible Role that installs the xz backdoor (CVE-2024-3094) on a Debian host and optionally installs the xzbot tool.
 antogit-sys/cve-2007-5962
vsftpd 2.0.5 - 'CWD' (Authenticated) Remote Memory Consumption
 ethicalpap/cve-2025-29775
Educational lab environment demonstrating SAMLStorm (CVE-2025-29775) vulnerability in xml-crypto library. Includes vulnerable SAML service provider,…
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
 sydsec1/syd
Air-gapped cybersecurity assistant for security professionals. 100% offline AI-powered analysis tool for Nmap, Volatility, BloodHound, Metasploit,…
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 0xnxt1me/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 that adds x-middleware-subrequest to bypass Next.js middleware authentication checks.
 splunk/attack_range
A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
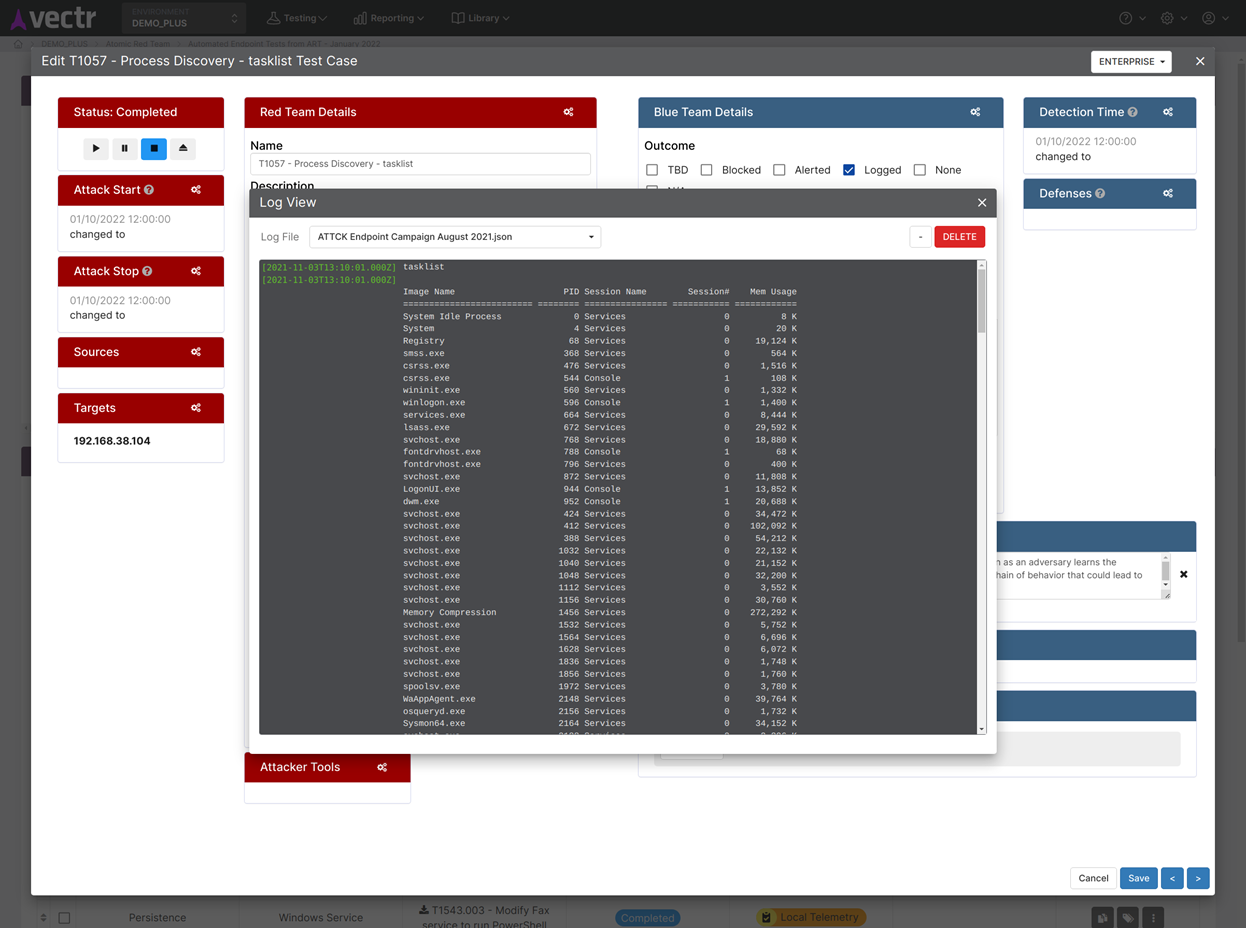 securityriskadvisors/vectr
Track red and blue team testing activities to measure detection and prevention capabilities across attack scenarios, with campaign management, TTP…