Gitea-template-sync-Path-Traversal-Privilege-Escalation-CVE-2026-38526-

PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…

PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…

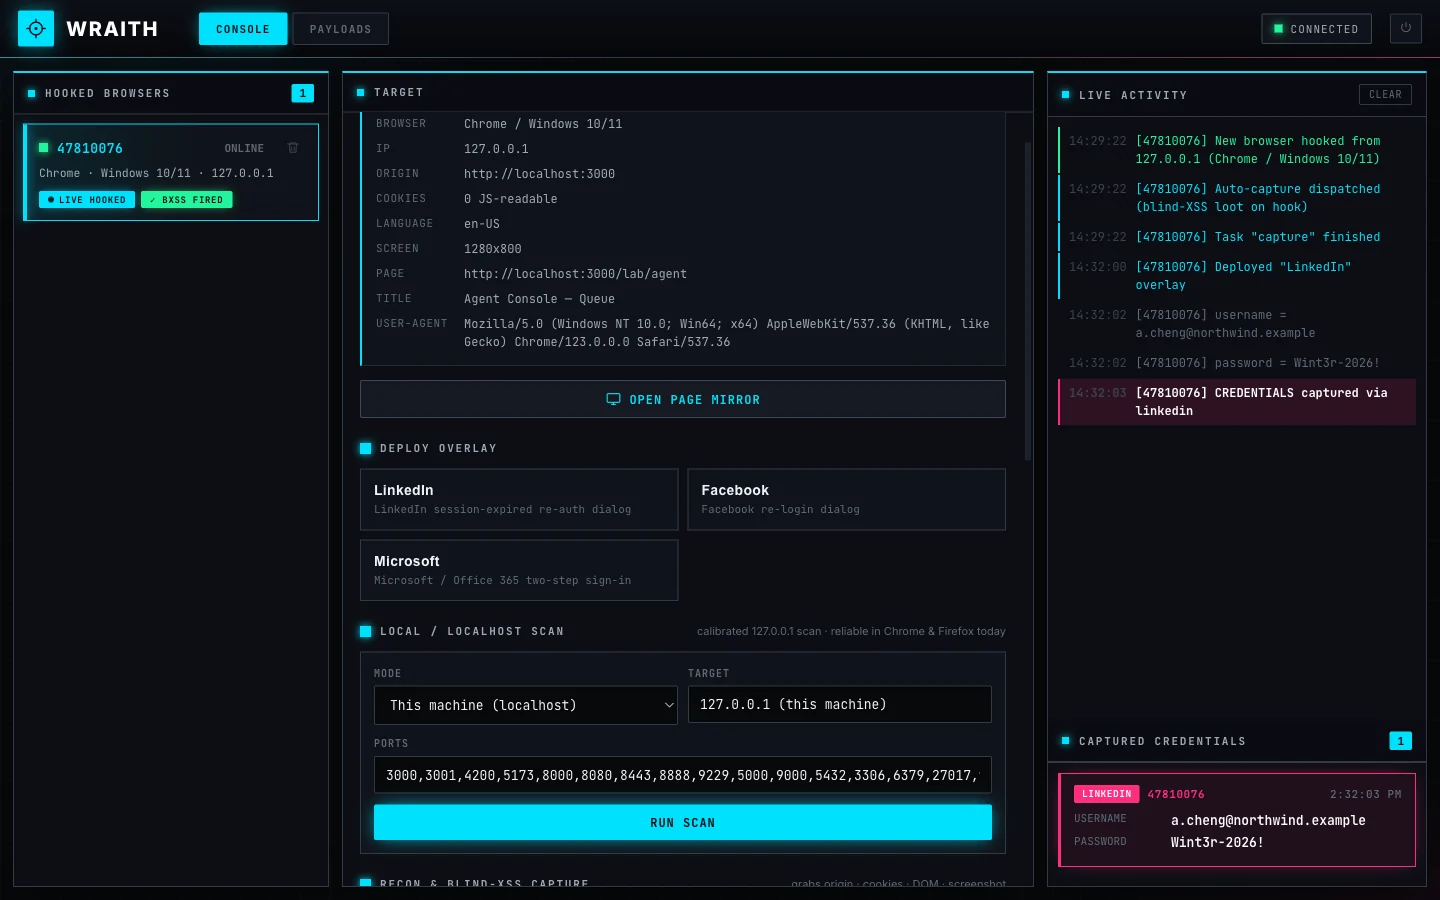
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…

This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).

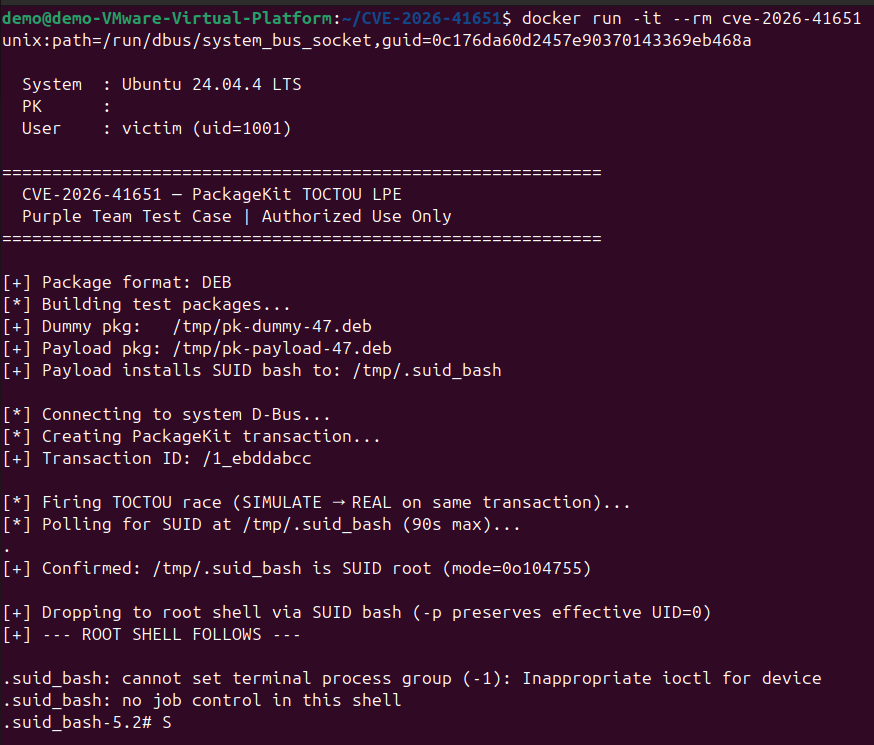
Proof-of-concept exploit for CVE-2026-41651, a PackageKit TOCTOU local privilege escalation, with technical analysis, detection logic, and…

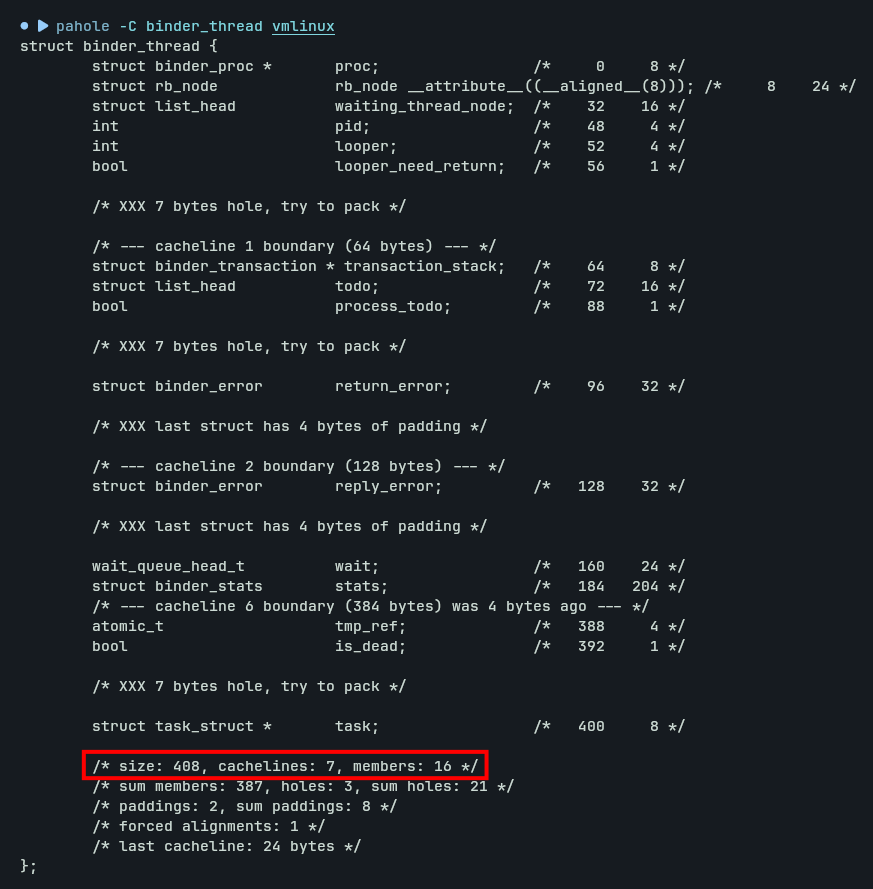
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.

An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.

Proof of concept with GDB‑assisted exploitation (educational / lab use only)

An intentionally-vulnerable GWT-based web application to test tooling and techniques

Curated collection of CVE demonstrations with fix recommendations for hands-on vulnerability analysis and educational exploitation practice.

Aritifacts of docker env of CVE-2021-3975

Trail of Bits Testing Handbook - appsec.guide

This repository contains a number of insecure self-hosted applications that allows interested security engineers to test vulnerabilities found by…

Vulnerable environments paired with ready-to-use Nuclei templates for security testing and learning! 🚀

This is a container of web applications that work with OWASP Bug Bounty for Projects

Helper scripts to remaster Linux Live CD images for the purpose of creating ready to use security wargames with pre-installed vulnerabilities to…

Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…

a python3 version of the exploit written for CVE-2014-6287. Useful for completing the "Steel Mountain" room on TryHackMe.com without the use of…