

BLT
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
curated-resourcesdevsecopseducation+7
11 day ago
owasp/bltMonorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
 abraxas/cve-2026-75650
Disclosure pack and lab reproduction script for CVE-2026-75650, an unauthenticated SSTI RCE in Magento Open Source GraphQL email templates.
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
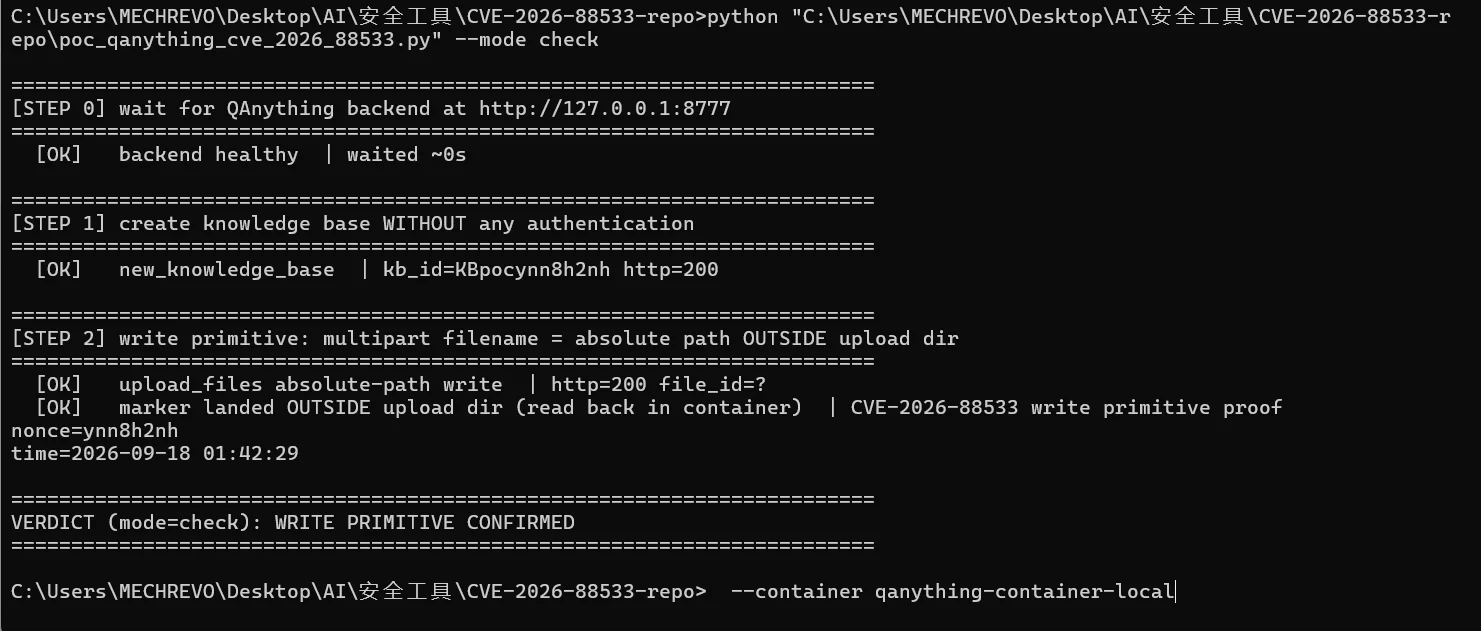 hemlock-lyk/cve-2026-88533
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…
 dinosn/cve-2026-75650-magento-validation-lab
Docker lab reproducing the complete CVE-2026-75650 StyleSmuggler unauthenticated HTTP RCE and validating Adobe VULN-39341.
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
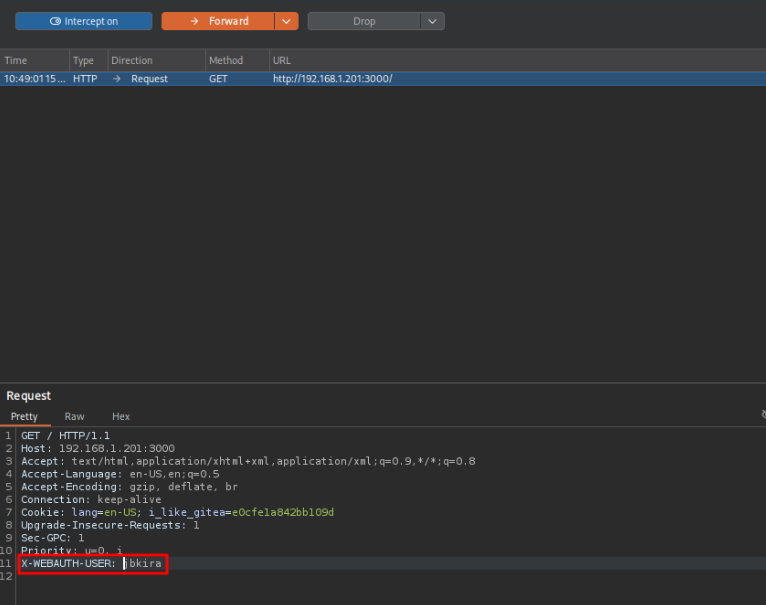 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 owasp/owasp-open-source-intelligence-standard
An open, vendor-neutral verification standard for traceable, reviewable, and rights-aware open-source intelligence. Current release: OOVS v0.1.0.
 rauljvc8/cve-2025-68616-detecting-and-patching-an-ssrf-in-weasyprint-with-wazuh
Hands-on vulnerability management case study: how Wazuh flagged a real SSRF (CVE-2025-68616) in WeasyPrint, and how I reproduced and patched it.
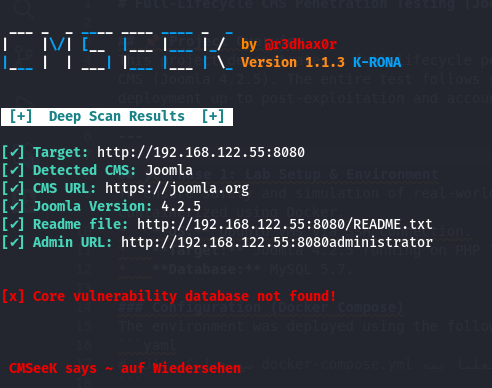 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 guigui237/exploitation-de-la-vuln-rabilit-cve-2015-5254-
Step-by-step exploitation guide for Apache ActiveMQ CVE-2015-5254 deserialization vulnerability using jmet, with Docker-based lab setup and…
 ibadovulfat/cve-2025-24893
A critical remote code execution (RCE) vulnerability (CVE‑2025‑24893) exists in the XWiki Platform, specifically in the SolrSearch RSS feed endpoint.
 corsisechero/cve-2019-9193byvulhub
Docker-based lab demonstrating CVE-2019-9193 PostgreSQL arbitrary command execution via COPY FROM PROGRAM, with step-by-step PoC for security testing…