
CVE-2026-24061
 tiborscholtz/cve-2026-24061
Educational Docker lab demonstrating Telnet NEW-ENVIRON username injection (CVE-2026-24061) with a Python client and vulnerable server for isolated…
educationexploitationlabs-practice+2
tiborscholtz/cve-2026-24061Educational Docker lab demonstrating Telnet NEW-ENVIRON username injection (CVE-2026-24061) with a Python client and vulnerable server for isolated…
 saku0512/cve-2026-9086-poc
CVE-2026-9086 proof-of-concept for Keycloak client URI validation bypass using mixed-case javascript: and data: XSS payloads, with Docker-based…
 doyensec/csptplayground
CSPTPlayground is an open-source playground to find and exploit Client-Side Path Traversal (CSPT).
 razureink/cve-2024-49113-ldap_nightmare_reproduction
Reproduction of cve-2024-49113-ldap_nightmare_reproduction
 taurusxin/cve-2021-44228
Educational RCE exploit for CVE-2021-44228 (Log4Shell) with RMI server and client demonstrating vulnerability recurrence via calculator popup.
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)
 pratikjojode/vcenter-cve-2021-21980-lab
Realistic vulnerable lab for CVE-2021-21980 (VMware vSphere Path Traversal) - Actual file exploitation, not a mock server
 dilan-diaz/point-to-point-protocol-daemon-rce-vulnerability-cve-2020-8597-
University assignment documenting CVE-2020-8597, a stack buffer overflow in pppd's EAP parser, with a remote code execution exploit demonstration…
 jacobtaylor3/c2-and-post-exploitation-framework
CVE-2021-21220 Exploitation infrastructure
 foudadev/cve-2007-2447
Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…
 gui2000guix-ui/cve-2021-21980-mock-server
CVE-2021-21980
 baldassarrefe/fep3370-advanced-ethical-hacking
DHCP exploitation with DynoRoot (CVE-2018-1111)
 h3raklez/cve-2024-3094
Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…
 gkdgkd123/cve-2026-29145-everything
Reproducible PoC environment for CVE-2026-29145 Apache Tomcat CLIENT_CERT + OCSP soft-fail bypass, including exploit scripts, mock OCSP responder,…
 hophtien/cve-2025-54424
CVE-2025-54424: 1Panel TLS client cert bypass enables RCE via forged CN 'panel_client' using a bundled scanning and exploitation tool. Affected: <=…
 trandonga3/poc-cve-2025-1094
Proof-of-concept exploit for CVE-2025-1094, a PostgreSQL psql SQL injection leading to RCE via libpq escaping bypass. Includes Docker environment,…
 alardiians/pocketbase-cve-2026-44166
Lab + writeup for CVE-2026-44166: PocketBase OAuth2 account pre-hijacking via unvalidated createData.email
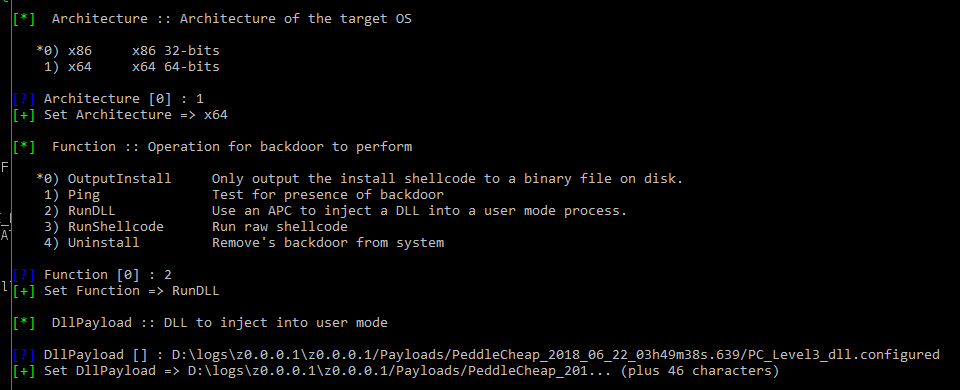 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands