
Resources-for-Application-Security
 security-prince/resources-for-application-security
Some good resources for getting started with application security
ctfcurated-resourcesdynamic-analysis-sandboxing+6
148
security-prince/resources-for-application-securitySome good resources for getting started with application security
 eshard/scared
Python framework for performing side-channel analysis attacks (e.g., CPA) on public datasets, designed for educational use and hands-on practice in…
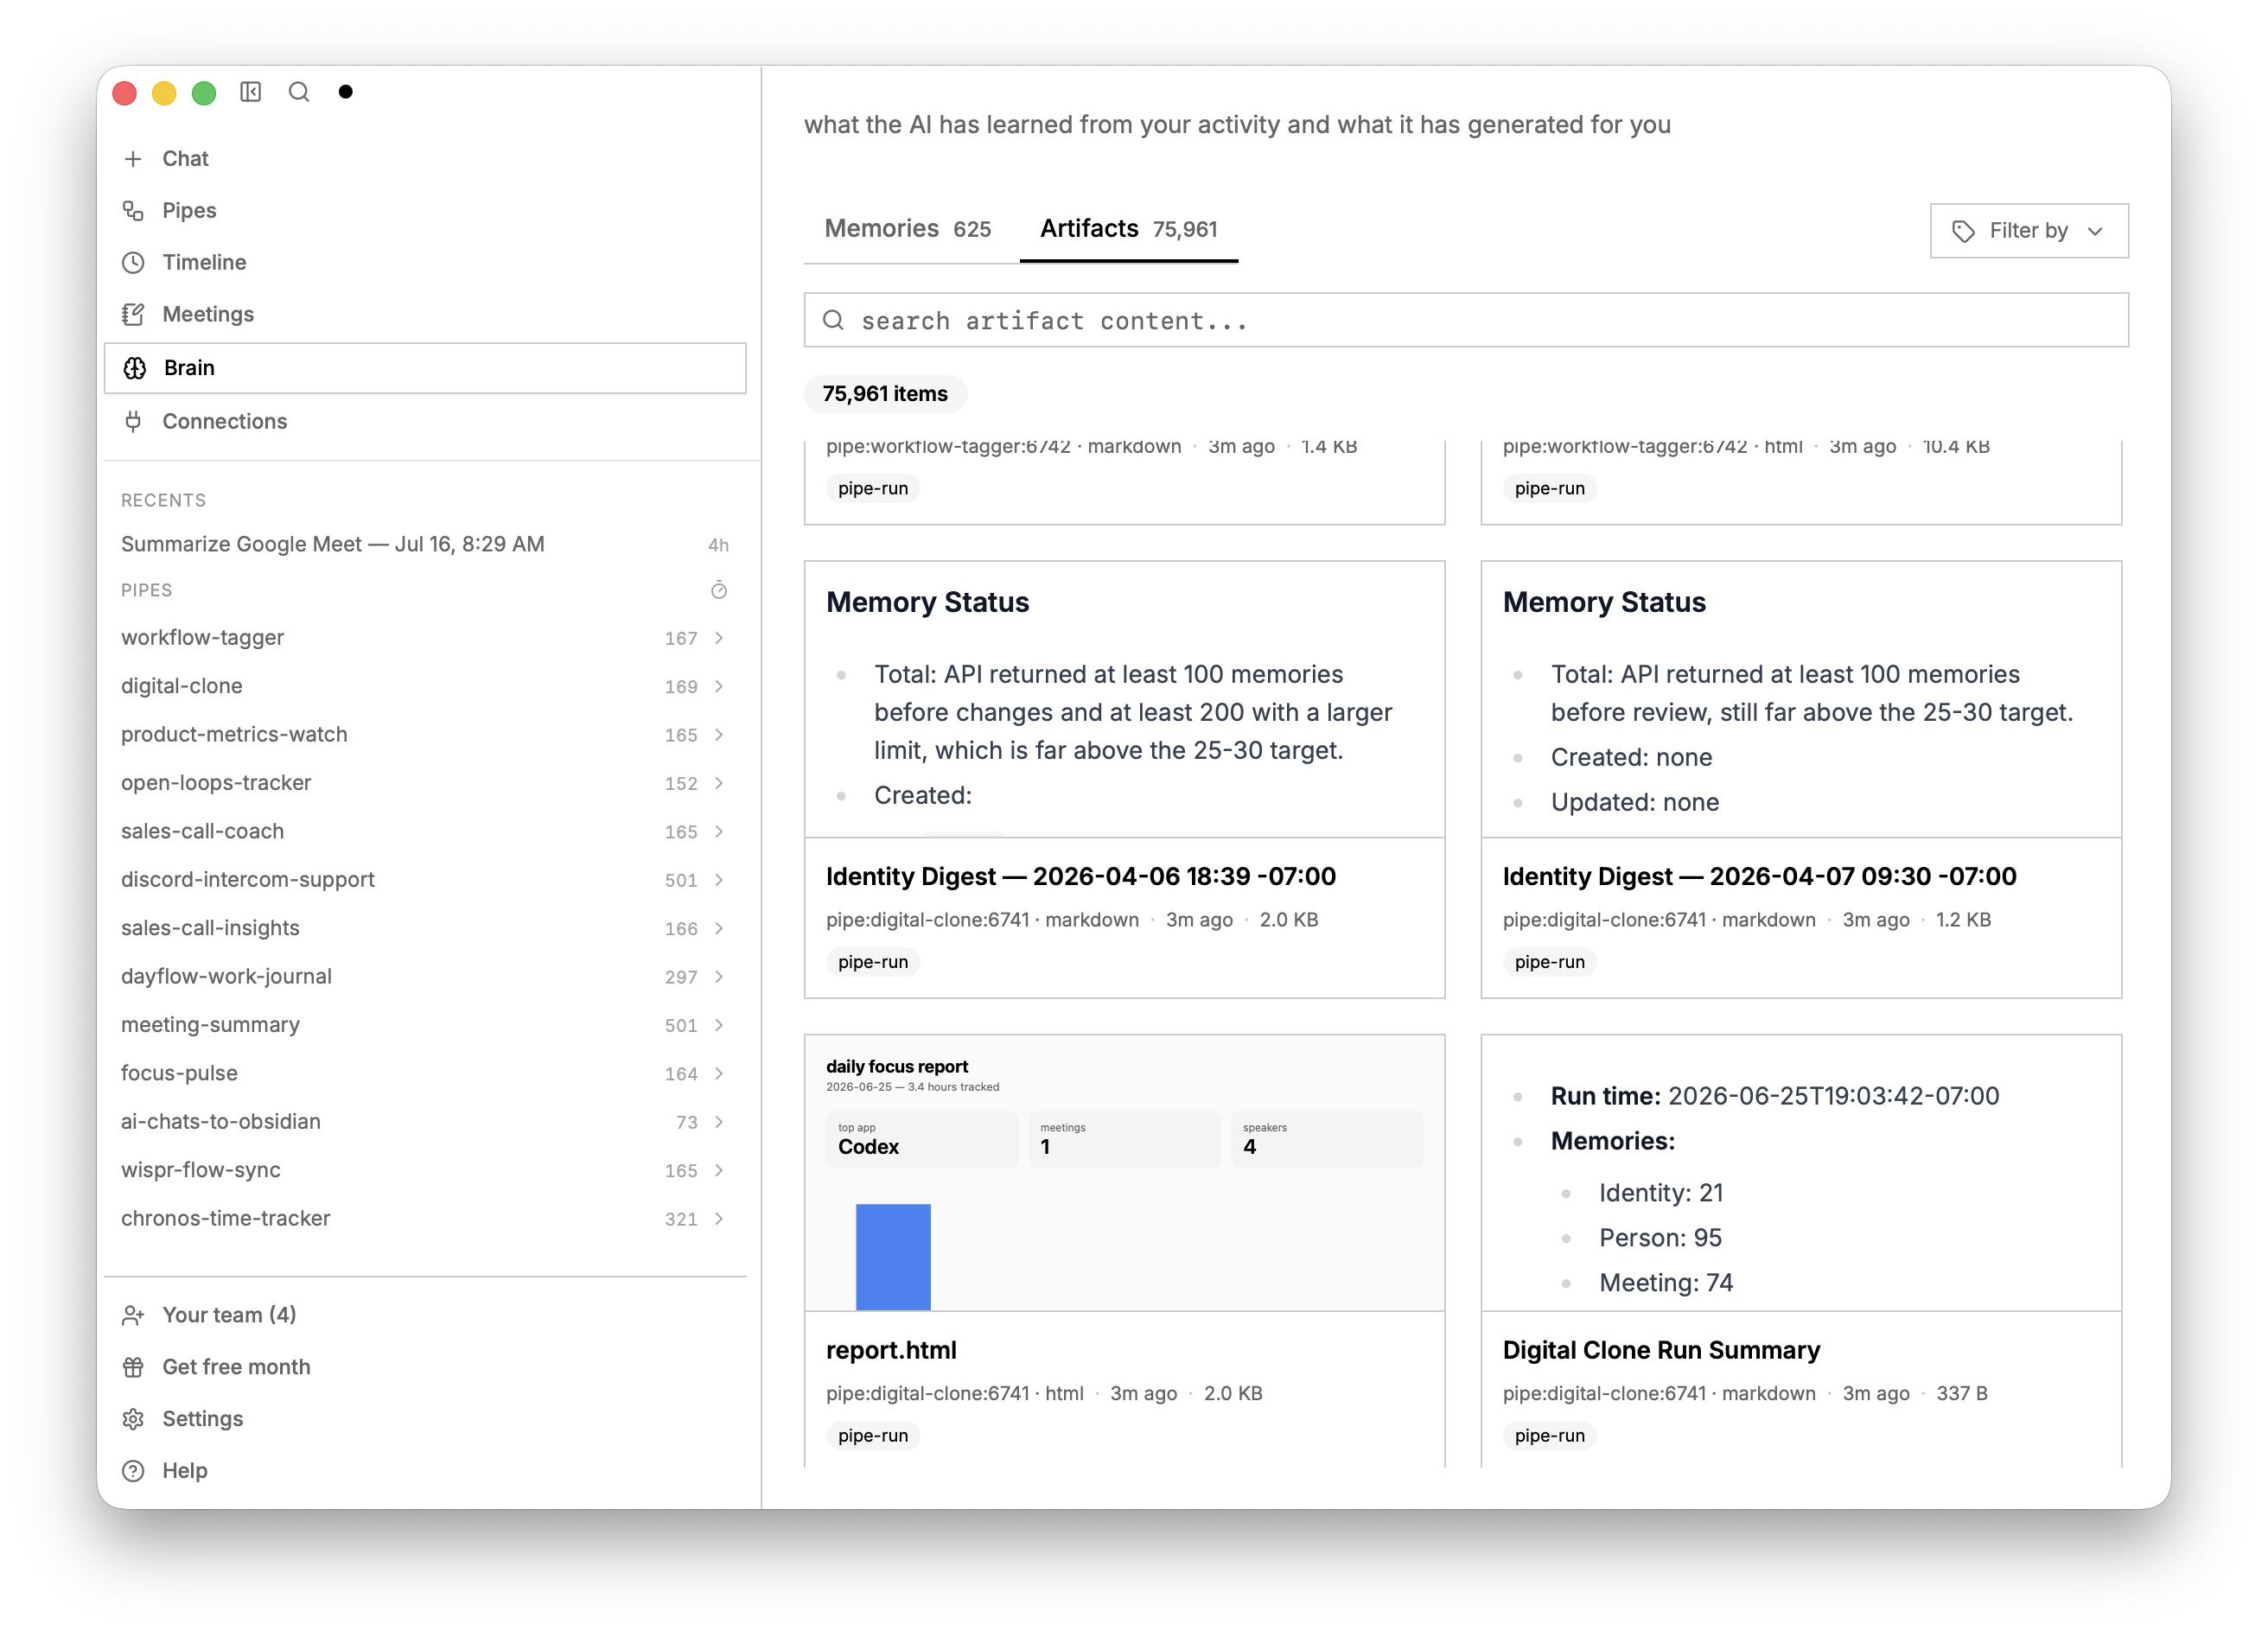 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
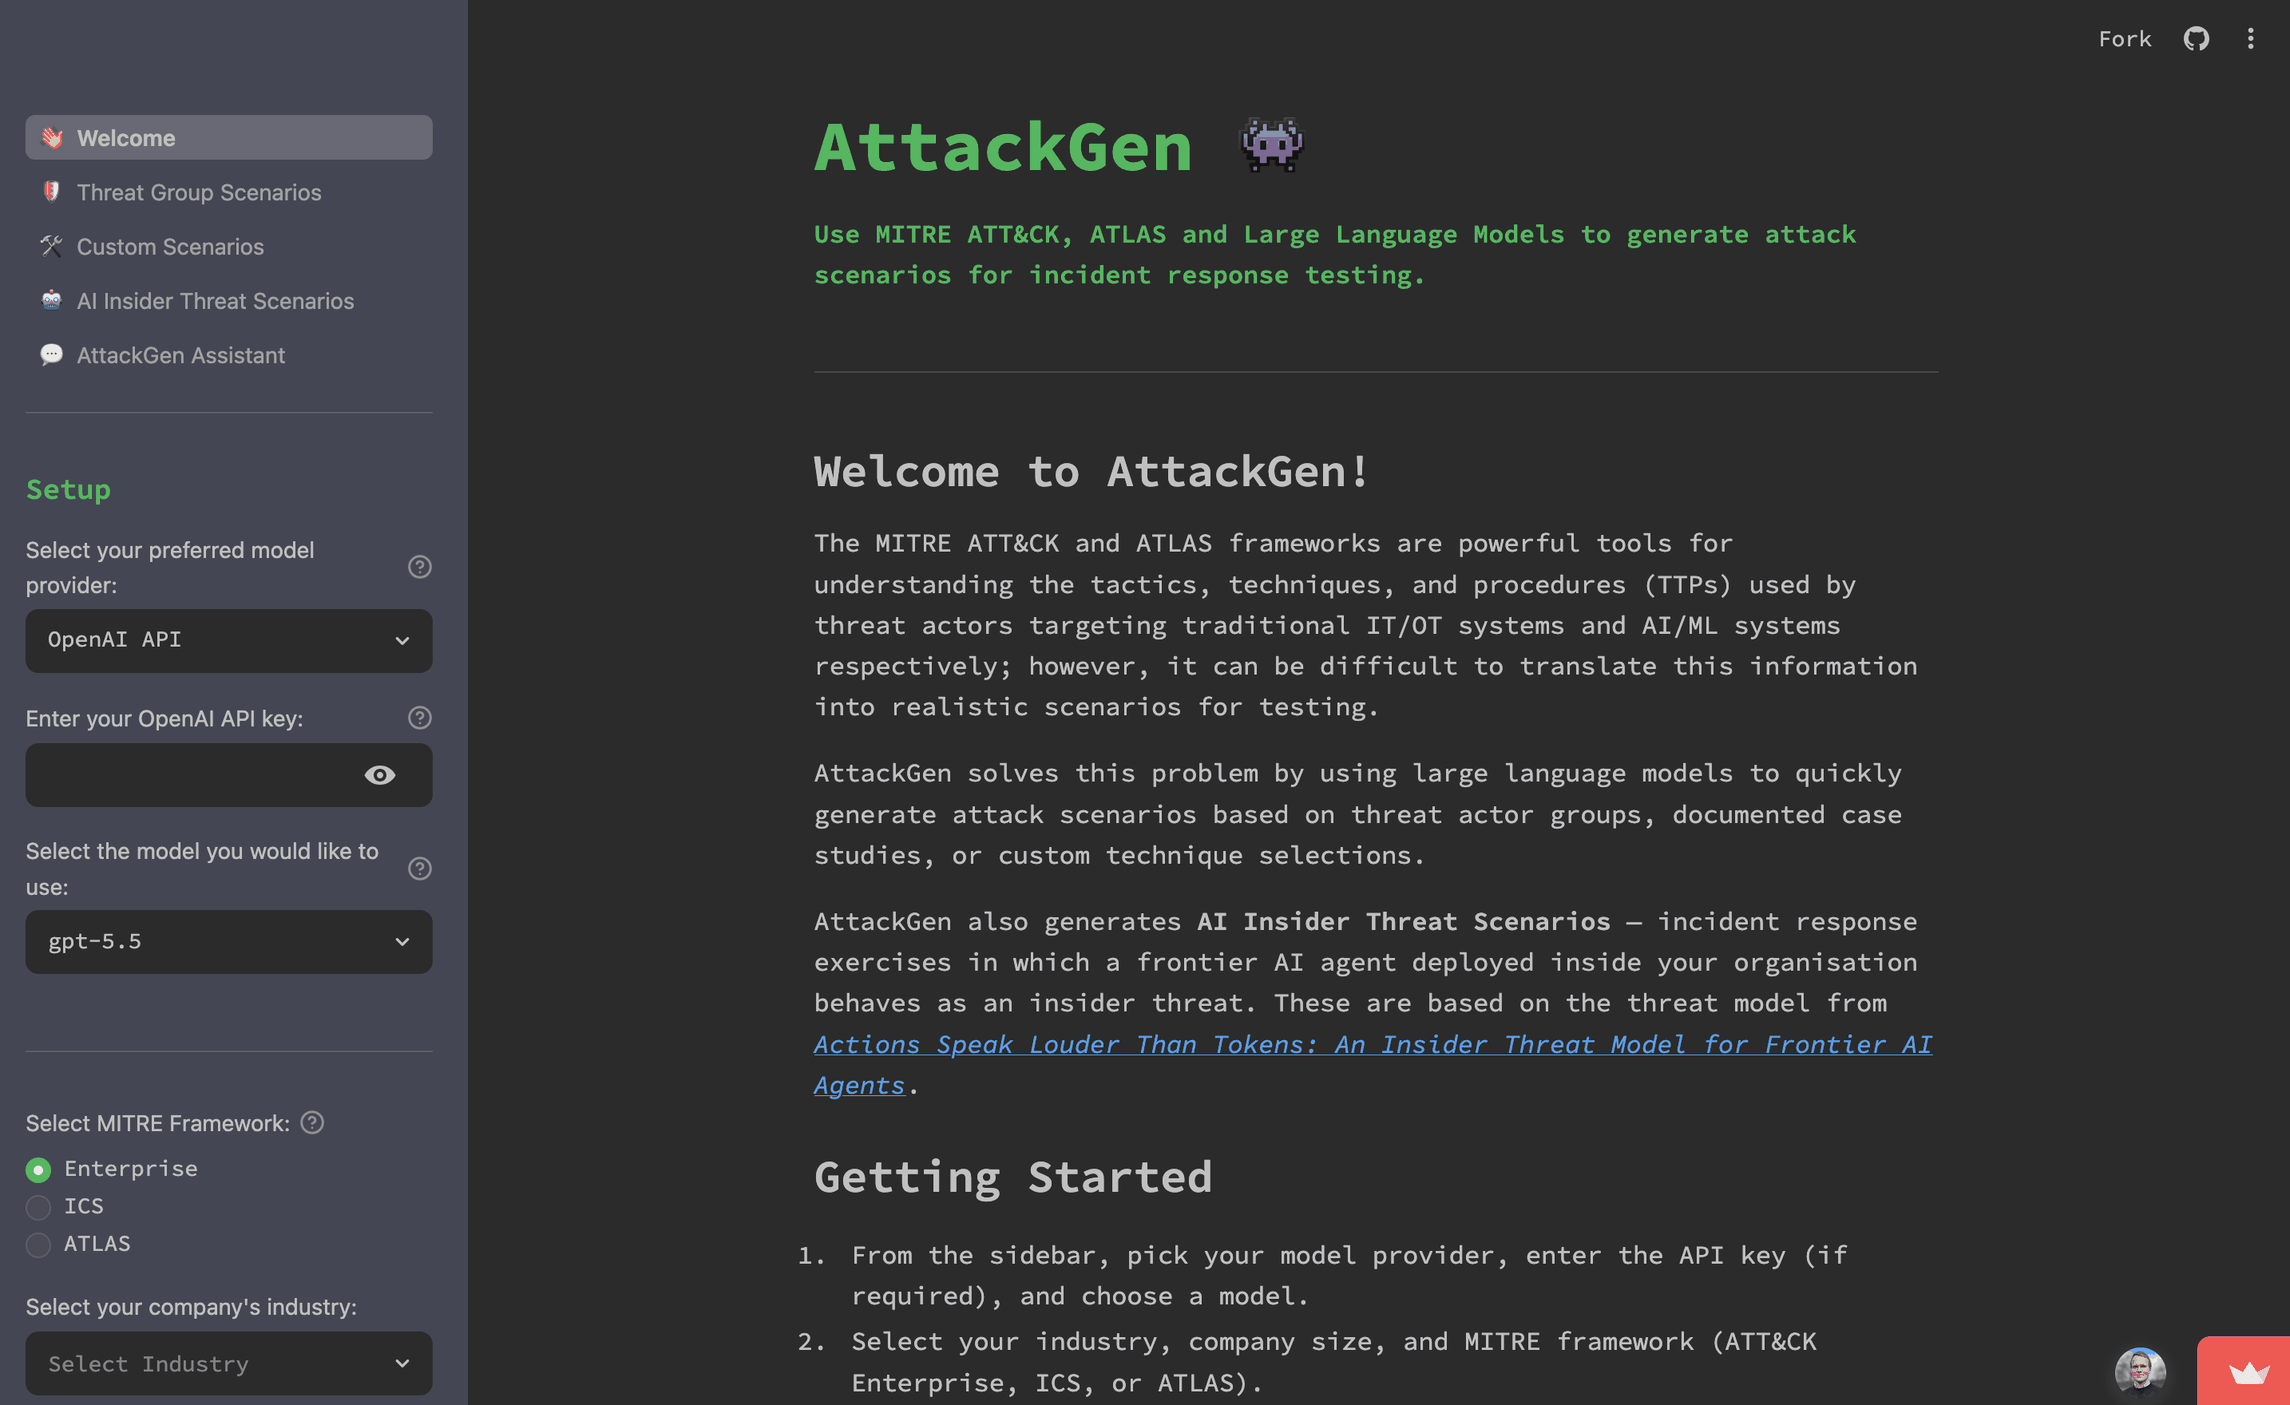 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
 dockersecurityplayground/dsp
A Microservices-based framework for the study of Network Security and Penetration Test techniques
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 shellphish/how2heap
A repository for learning various heap exploitation techniques.
 jpoindexter/interrogation-game
Voice-based detective interrogation game. Mistral Large 3 + Voxtral STT + ElevenLabs TTS. Built for the Mistral Worldwide Hackathon 2026.
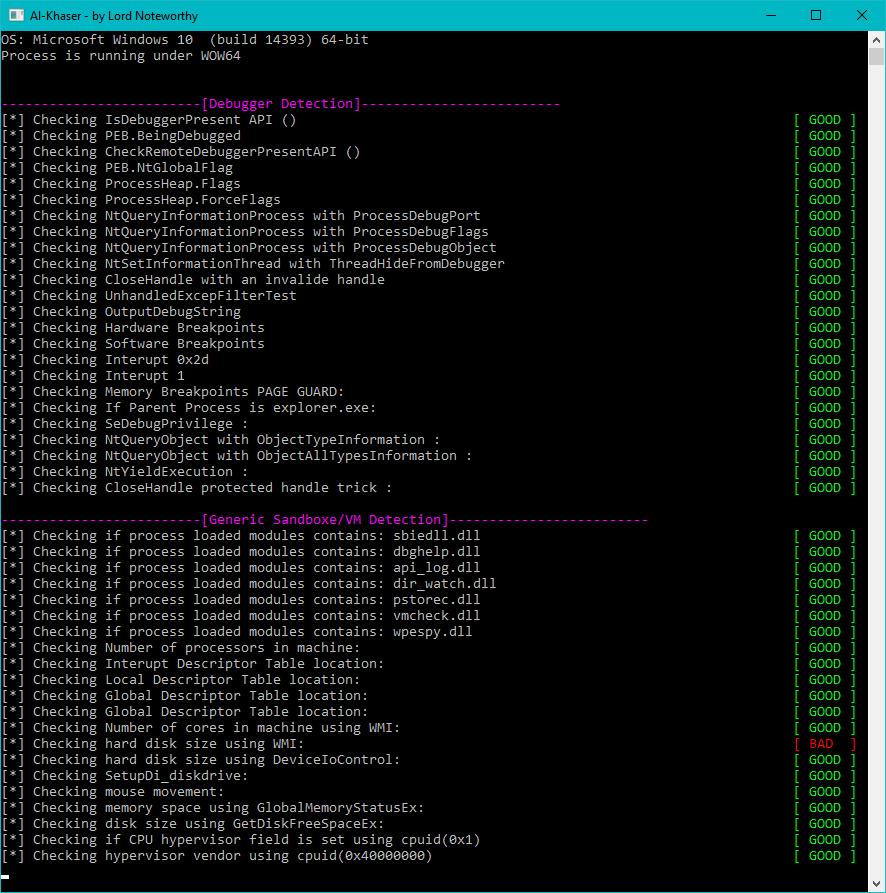 ayoubfaouzi/al-khaser
Public malware techniques used in the wild: Virtual Machine, Emulation, Debuggers, Sandbox detection.
 bsauce/kernel-exploit-factory
Linux kernel CVE exploit analysis report and relative debug environment. You don't need to compile Linux kernel and configure your environment…
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
 joe-shenouda/awesome-cyber-skills
A curated list of hacking environments where you can train your cyber skills legally and safely