Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
13 results
TP-Link-TL-WR820N-CVE-2025-14175 preview

TP-Link-TL-WR820N-CVE-2025-14175

GitHubcybervinner/tp-link-tl-wr820n-cve-2025-14175

Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.

cryptographyeducationembedded-systems-security+3
8 months ago
CVE-2023-33381-MitraStar-GPT-2741GNAC preview

CVE-2023-33381-MitraStar-GPT-2741GNAC

GitHubduality084/cve-2023-33381-mitrastar-gpt-2741gnac

Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…

binary-analysisembedded-systems-securityexploitation+4
133 years ago
ble_norton_core preview

ble_norton_core

GitHubembedi/ble_norton_core

Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…

bluetooth-securityexploitationhardware-security+5
318 years ago
CVE-2022-24693 preview

CVE-2022-24693

GitHublukejenkins/cve-2022-24693

Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…

embedded-systems-securityexploitationfirmware-analysis+6
31 year ago
project-memoria-detector preview

project-memoria-detector

GitHubforescout/project-memoria-detector

Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…

embedded-systems-securityfirmware-analysisiot-security+2
3245 years ago
CVE-2021-36260-hikvision preview

CVE-2021-36260-hikvision

GitHubshubtheone/cve-2021-36260-hikvision

Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…

command-and-controlexploitationiot-security+3
8 months ago
hassh preview
Archived

hassh

GitHubsalesforce/hassh

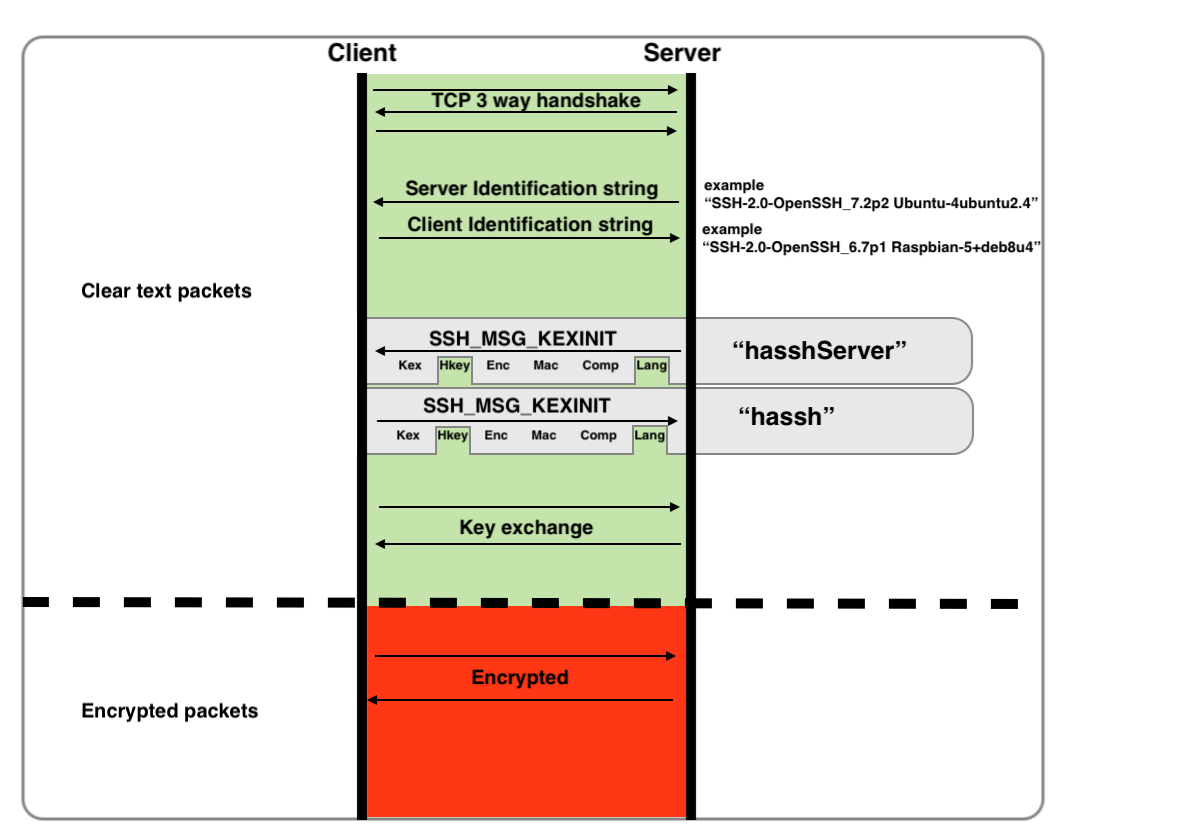
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…

anomaly-detectionforensicsincident-response+5
5541 year ago
Privilege-escalation-MitraStar preview

Privilege-escalation-MitraStar

GitHubleoservalli/privilege-escalation-mitrastar

Privilege escalation vulnerability on MitraStar routers

exploitationiot-securityprivilege-escalation+1
154 years ago
fapro preview

fapro

GitHubfofapro/fapro

Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…

defensive-toolsfingerprint-spoofinginformation-gathering+3
1.6k1 year ago
openwisp-controller preview

openwisp-controller

GitHubopenwisp/openwisp-controller

Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…

identity-access-managementiot-securitynetwork-access-control+3
7723 days ago
CVE-2024-22894 preview

CVE-2024-22894

GitHubjaarden/cve-2024-22894

Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…

cryptographyembedded-systems-securityexploitation+6
32 years ago
cve-2026-8697 preview

cve-2026-8697

GitHubitzmetanjim/cve-2026-8697

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…

educationexploitationhardware-iot-security+7
13 months ago
CVE-2024-30973 preview

CVE-2024-30973

GitHubathos-zago/cve-2024-30973

POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN

exploitationiot-securitymisconfiguration+3
2 years ago