
cotopaxi
 samsung/cotopaxi
Set of tools for security testing of Internet of Things devices using specific network IoT protocols
fuzzingiot-securitynetwork-security+2
samsung/cotopaxiSet of tools for security testing of Internet of Things devices using specific network IoT protocols
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 whad-team/whad-client
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
 breaktoprotect/cve-2017-16778-intercom-dtmf-injection
A coordinated disclosure and security advisory on Fermax Intercom DTML Injection vulneraiblity. Special thanks to Fermax International for prompt…
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
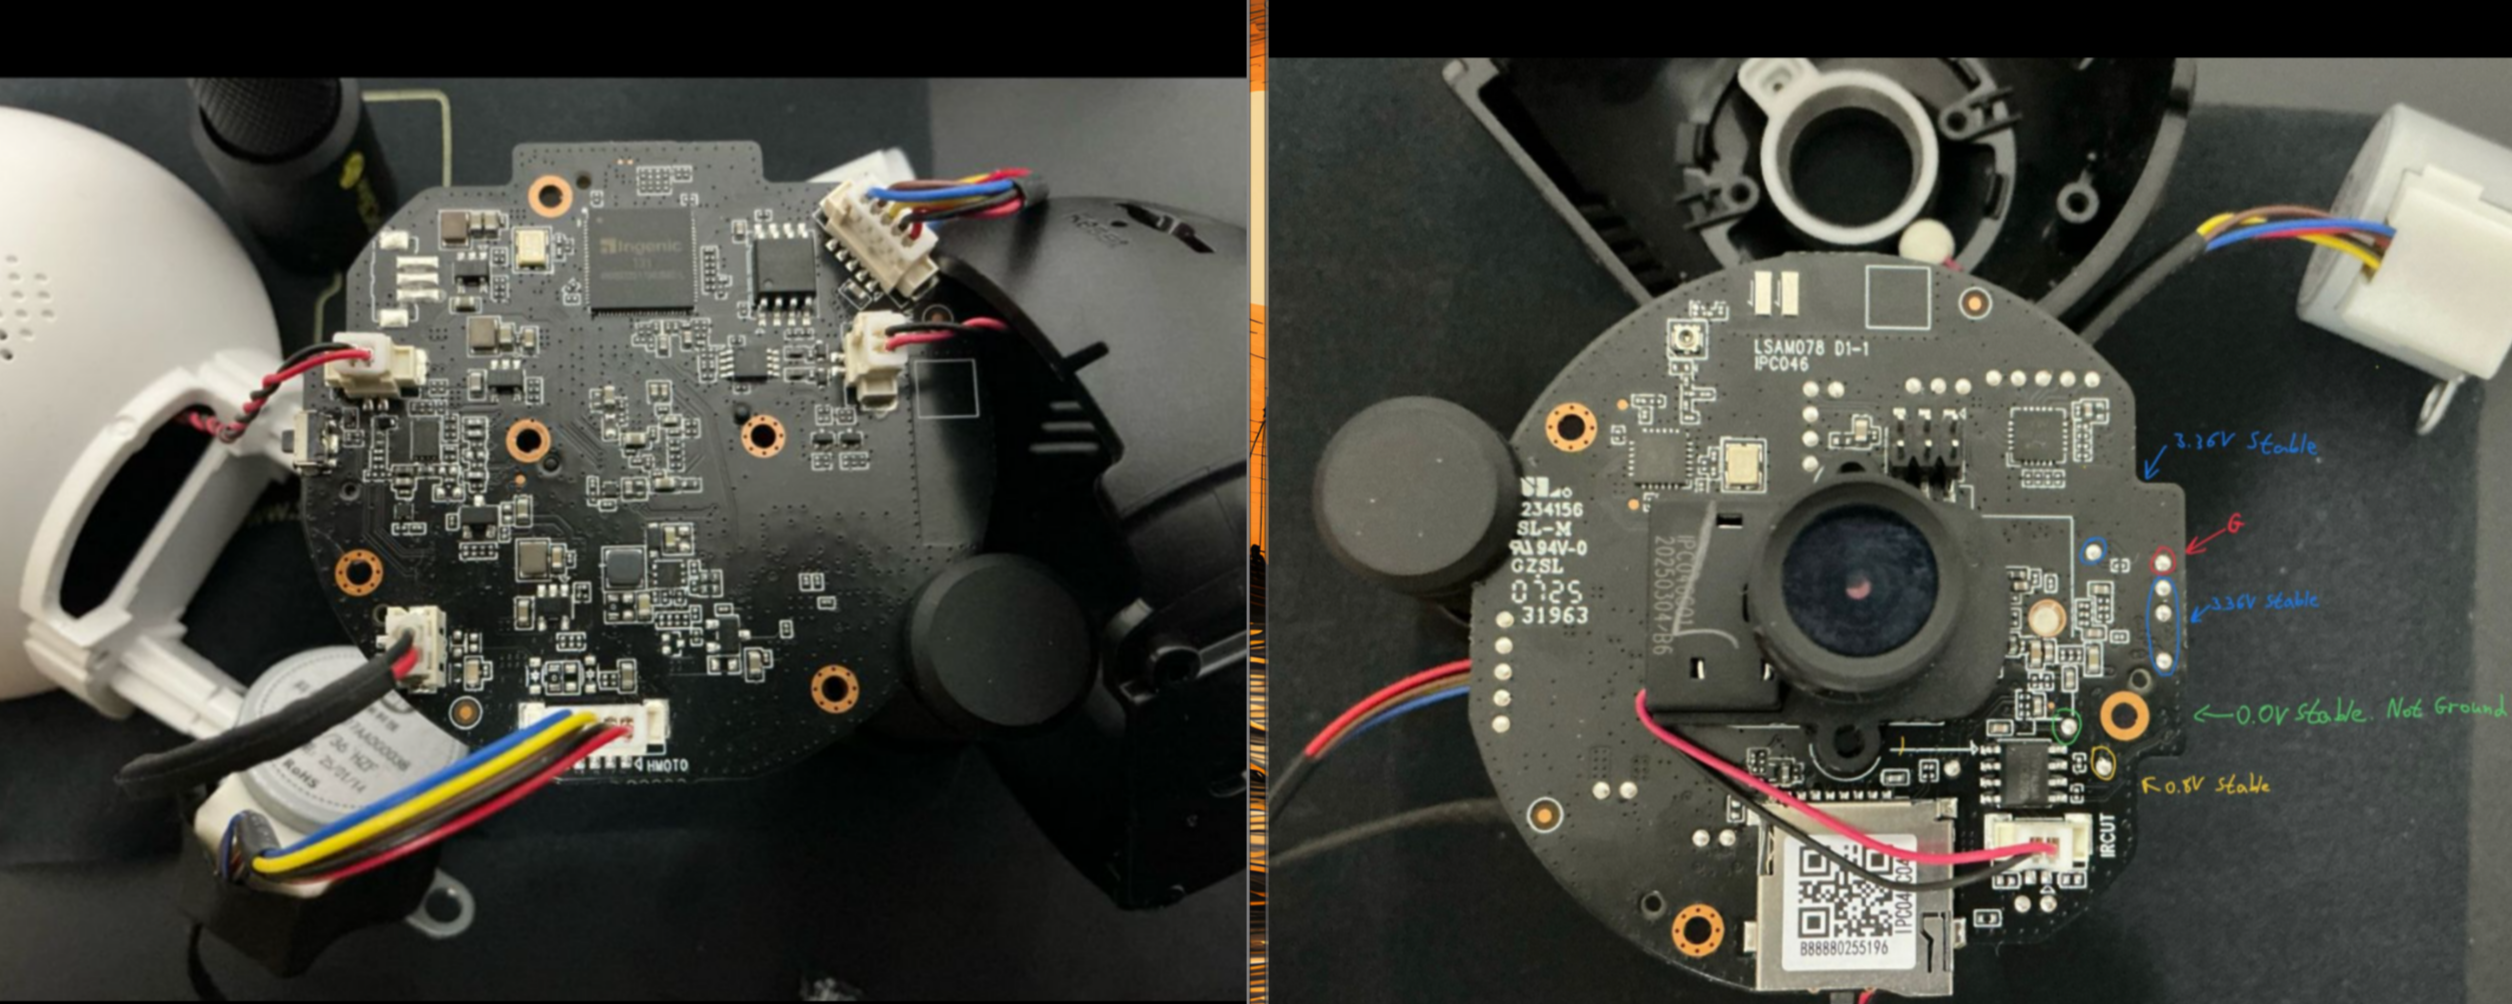 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
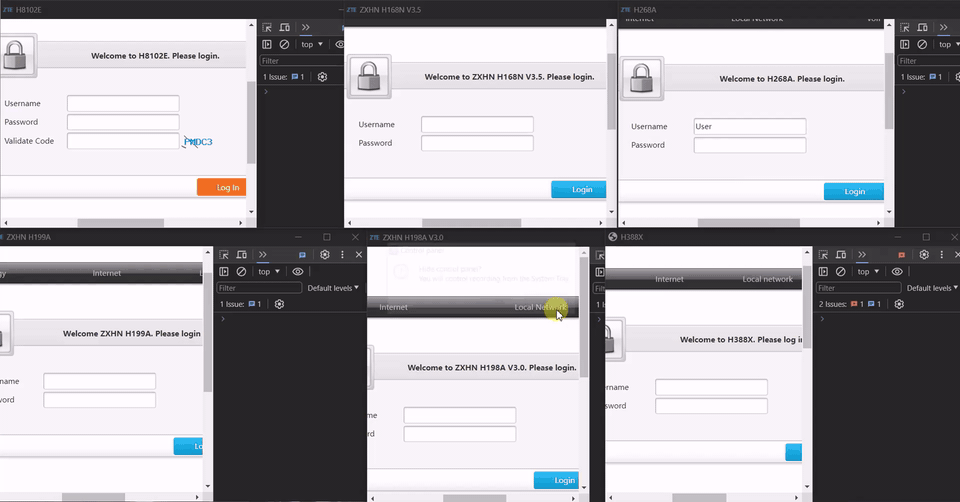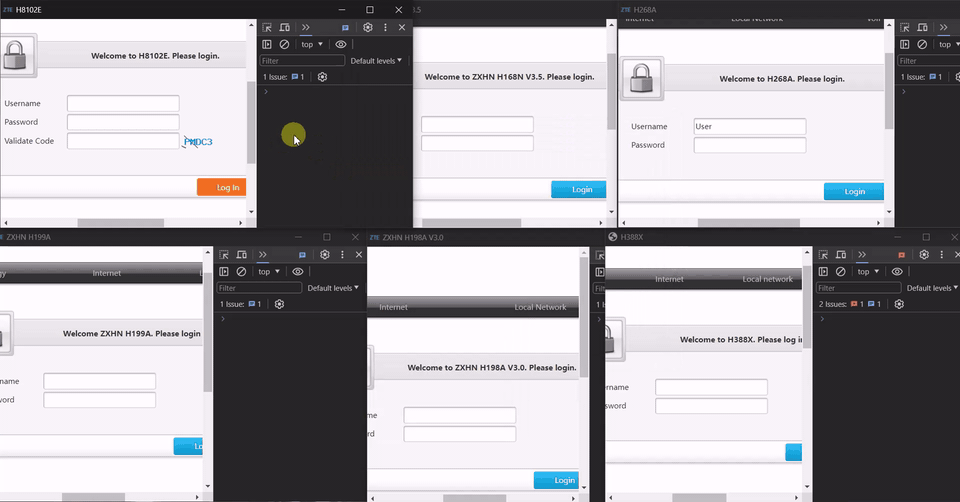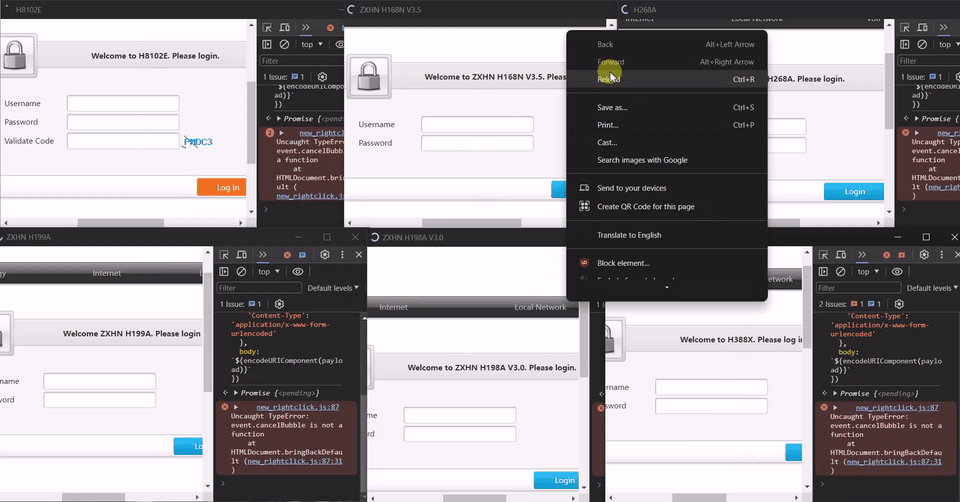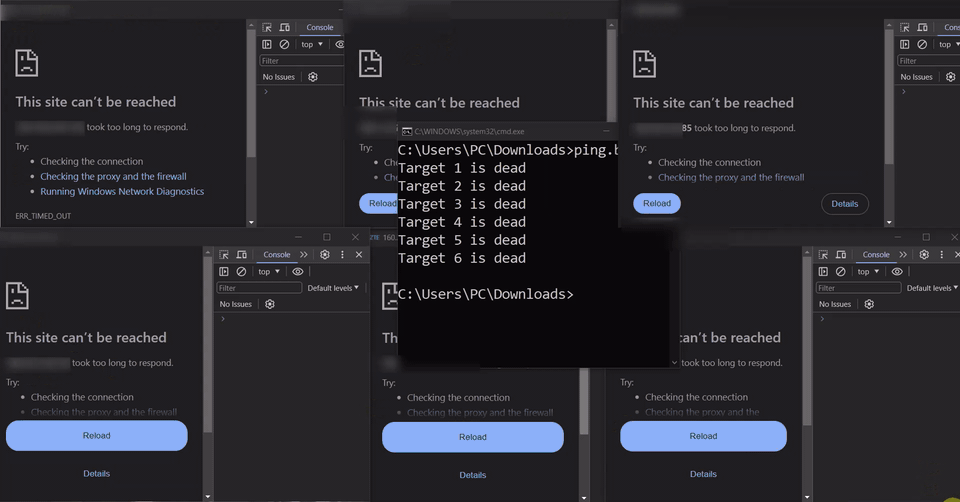 minanagehsalalma/cve-2026-34473-unauthenticated-dos-zte-routers
Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.
 deepwoodssec/cve-2026-36522
Proof-of-concept exploit for CVE-2026-36522: unauthenticated NaN injection via MAVLink PARAM_SET in ArduPilot ArduPlane, causing DoS or silent…

 dorskfr/tapodate
Sets up a local Tapo C200 using CVE-2021-4045
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…