

obike
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
api-securitybluetooth-securitycryptography+4
427 years ago
antoinet/obikeReverse engineering of the oBike protocol communication (BLE and HTTP)
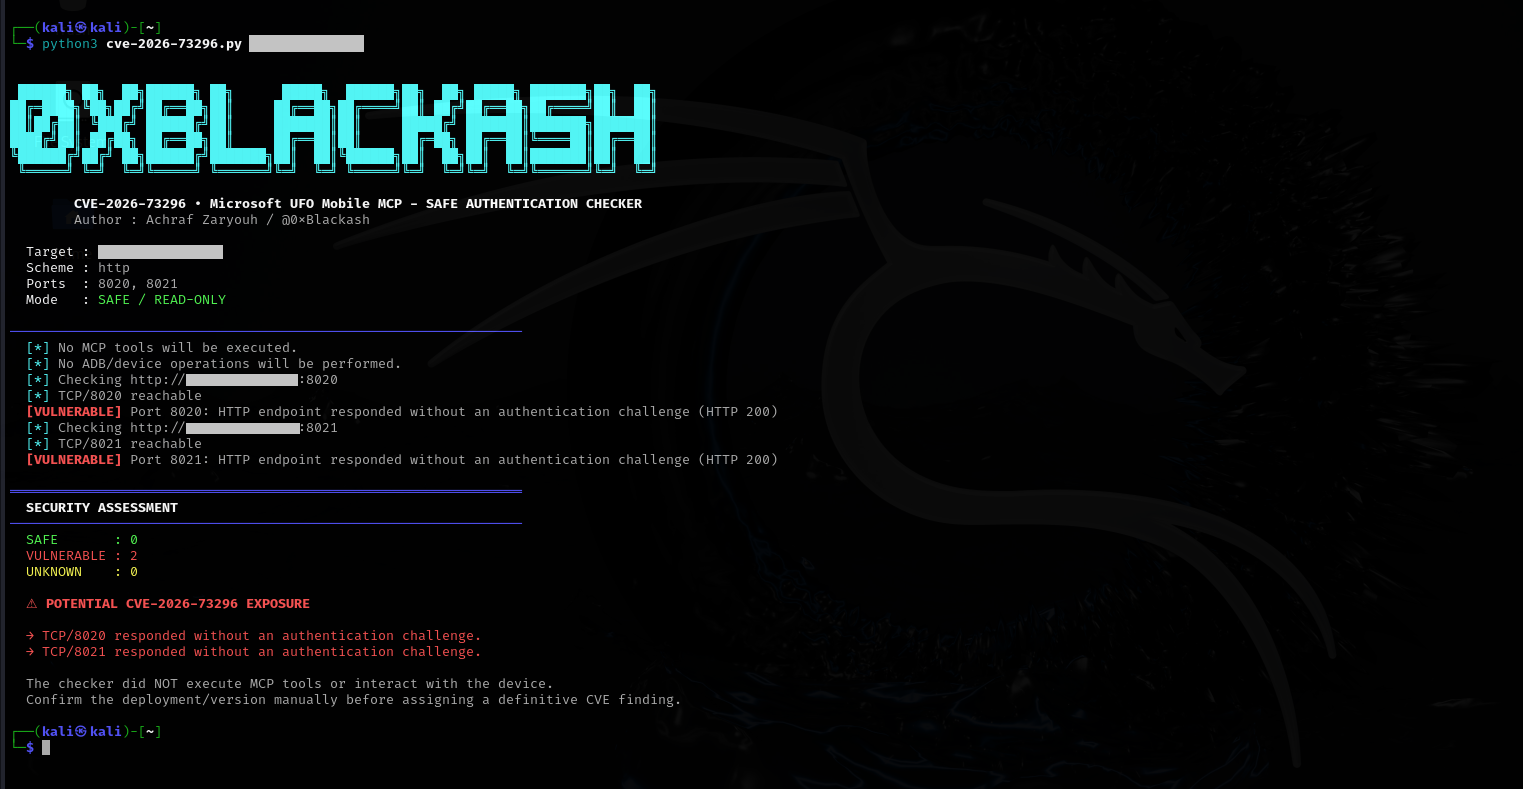 0xblackash/cve-2026-73296
Non-destructive security assessment tool for CVE-2026-73296, checking authentication boundaries on exposed Mobile MCP HTTP servers (ports 8020/8021)…
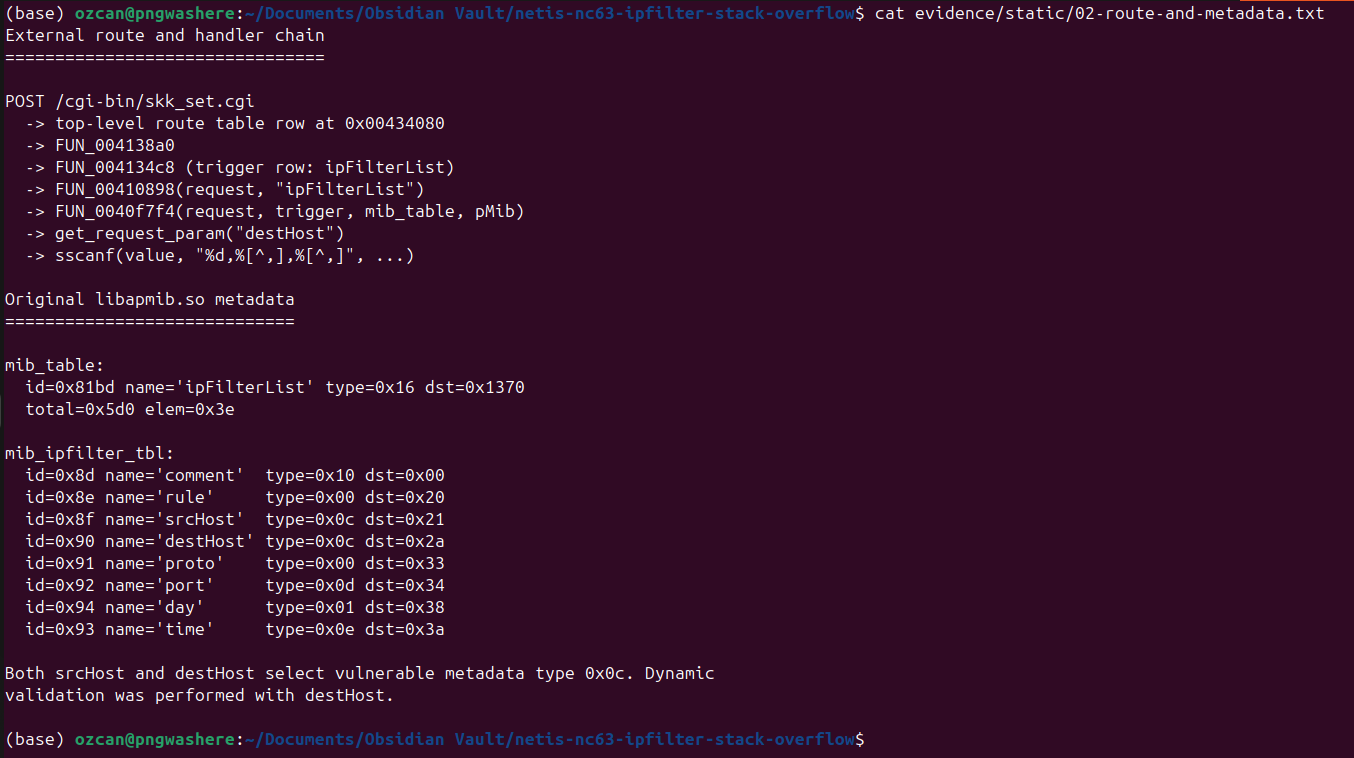 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 thingsboard/thingsboard
Open-source IoT Platform - Device management, data collection, processing and visualization.
 forescout/project-memoria-detector
Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
 thewhiteh4t/cve-2020-9375
TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
 inartin/365cam-stream
Local streaming tool for cheap WiFi cameras that bypasses cloud services and phone apps. Discovers cameras on your network, authenticates via PPPP…
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 secforce/cve-2021-37748
Exploit code for CVE-2021-37748 targeting Grandstream HT801 ATA, demonstrating remote code execution via crafted HTTP requests.
 dumitory-dev/cve-2020-35391-poc
Tenda N300 Authentication Bypass via Malformed HTTP Request Header
 k3ystr0k3r/routeglass
Multi-threaded router fingerprinting tool that identifies web-exposed network devices by analyzing HTTP responses, headers, and favicon hashes for…
 george0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http
Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 tim-hoekstra/cve-2022-37932
Proof-of-concept exploit for an authentication bypass in HP 1920 Series switches, allowing unauthenticated admin password change via crafted HTTP…
 fzbacon/cve-2023-27216_d-link_dsl-3782_router_command_injection
Proof-of-concept exploit for CVE-2023-27216, a command injection vulnerability in D-Link DSL-3782 routers, enabling remote code execution via crafted…
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 mrali-code/cve-2018-9995_dvr_credentials
Exploit tool for CVE-2018-9995 that extracts DVR credentials via unauthenticated HTTP request to vulnerable Nov, CeNova, QSee, and other DVR devices.
 likaifeng0/cve-2018-9995_dvr_credentials-dev_tool
Exploit tool for CVE-2018-9995 that extracts credentials from exposed DVR devices via HTTP request with cookie bypass, targeting multiple vendor…