
SecureTea-Project
 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
defensive-toolsintrusion-detectioniot-security+4
302
owasp/securetea-projectThe OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 xewdy444/netgrave
A tool for retrieving login credentials from Netwave IP cameras using a memory dump vulnerability (CVE-2018-17240)
 keowu/sjcam
Reverse engineering research and custom firmware for Allwinner V3-based IoT cameras, including firmware parsers, an AVIOCTRL client, and a…
 jollyjumbuckk/linksysleaks
Python3 script to scan for Linksys smart wifi devices that are vulnerable to CVE-2014-8244
 jarrettgohxz/cve-research
A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 spacehuhntech/esp8266_deauther
Affordable WiFi hacking platform for testing and learning
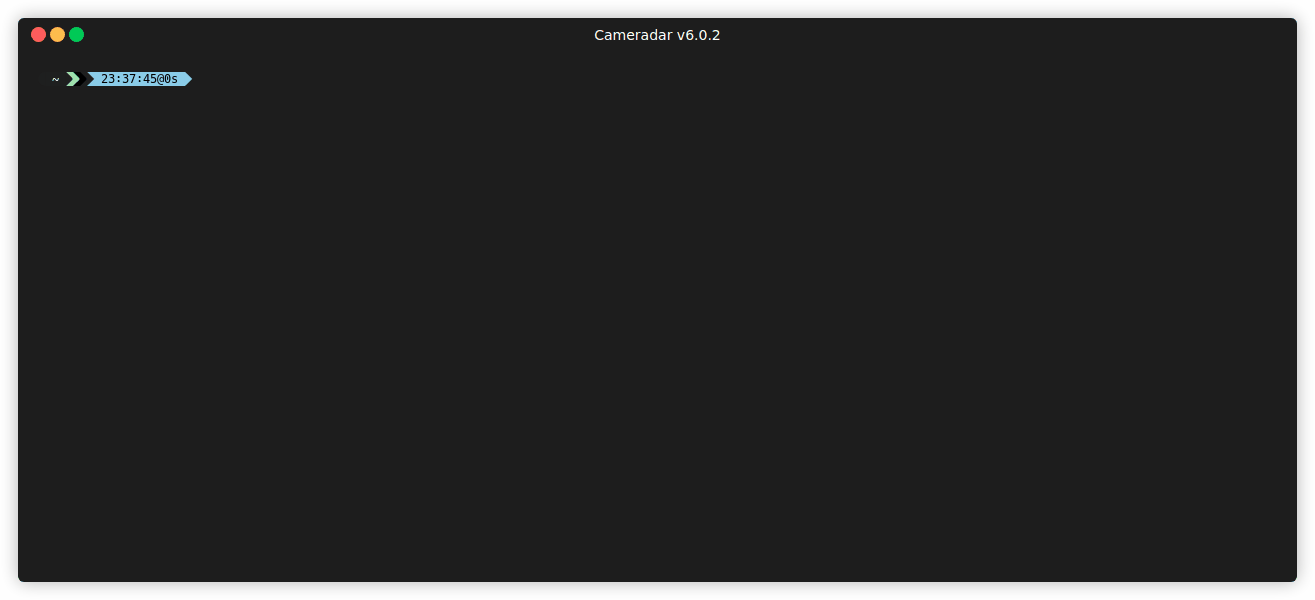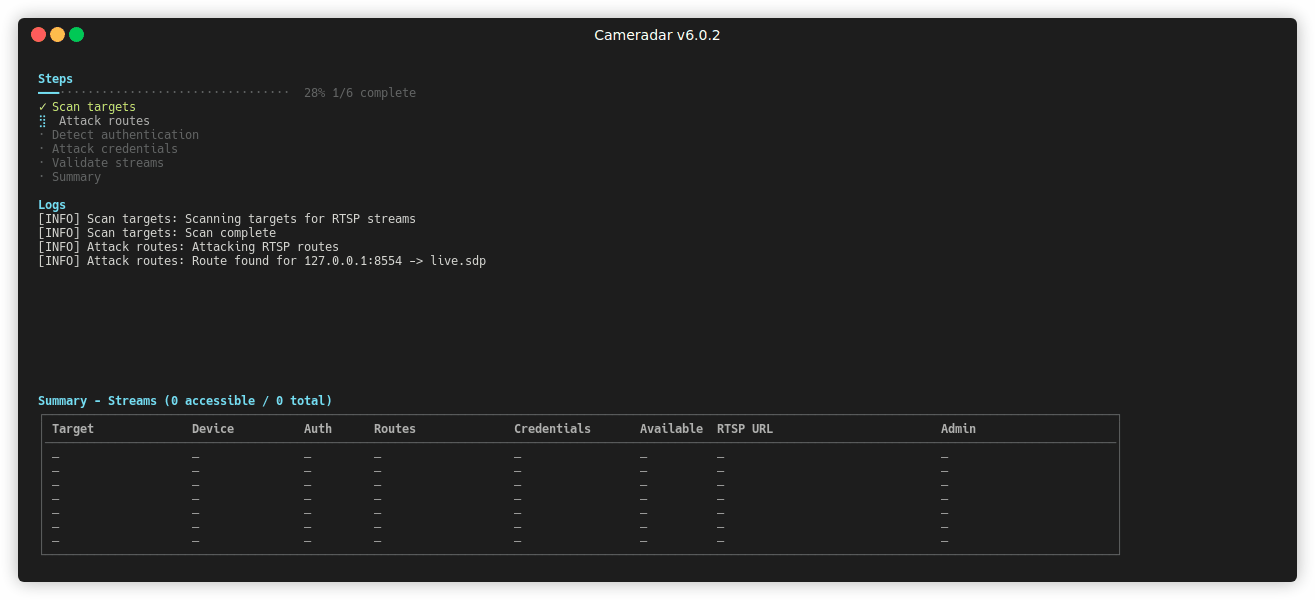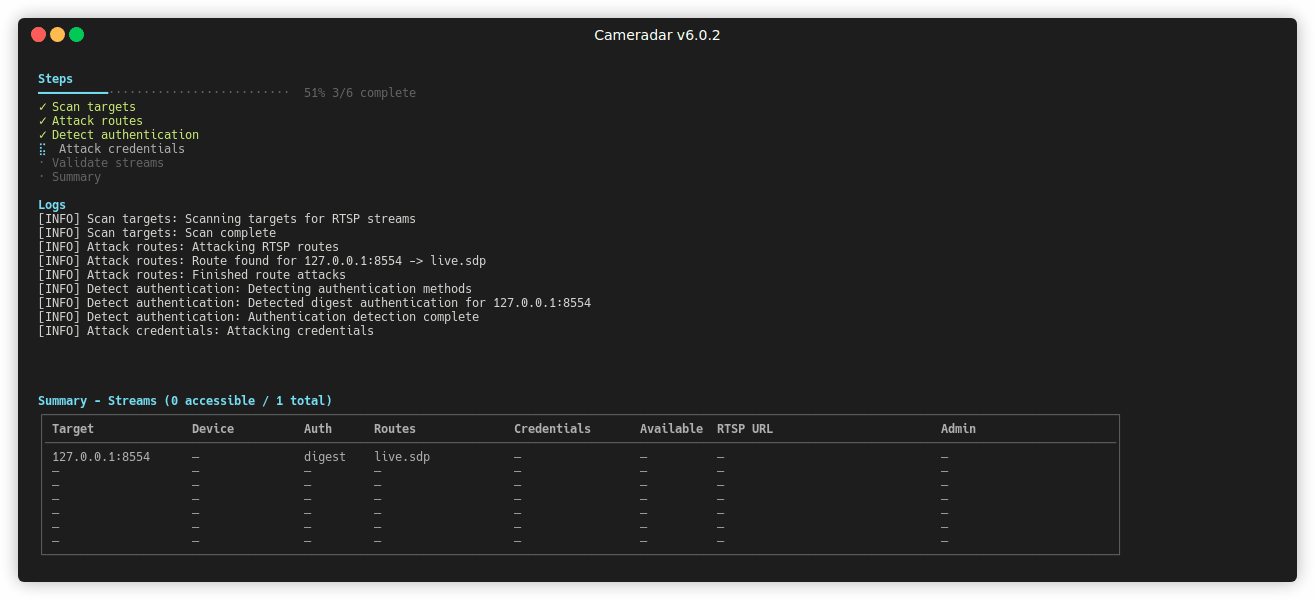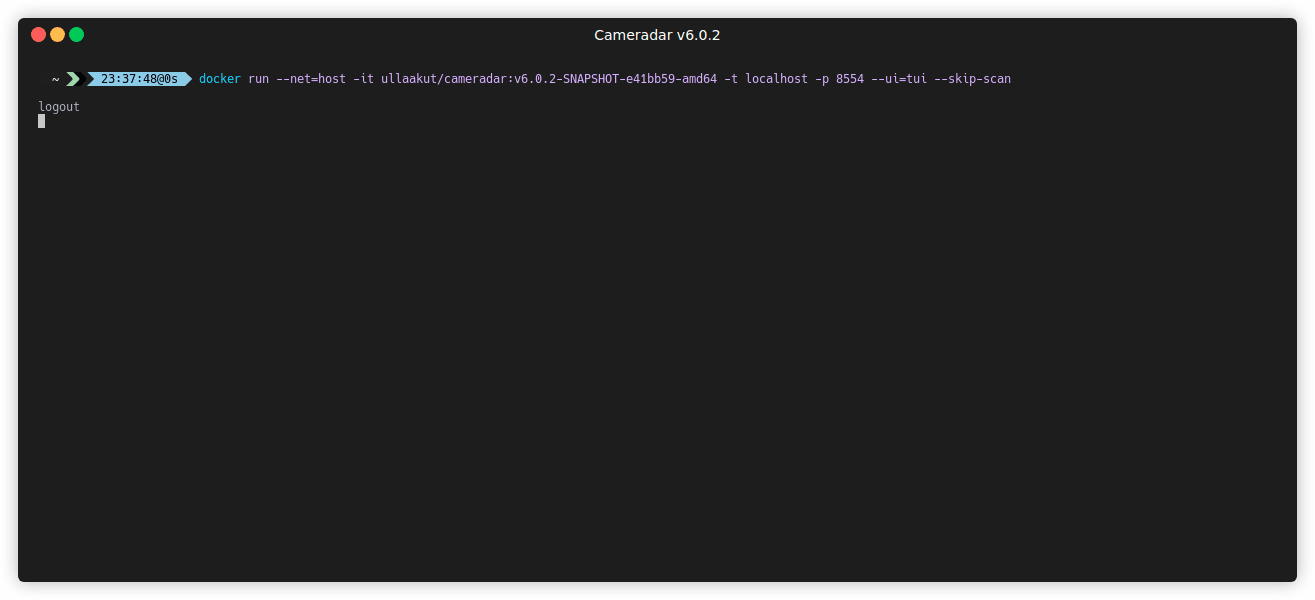 ullaakut/cameradar
Cameradar hacks its way into RTSP videosurveillance cameras
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
 umair-aziz025/dahua-cve-research
Dahua IP camera CVE research toolkit (CVE-2021-33044/33045, CVE-2025-31700/31701)
 0xnslabs/cve-2022-36267-poc
PoC Script for CVE-2022-36267: Exploits an unauthenticated remote command injection vulnerability in Airspan AirSpot 5410 antenna.
 spy0x7/cve-2021-33044
Dahua IPC/VTH/VTO devices auth bypass exploit
 interceptsuite/interceptsuite
MITM proxy for TCP/TLS/DTLS/UDP traffic, with STARTTLS, IoT, Thick Client and more.
 0xnslabs/cve-2022-36553-poc
PoC Script for CVE-2022-36553: Exploits an unauthenticated remote command injection vulnerability in Hytec Inter HWL-2511-SS device.
 ozcanpng/cve-2026-73673
Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…
 0xnslabs/cve-2024-25832-poc
PoC Script for CVE-2024-25832: Exploit chain reverse shell, information disclosure (root password leak) + unrestricted file upload in DataCube3