
emba
 e-m-b-a/emba
EMBA - The firmware security analyzer
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+8
3.7k
e-m-b-a/embaEMBA - The firmware security analyzer
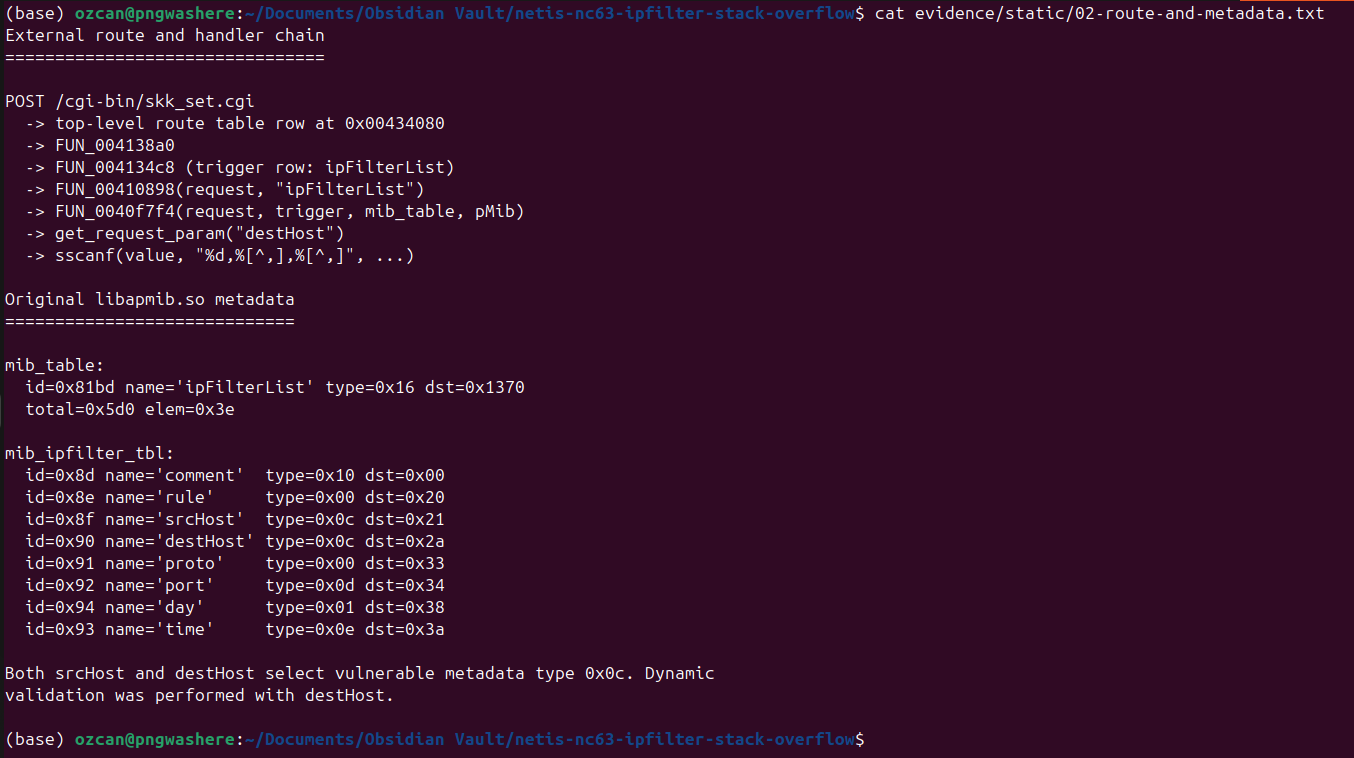 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
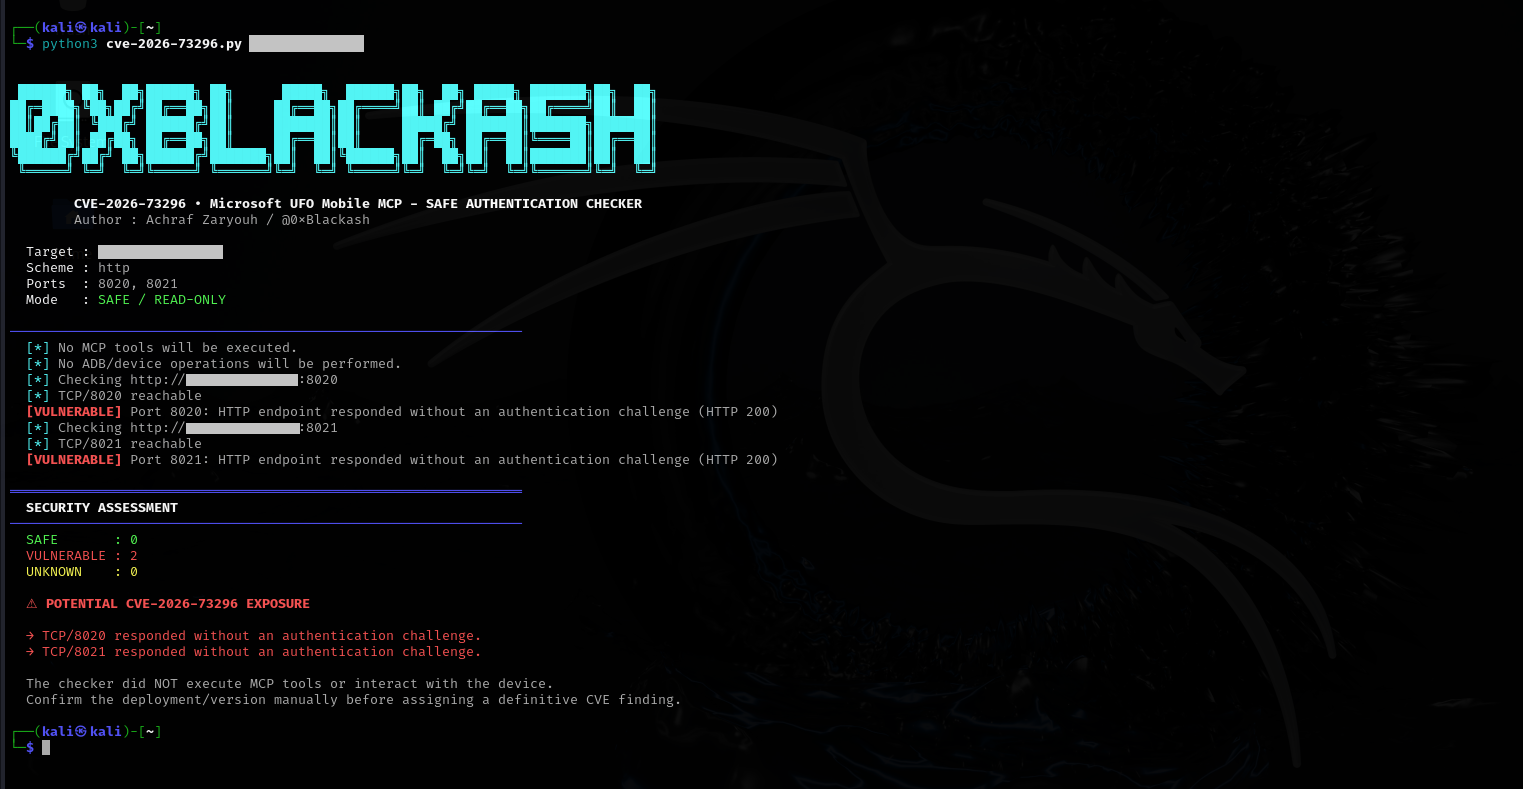 0xblackash/cve-2026-73296
Non-destructive security assessment tool for CVE-2026-73296, checking authentication boundaries on exposed Mobile MCP HTTP servers (ports 8020/8021)…
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 danish1162/cve-2026-2035703-x300
Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 limingxi6/cve-2020-9373-netgear-r6400
解决网络安全漏洞
 we5ter/scanners-box
A powerful and open-source toolkit for hackers and security automation - 安全行业从业者自研开源扫描器合辑

 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 yeahhbean/cve-2026-45729
ThorVG NULL pointer dereference via malformed SVG — AFL++ fuzzing writeup
 keowu/sjcam
Reverse engineering research and custom firmware for Allwinner V3-based IoT cameras, including firmware parsers, an AVIOCTRL client, and a…
 runzeroinc/vulns-2026-fatfs-chance
Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…
 redr0nin/code-27-companion-hub-exploits
Proof of concept for CVE-2026-36027 and CVE-2026-36028
 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…