

Penetration_Testing_POC
 mr-xn/penetration_testing_poc
渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
curated-resourceseducationexploitation+6
7.4k
mr-xn/penetration_testing_poc渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 4onurdemir/tcl-androidtv-root-attempts
Documents reverse engineering of a TCL Android TV factory layer: 56 kHz IR protocol, tclfactoryos daemon, kernel IR driver, and evidence that…
 hcbt/cve-2026-9151
Authenticated OS command injection in the TP-Link Archer AX17 v1 VPN client import.
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
 vulncheck-oss/initial-access-community
Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…
 thebadinteger/p2pwn
Dahua cameras security scanner via P2P
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 cplusplus17/deco-filepush-disclosure
Disclosure and PoC for a root file read/write flaw in the TP-Link Deco XE75 Pro V3 debug channel (tmpsvr opcodes 0xC456/0xF0), with CVSS analysis and…
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
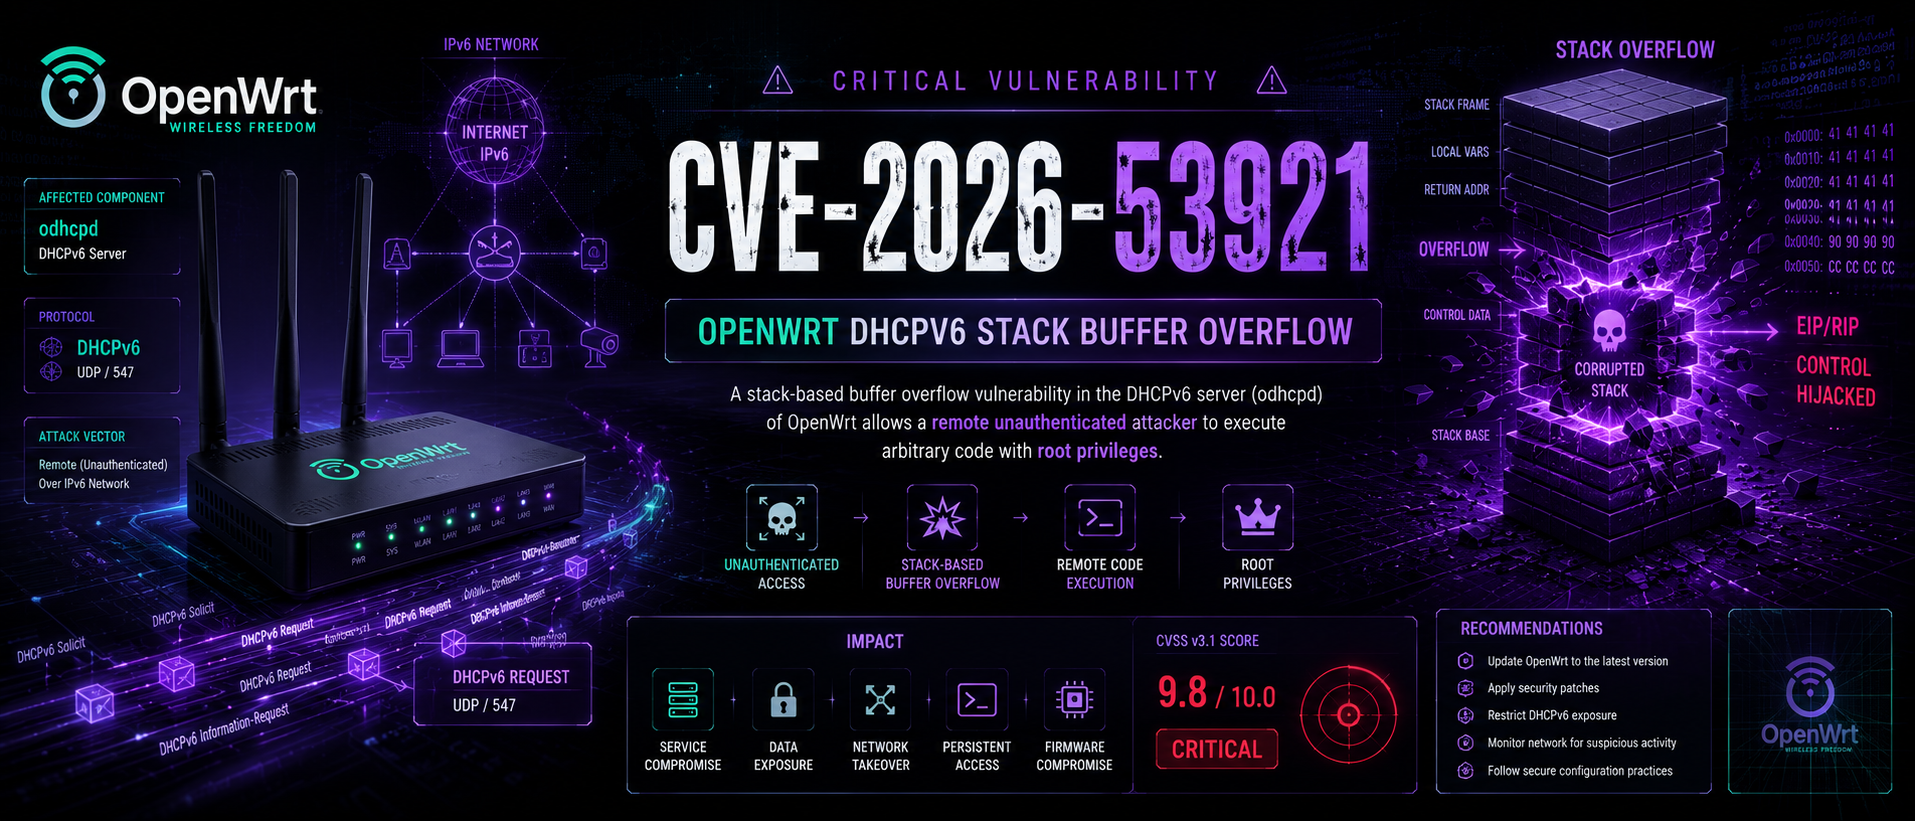 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
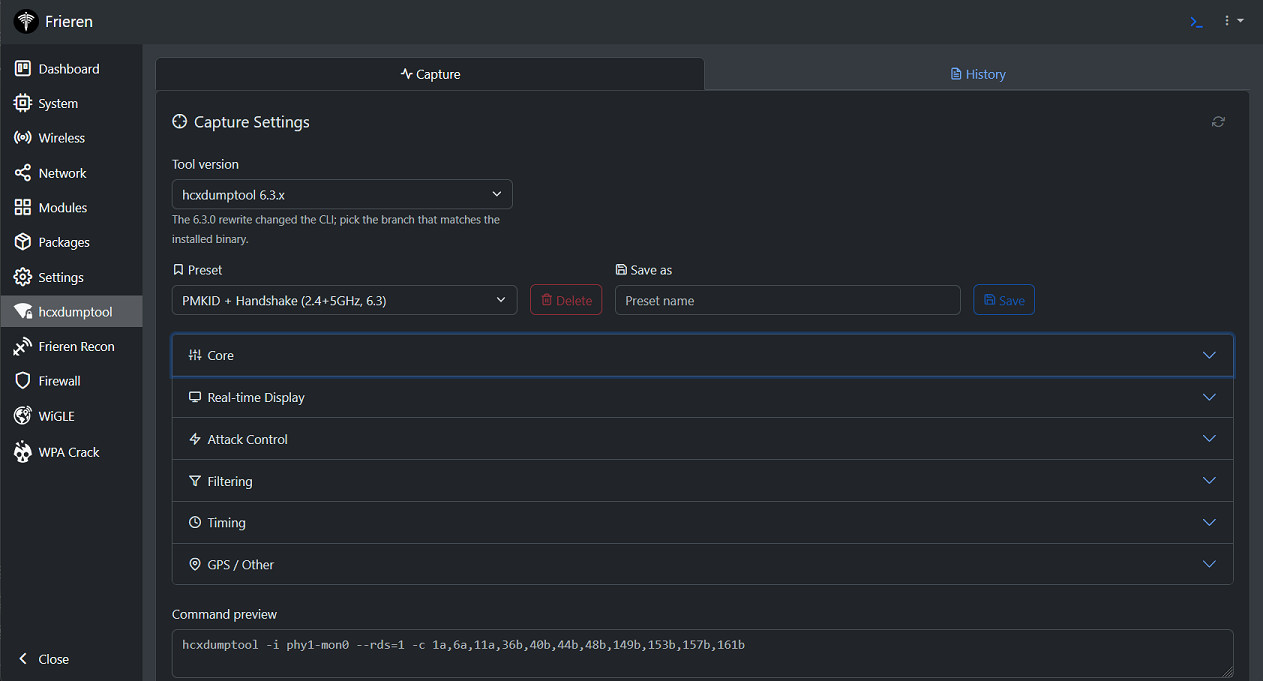 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
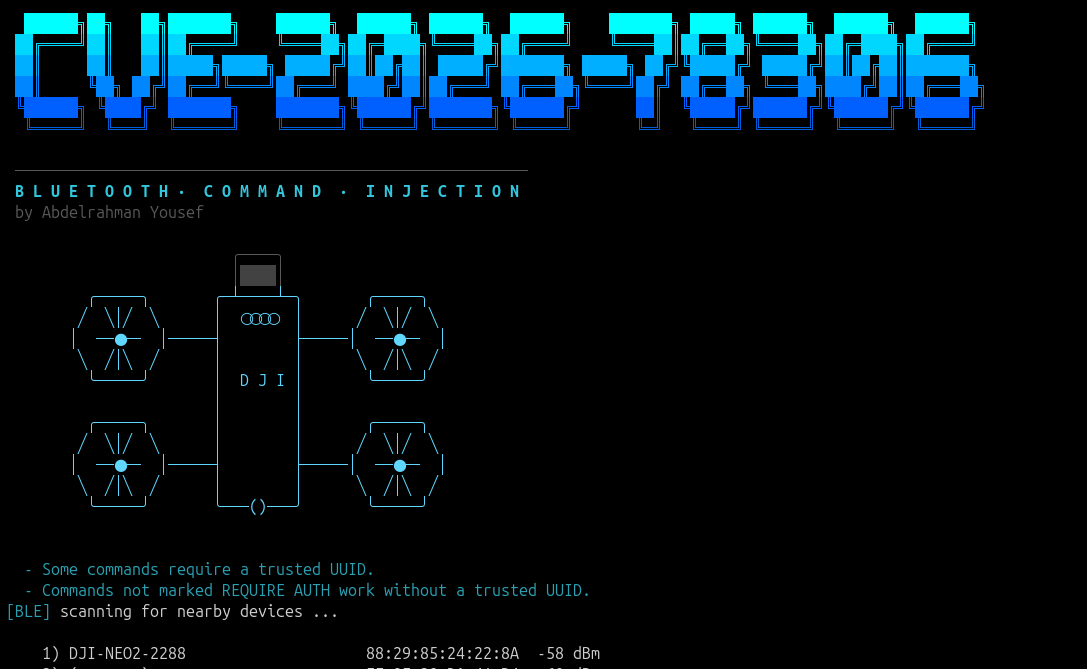 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
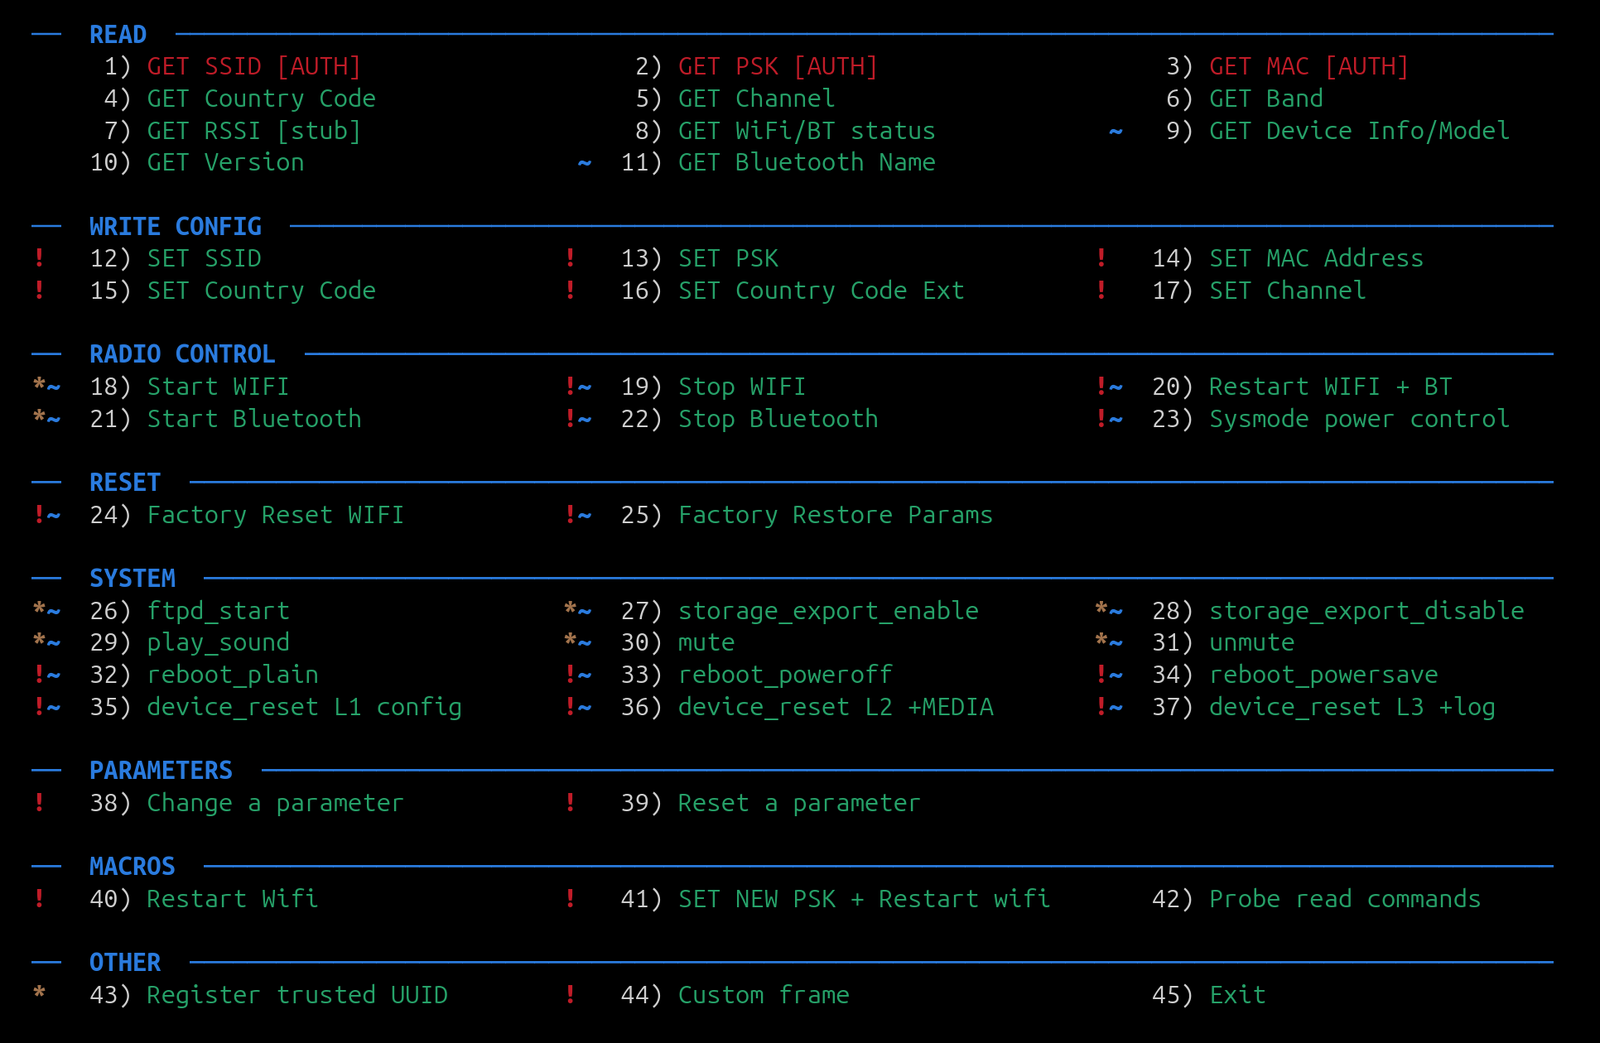 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…