

scapy
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
bluetooth-securitycryptographydata-exfiltration+23
12.7k
secdev/scapyPython-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 mr-xn/penetration_testing_poc
渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
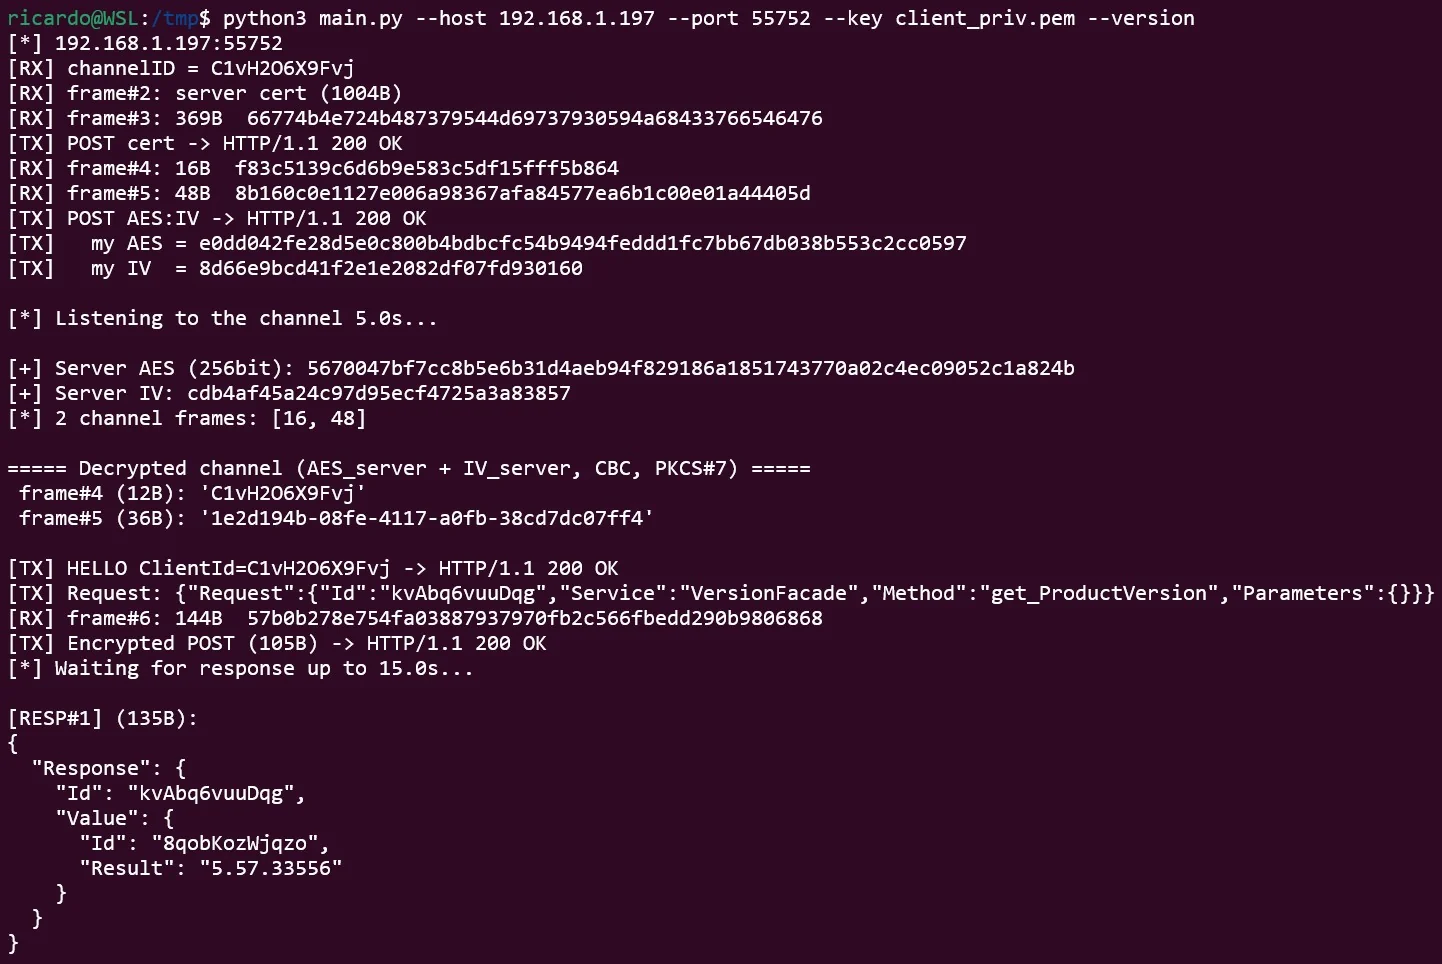 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 interceptsuite/interceptsuite
MITM proxy for TCP/TLS/DTLS/UDP traffic, with STARTTLS, IoT, Thick Client and more.
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 wantasticapp/wantasticcore
AIO Cloud Managment Server
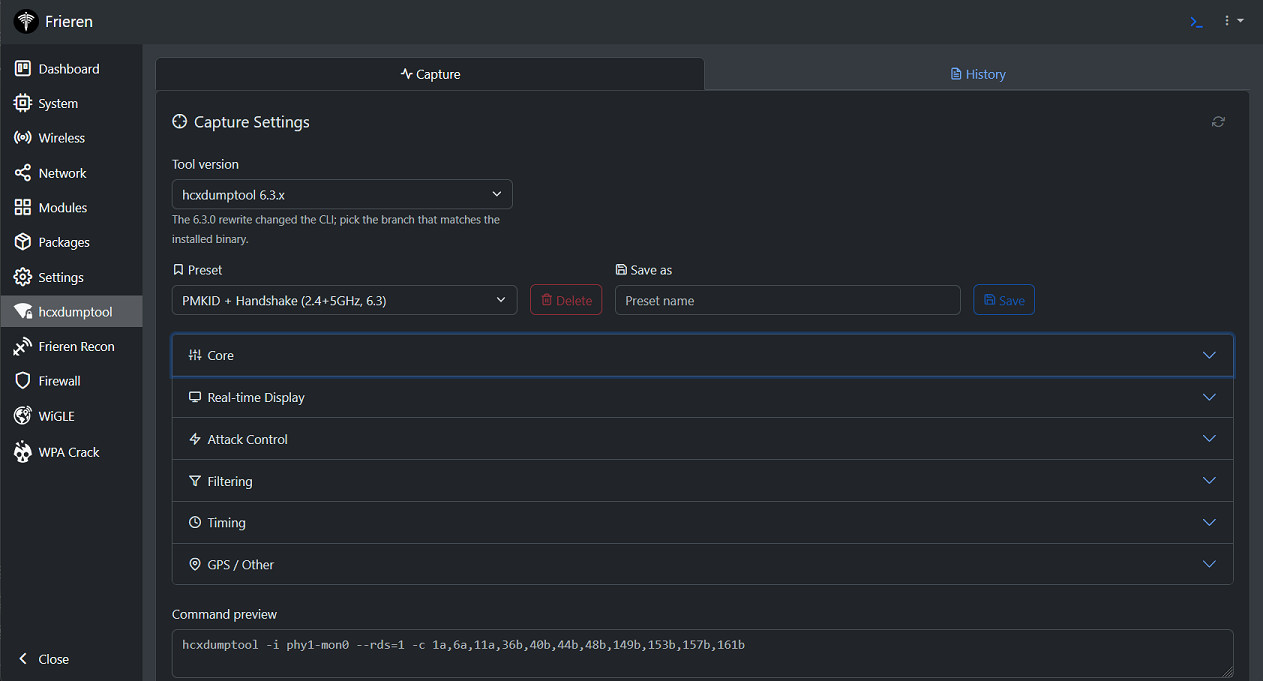 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…