 xjghnxhlh/hikihack
Hikvision CVE-2017-7921 hack


This repository documents, for educational and cybersecurity awareness purposes, the possible consequences of equipment vulnerable to CVE-2017-7921 (a public vulnerability disclosed in 2017, affecting certain firmware of Hikvision cameras/recorders that have not been updated).
⚠️ Legal notice
All demonstrations in this repository were carried out in an authorized test environment, for exclusively educational, research and awareness purposes. Before publication, all sensitive information (credentials, passwords, IP addresses, serial numbers, hostnames, etc.) was anonymized or blurred.
This repository is neither an exploitation guide nor an incitement to act against systems belonging to third parties. Any use must be part of a legal and ethical framework, and must have the explicit authorization of the owner of the equipment concerned.
CVE-2017-7921 is a public vulnerability affecting certain firmware of Hikvision equipment, referenced in the National Vulnerability Database (NVD). Equipment exposed on the Internet and not updated may potentially disclose sensitive information or allow unauthorized access to its administration interface.
This repository is not intended to detail the mechanics of exploitation, but to illustrate why this type of vulnerability is critical and how to protect against it (firmware updates, network segmentation, no direct exposure of administration interfaces on the Internet).
A detailed technical report accompanies this repository. It presents in particular:
➡️ Prevention report – CVE-2017-7921
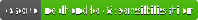
The screenshots below were taken in an authorized demonstration environment. All elements that could identify a real system (credentials, IPs, owner, etc.) were anonymized or blurred before publication. They are not a set of instructions, but a visual representation of the potential impact of equipment that has not been updated.
Example of the type of information that can be exposed when equipment affected by CVE-2017-7921 has not been properly updated or secured.
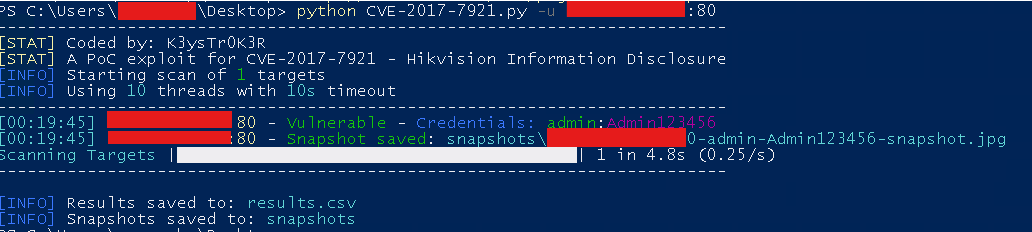
Administration interface of equipment, in an authorized demonstration environment. Objective: to illustrate the consequences of an unpatched vulnerability on equipment exposed without appropriate security measures.
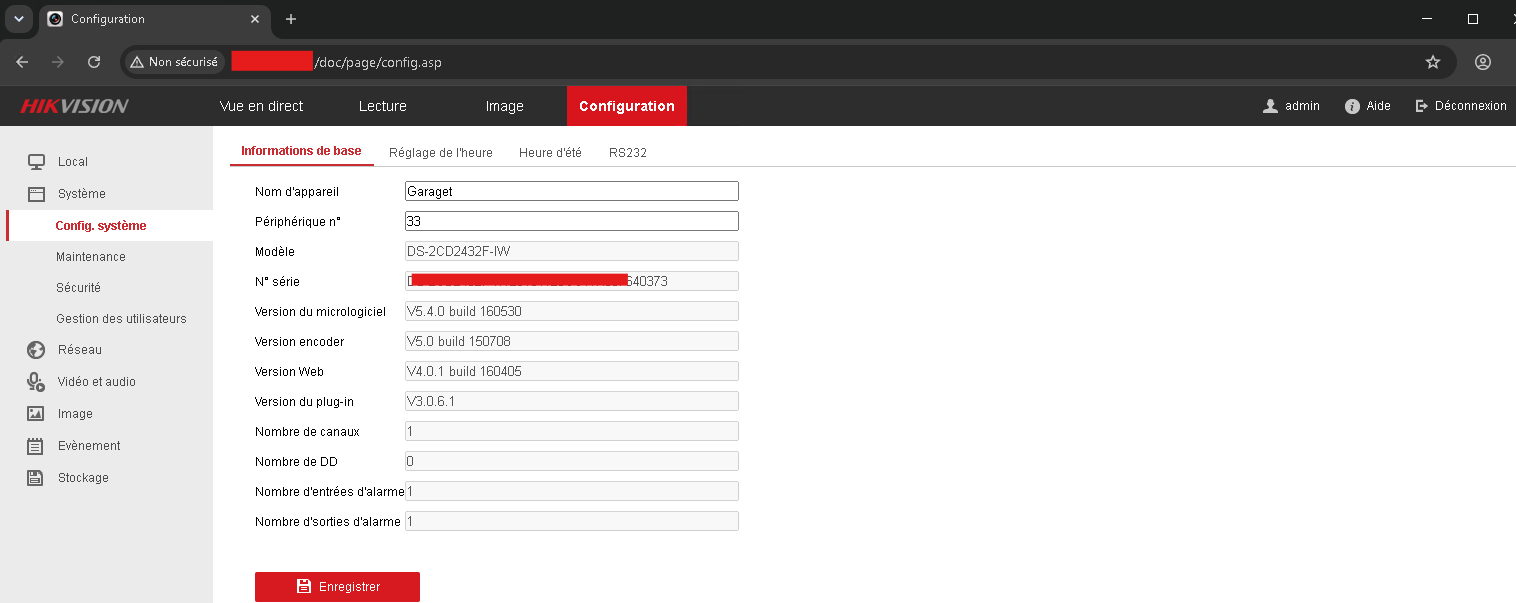
These resources aim to raise awareness among administrators, security researchers and students about the consequences of a vulnerability such as CVE-2017-7921 when it is not patched. They concretely illustrate:
Distributed under the MIT license.
