
p2pwn
 thebadinteger/p2pwn
Dahua cameras security scanner via P2P
exploitationhardware-iot-securityinformation-gathering+6
thebadinteger/p2pwnDahua cameras security scanner via P2P
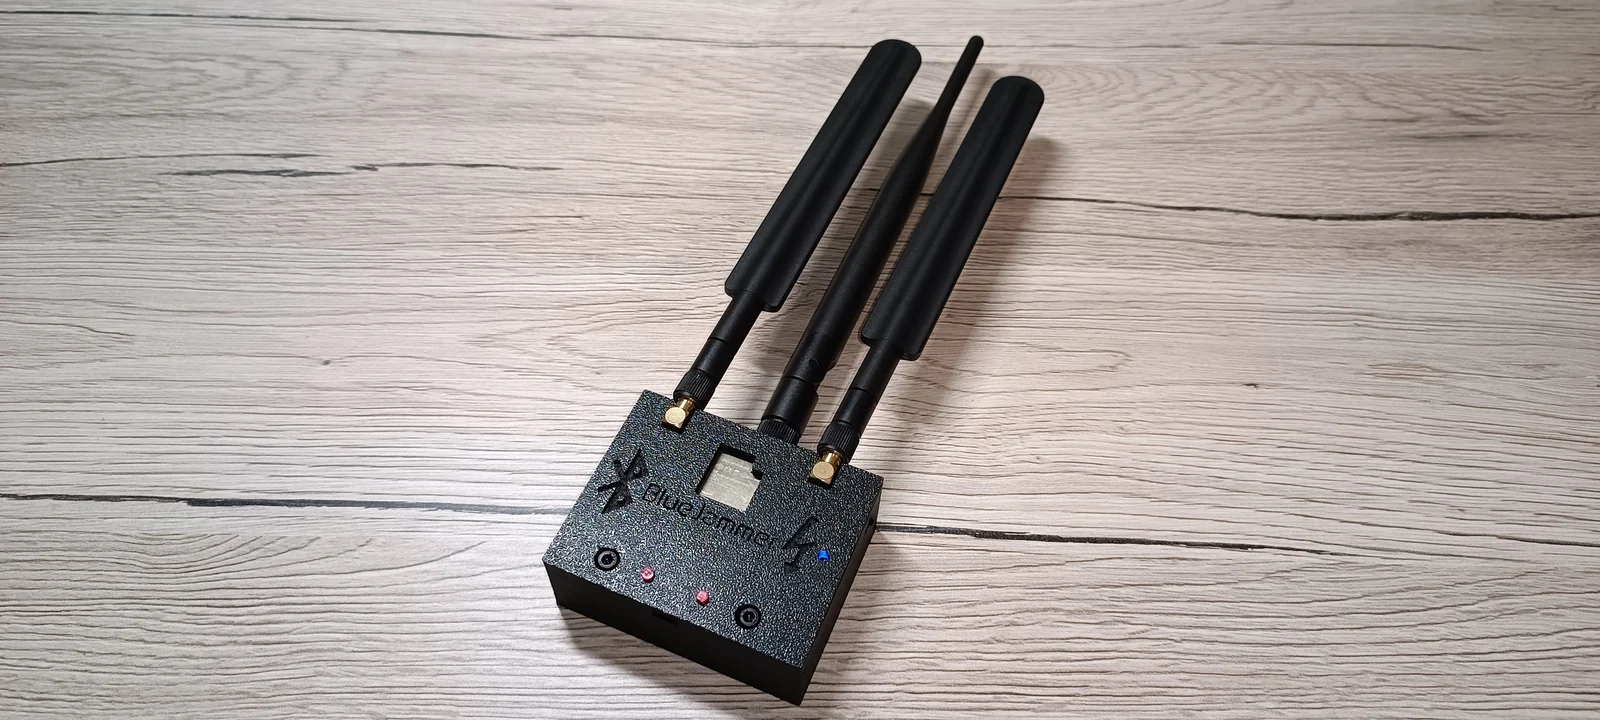 emenstanougat/esp32-bluejammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 poxsky/cve-2026-38577
Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
 hellkkid/cve-2026-56718
AJCloud AJY IPC Firmware Path Traversal via jdbhttpd
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 danish1162/cve-2026-2035703-x300
Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
 mbanyamer/cve-2026-32743-px4-autopilot-mavlinkloghandler-stack-buffer-overflow-dos-
A remote Denial of Service (DoS) exploit for PX4 Autopilot versions ≤1.17.0-rc2 via a stack‑based buffer overflow in the MavlinkLogHandler.
 mbanyamer/cve-2026-32707-px4-autopilot-tattu_can-stack-buffer-overflow-dos-
Proof-of-concept exploit for CVE-2026-32707, a stack buffer overflow in the PX4-Autopilot tattu_can driver, causing denial of service via crafted CAN…
 mbanyamer/cve-2026-26235-jung-smart-visu-server-unauthenticated-reboot-shutdown
Proof-of-concept exploit for CVE-2026-26235, an unauthenticated denial-of-service vulnerability in JUNG Smart Visu Server <=1.1.1050, allowing remote…
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 szym0n13k/cve-2025-55971-blind-unauthenticated-ssrf-in-tcl-smart-tv-upnp-dlna-avtransport
TCL 65C655 Smart TV, running firmware version V8-R75PT01-LF1V269.001116 (Android TV, Kernel 5.4.242+), is vulnerable to a blind, unauthenticated…
 totekuh/cve-2026-75616
Proof-of-concept exploit for authenticated OS command injection in TP-Link Archer C20 v6 web management interface, executing root commands via BPA…