Glass-Cage-iOS18-CVE-2025-24085-CVE-2025-24201

Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…

Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…

Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…

A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.

OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar

Write-up and proof of concepts for CVE-2021-30862, 1-click RCE bug in iOS iTunes U

Proof-of-concept exploit for a cross-site scripting (XSS) vulnerability in Microsoft Outlook for iOS, enabling email-based spoofing attacks and…

Extraction of iMessage Data via XSS

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…

webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…

CVE-2016-4657 web-kit vulnerability for ios 9.3, nintendo switch browser vulnerability

Proof-of-concept exploit for CVE-2024-25733 demonstrating address bar spoofing in ARC Browser on iOS/iPadOS using JavaScript-based navigation…

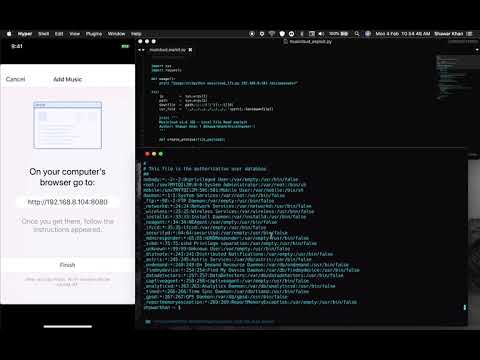
[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application

CTT-Enhanced iOS Safari Exploit (based on CVE-2025-43529)

Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…

Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…

Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…