CVE-2025-70600---Urve-Smart-Office---Stored-XSS-in-iOS-App

Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…

Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…

Technical analysis and exploit demonstration of CVE-2022-32898, a kernel memory corruption vulnerability in Apple Neural Engine driver, with detailed…

Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

open-source jailbreaking tool for many iOS devices

The OWASP MASVS (Mobile Application Security Verification Standard) is the industry standard for mobile app security.

kfd, short for kernel file descriptor, is a project to read and write kernel memory on Apple devices.

a Ghidra framework for iOS kernelcache reverse engineering

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.

This uses CVE-2025-43407 as exploit and still testing working not gauranteed.

Analysis of CVE-2025-43529 (WebKit UAF) + CVE-2025-14174 (ANGLE OOB) exploit chain - iOS Safari

PoC Exploit iOS 12 to iOS 12.1 (CVE-2018-4431)

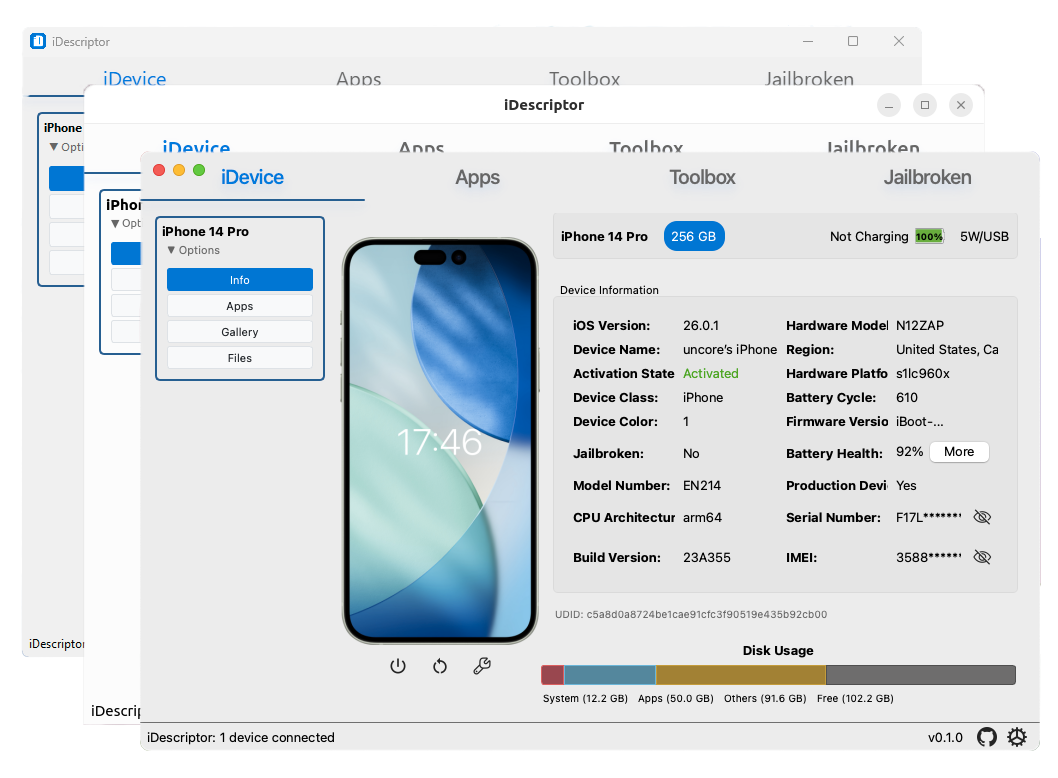
privacy-first, open-source and free idevice management tool written in Rust and Qt

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…

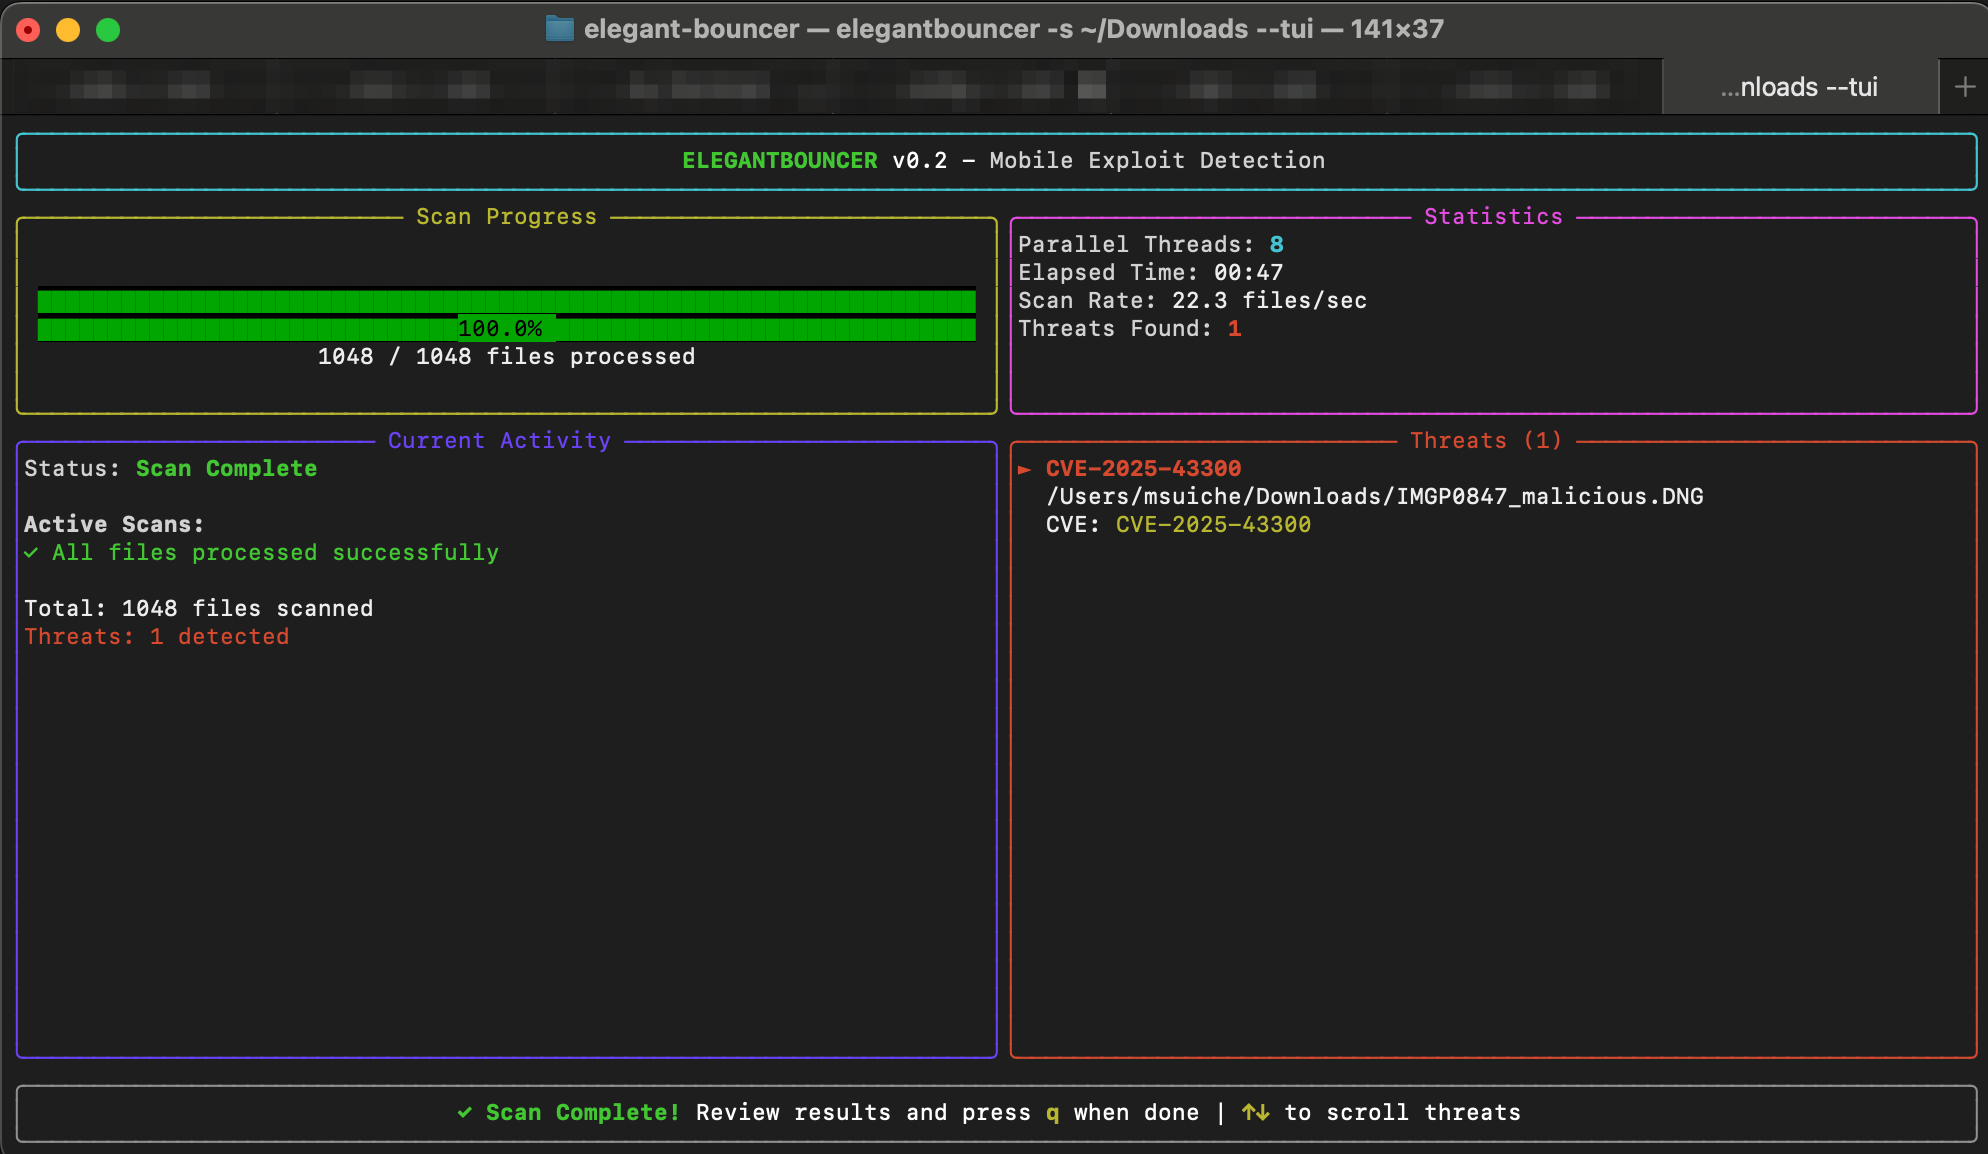
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.

This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices

Bash script to extract data from a "chekcra1ned" iOS device

Collection of materials relating to FORCEDENTRY