hi_my_name_is_keyboard

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

Analysis of public exploits or my 1day exploits

Unofficial frida extension for VSCode

Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…

Linux Distro for Mobile Security, Malware Analysis, and Forensics

Binary & scripts associated with "The Poor Man's Obfuscator" presentation

A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…

Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

Glass - a fast and free IDA Pro alternative

Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…

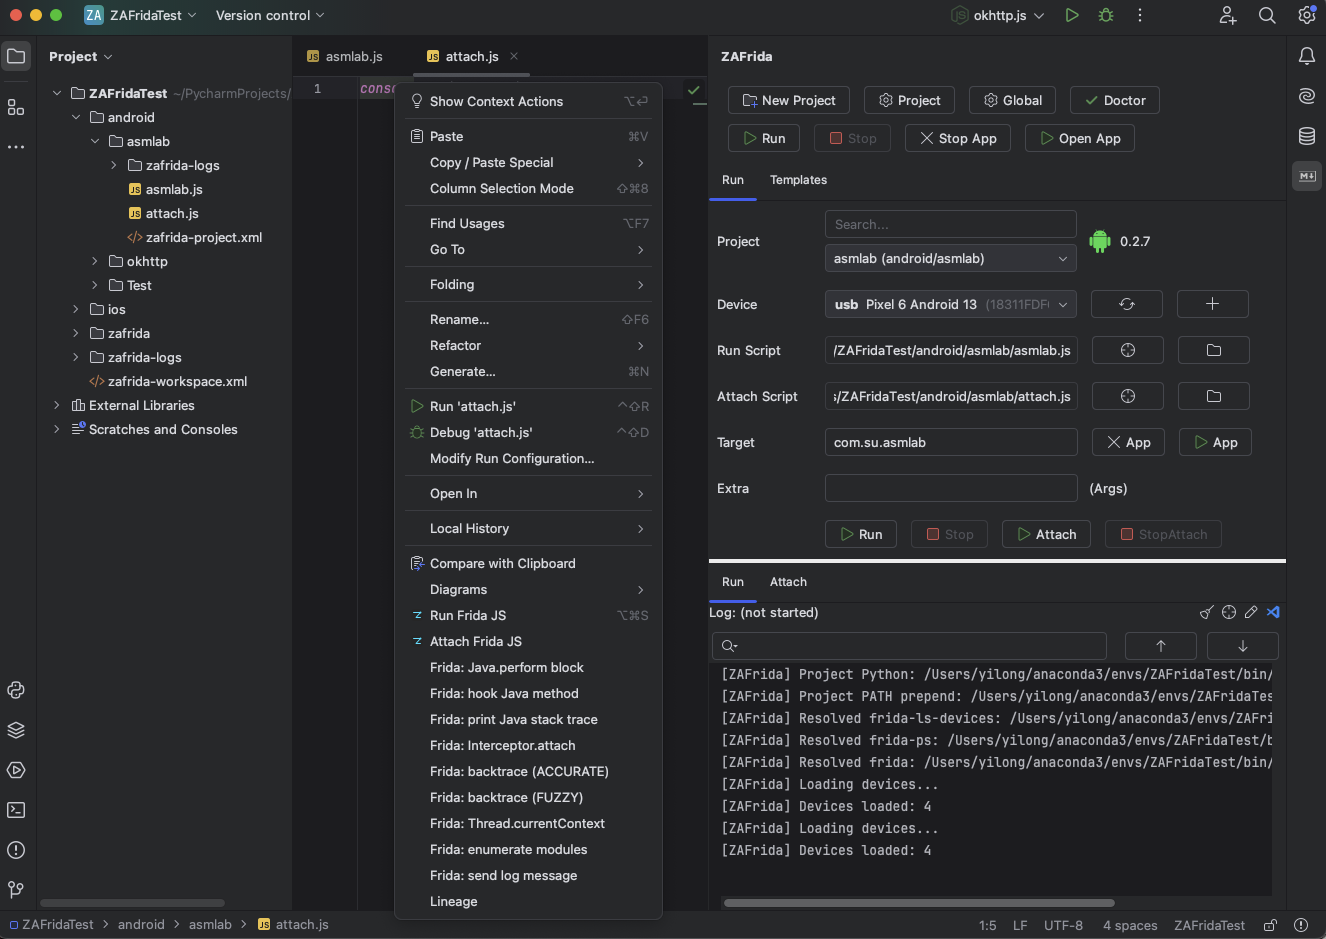
A Frida UI tool window inside PyCharm / JetBrains IDEs.

Static analysis tool for Android/iOS apps focusing on security issues outside the source code

Non-decompiling iOS/Android app vulnerability scanner (DC25 demo lab, CB17)

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

Broadpwn bug (CVE-2017-9417)

Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…

A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…