grapefruit
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
android-securitybinary-analysisdynamic-code-analysis+5
1.4k
chichou/grapefruitOpen-source mobile security testing suite for iOS and Android. Previously Passionfruit
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 stationedk-06/darksword_analysis
Static analysis of the DarkSword iOS WebKit exploit chain — delivery, staging, and CVE breakdown (CVE-2025-31277, CVE-2025-43529)
 chichou/vscode-frida
Unofficial frida extension for VSCode
 rohitberiwala/cve-2024-23222-coruna-exploit-kit-deobfuscated
Comprehensive deobfuscated research of the Coruna iOS exploit kit targeting CVE-2024-23222. Analysis of WebKit Type Confusion, PAC Bypass, and…
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 shawarkhanethicalhacker/cve-2019-8389
[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application
 gabrielg/cve-2014-1266-poc
Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…
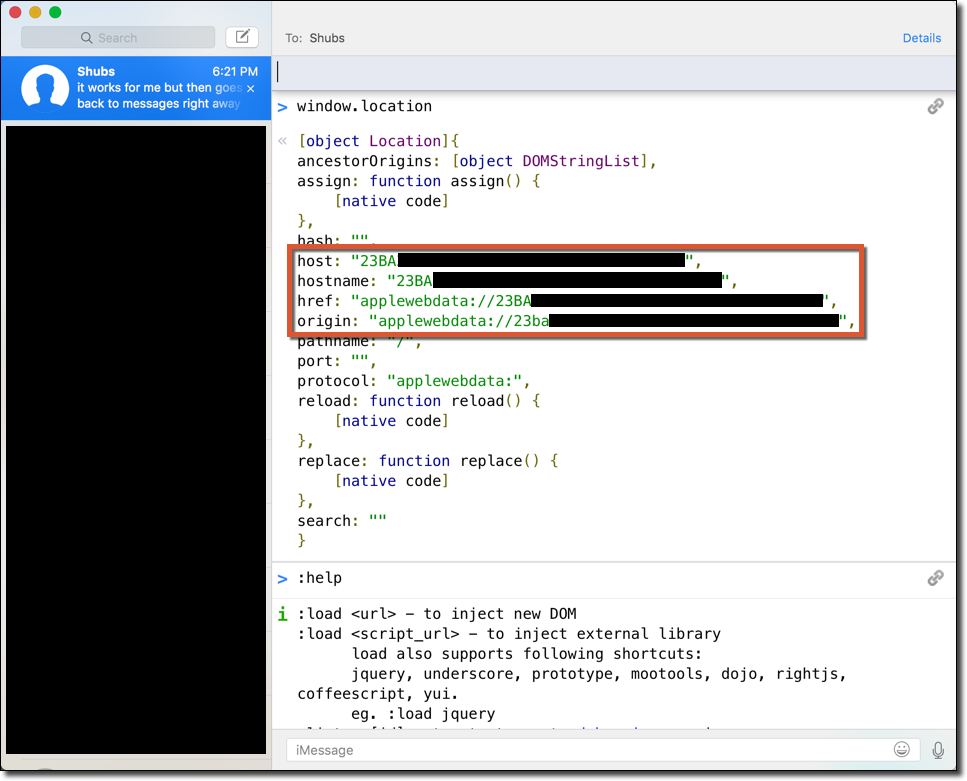 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 gpheheise/cve-2025-70600---urve-smart-office---stored-xss-in-ios-app
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…
 3h6-1/cve-2021-30862
Write-up and proof of concepts for CVE-2021-30862, 1-click RCE bug in iOS iTunes U
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…