objection
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
android-securitydynamic-analysis-sandboxingexploitation+9
9.3k
sensepost/objectionFrida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 theos/sdks
Patched sdks that include private framework tbds
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
 0neday/multi_path
CVE-2018-4241: XNU kernel heap overflow due to bad bounds checking in MPTCP for iOS 11 - 11.3.1released by Ian Beer
 georgiaw/smartphone-pentest-framework
Repository for the Smartphone Pentest Framework (SPF)
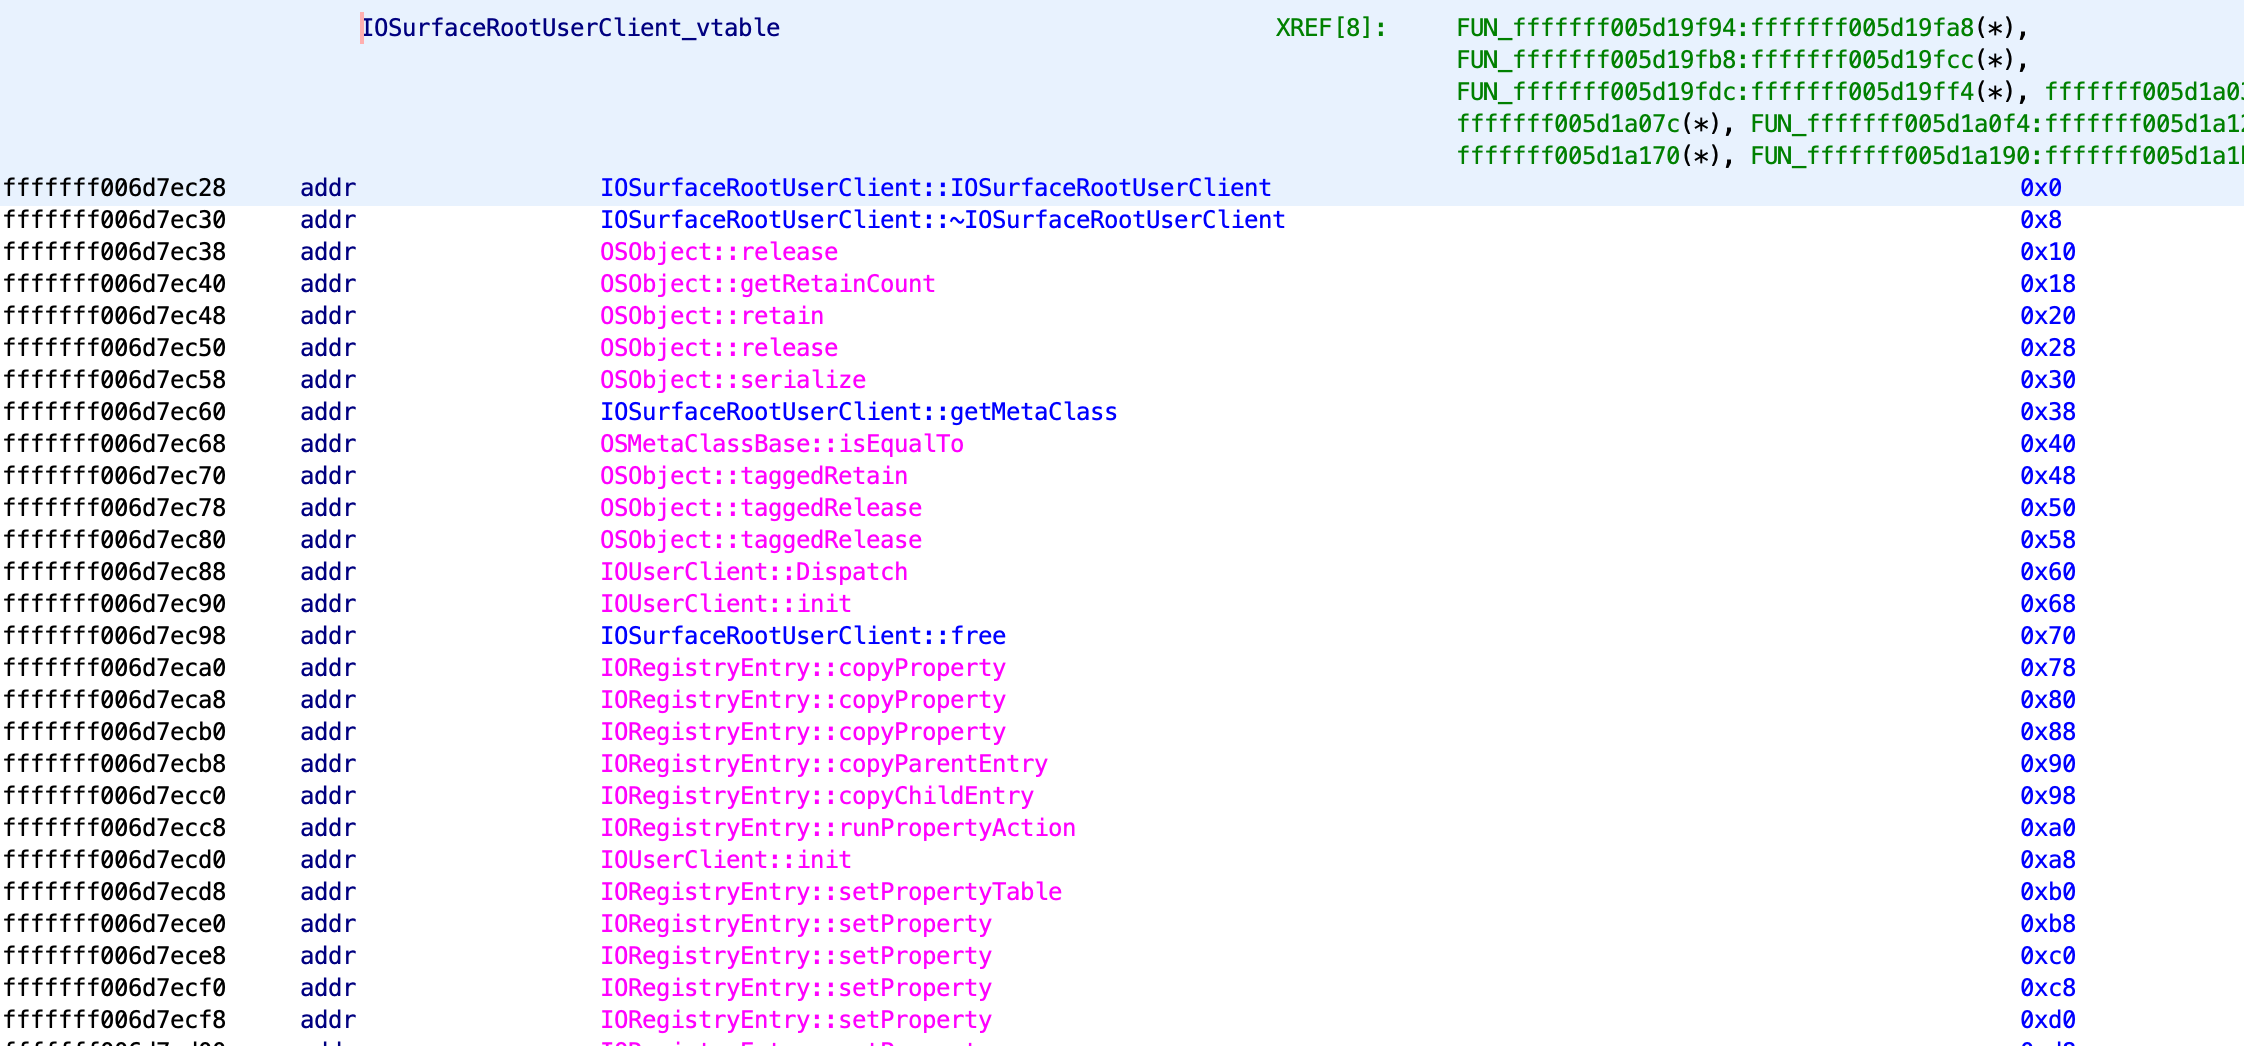 0x36/ghidra_kernelcache
a Ghidra framework for iOS kernelcache reverse engineering
 hunters-sec/cve-2025-31200
IOS audio buffer overflow CVE-2025-31200 POC
 genericcoding/pois0nsword
A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
 techupdate24/capacitor-flaw-cve-2026-103922
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 ox1111/jailbreak-ios12
OS 12.0 & 12.1.2 - Jailbreak with CVE-2019-6225