
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
Reversecore_MCP preview

Reversecore_MCP

GitHubsjkim1127/reversecore_mcp

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

binary-analysisdigital-forensicsdynamic-analysis-sandboxing+7
202
2 days ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

command-and-controlcryptographydigital-forensics+7
43 days ago
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

command-and-controldata-exfiltrationdigital-forensics+7
1 day ago
labs-releases preview

labs-releases

GitHubelastic/labs-releases

Elastic Security Labs releases

curated-resourcesioc-managementmalware-analysis+2
913 days ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

android-securitydigital-forensicsdisk-forensics+7
13.1k8h 1m ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k6 days ago
malwoverview preview

malwoverview

GitHubalexandreborges/malwoverview

Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…

android-securityinformation-gatheringioc-management+4
4.1k1 month ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k17 days ago
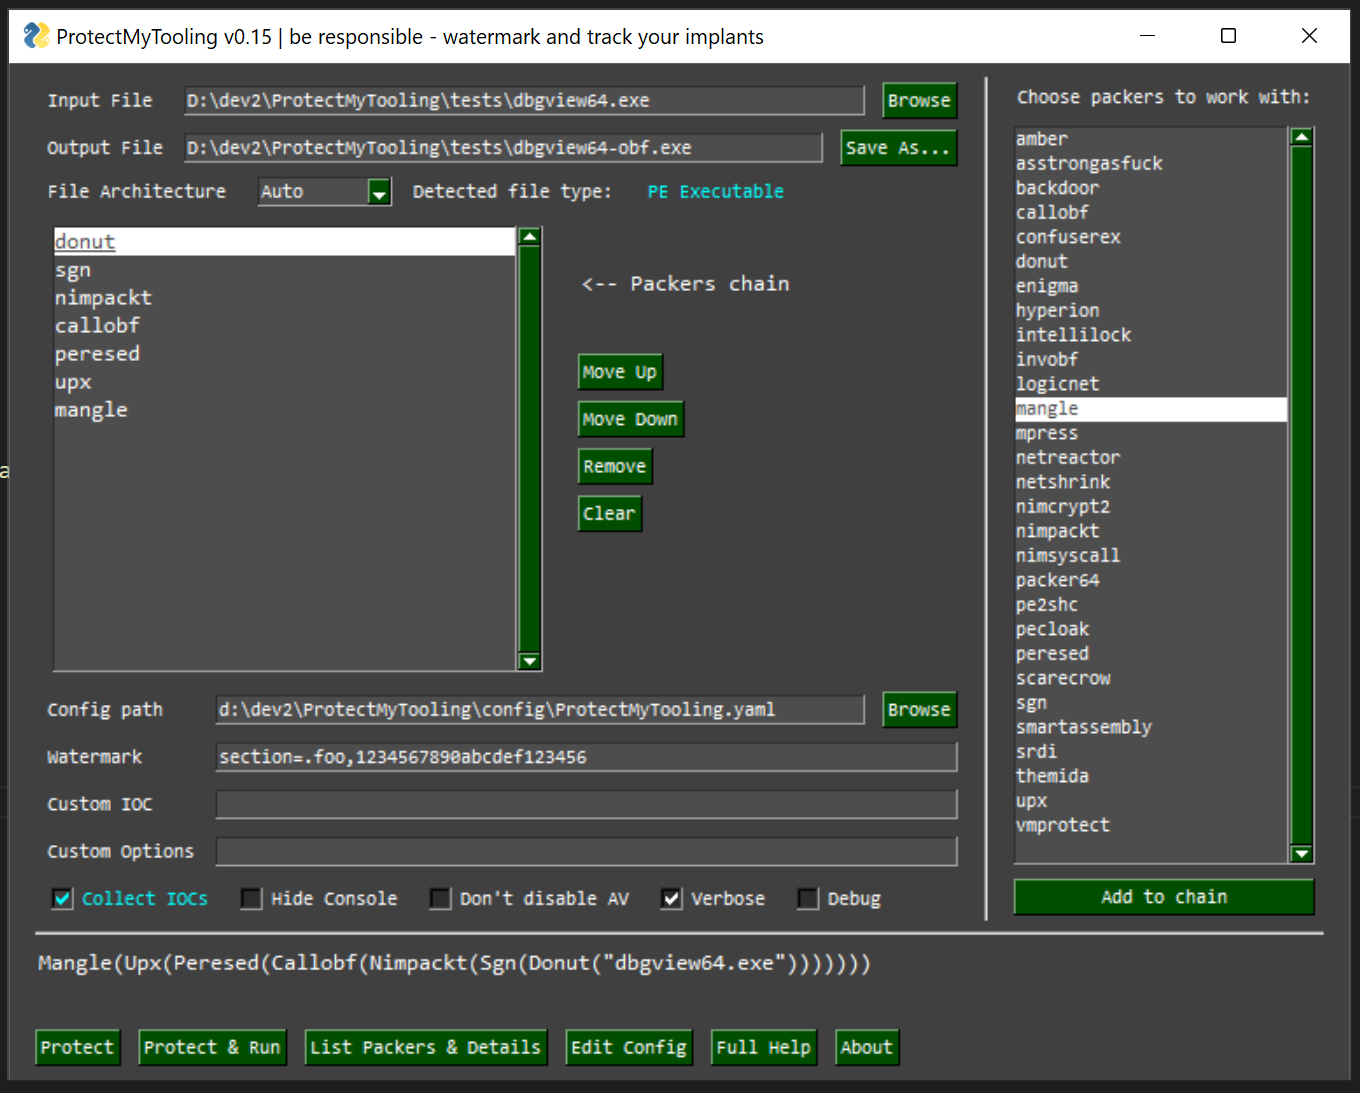
ProtectMyTooling preview

ProtectMyTooling

GitHubmgeeky/protectmytooling

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

binary-analysisexploit-frameworksioc-management+5
1.1k11 months ago
SPiCa preview

SPiCa

GitHub0xkirisame/spica

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…

anomaly-detectionbinary-analysisdefensive-tools+7
1042 months ago
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.

binary-analysiscurated-resourcesdynamic-analysis-sandboxing+8
838 months ago
iocx preview

iocx

GitHubiocx-dev/iocx

An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…

binary-analysisdevsecopsforensics+6
295 days ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…

binary-analysisdebuggersdigital-forensics+9
451 year ago
Android-Projector-C2-Malware preview

Android-Projector-C2-Malware

GitHubkavan00/android-projector-c2-malware

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

android-securitycommand-and-controldigital-forensics+9
185 months ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

binary-analysiscontainer-escapedata-recovery+7
1026 days ago
Veto preview

Veto

GitHubprofessorquantumuniverse/veto

Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…

android-securitydynamic-analysis-sandboxingforensics+8
138 days ago
AgentTesla-Config-Extractor preview

AgentTesla-Config-Extractor

GitHubembee-research/agenttesla-config-extractor

Config extractor for AgentTesla - Discord/Telegram Variant

binary-analysiscommand-and-controlioc-management+4
32 years ago