Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
124 results
CVE-2025-57819-ioc-check preview
Archived

CVE-2025-57819-ioc-check

GitHubsucuri-labs/cve-2025-57819-ioc-check

This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
digital-forensicsforensicsincident-response+3
1 year ago
CTWall preview

CTWall

GitHubcybergabisoft/ctwall

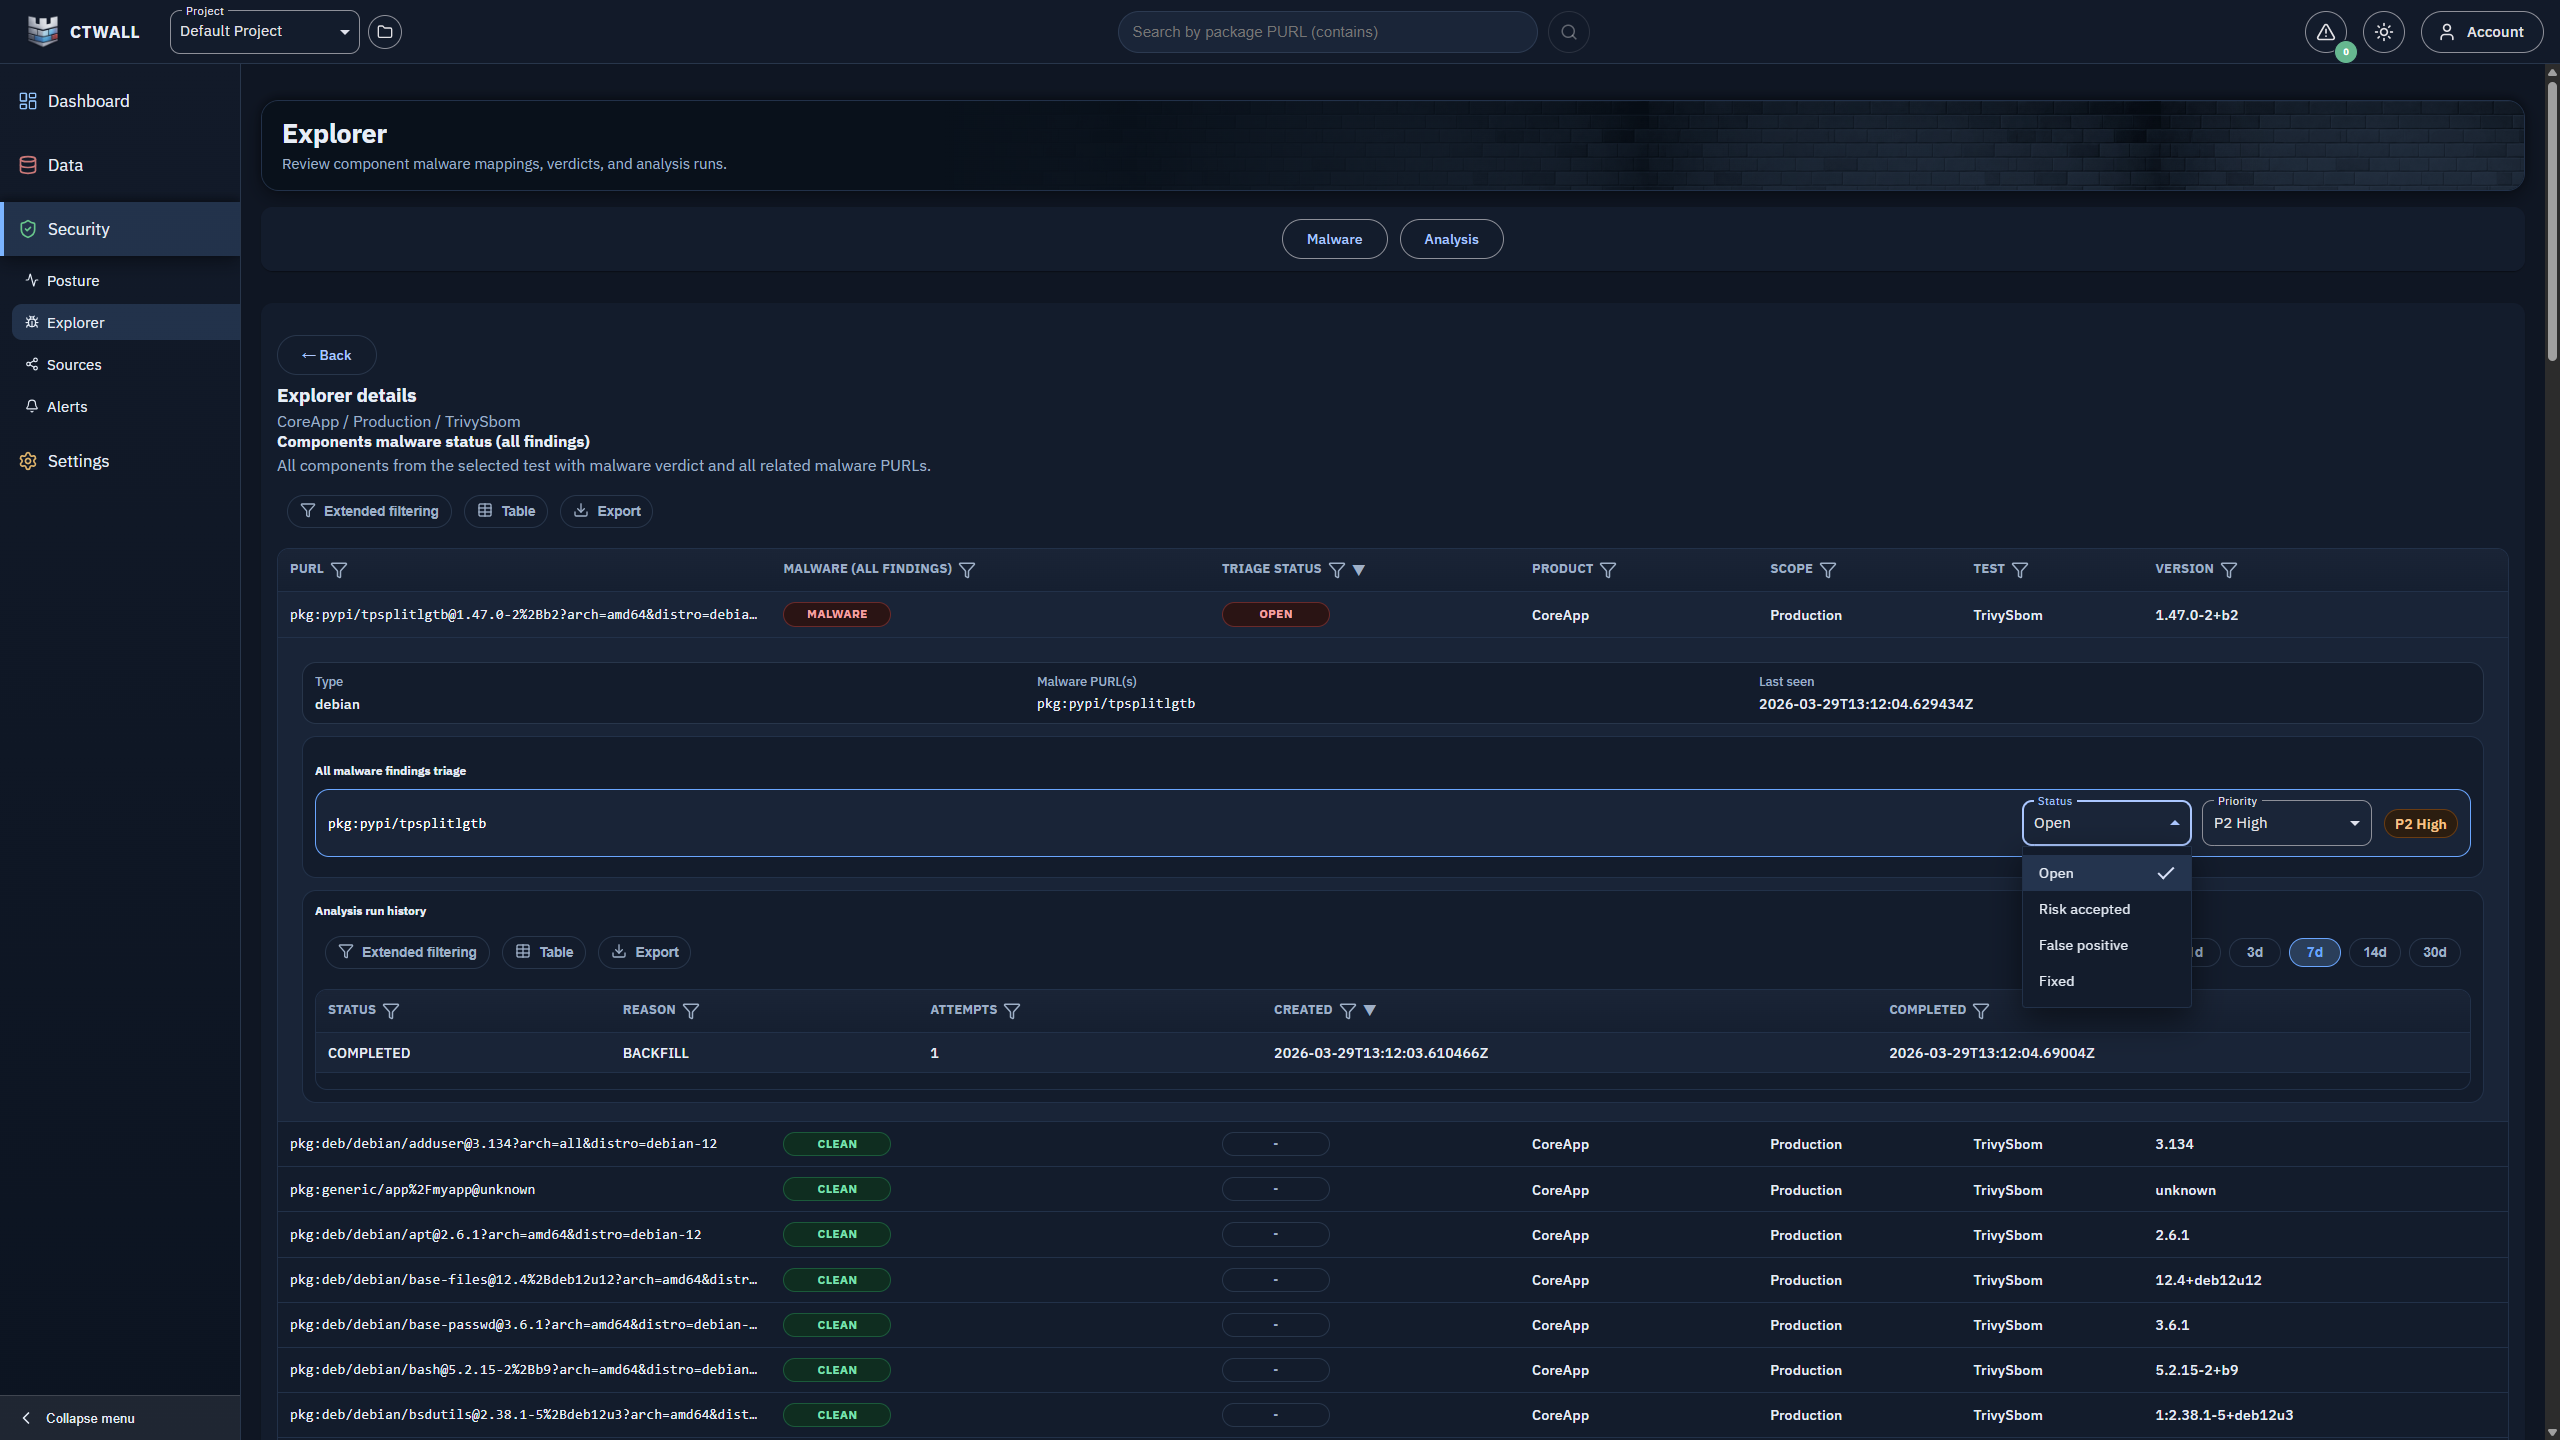
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
cloud-securitycontainer-securitydevsecops+6
13 months ago
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

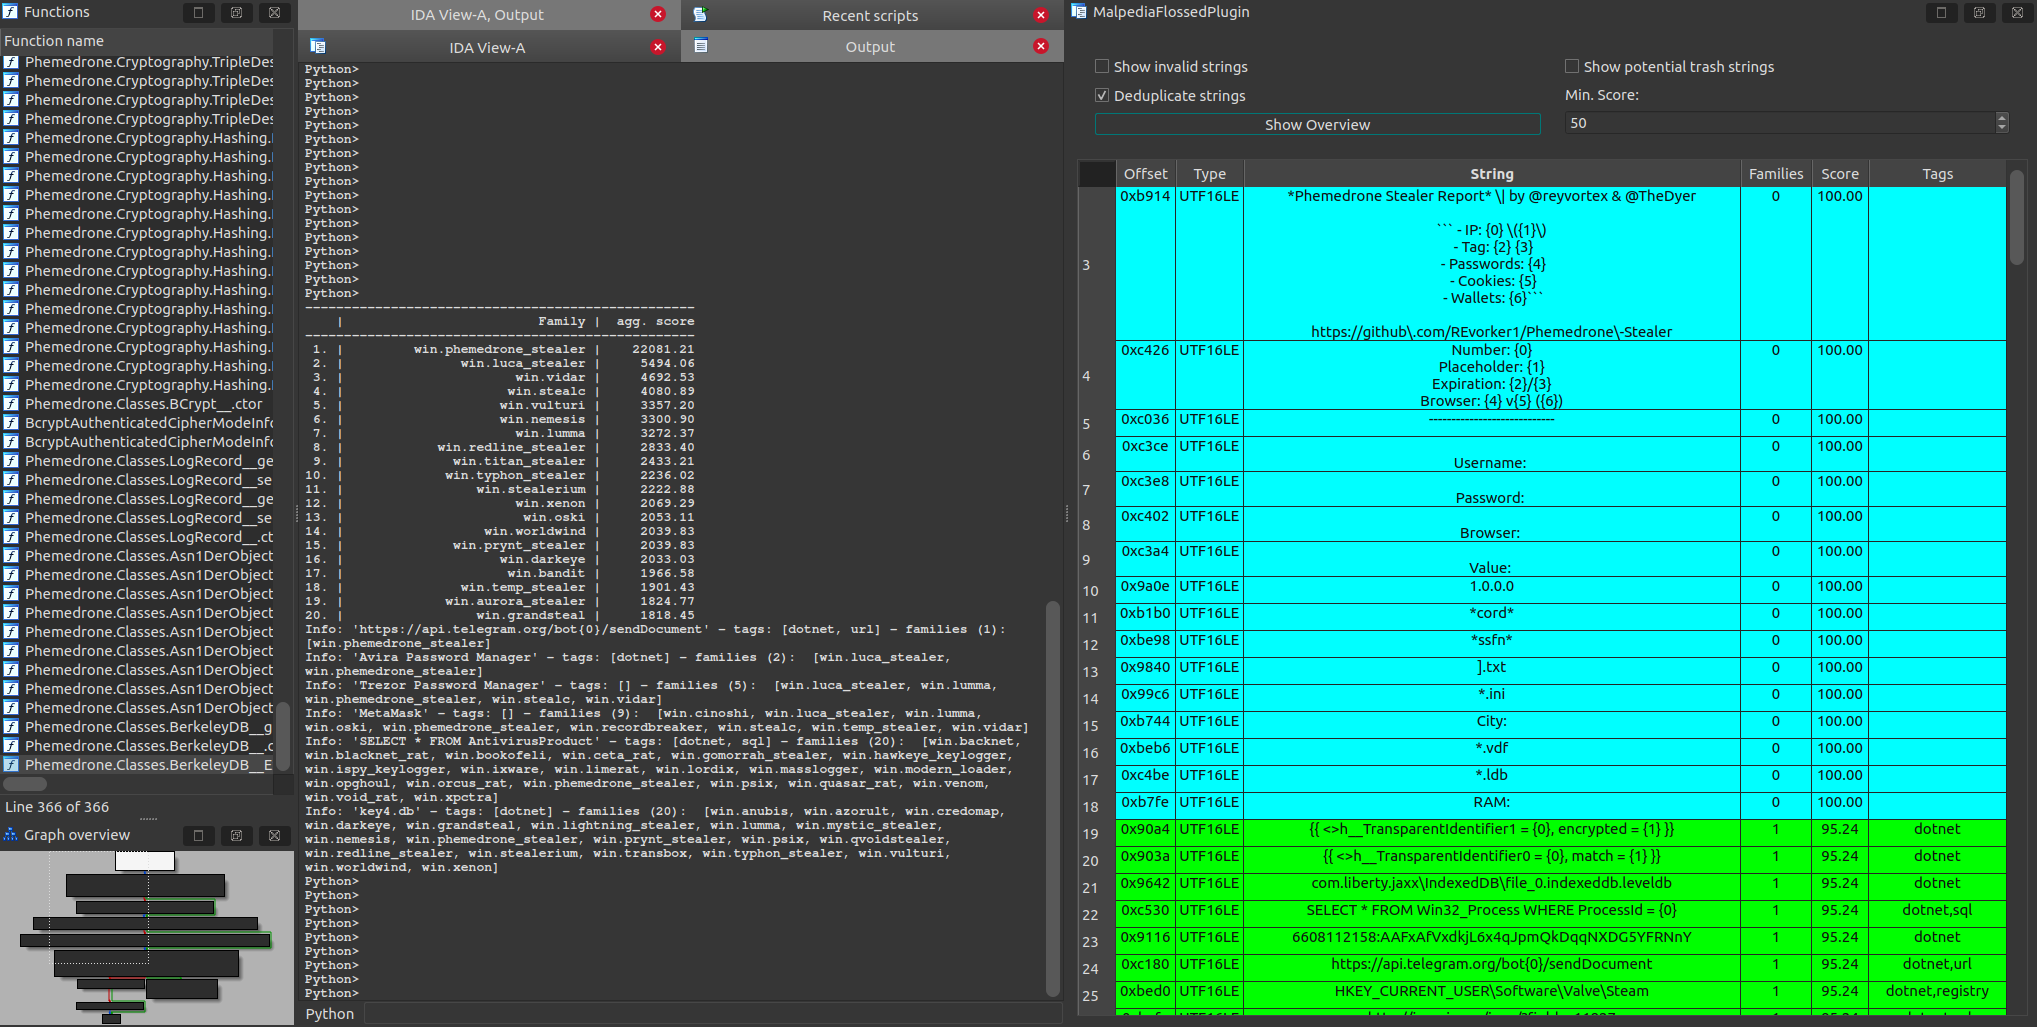
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
binary-analysiscurated-resourcesdynamic-analysis-sandboxing+8
849 months ago
hexora preview

hexora

GitHubrushter/hexora

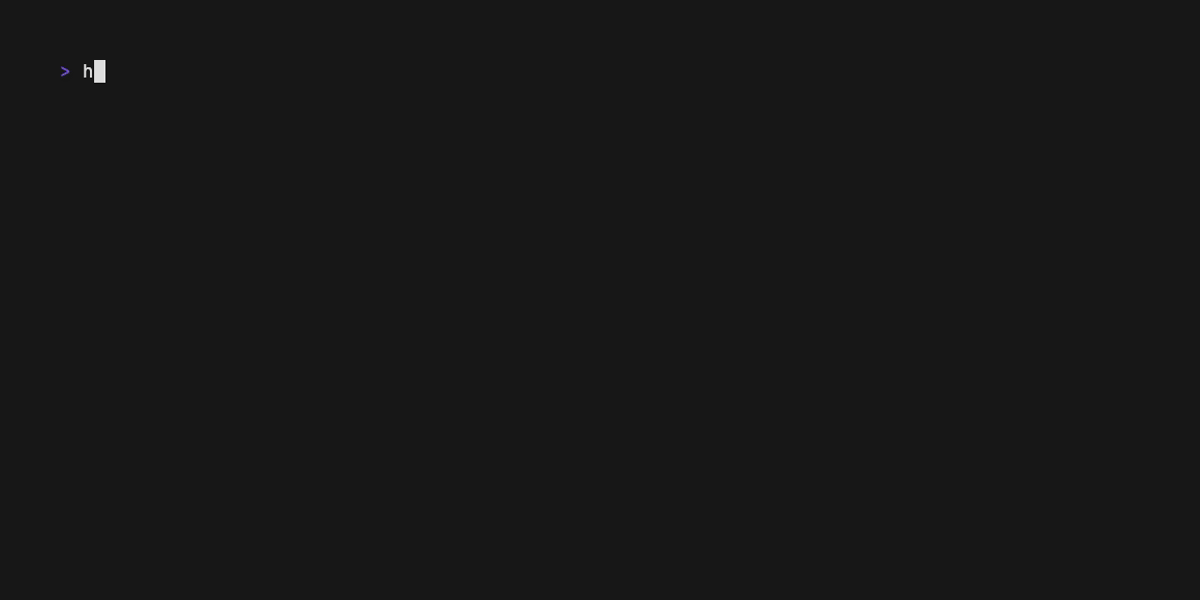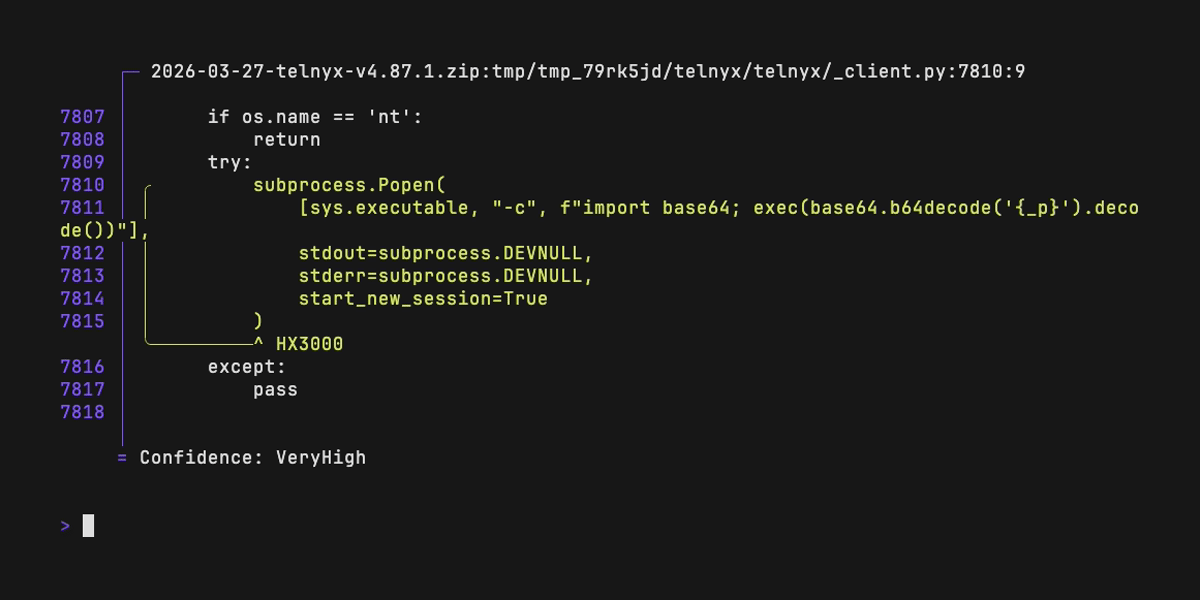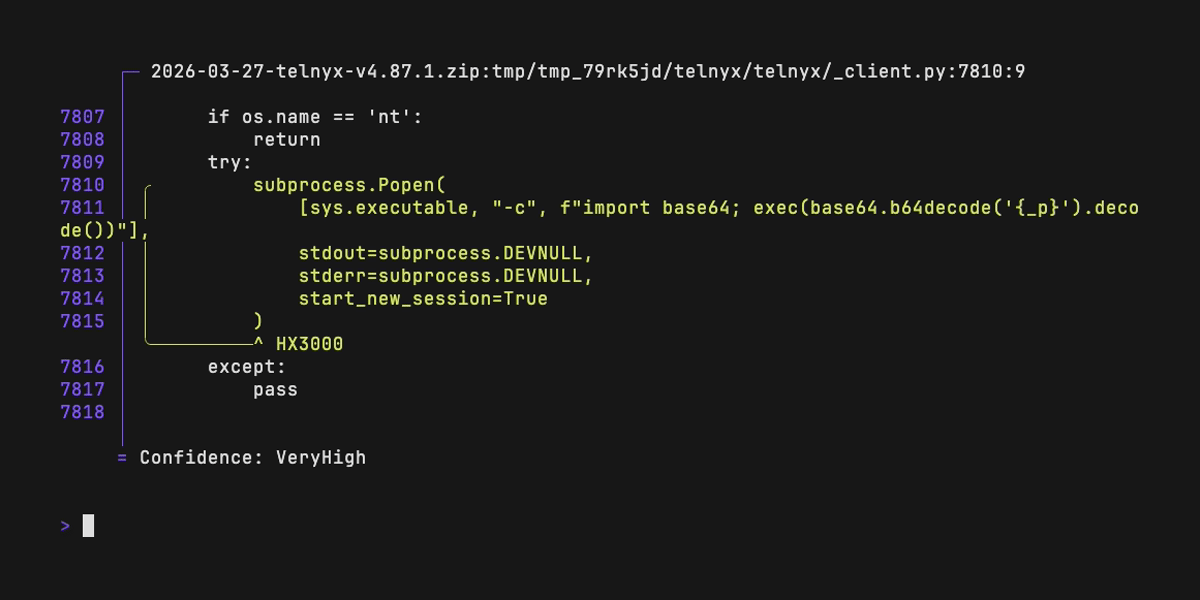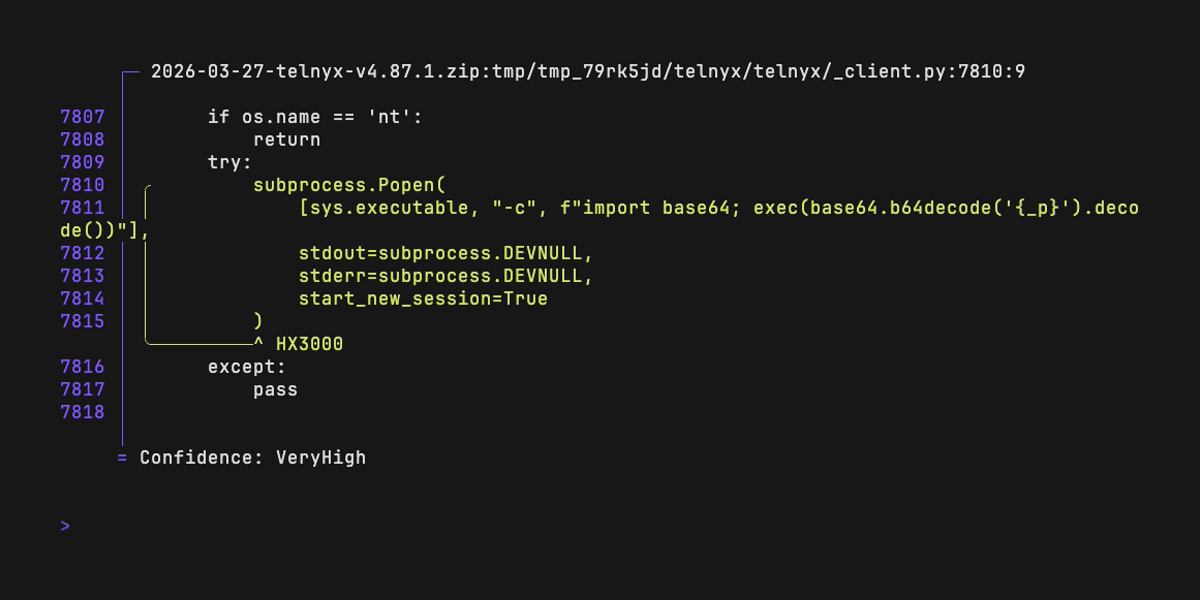
Static analysis of malicious Python code
code-analysisioc-managementmachine-learning+4
1731 month ago
hassh preview
Archived

hassh

GitHubsalesforce/hassh

HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…

anomaly-detectionforensicsincident-response+5
5531 year ago
pulse-meter preview

pulse-meter

GitHubrxwx/pulse-meter

Parses the System Snapshot from an Ivanti Connect Secure applicance to identify possible IOCs related to CVE-2023-46805, CVE-2024-21887 and…

exploitationforensicsincident-response+3
11 year ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.2k6 days ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
RansomCoinPublic preview

RansomCoinPublic

GitHubconcinnity-risks/ransomcoinpublic

A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
cryptographydigital-forensicsforensics+3
565 years ago
Threat-Intelligence-Hunter preview

Threat-Intelligence-Hunter

GitHubabhinavbom/threat-intelligence-hunter

TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…

information-gatheringioc-managementosint+1
1568 years ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k11h 50m ago
OreNPMGuard preview

OreNPMGuard

GitHubrapticore/orenpmguard

Defense Against the Shai-Hulud Supply Chain Attack
code-analysisdevsecopseducation+6
139 months ago
box-js preview

box-js

GitHubcapacitorset/box-js

A tool for studying JavaScript malware.

dynamic-analysis-sandboxingforensicsioc-management+1
6733 months ago
Sandbox_Scryer preview

Sandbox_Scryer

GitHubpayloadsecurity/sandbox_scryer

Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
dynamic-analysis-sandboxingeducationinformation-gathering+6
2284 years ago
Kalim_Backdoor preview

Kalim_Backdoor

GitHubsalaheldinfikri/kalim_backdoor

Kalim backdooe Malware Report

command-and-controldigital-forensicsdynamic-analysis-sandboxing+6
46 months ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k10h 12m ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k3 days ago
Onapsis-Mandiant-CVE-2025-31324-Vuln-Compromise-Assessment preview

Onapsis-Mandiant-CVE-2025-31324-Vuln-Compromise-Assessment

GitHubonapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment

CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool

cloud-securityforensicsincident-response+4
91 year ago
Previous1234567Next
