
box-js
 capacitorset/box-js
A tool for studying JavaScript malware.
dynamic-analysis-sandboxingforensicsioc-management+1
capacitorset/box-jsA tool for studying JavaScript malware.
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
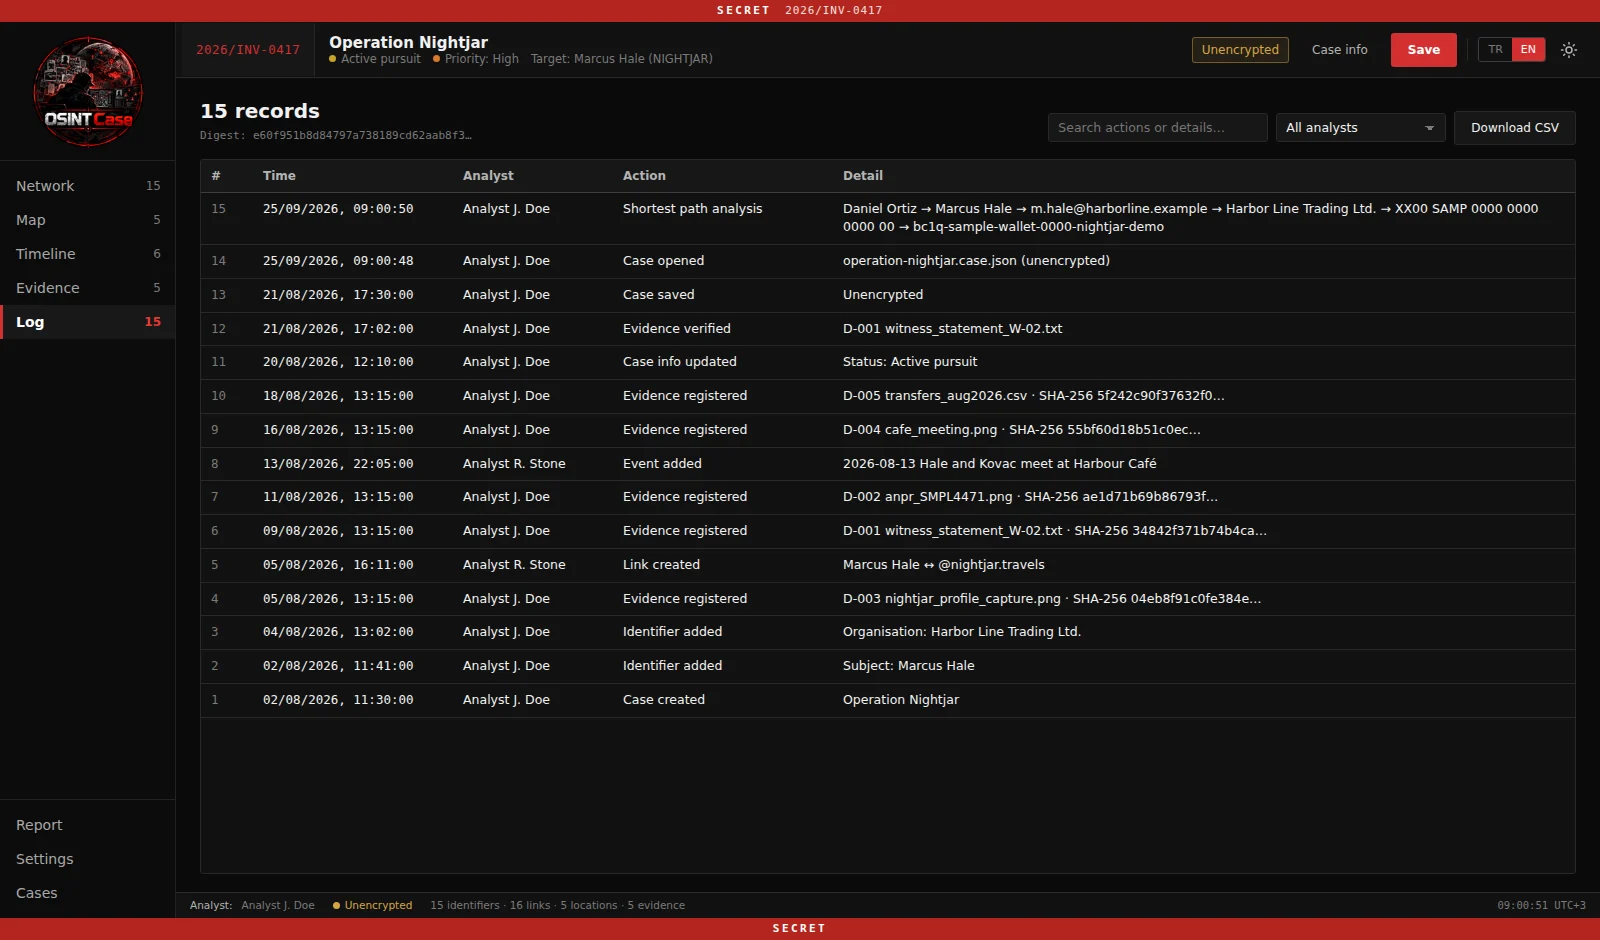 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
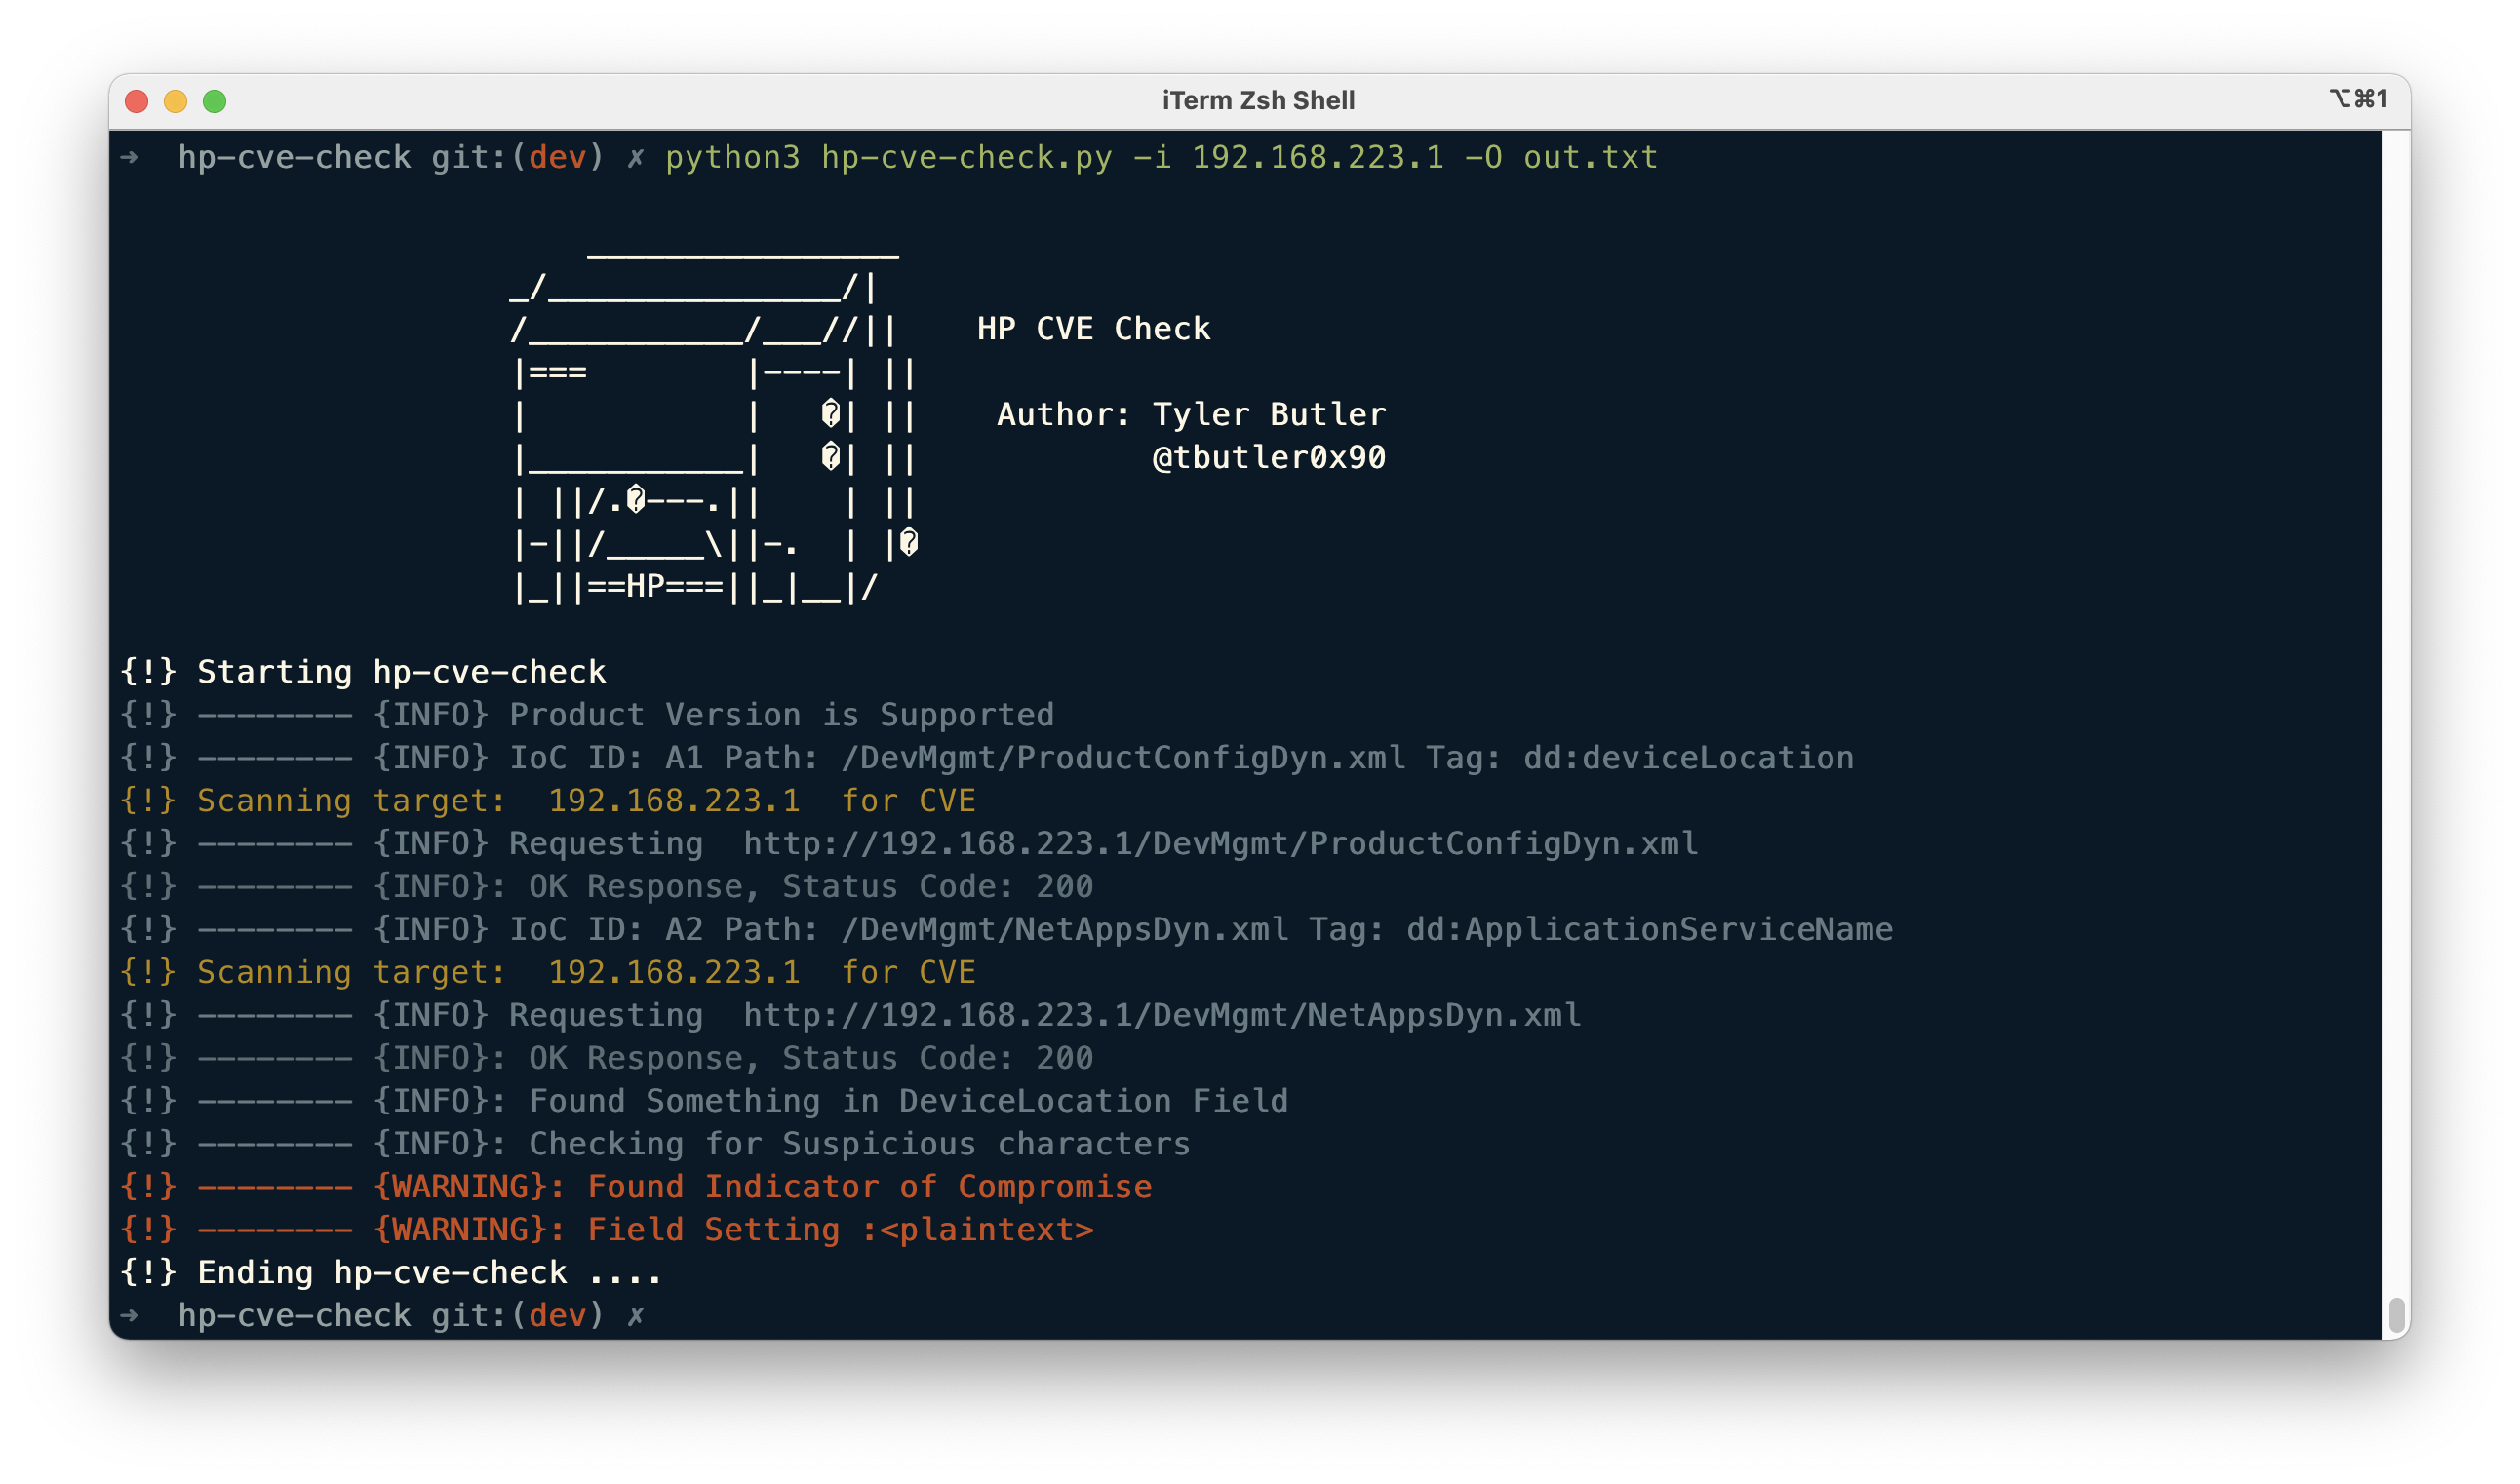 tcbutler320/cve-2021-3441-check
CVE-2021-3441 CVE Check is a python script to search targets for indicators of compromise to CVE-2021-3441
 cyberdudebivash/cyberdudebivash-cisco-asyncos-cve-2025-20393-scanner
This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 onapsis/cve-2020-6287_recon-scanner
Black-box vulnerability scanner and indicator-of-compromise analyzer for CVE-2020-6287 (RECON) in SAP NetWeaver Java applications, enabling rapid…
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…