
memory-forensic
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
binary-analysiscontainer-escapedata-recovery+7
10
securityronin/memory-forensicWalk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
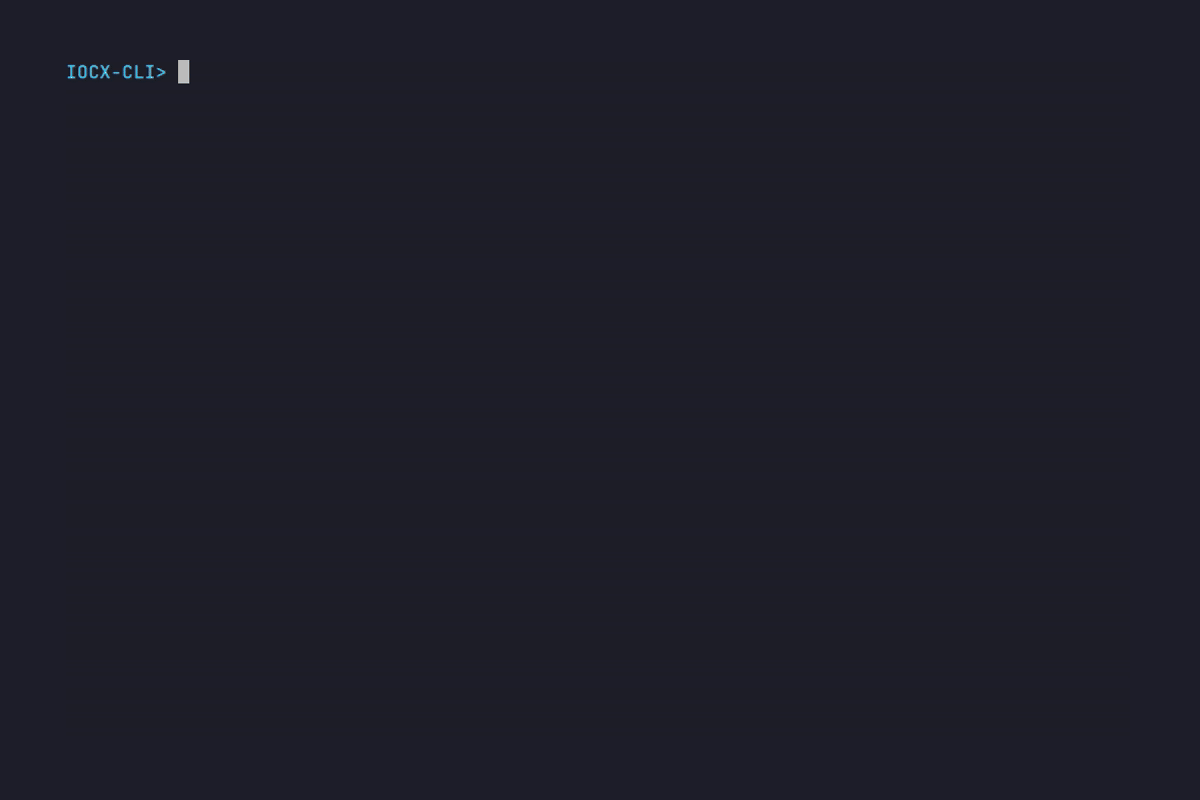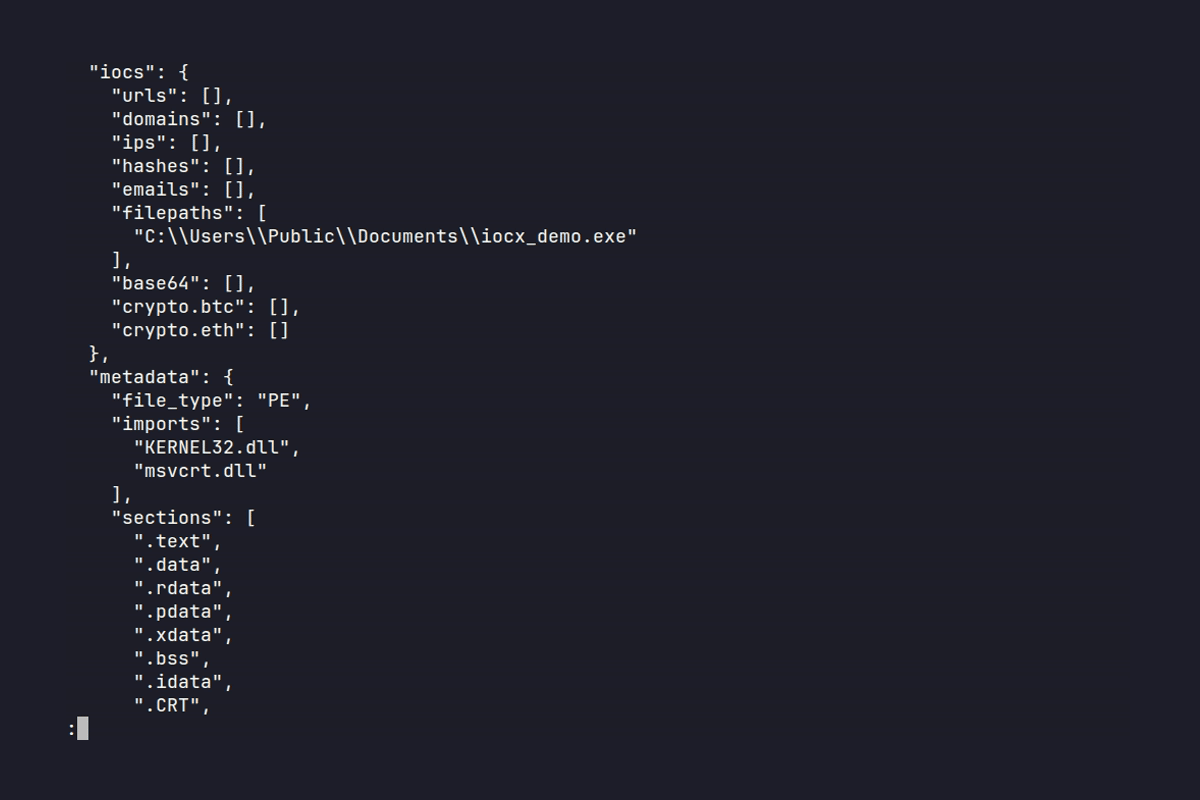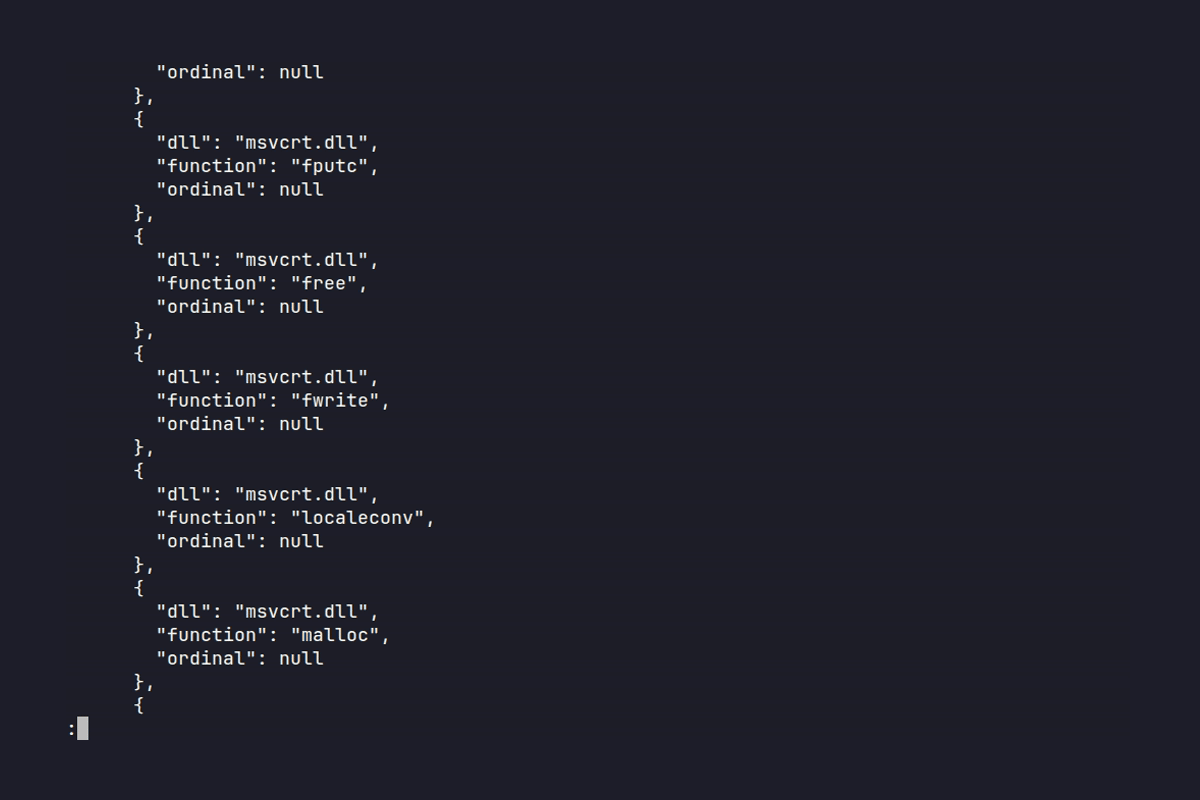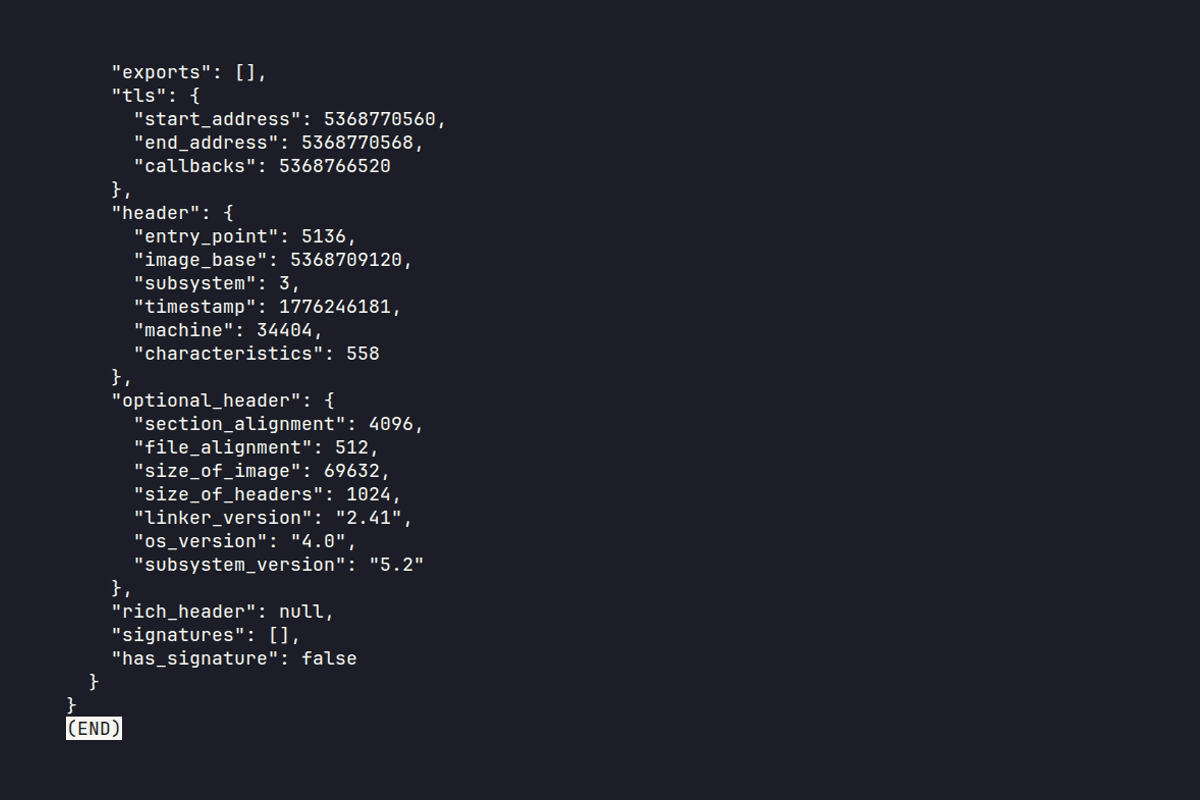 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
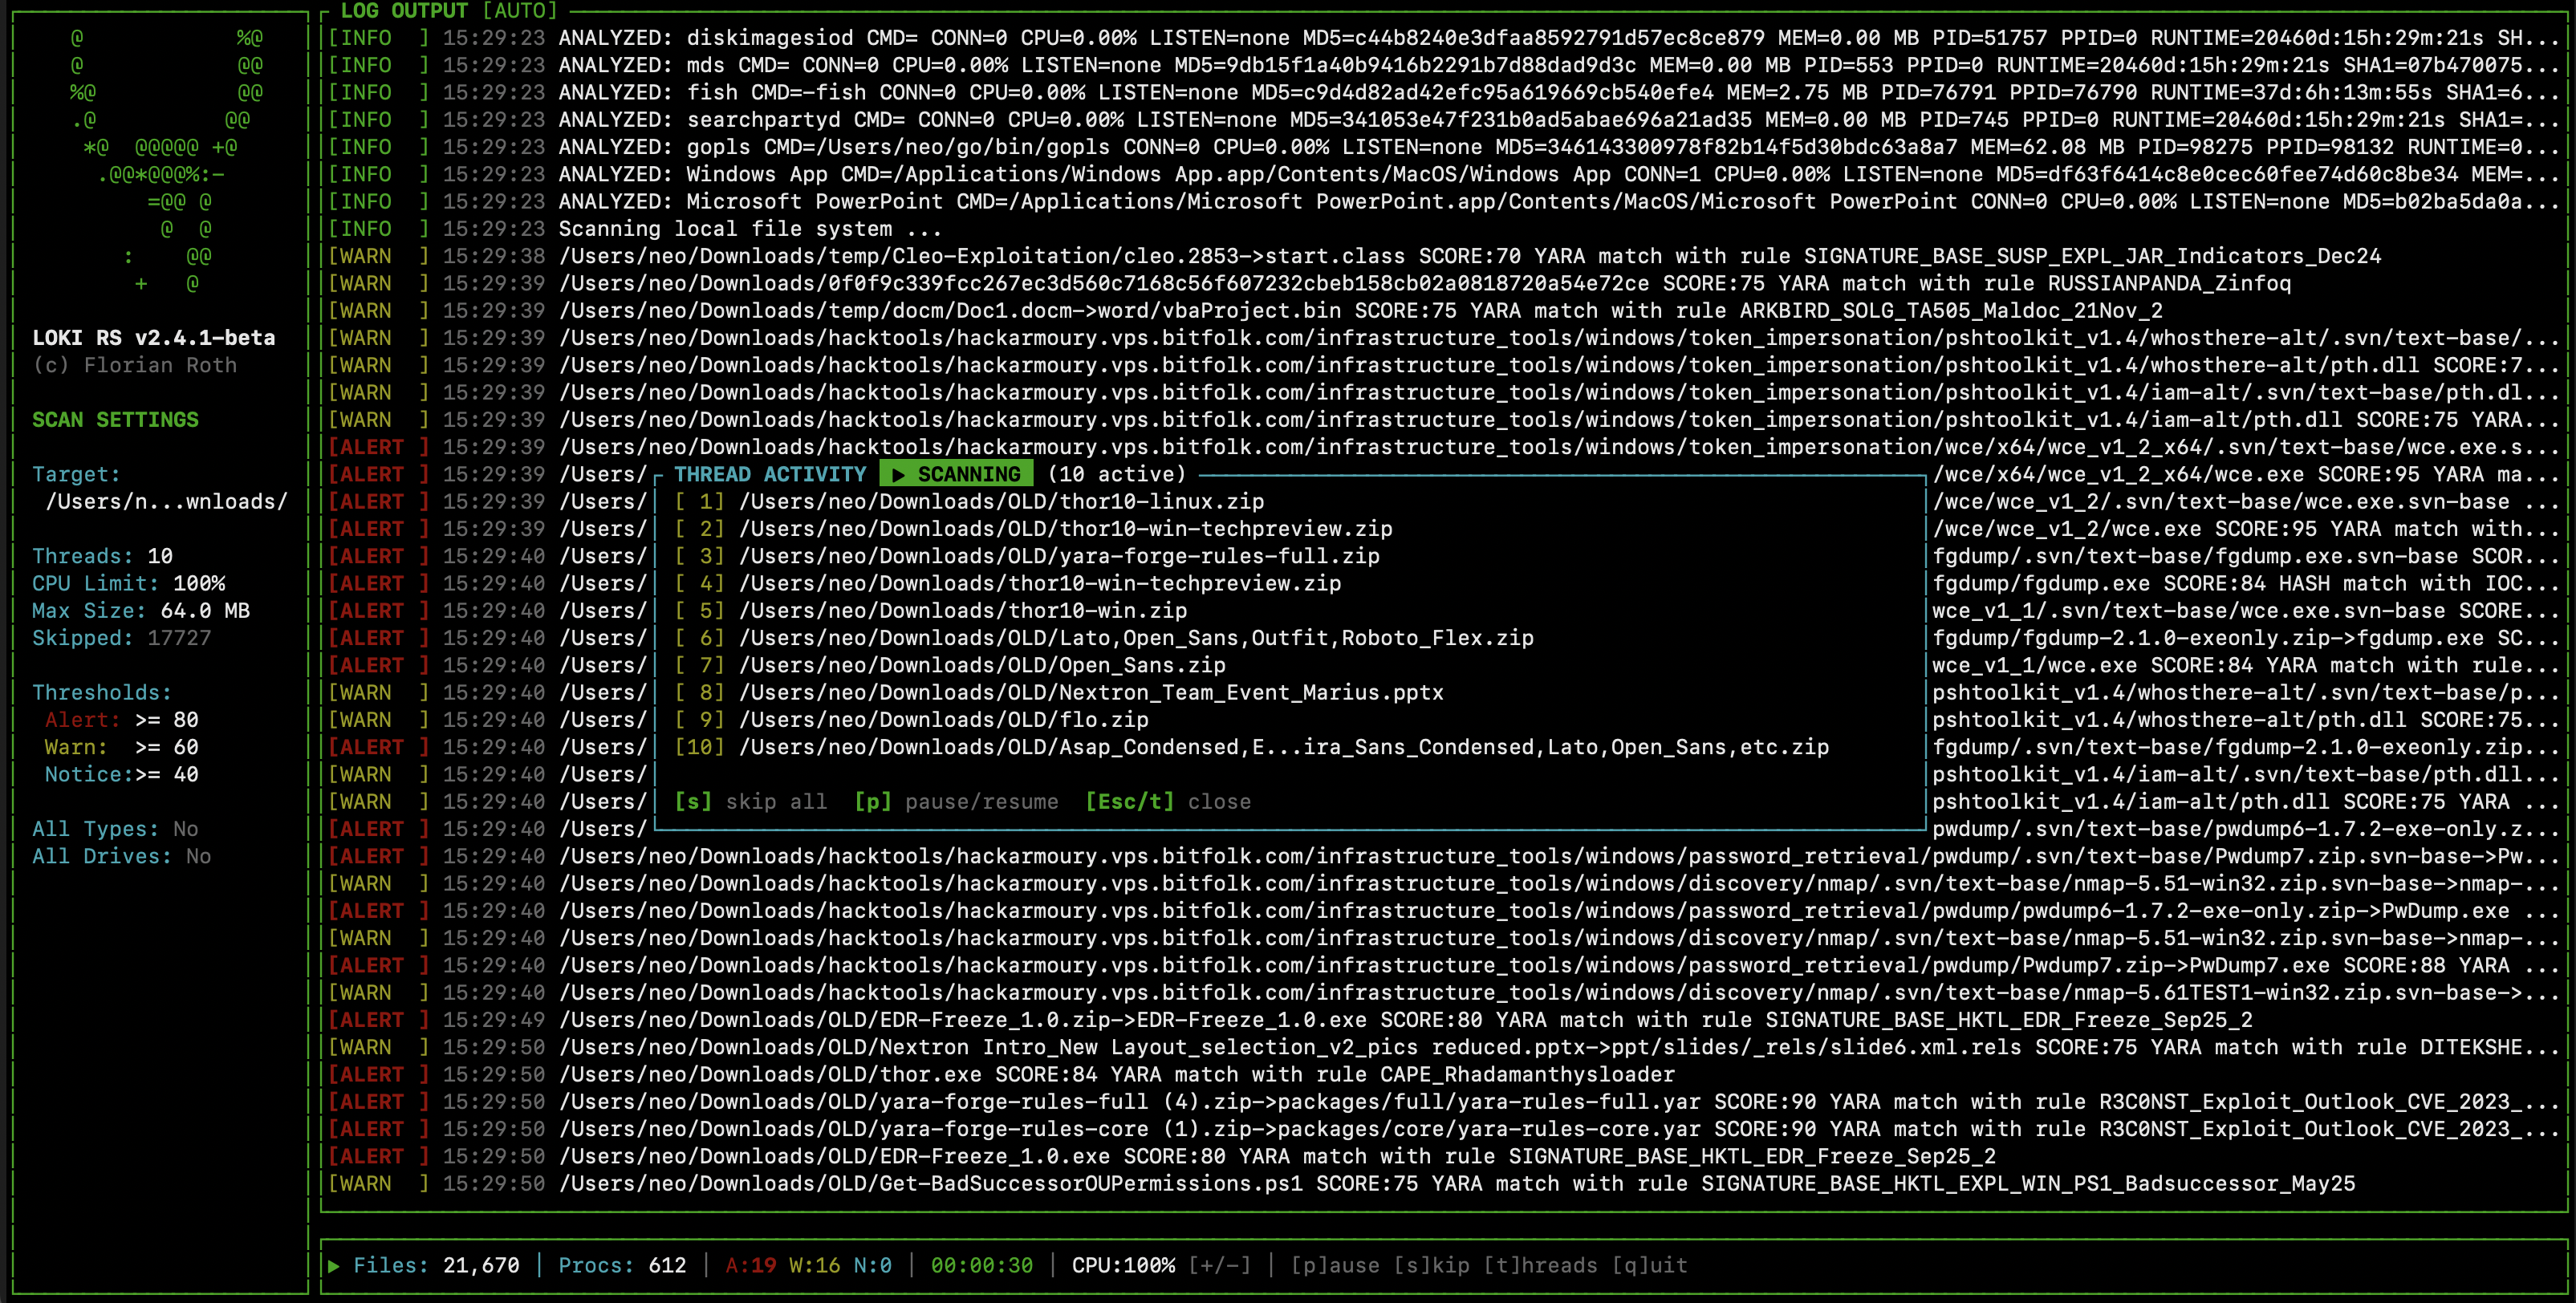 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

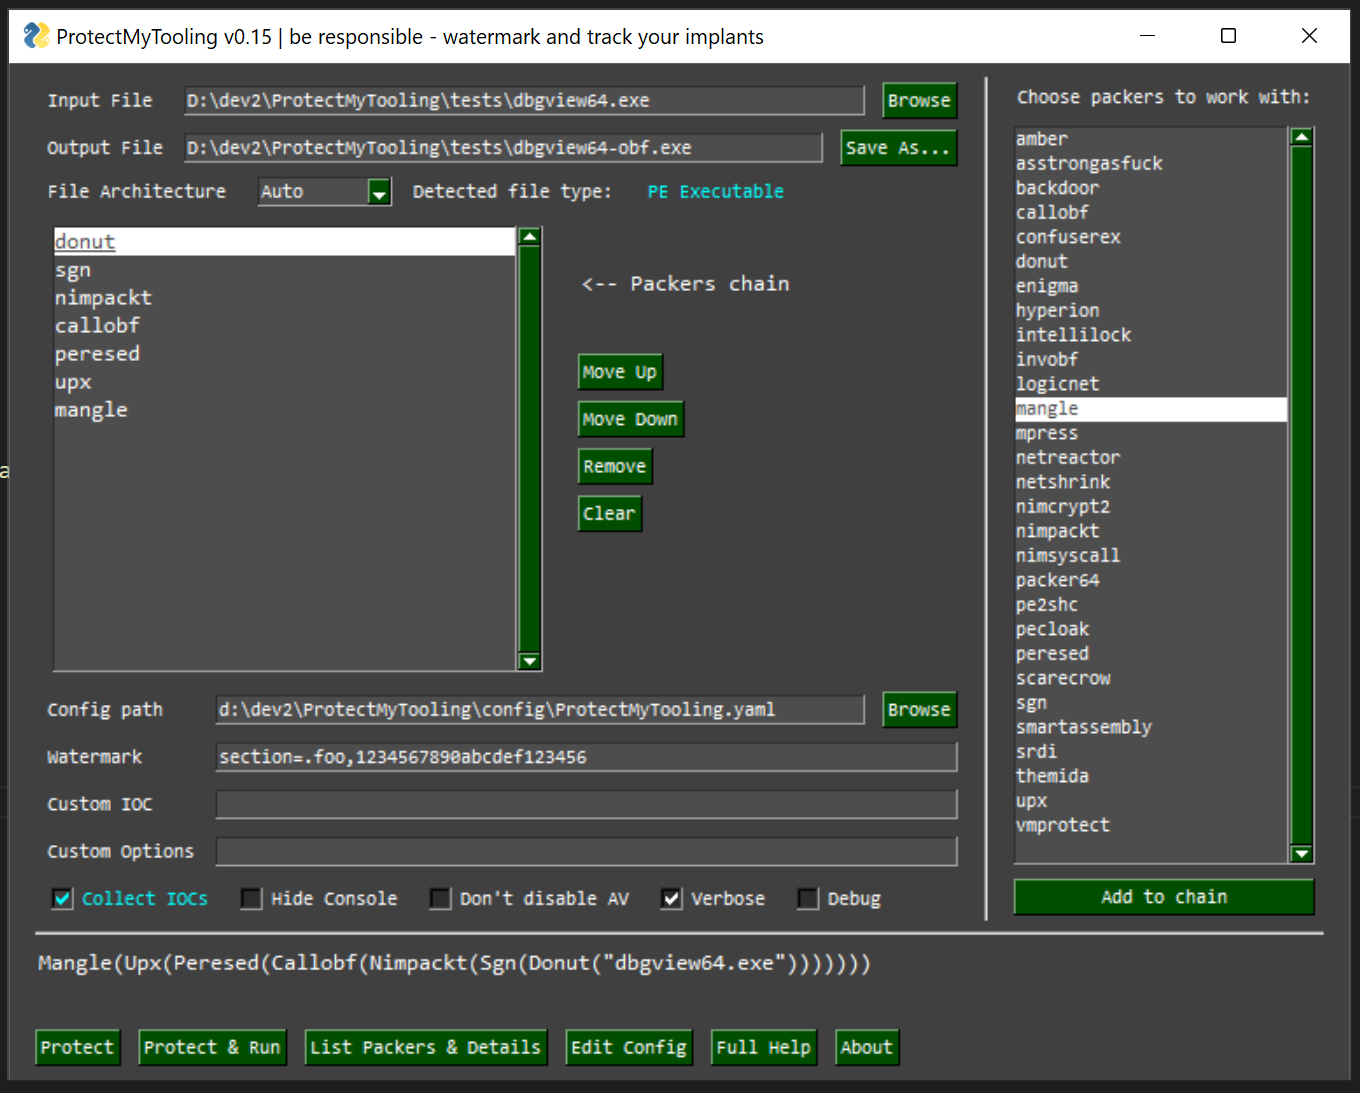 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
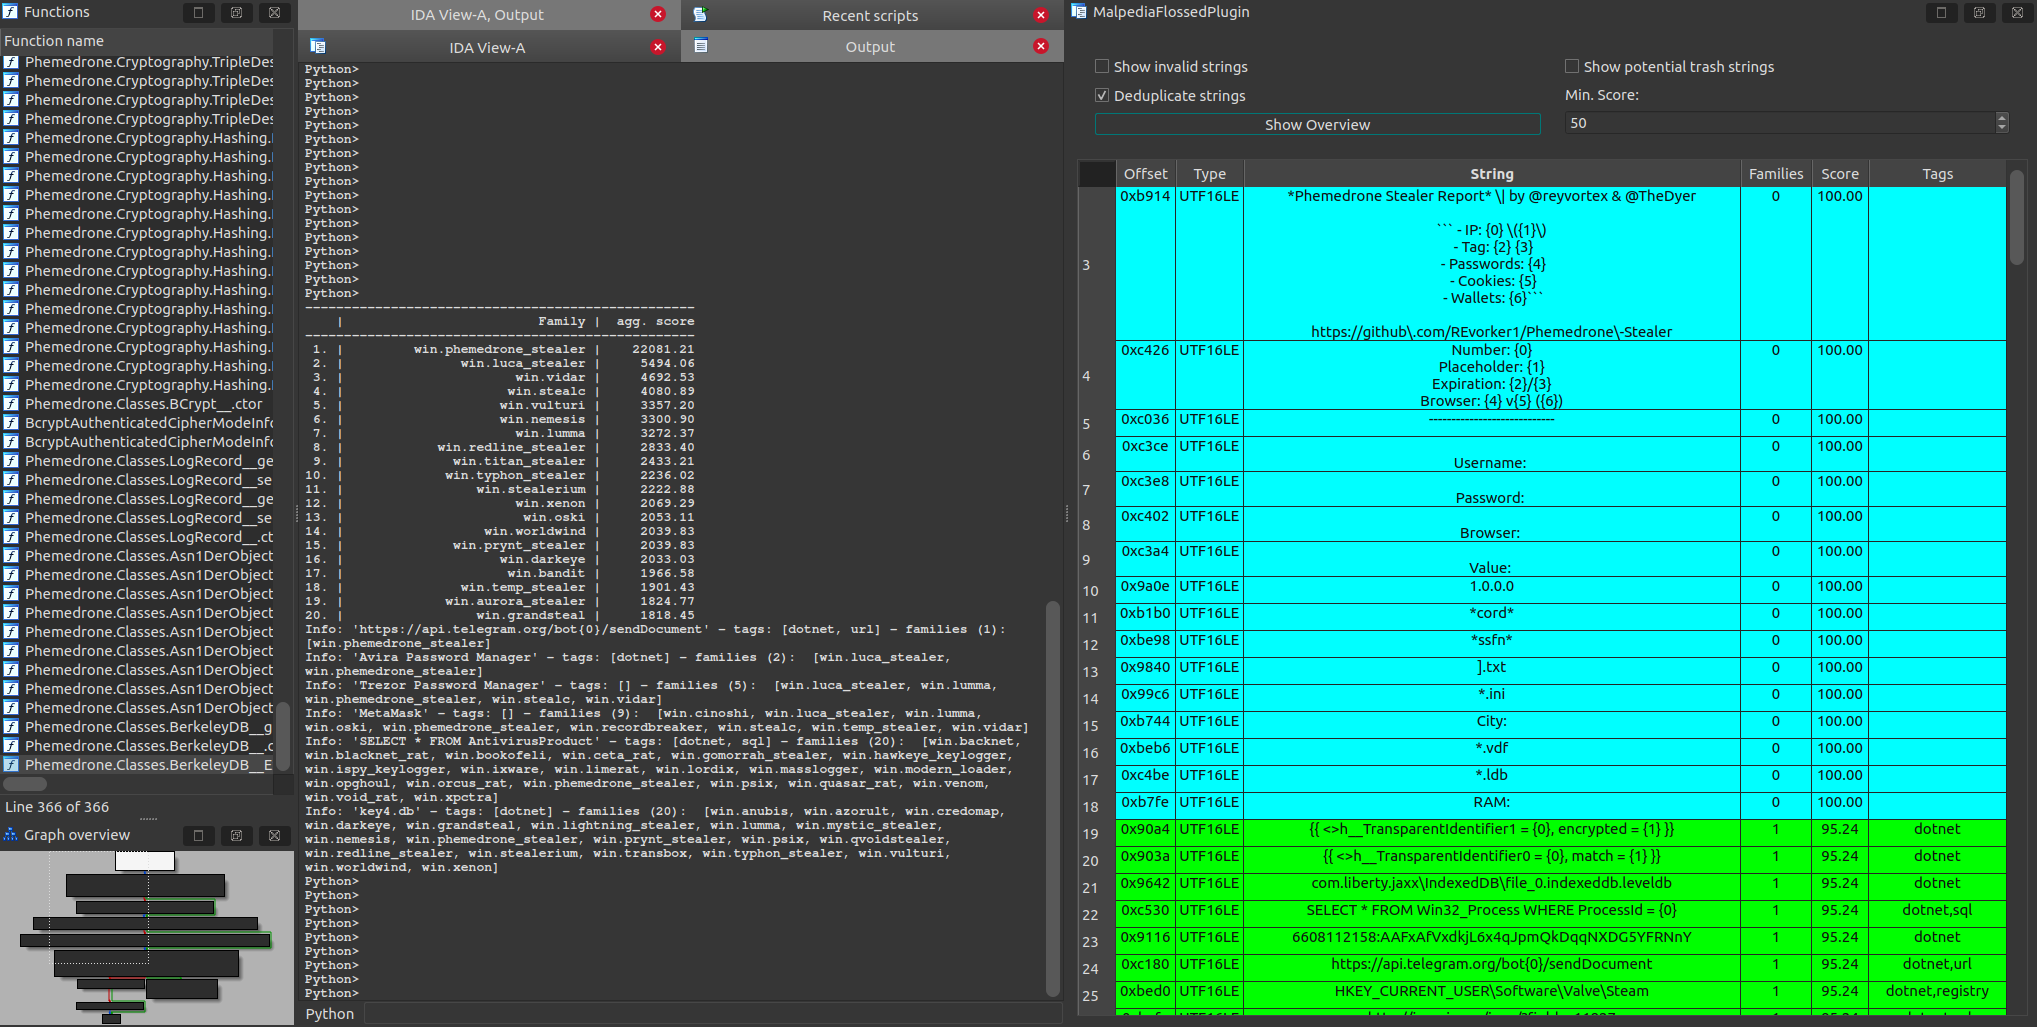 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 ares-sys/uefi_bootkit_softlanding
First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…
 embee-research/agenttesla-config-extractor
Config extractor for AgentTesla - Discord/Telegram Variant
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
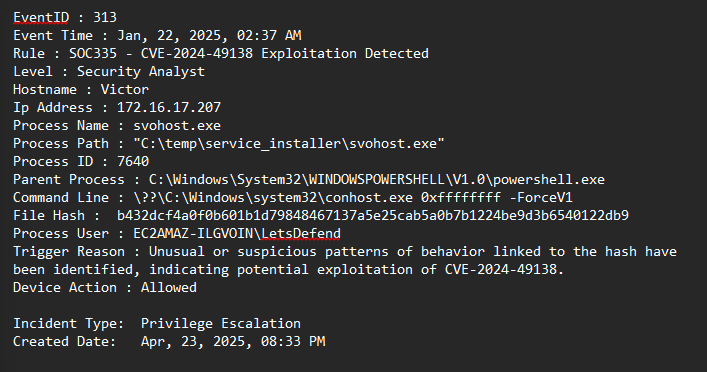 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.