
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
142 results
GOSINT preview
Archived

GOSINT

GitHubciscocsirt/gosint

The GOSINT framework is a project used for collecting, processing, and exporting high quality indicators of compromise (IOCs).

information-gatheringioc-managementosint+3
560

3 years ago
LogsTotal preview

LogsTotal

GitHubwagga40/logstotal

Self-hosted multi-engine Sigma detection for event logs

defensive-toolsdigital-forensicsincident-response+5
91 day ago
opencve preview

opencve

GitHubopencve/opencve

Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…

incident-responseioc-managementthreat-intelligence+2
2.8k9 days ago
malwoverview preview

malwoverview

GitHubalexandreborges/malwoverview

Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…

android-securityinformation-gatheringioc-management+4
4.1k1 month ago
yeti preview

yeti

GitHubyeti-platform/yeti

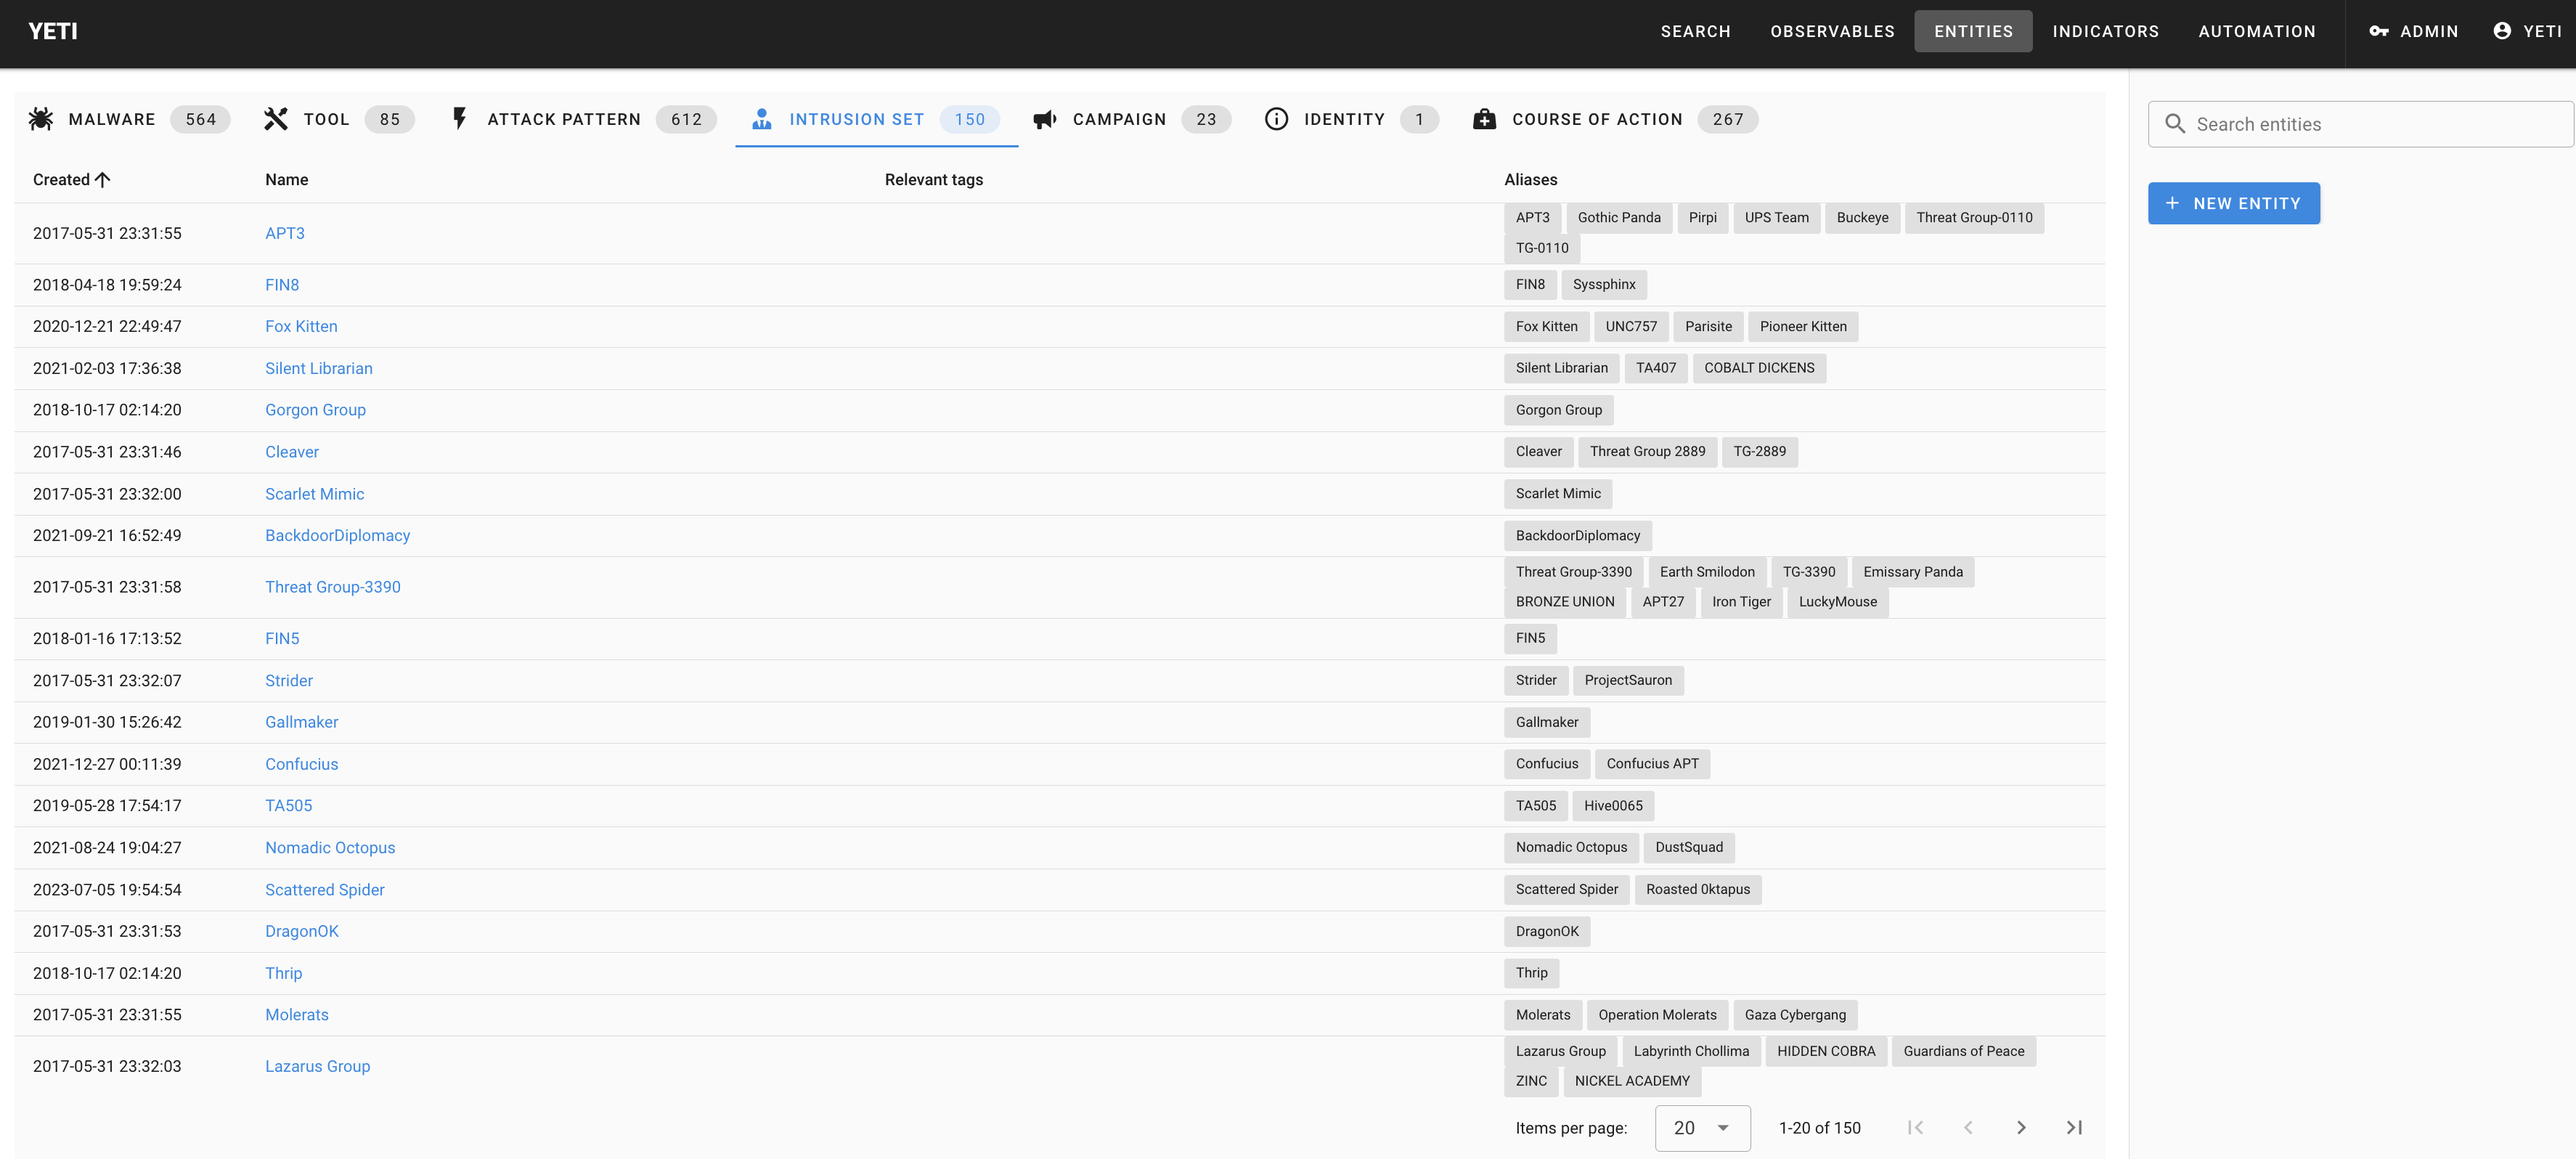
Your Everyday Threat Intelligence

digital-forensicseducationforensics+8
2.0k5 days ago
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

intrusion-detectionioc-managementnetwork-security+3
97012h 35m ago
numbat preview

numbat

GitHubperplexityai/numbat

Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
ai-securityanomaly-detectiondefensive-tools+7
1.2k2 days ago
ThePhish preview

ThePhish

GitHubemalderson/thephish

ThePhish: an automated phishing email analysis tool
digital-forensicsemail-securityincident-response+5
1.4k2 years ago
misp-galaxy preview

misp-galaxy

GitHubmisp/misp-galaxy

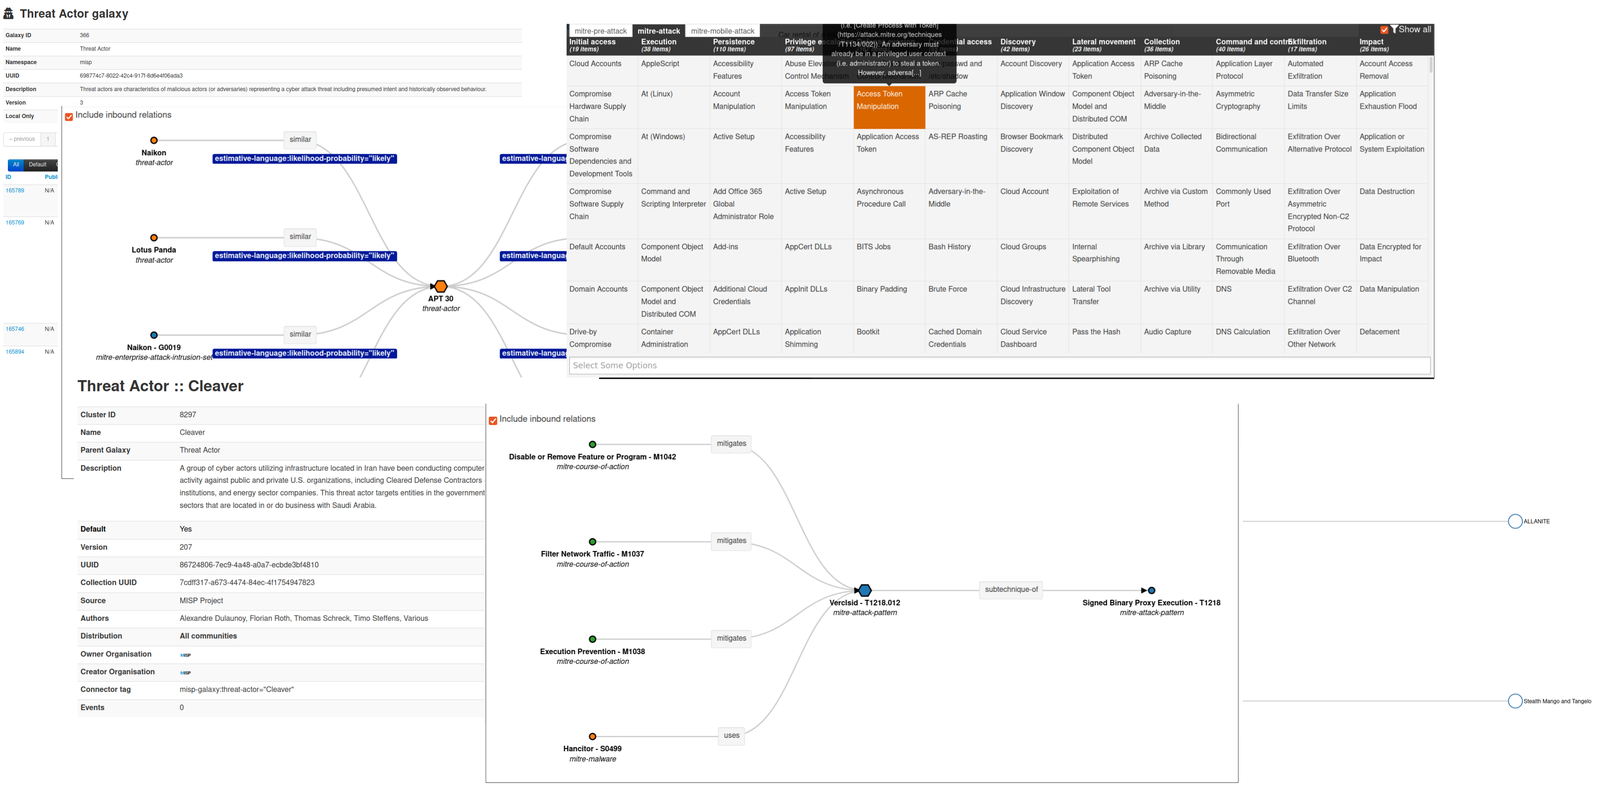
Clusters and elements to attach to MISP events or attributes (like threat actors)

adversarial-attackcurated-resourcesioc-management+5
6501 day ago
attack-stix-data preview

attack-stix-data

GitHubmitre-attack/attack-stix-data

STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
curated-resourcesioc-managementmobile-security+4
70719 days ago
php2shell preview

php2shell

GitHubncsc-nl/php2shell

Operational advisory repository tracking CVE-2026-109618 and CVE-2026-109619 PHP RCE flaws, with detection and mitigation guidance, affected software…
curated-resourcesdefensive-toolsincident-response+4
3502h 2m ago
OpenSSL-2022 preview

OpenSSL-2022

GitHubncsc-nl/openssl-2022

Operational information regarding CVE-2022-3602 and CVE-2022-3786, two vulnerabilities in OpenSSL 3
cryptographycurated-resourcesincident-response+3
5283 years ago
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

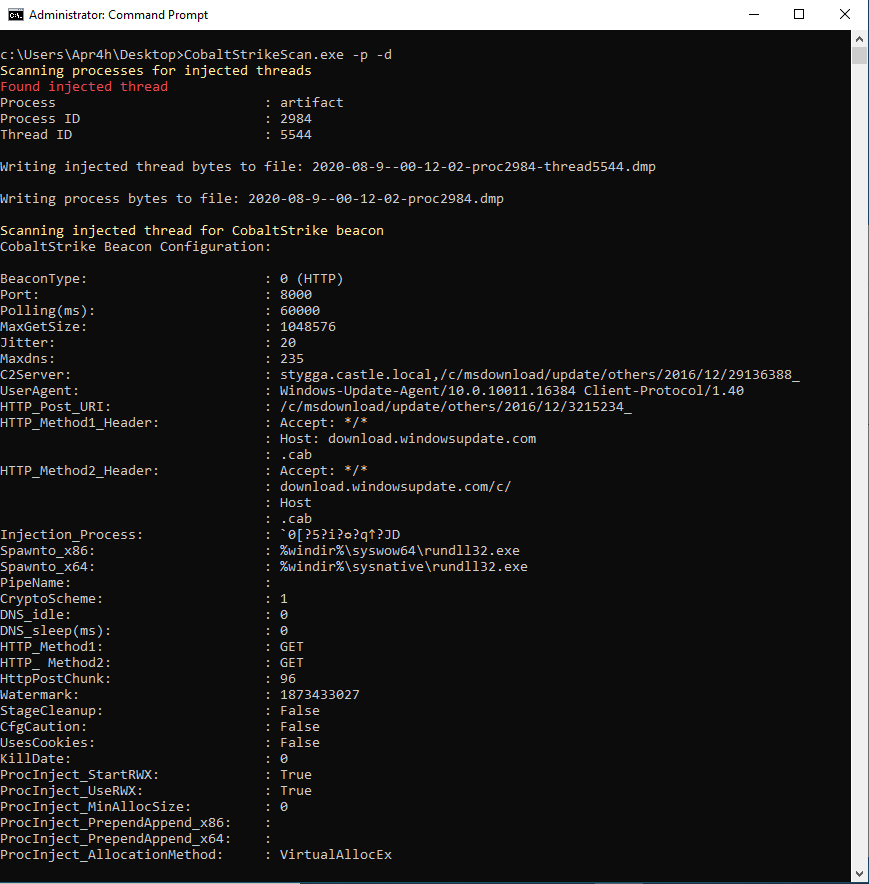
Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9195 years ago
yara-rules preview

yara-rules

GitHubinquest/yara-rules

Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
curated-resourcesdefensive-toolsincident-response+5
3894 years ago
artillery preview

artillery

GitHubtrustedsec/artillery

Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
anomaly-detectiondefensive-toolshardware-iot-security+5
3386 years ago
kev-data preview

kev-data

GitHubcisagov/kev-data

Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…

curated-resourcesdefensive-toolsinformation-gathering+5
1362 days ago
CVE-2021-44228-Log4Shell-Hashes preview

CVE-2021-44228-Log4Shell-Hashes

GitHubmubix/cve-2021-44228-log4shell-hashes

Hashes for vulnerable LOG4J versions
forensicsincident-responseioc-management+3
1554 years ago
iocs preview

iocs

GitHubthreatlabz/iocs

This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports

curated-resourcesincident-responseioc-management+4
793 days ago
Previous1…345…8Next