data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…

A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…

Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…

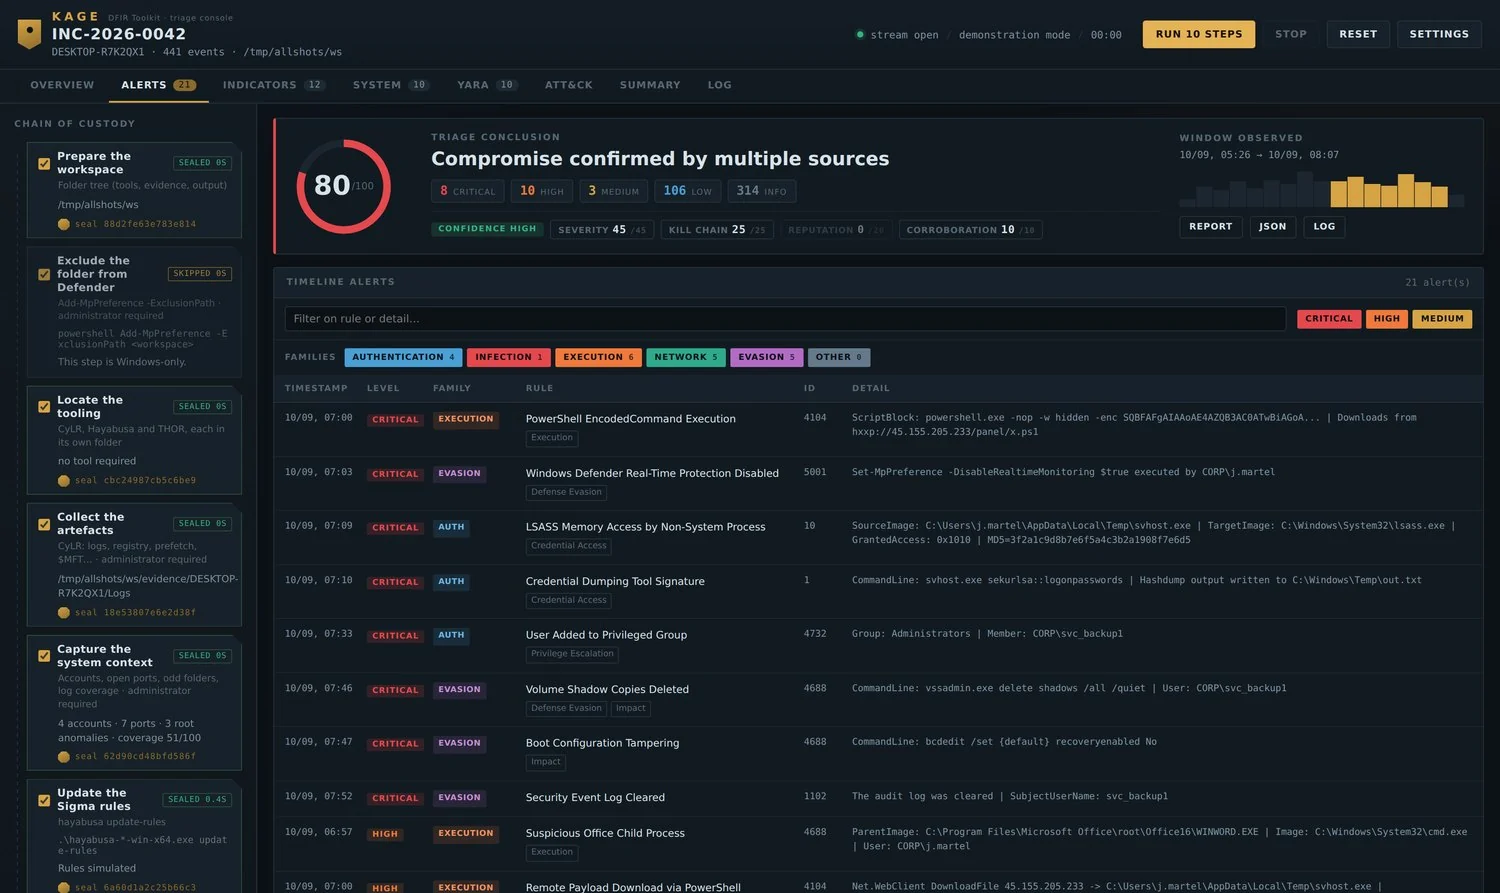
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…

IOCPARSER.COM is a Fast and Reliable service that enables you to extract IOCs and intelligence from different data sources.

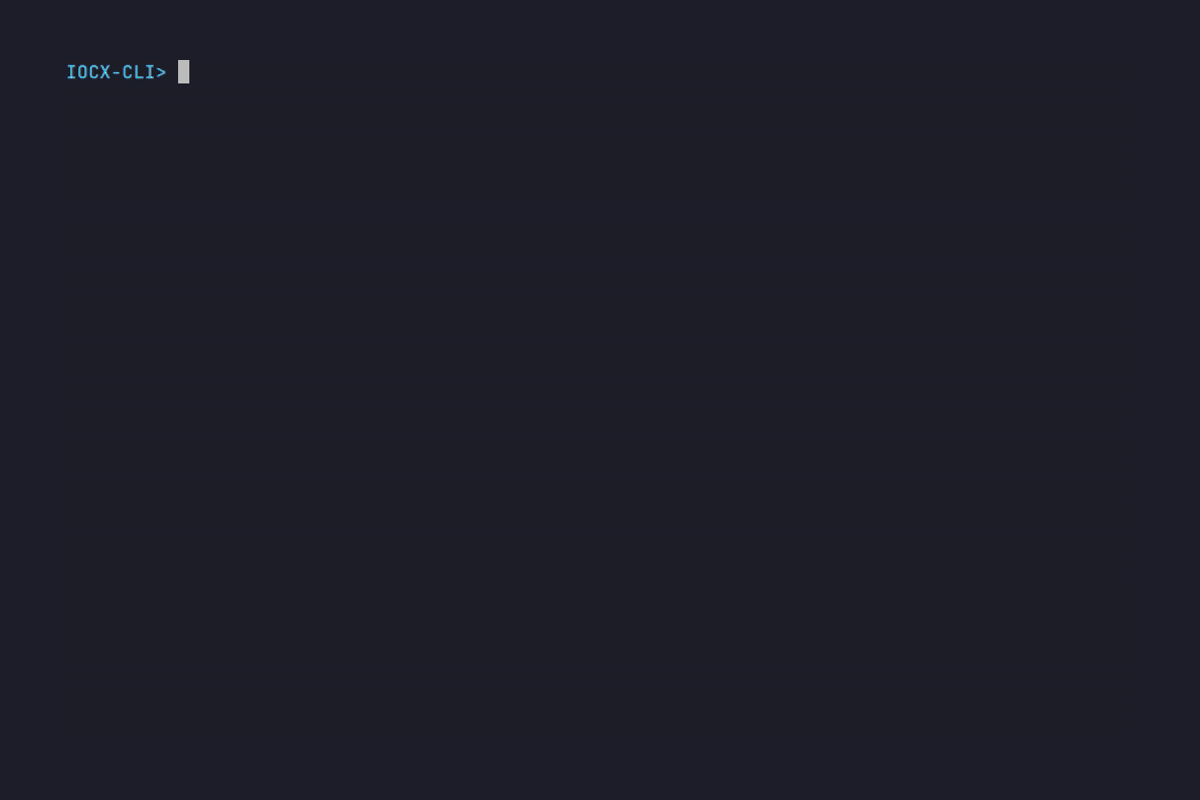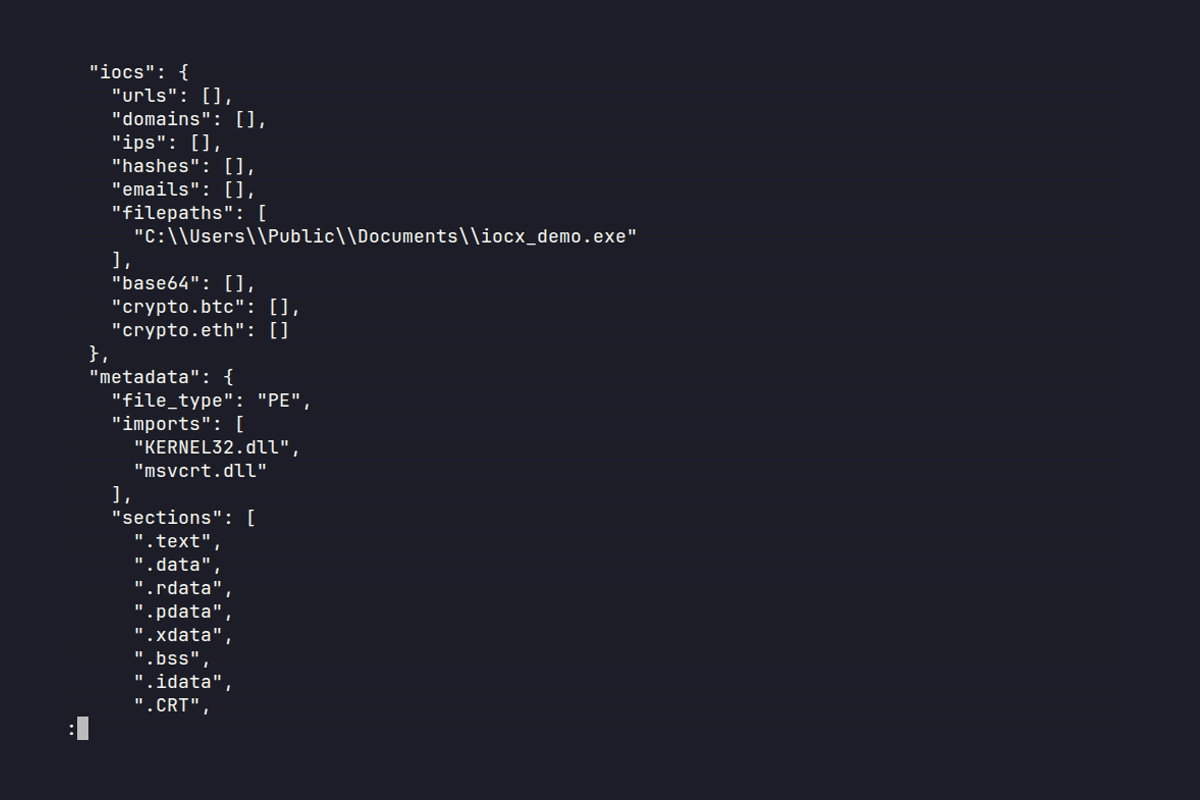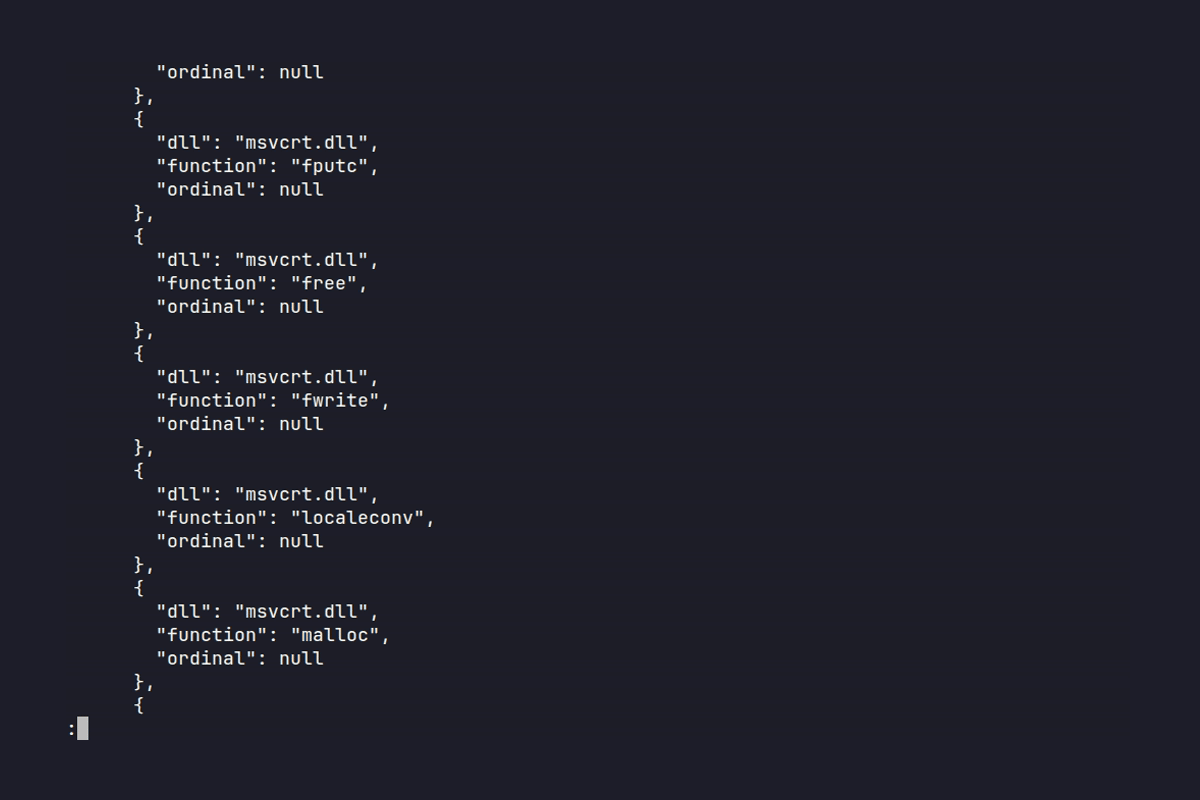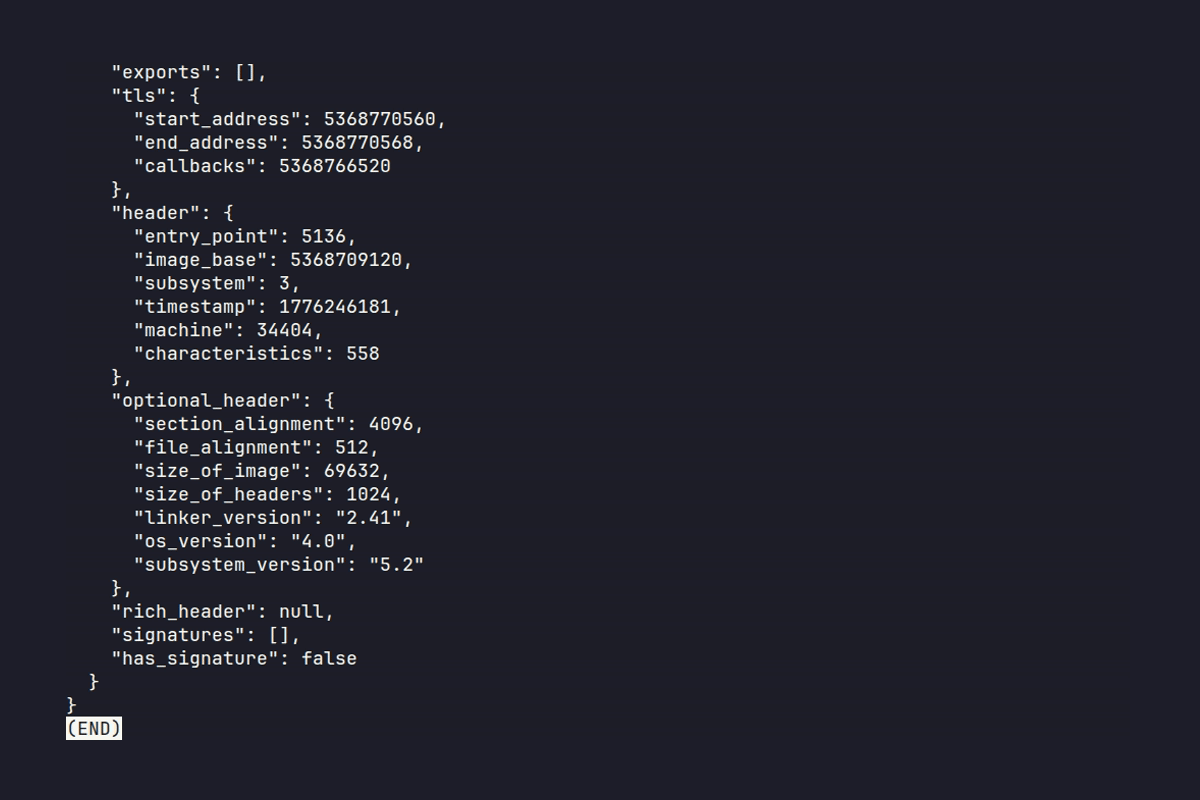
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…

Local F5 BIG-IP script that scans for Indicators of Compromise (IoCs) related to CVE-2020-5902, checking logs, files, and system integrity to detect…

Centralized IoC scanner that deploys Loki across endpoints, collects detection results, and parses logs into CSV for incident response and forensic…

USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…

This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…

Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.

This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…

Python-based scanner for CVE-2025-31324 that identifies vulnerable SAP NetWeaver Visual Composer instances and detects indicators of compromise from…

React2Shell, CVE-2025-55182, RCE Vulnerability: A critical breakdown of the unsafe deserialization flaw in React Server Components that enables…

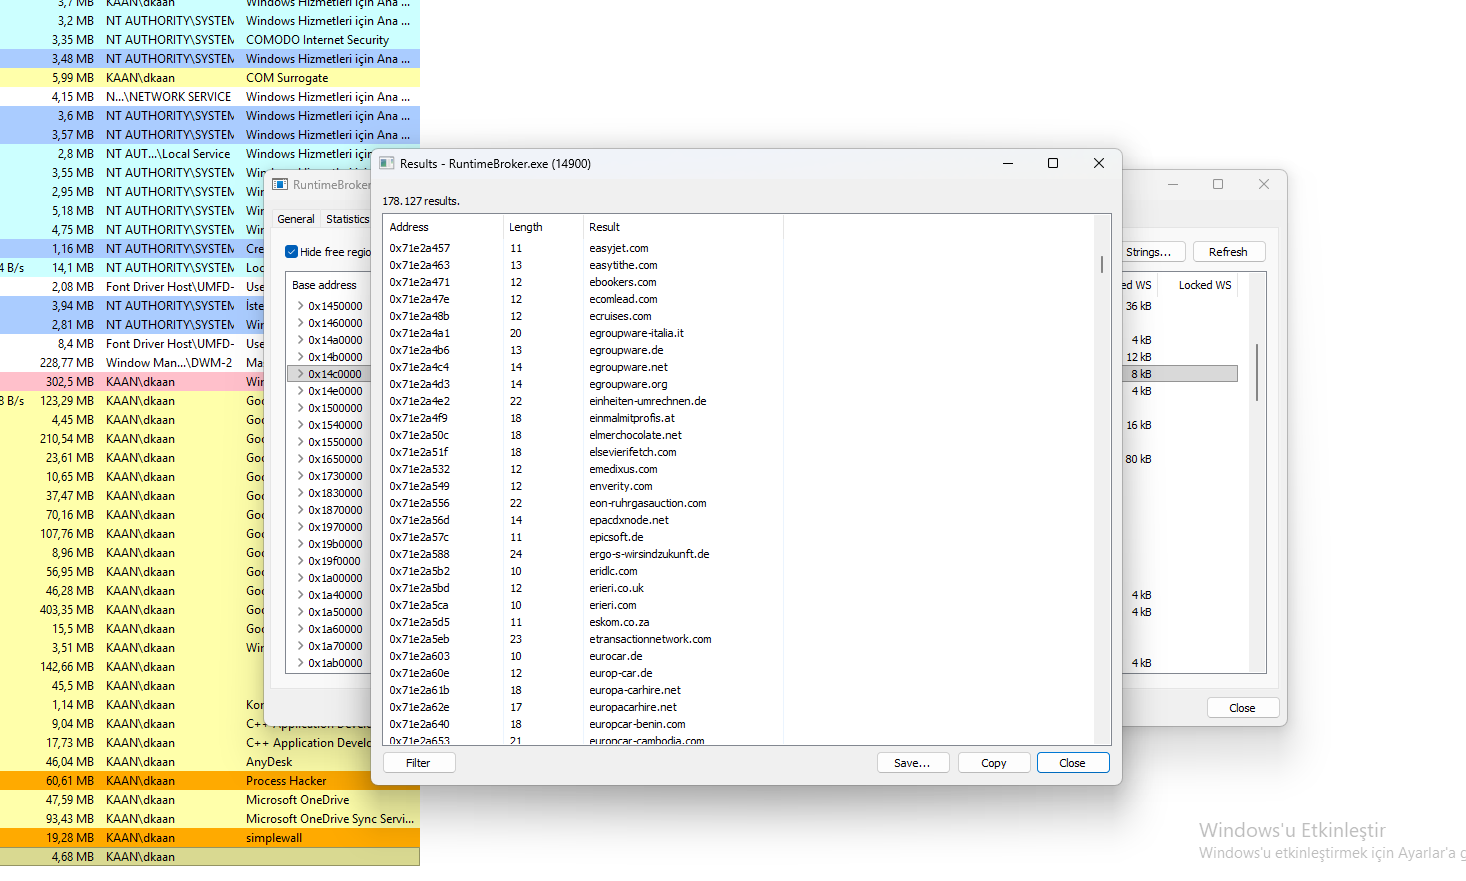
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Shell and SmartDashboard scripts that check Check Point management servers for indicators of compromise tied to CVE-2026-93616, including rogue…

Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…