
destroylist
 phishdestroy/destroylist
Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats
curated-resourcesdefensive-toolsdns-analysis+8
1.9k
phishdestroy/destroylistReal-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats
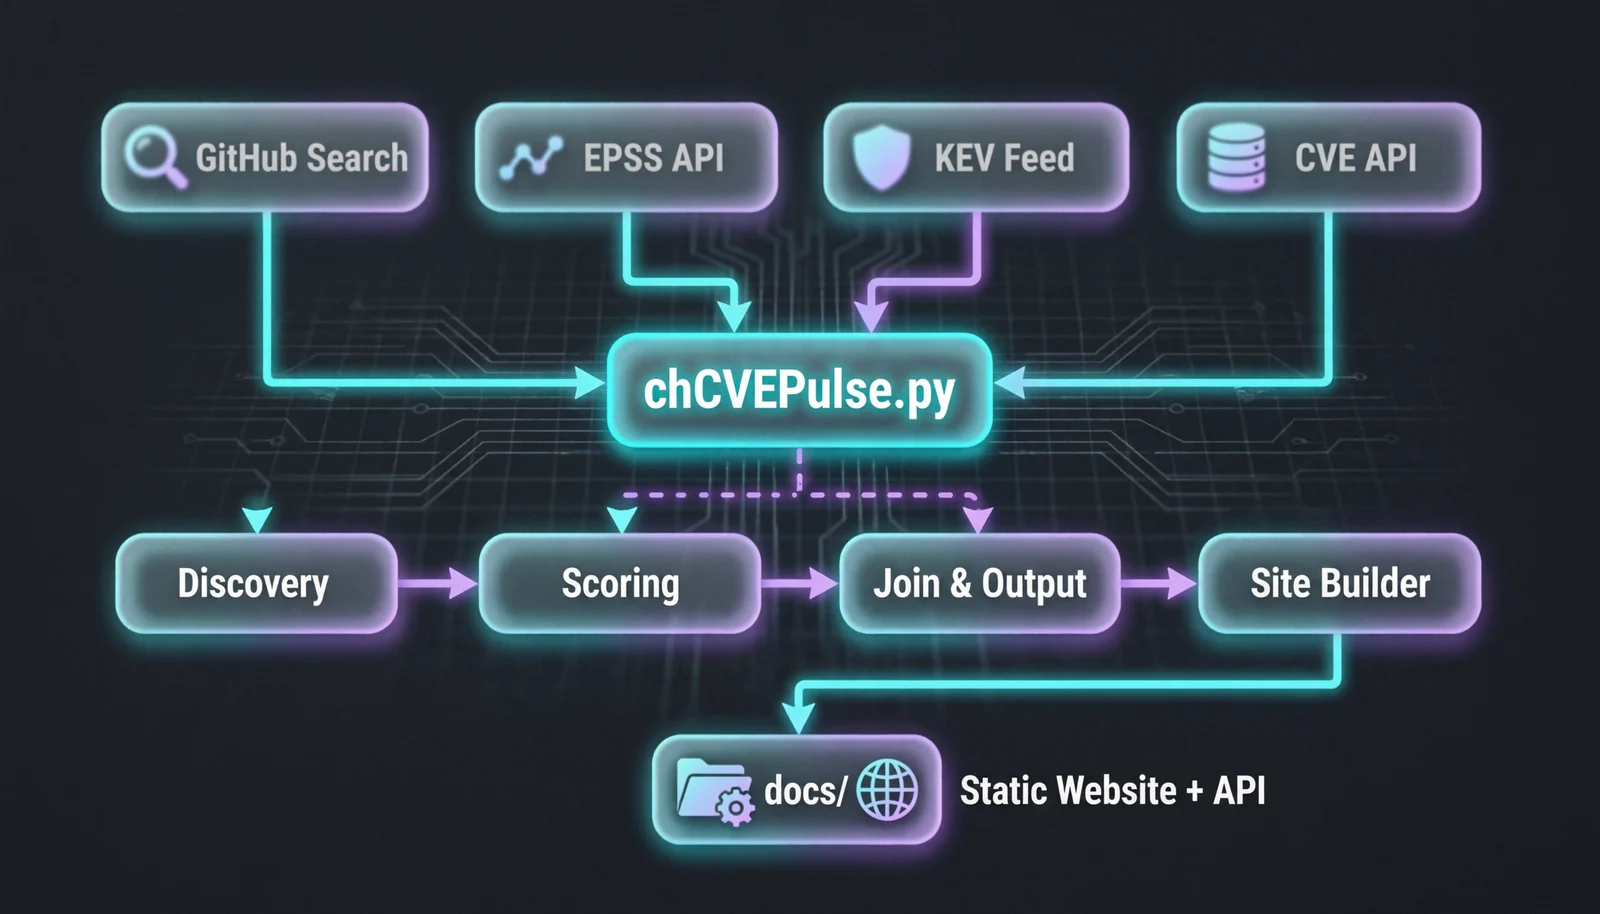 ch4120n/ch4120n-cve-pulse
Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 prox0959/omnitriage
Zero-dependency, sub-second Windows live digital forensics & incident response (DFIR) triage engine for USB responders.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
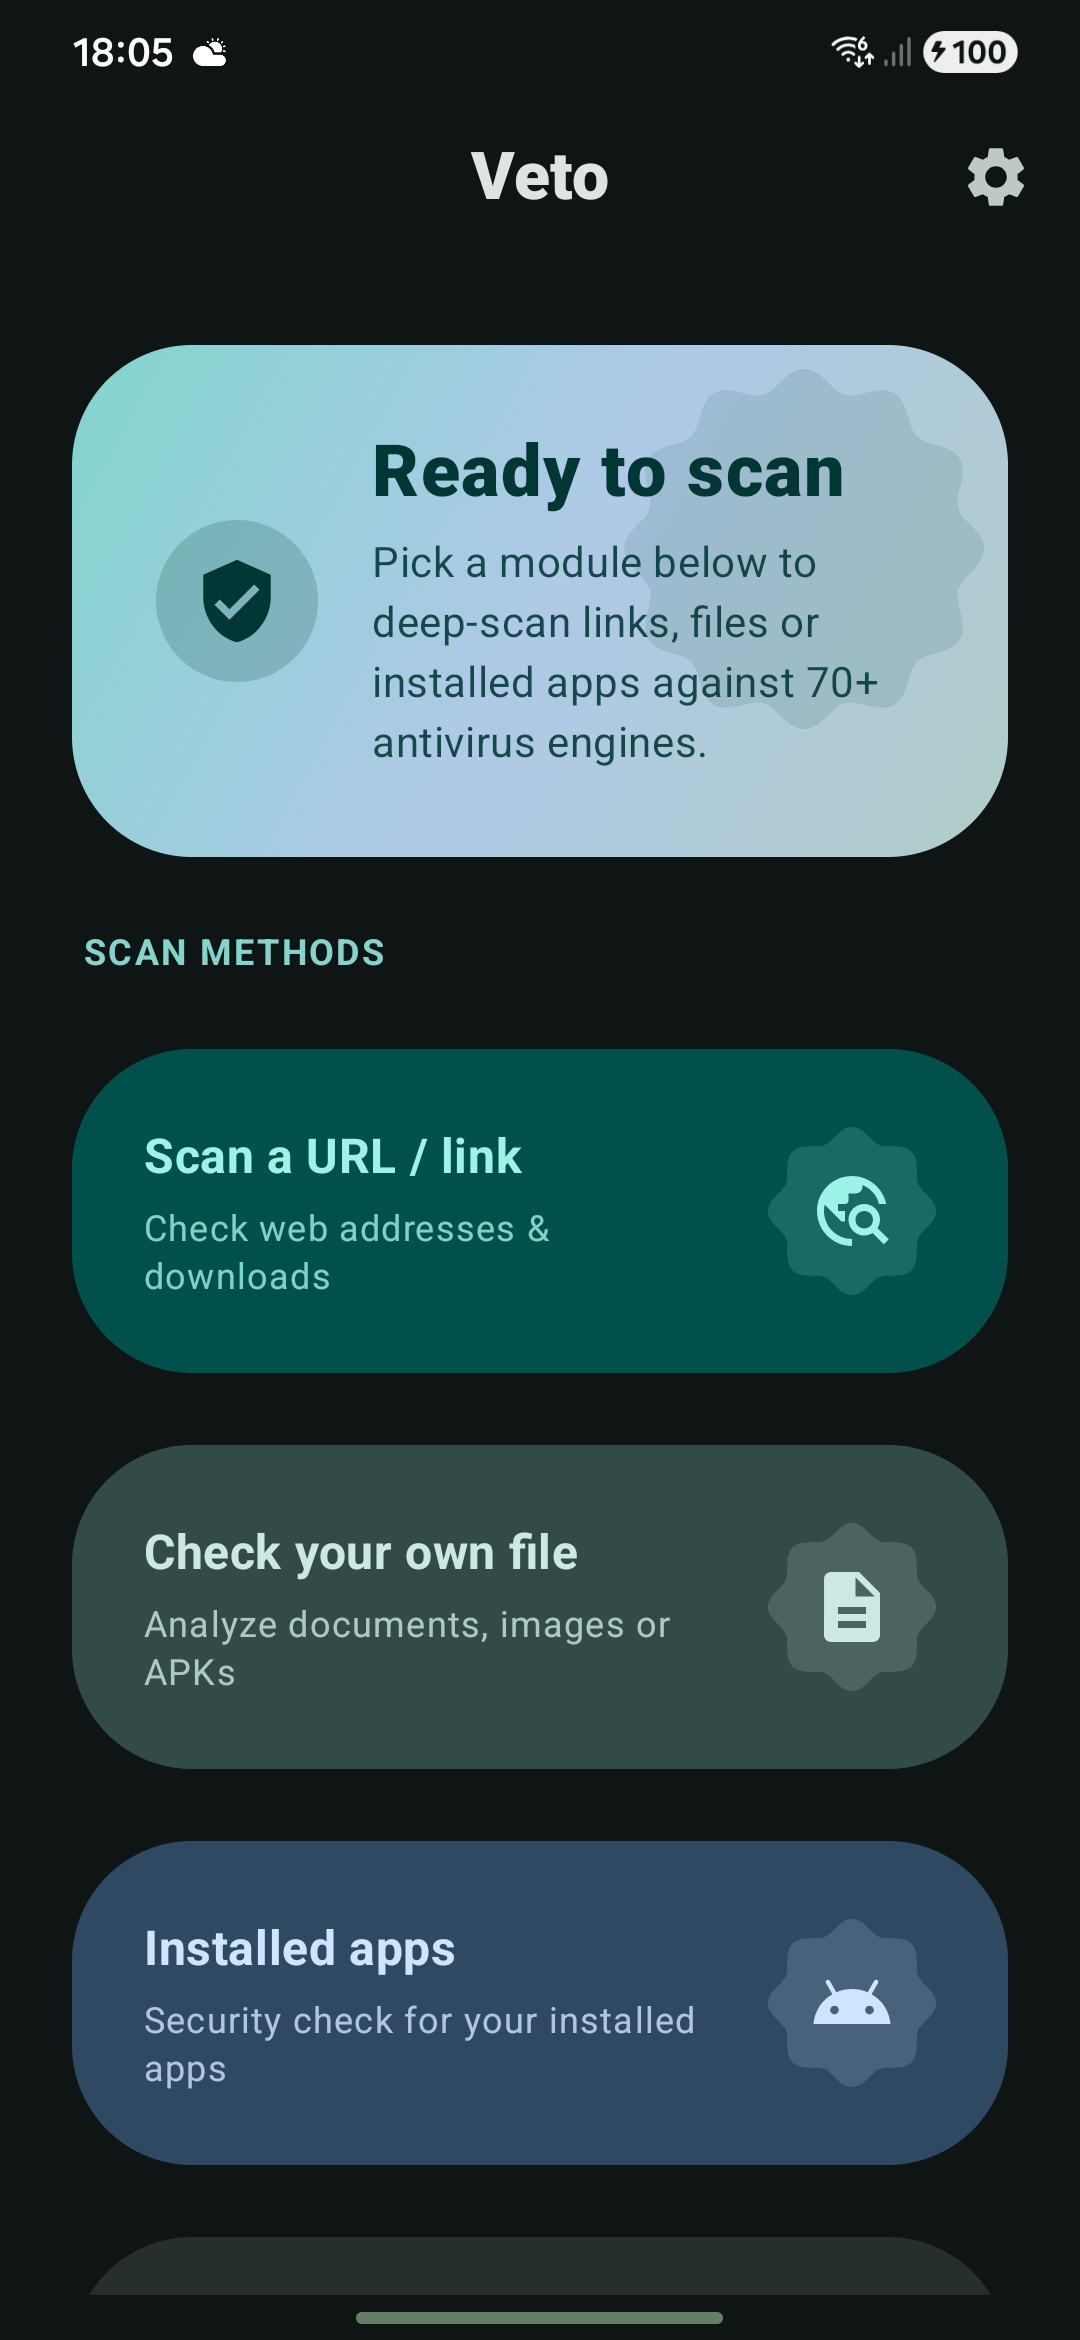 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
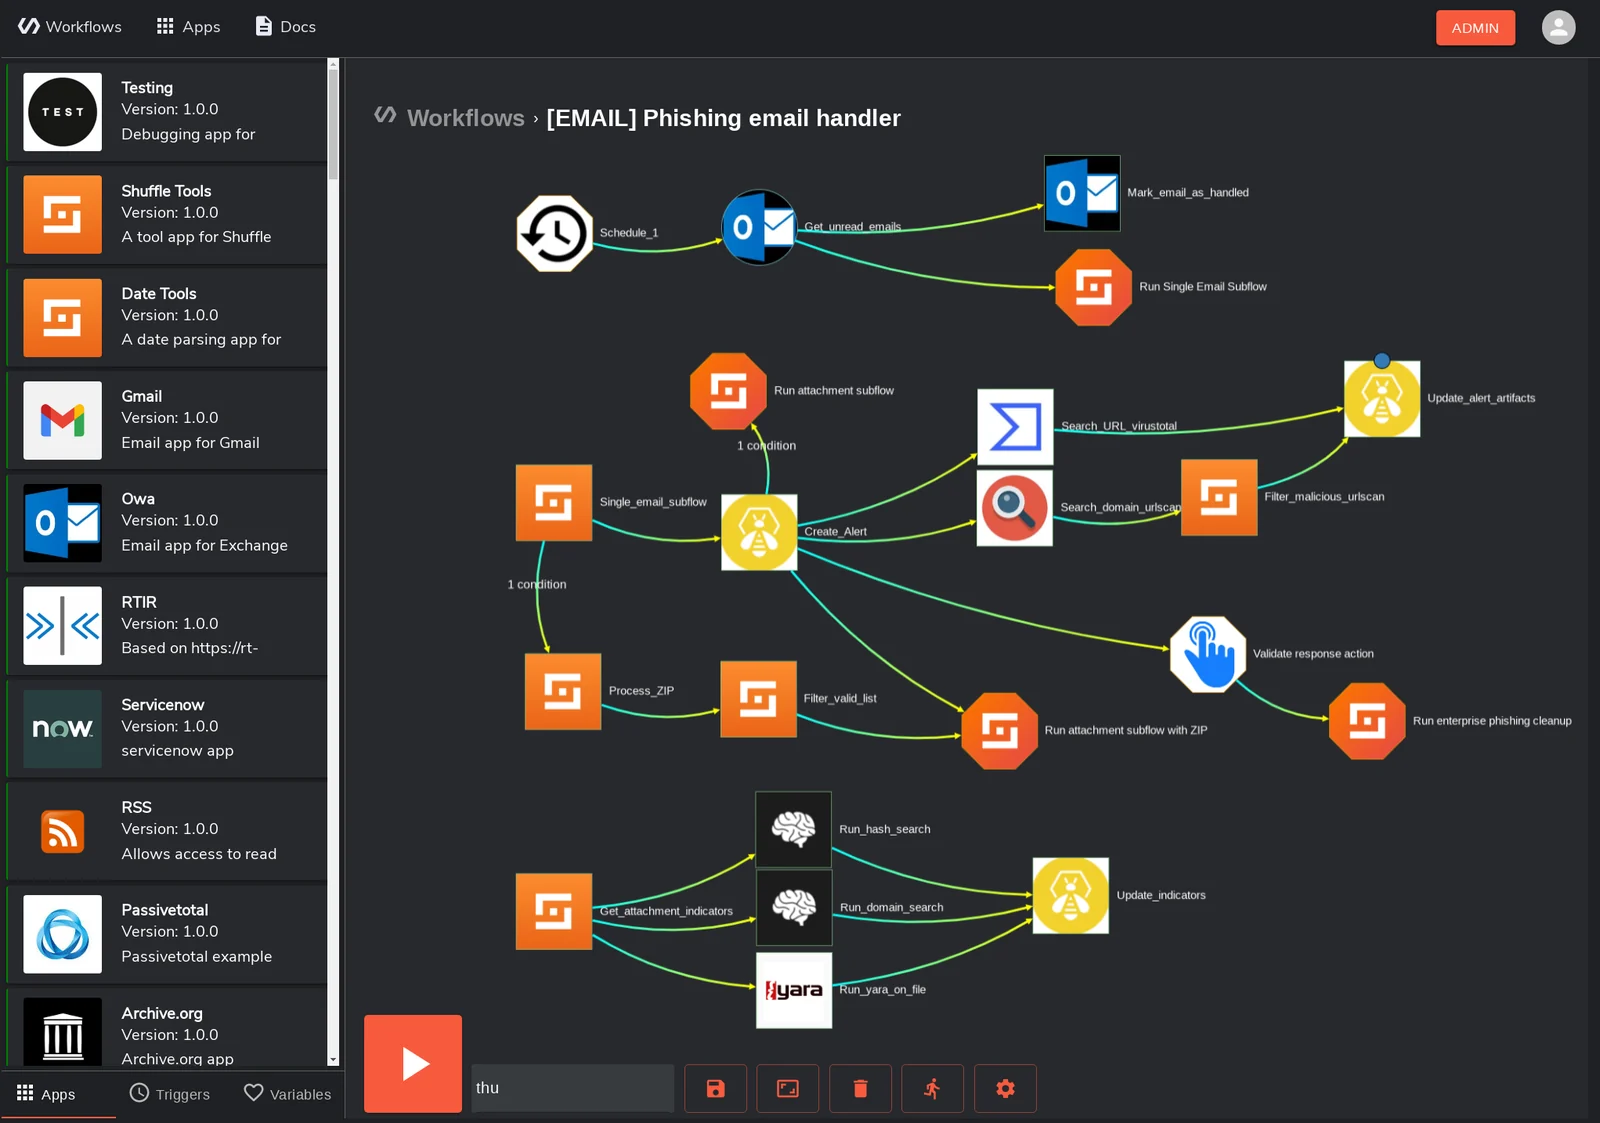 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 wadesweaponshed/cve-2026-93616_checks
Shell and SmartDashboard scripts that check Check Point management servers for indicators of compromise tied to CVE-2026-93616, including rogue…
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 soc-irdoc/irdoc-app
Incident Response Documentation Platform
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
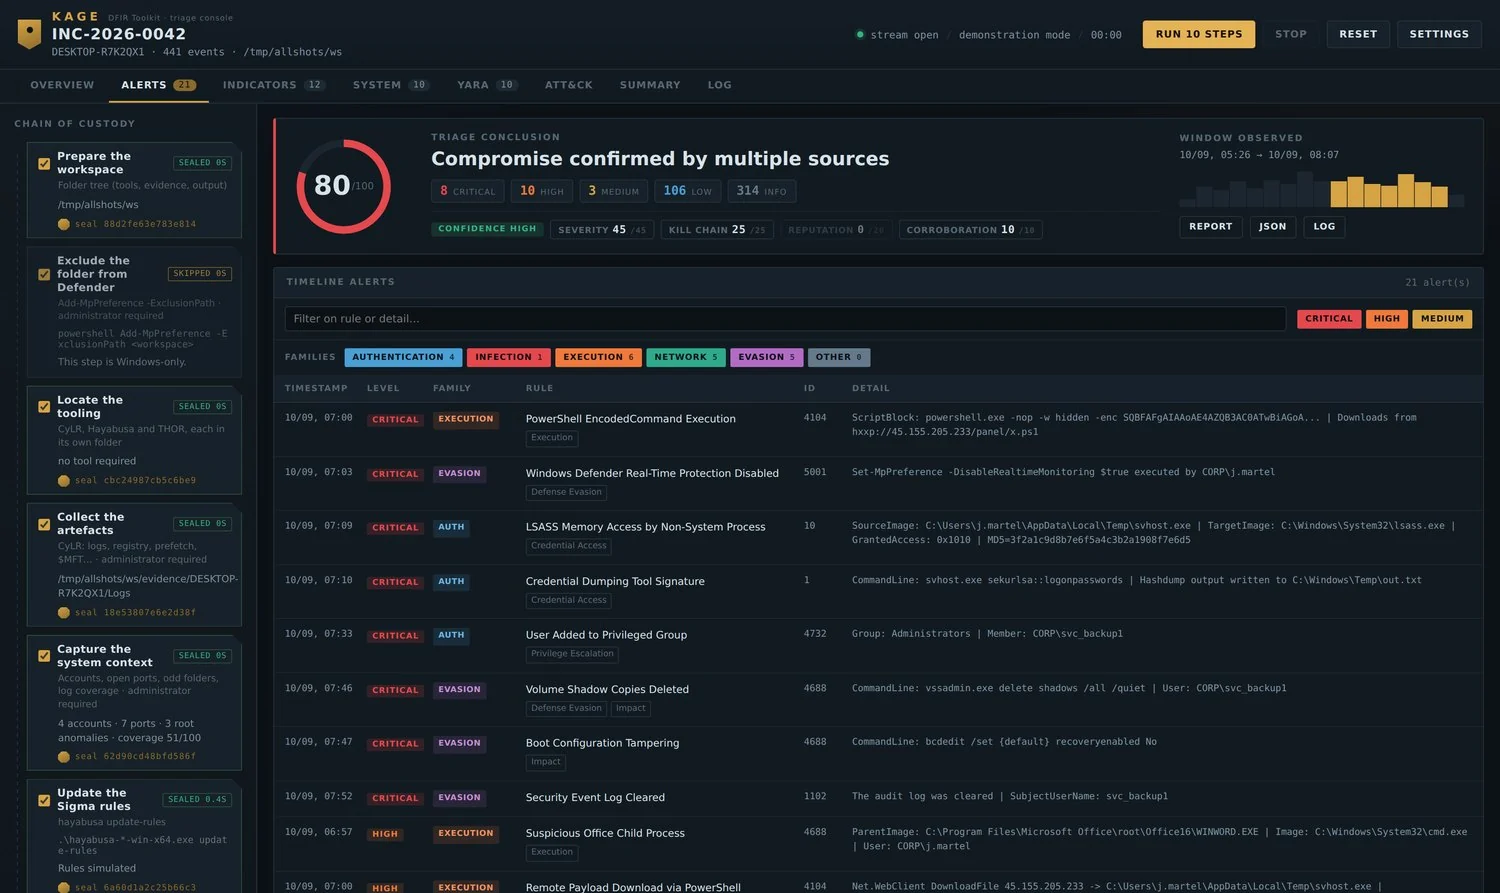 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…