
LOLRMM
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
curated-resourcesdefensive-toolseducation+6
396
magicsword-io/lolrmmCurated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
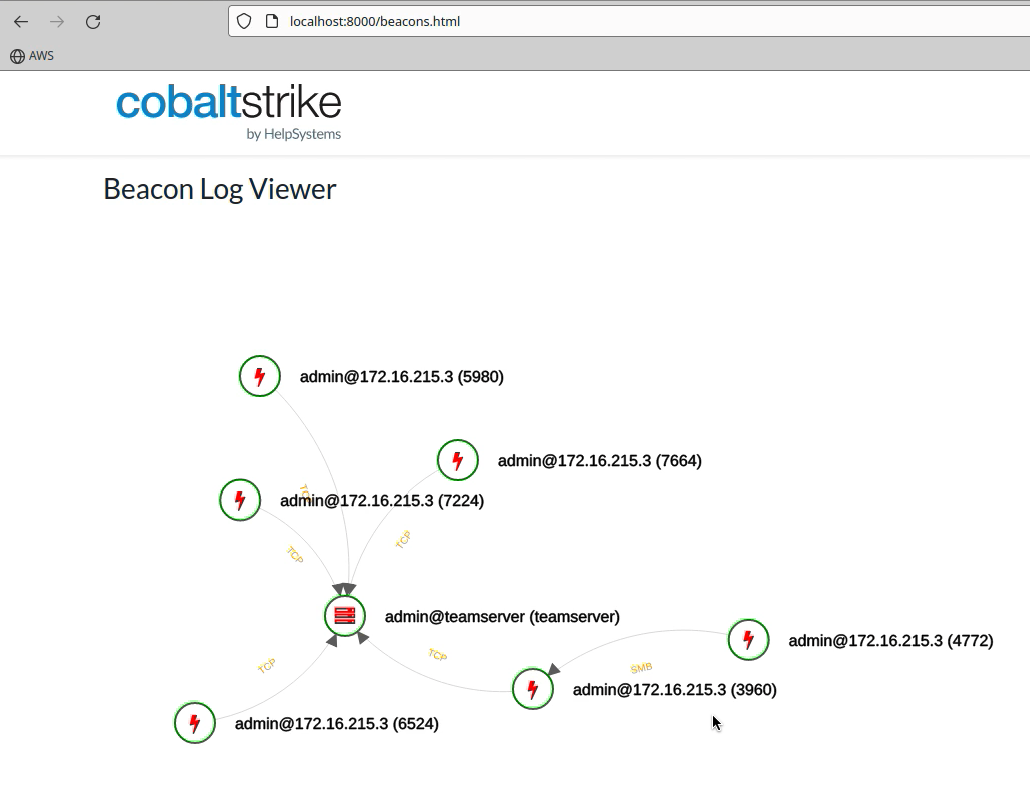 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
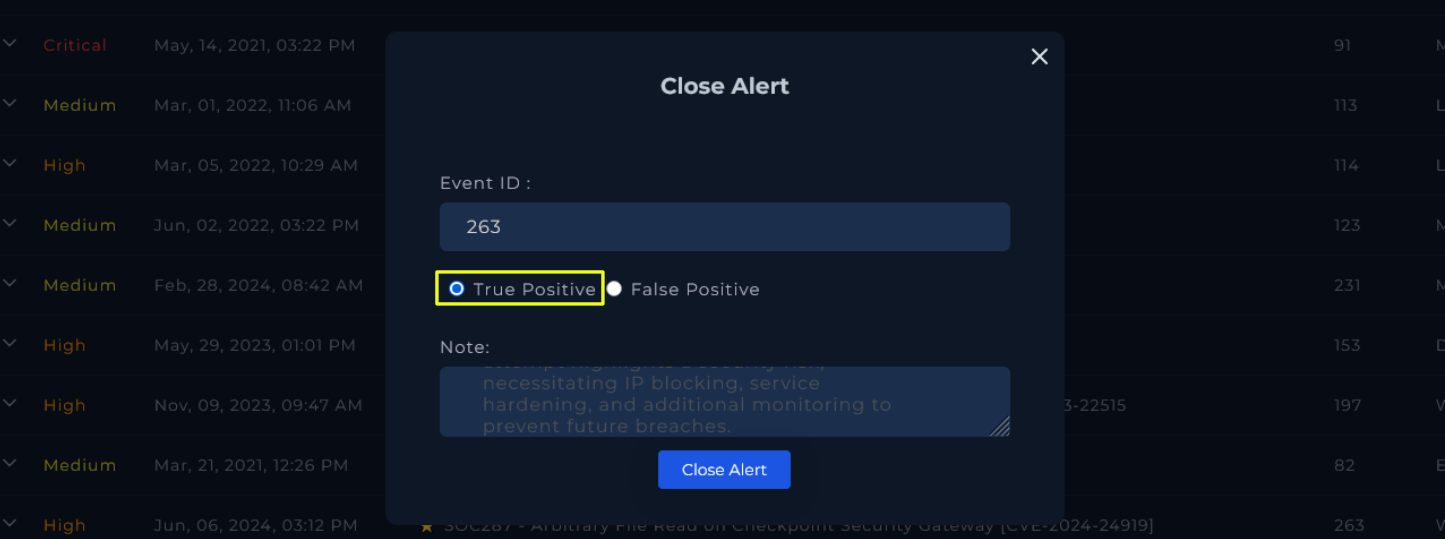 macuchegit/detecting-and-analyzing-cve-2024-24919-exploitation
Step-by-step walkthrough of detecting and analyzing CVE-2024-24919 exploitation using a SIEM platform, including traffic analysis, IOC documentation,…
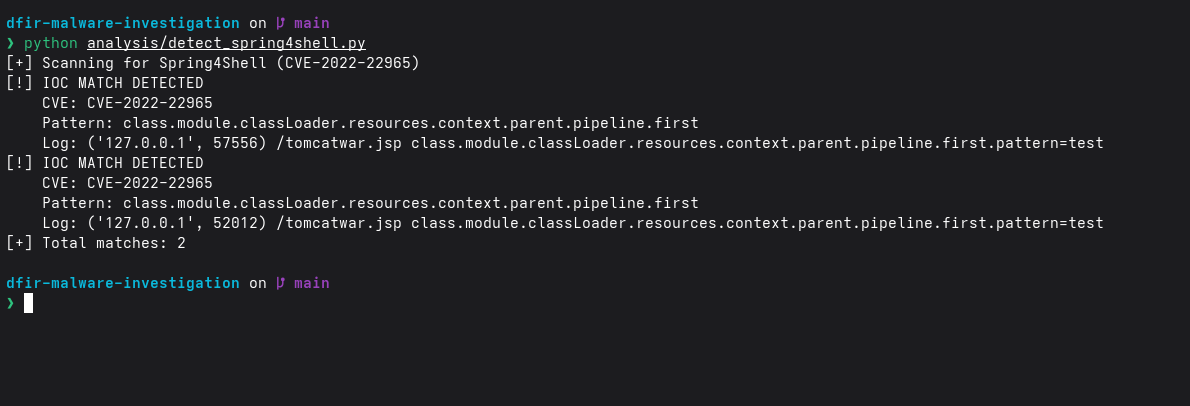 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
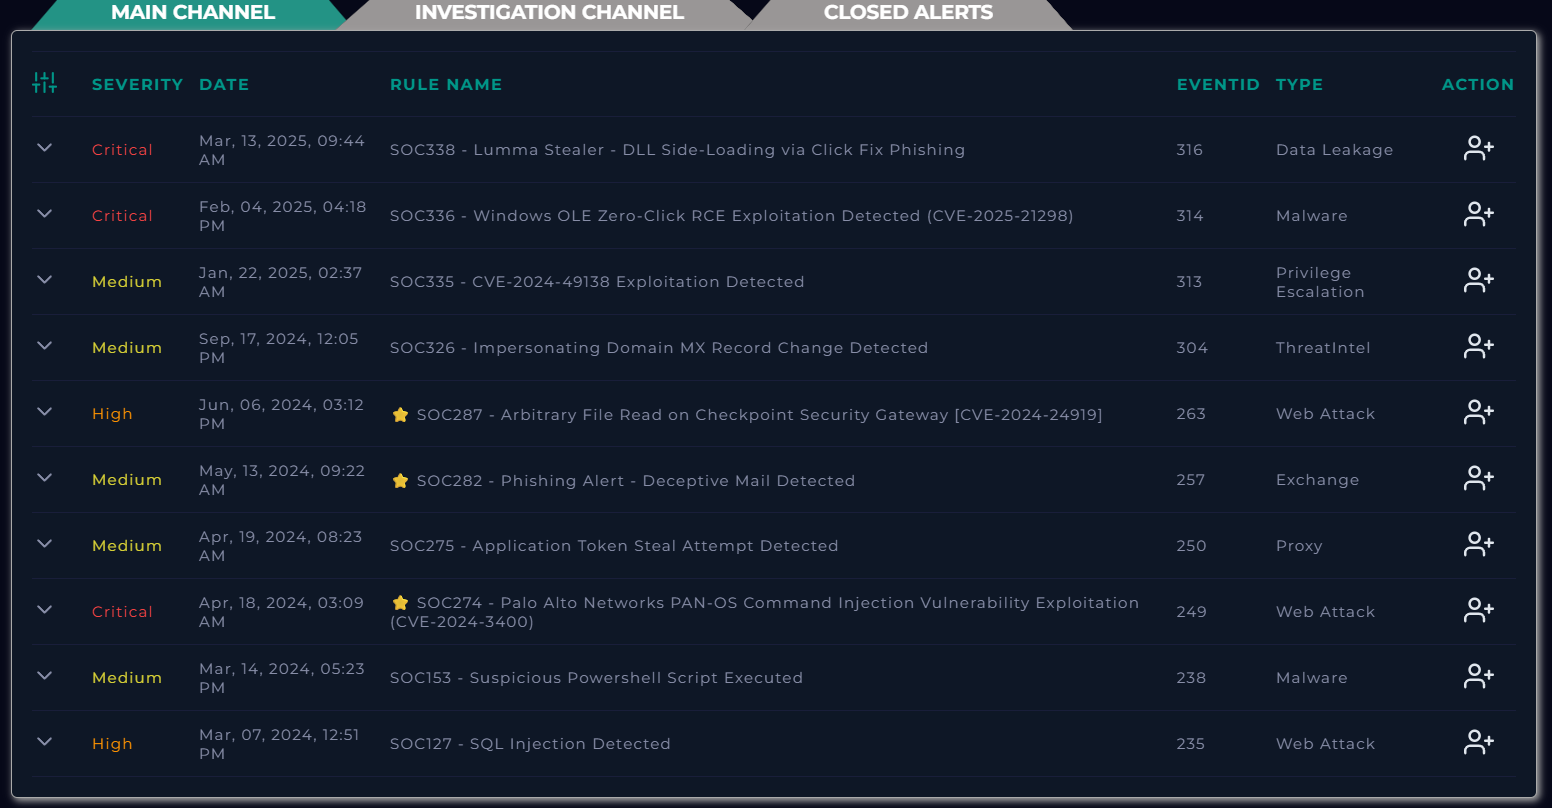 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 zedocun/sharepoint-toolshell-cve-2025-53770-incident-analysis
Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.
 bridg3ops/soc335-cve-2024-49138-exploitation-detected
Detailed incident response walkthrough analyzing CVE-2024-49138 exploitation on Windows, covering process tree analysis, IOC identification, and…
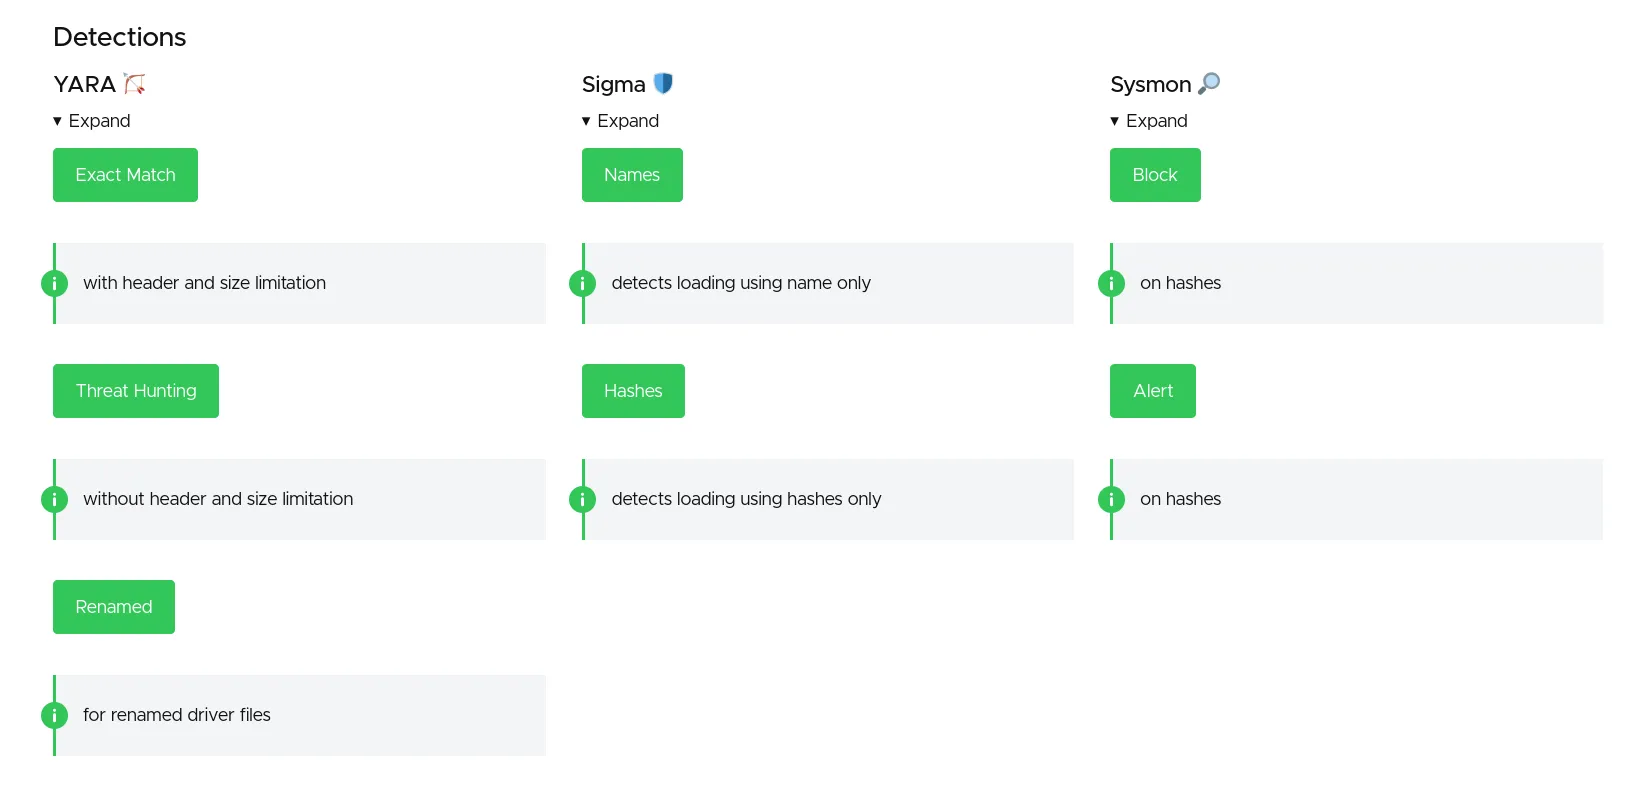 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
