
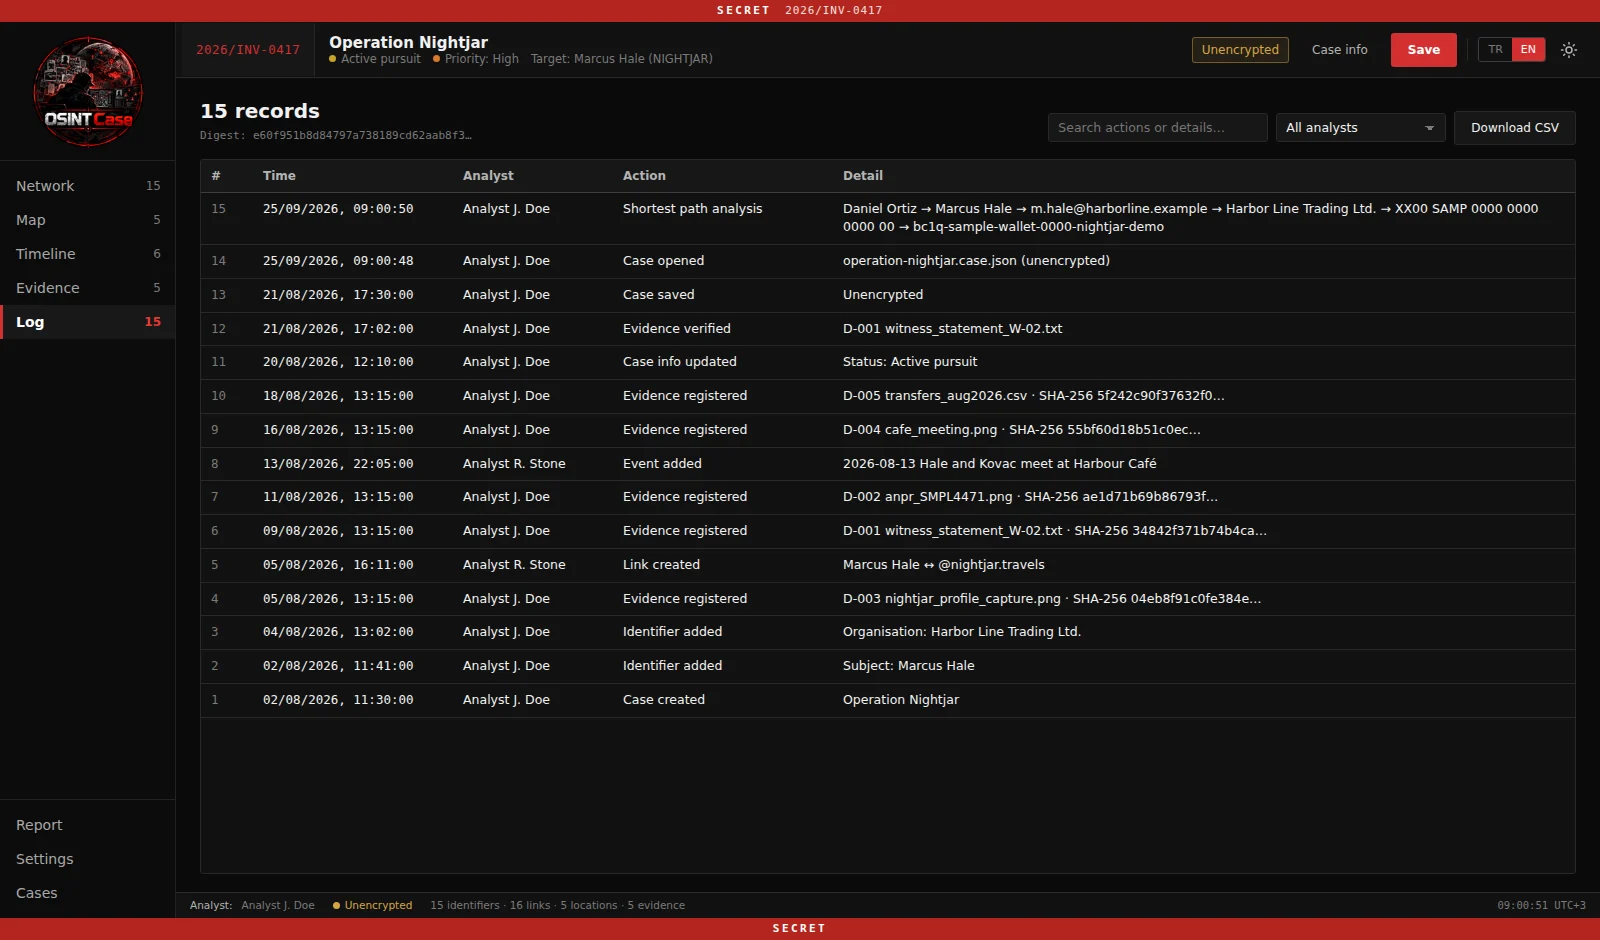
OsintCase
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
curated-resourcesdata-recoverydigital-forensics+6
emrekybs/osintcaseAn OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
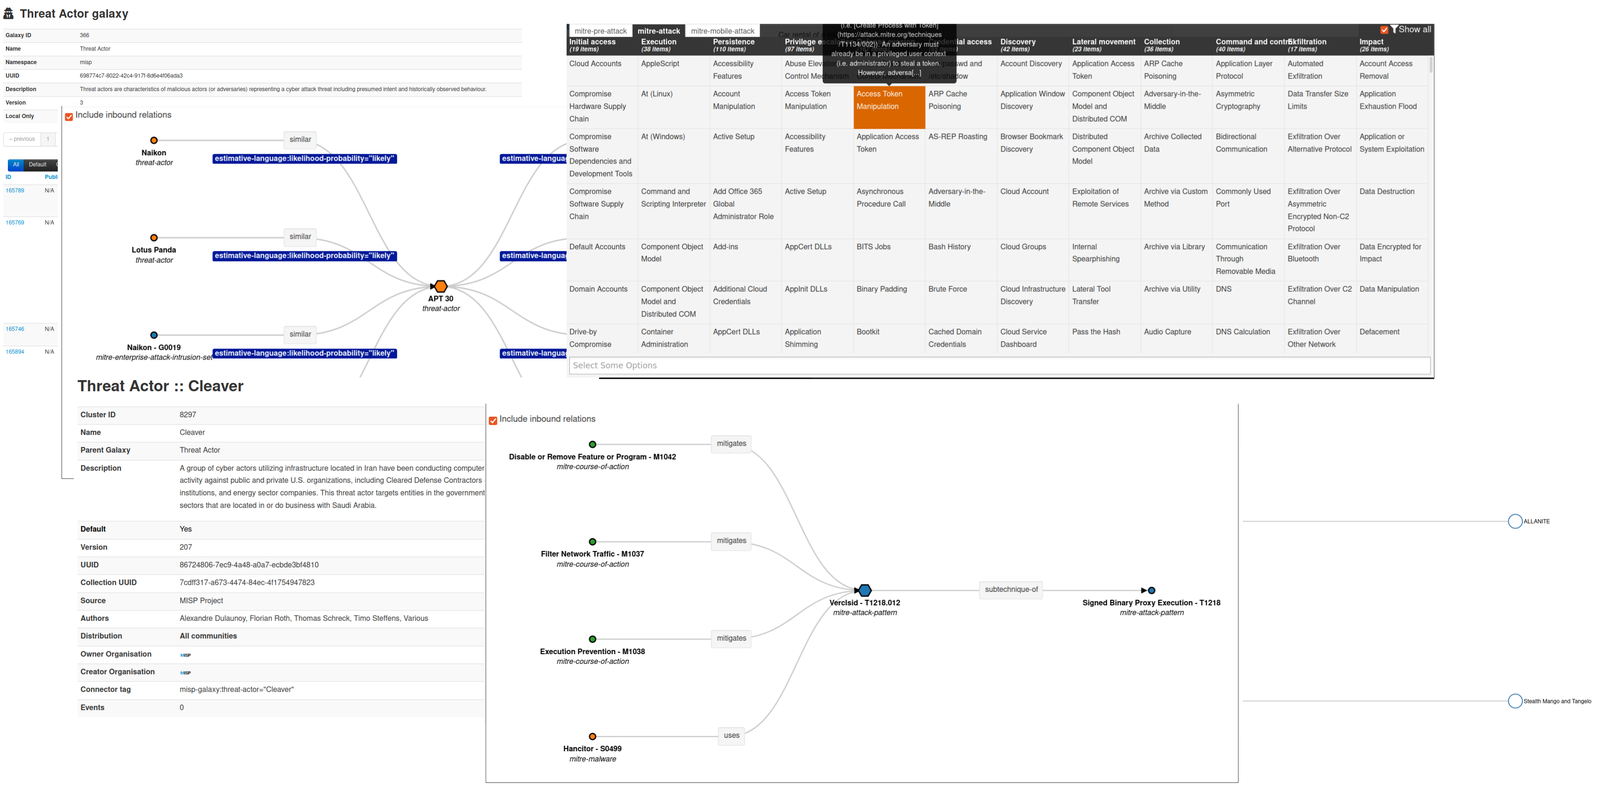 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.

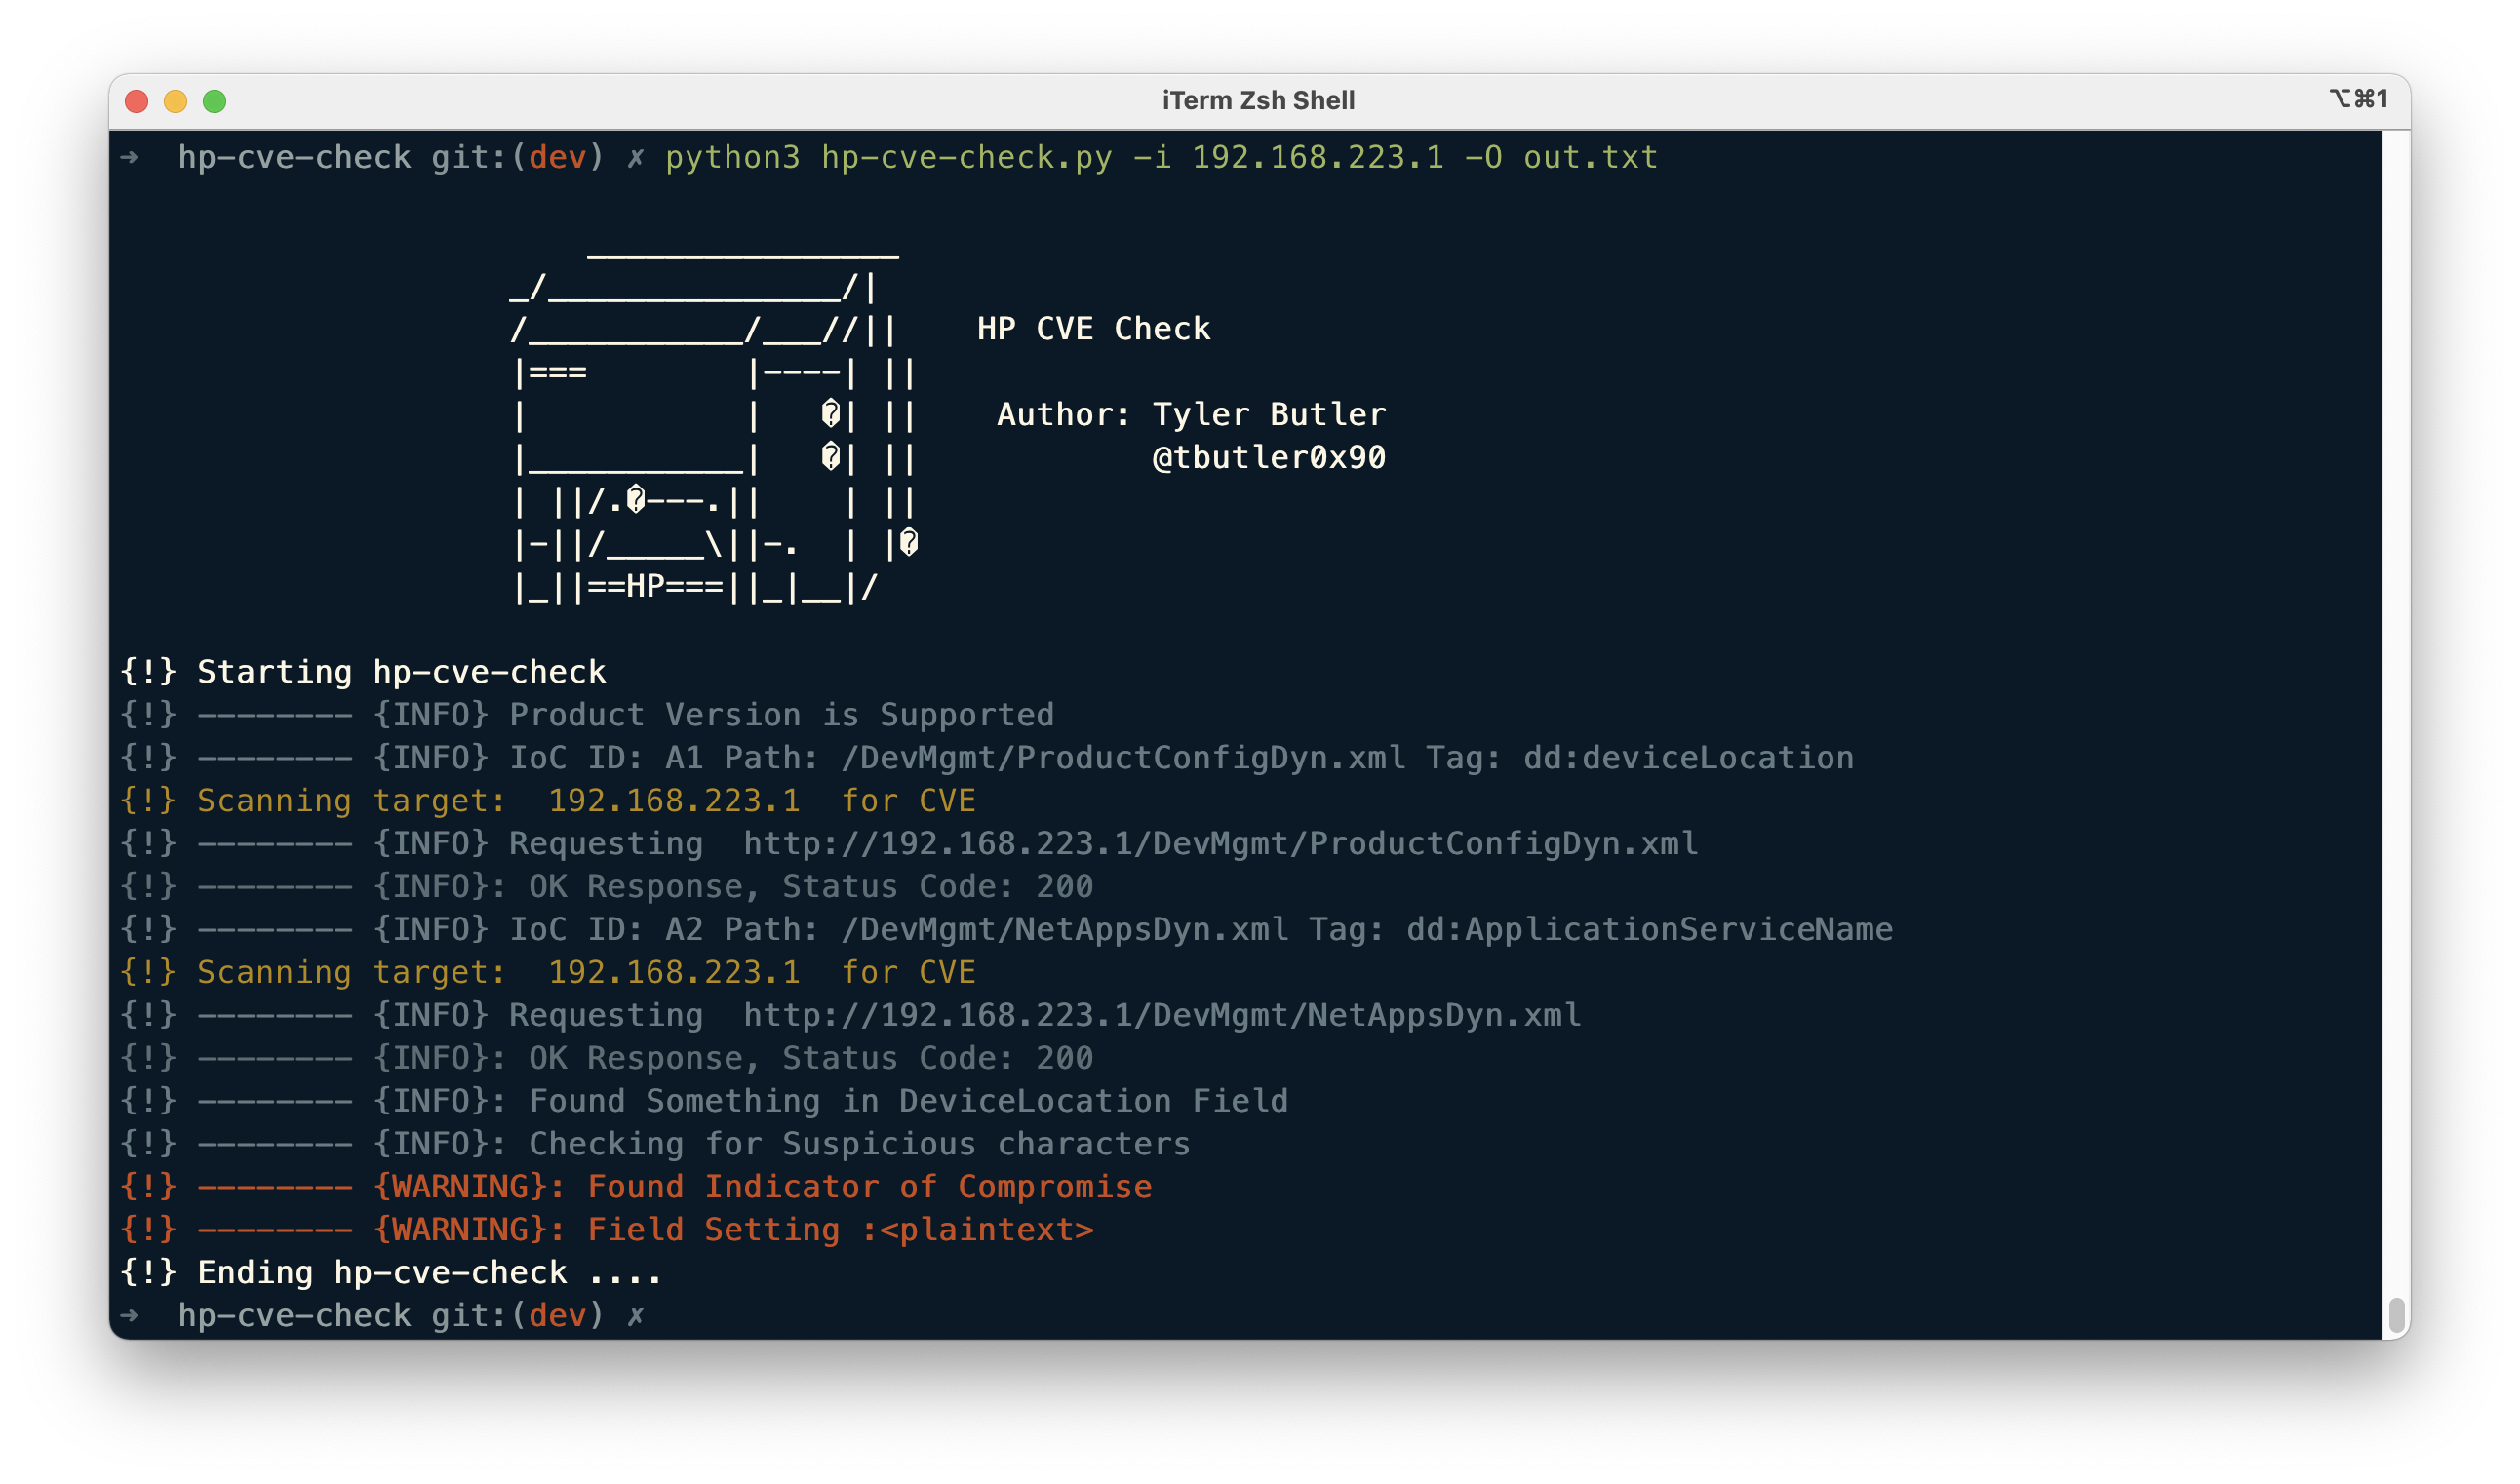 tcbutler320/cve-2021-3441-check
CVE-2021-3441 CVE Check is a python script to search targets for indicators of compromise to CVE-2021-3441
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 onapsis/cve-2020-6287_recon-scanner
Black-box vulnerability scanner and indicator-of-compromise analyzer for CVE-2020-6287 (RECON) in SAP NetWeaver Java applications, enabling rapid…
 gyaansastra/cve-2022-30190
Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…
 cyberdudebivash/cyberdudebivash-cisco-asyncos-cve-2025-20393-scanner
This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…