

Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
151 results
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

anomaly-detectionanti-botdefensive-tools+11
8.6k
7h 54m ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.0k19h 29m ago
darknet-mcp-server preview

darknet-mcp-server

GitHubbadchars/darknet-mcp-server

66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
ai-securitydata-exfiltrationinformation-gathering+8
4618 days ago
citrix-netscaler-triage preview

citrix-netscaler-triage

GitHubfox-it/citrix-netscaler-triage

Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
digital-forensicsincident-responseioc-management+3
7410 months ago
HAFNIUM-IOC preview
Archived

HAFNIUM-IOC

GitHubsoteria-security/hafnium-ioc

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865

digital-forensicsforensicsincident-response+3
225 years ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k22 days ago
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

intrusion-detectionioc-managementnetwork-security+3
9493 days ago
BlueBox preview

BlueBox

GitHubsvdwi/bluebox

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
ioc-managementmachine-learningmalware-analysis+4
504 years ago
destroylist preview

destroylist

GitHubphishdestroy/destroylist

Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats

curated-resourcesdefensive-toolsdns-analysis+8
1.9k13h 26m ago
ndaal_public_SBOM_Auditor preview

ndaal_public_SBOM_Auditor

GitLabvpierre/ndaal_public_sbom_auditor

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

configuration-auditingdefensive-toolsdevsecops+7
7 days ago
Exploitarium-Detections preview

Exploitarium-Detections

GitHubethan-andrews/exploitarium-detections

KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…

educationincident-responseintrusion-detection+3
5017 days ago
awesome-lists preview

awesome-lists

GitHubmthcht/awesome-lists

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
1.9k10h 20m ago
Data-Shield_IPv4_Blocklist preview

Data-Shield_IPv4_Blocklist

GitHubduggytuxy/data-shield_ipv4_blocklist

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

defensive-toolsincident-responseinformation-gathering+5
6071 day ago
opencve preview

opencve

GitHubopencve/opencve

Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
incident-responseioc-managementthreat-intelligence+2
2.8k14h 48m ago
ioc-scanner-CVE-2019-19781 preview

ioc-scanner-CVE-2019-19781

GitHubcitrix/ioc-scanner-cve-2019-19781

Indicator of Compromise Scanner for CVE-2019-19781
digital-forensicsforensicsincident-response+5
586 years ago
douglas-042-HQ preview

douglas-042-HQ

GitHubdouglas-042/douglas-042-hq

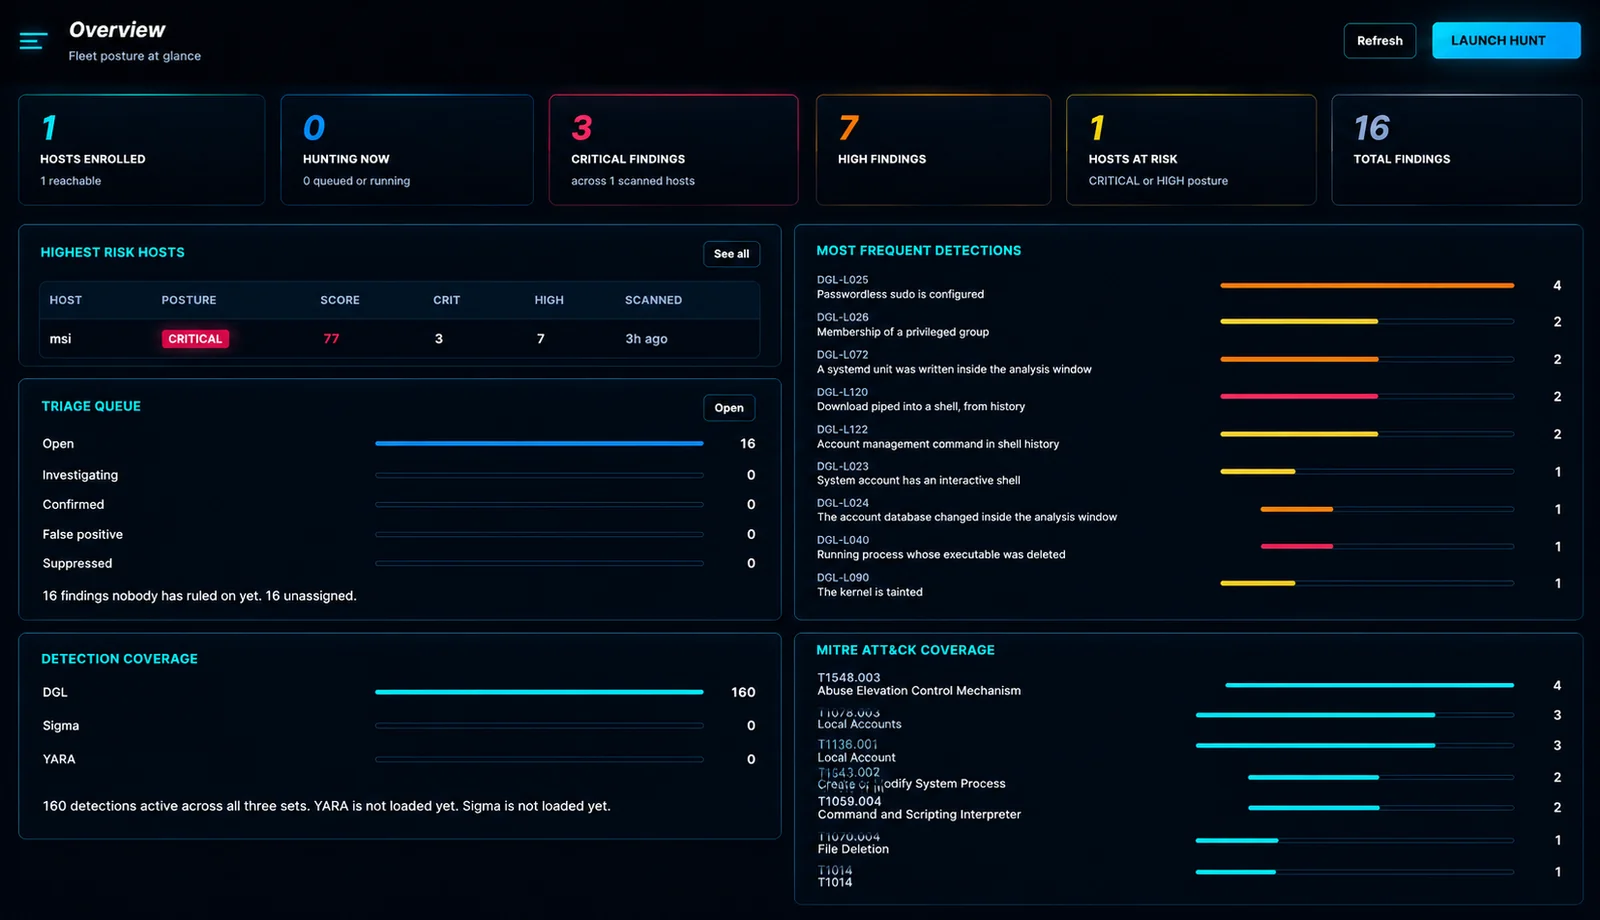
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
defensive-toolsforensicsincident-response+5
1 month ago
VolWeb preview

VolWeb

GitHubk1nd0ne/volweb

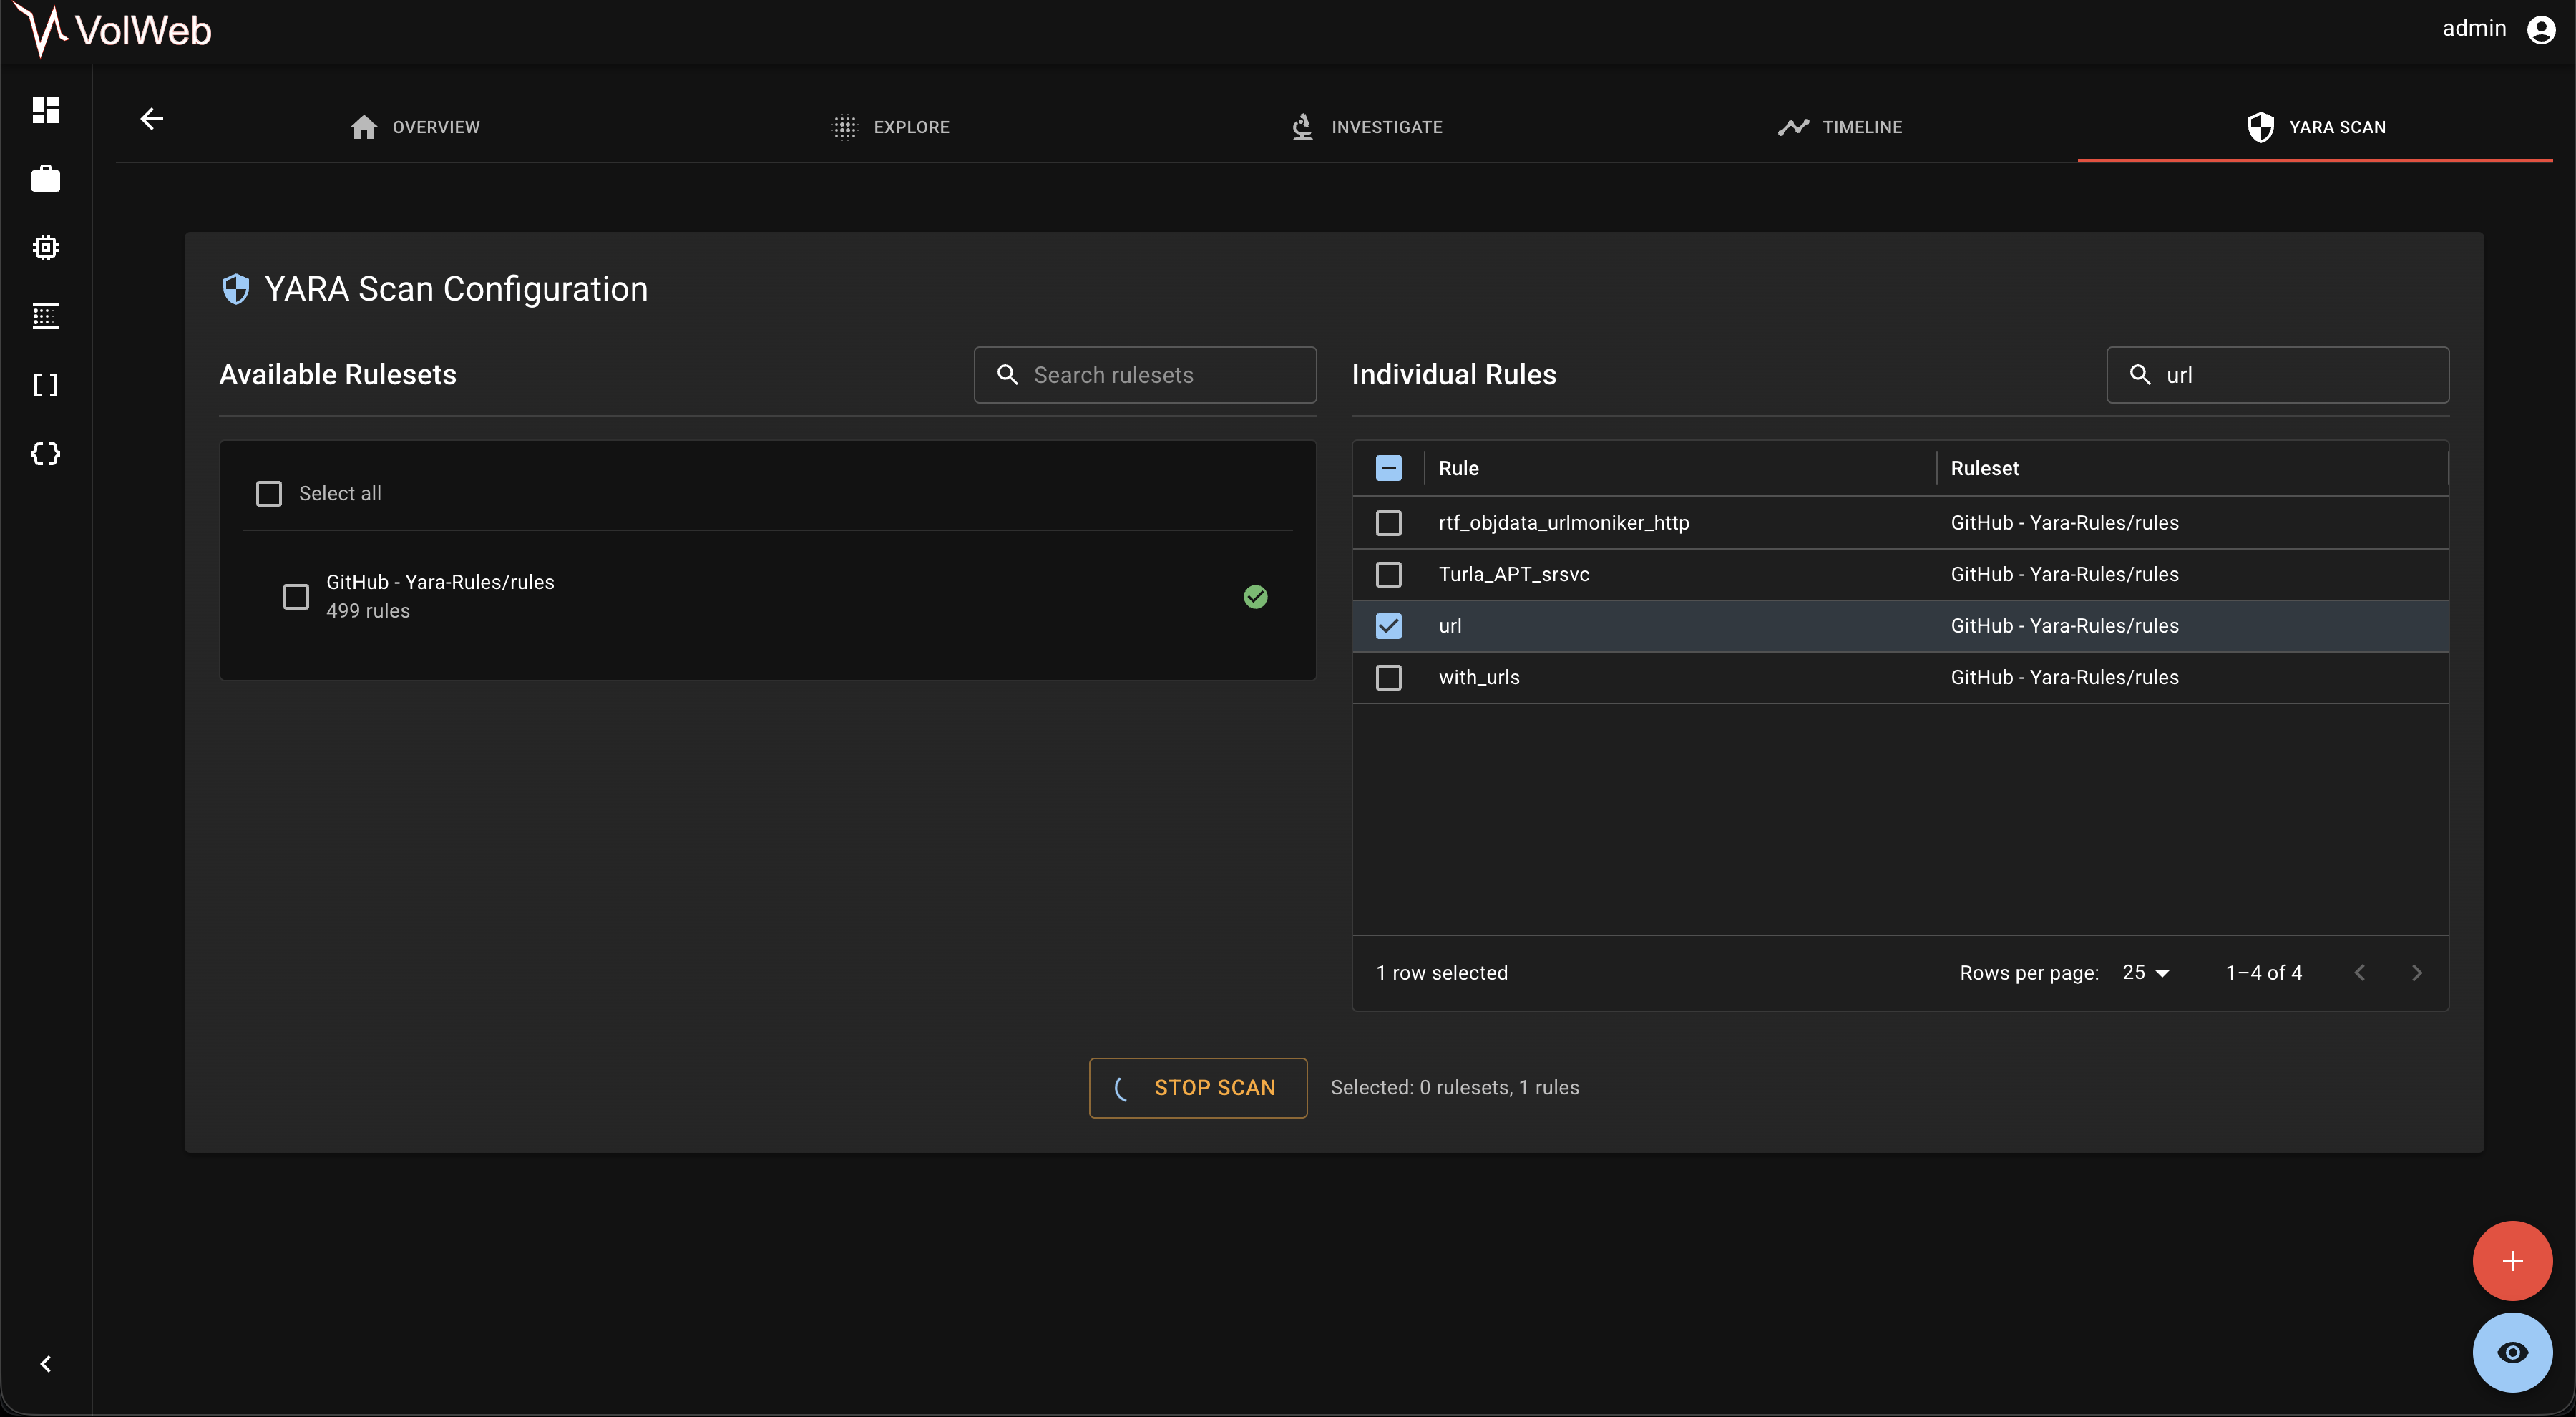
A centralized and enhanced memory analysis platform
digital-forensicseducationforensics+5
5381 day ago
Threat-Intelligence-Hunter preview

Threat-Intelligence-Hunter

GitHubabhinavbom/threat-intelligence-hunter

TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…

information-gatheringioc-managementosint+1
1568 years ago
Previous12…9Next