
Exploit-Index
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
curated-resourcesexploitationinformation-gathering+8
102
securewithumer/exploit-indexZero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 vulncheck-oss/cli
VulnCheck's official command line tool
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
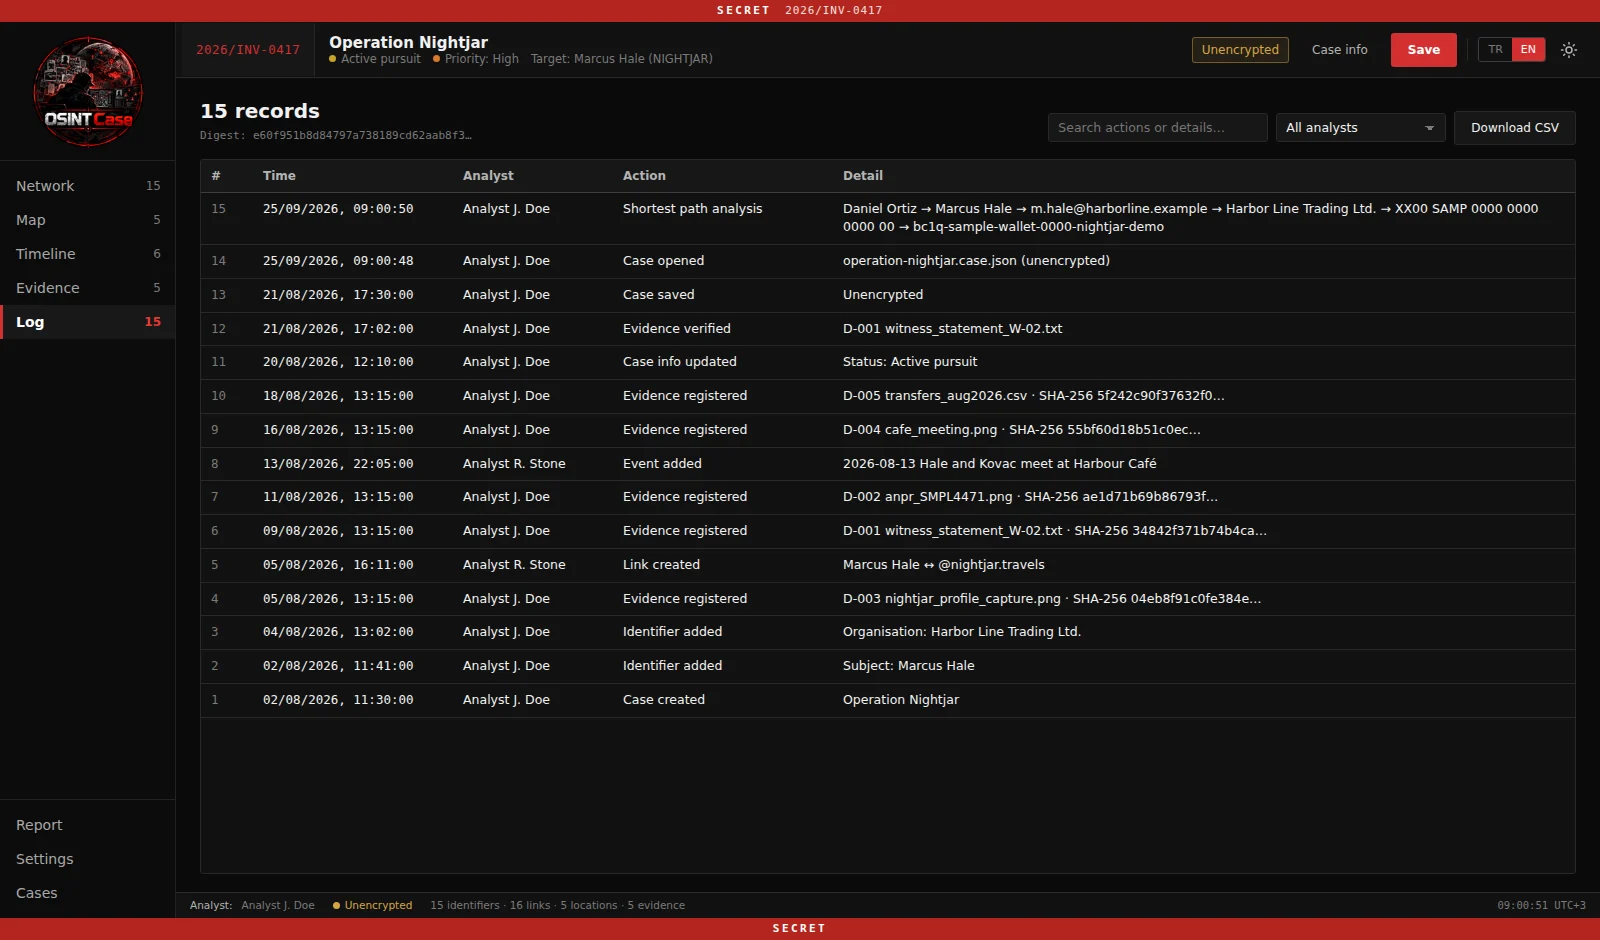 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 deepfield/public-research
DDoS botnet research and indicators of compromise from Nokia Deepfield ERT