Open-Source-Threat-Intel-Feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis

Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…

TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.

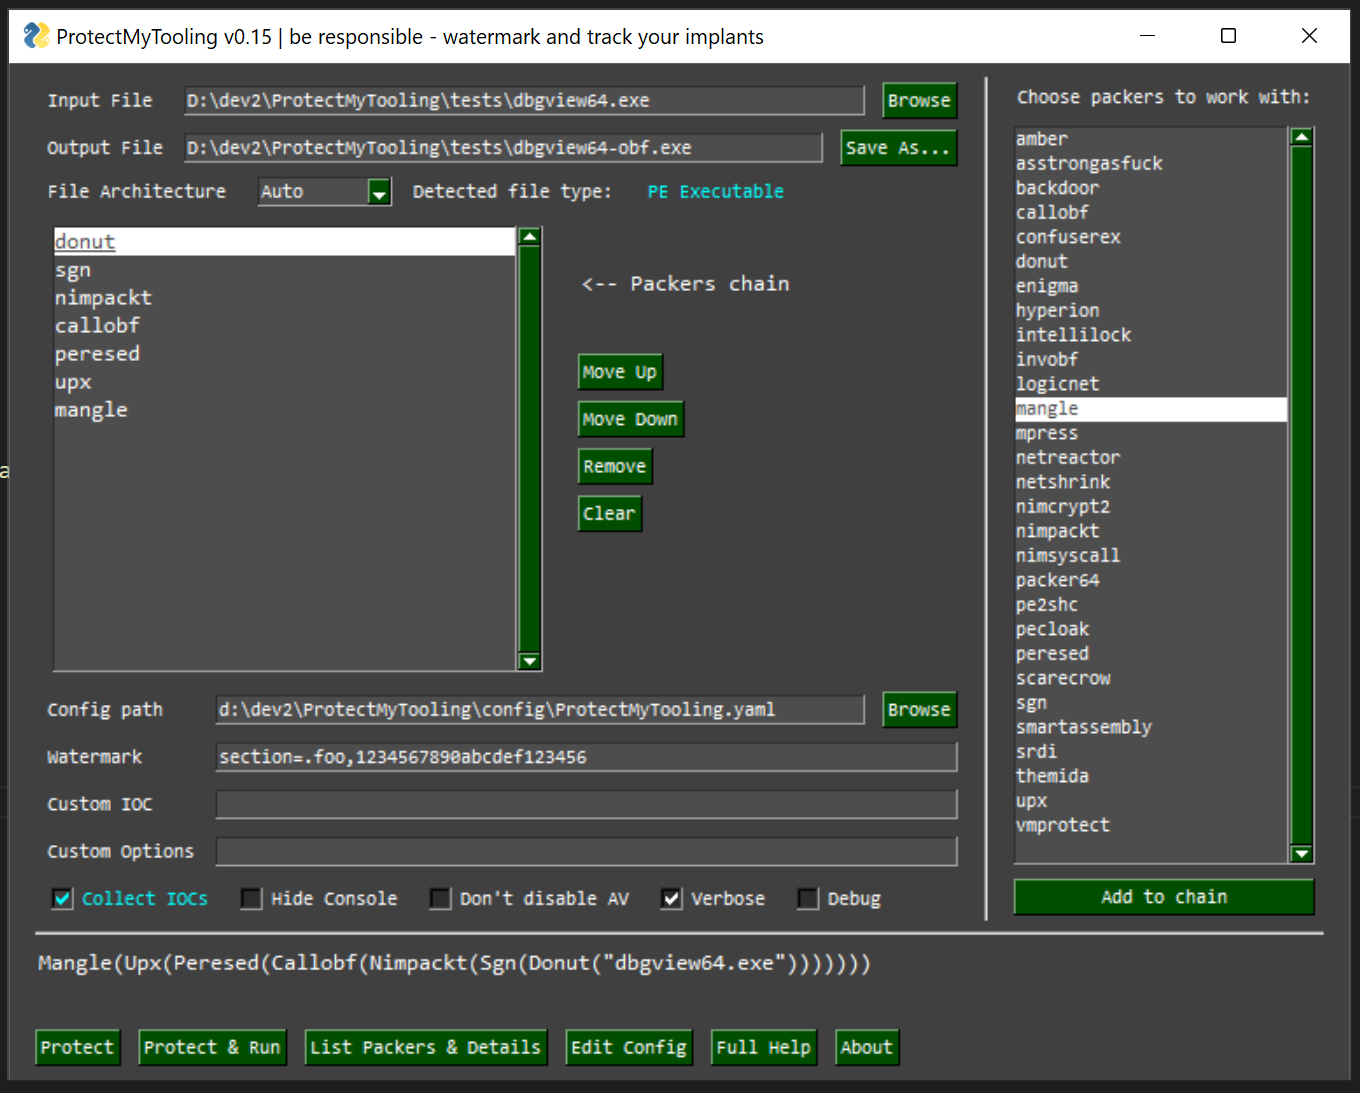
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…

log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)

Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.

Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.