
Exploit-Index
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
curated-resourcesexploitationinformation-gathering+8
102
securewithumer/exploit-indexZero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 happyhackingspace/claude-code-backdoor-check
Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…
 emcghee/payloadautomation
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
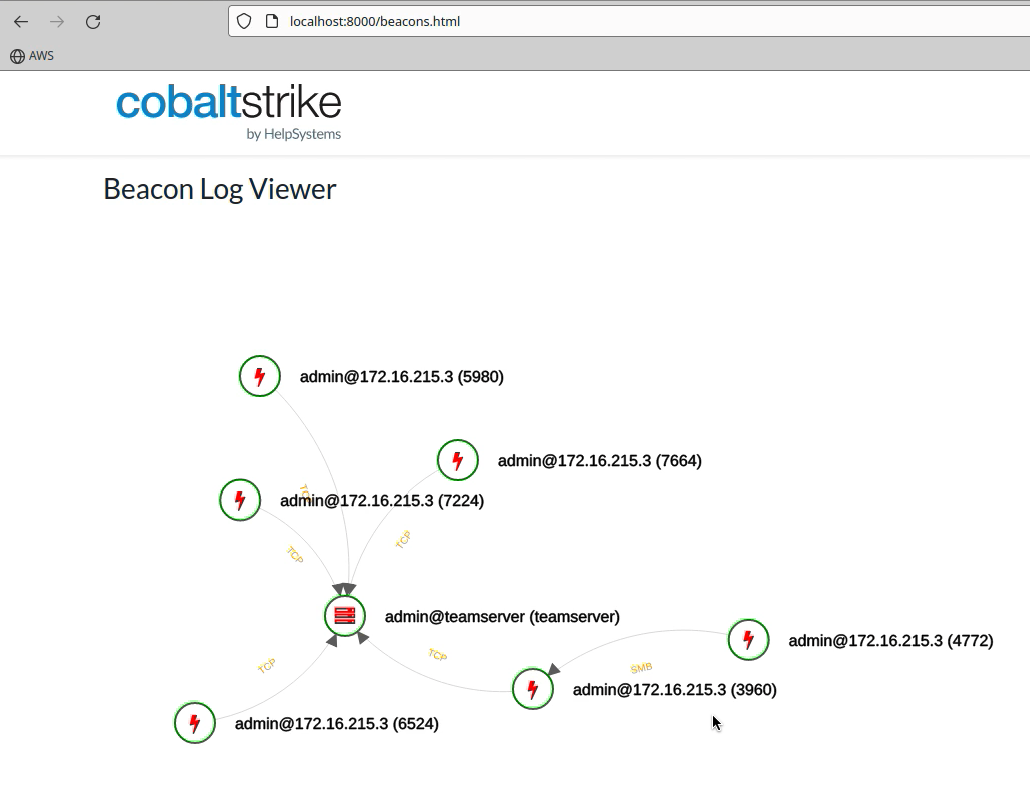 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 salaheldinfikri/kalim_backdoor
Kalim backdooe Malware Report
 creamyg31337/ncentral-compromise-ioc-triage
Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints
