

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
13.1k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 deepfield/public-research
DDoS botnet research and indicators of compromise from Nokia Deepfield ERT
 soteria-security/hafnium-ioc
A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
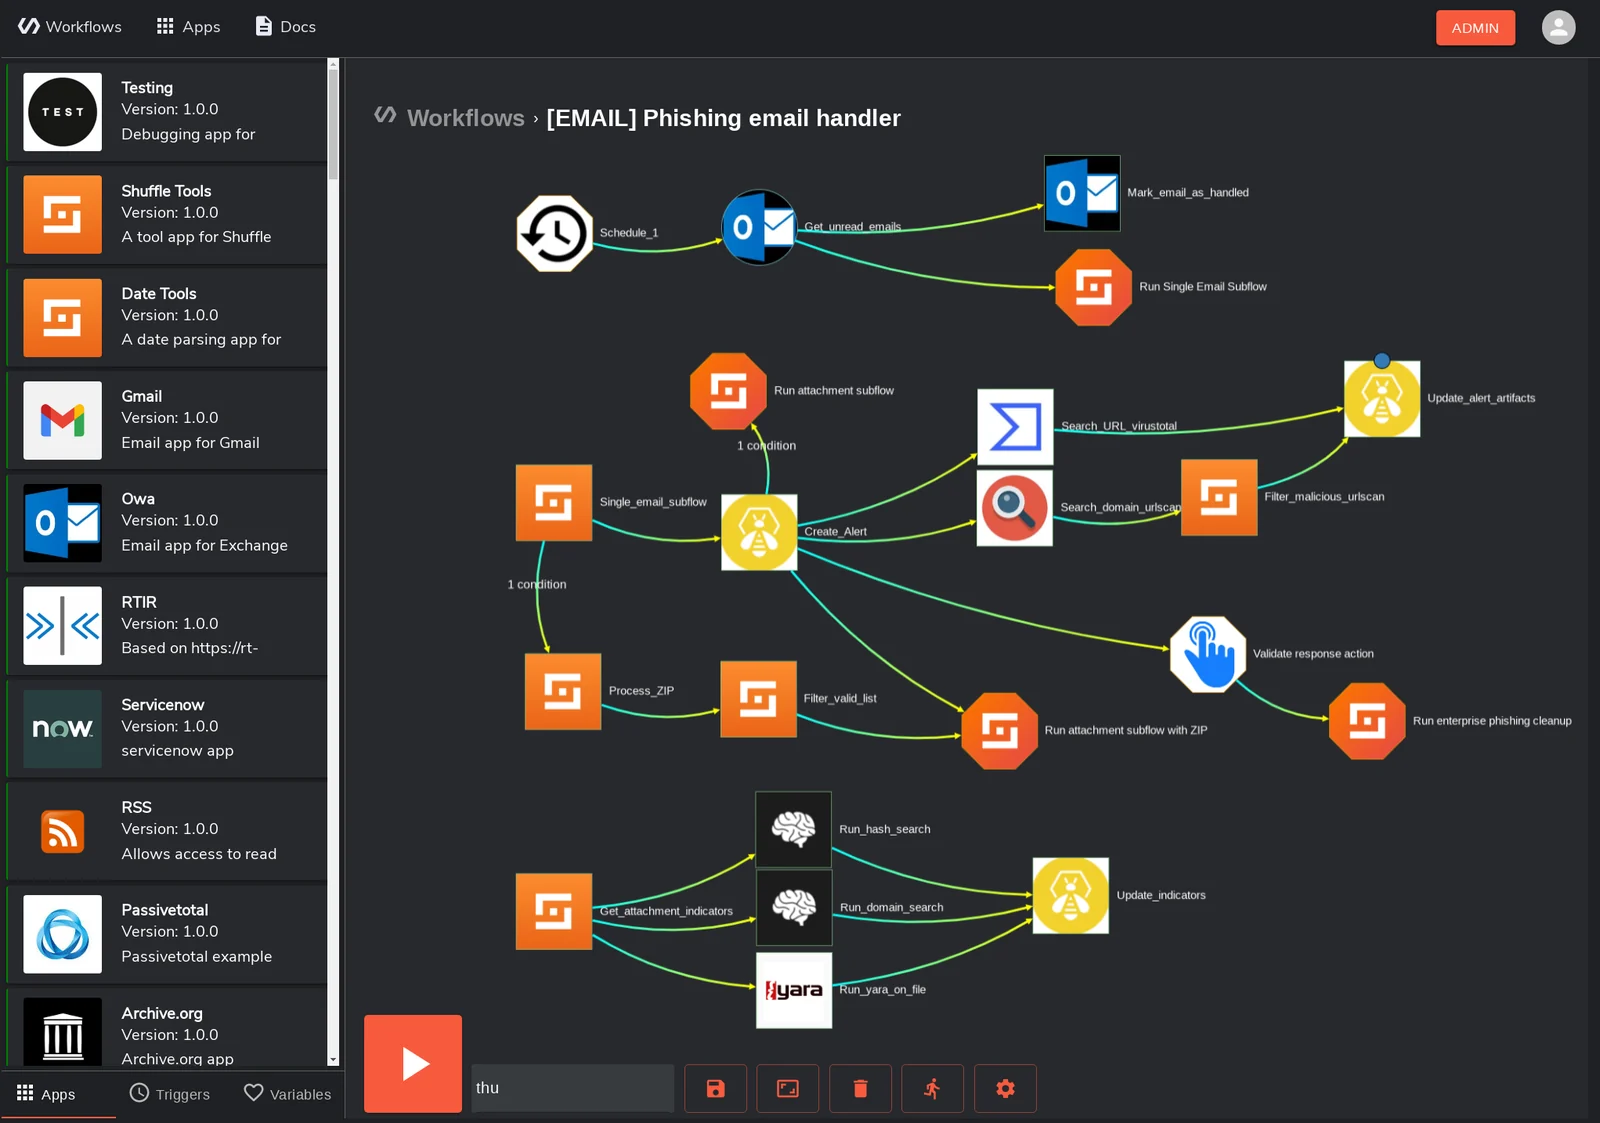 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 sh0ckfr/log4j-cve-2021-44228-public-iocs
Public IoCs about log4j CVE-2021-44228
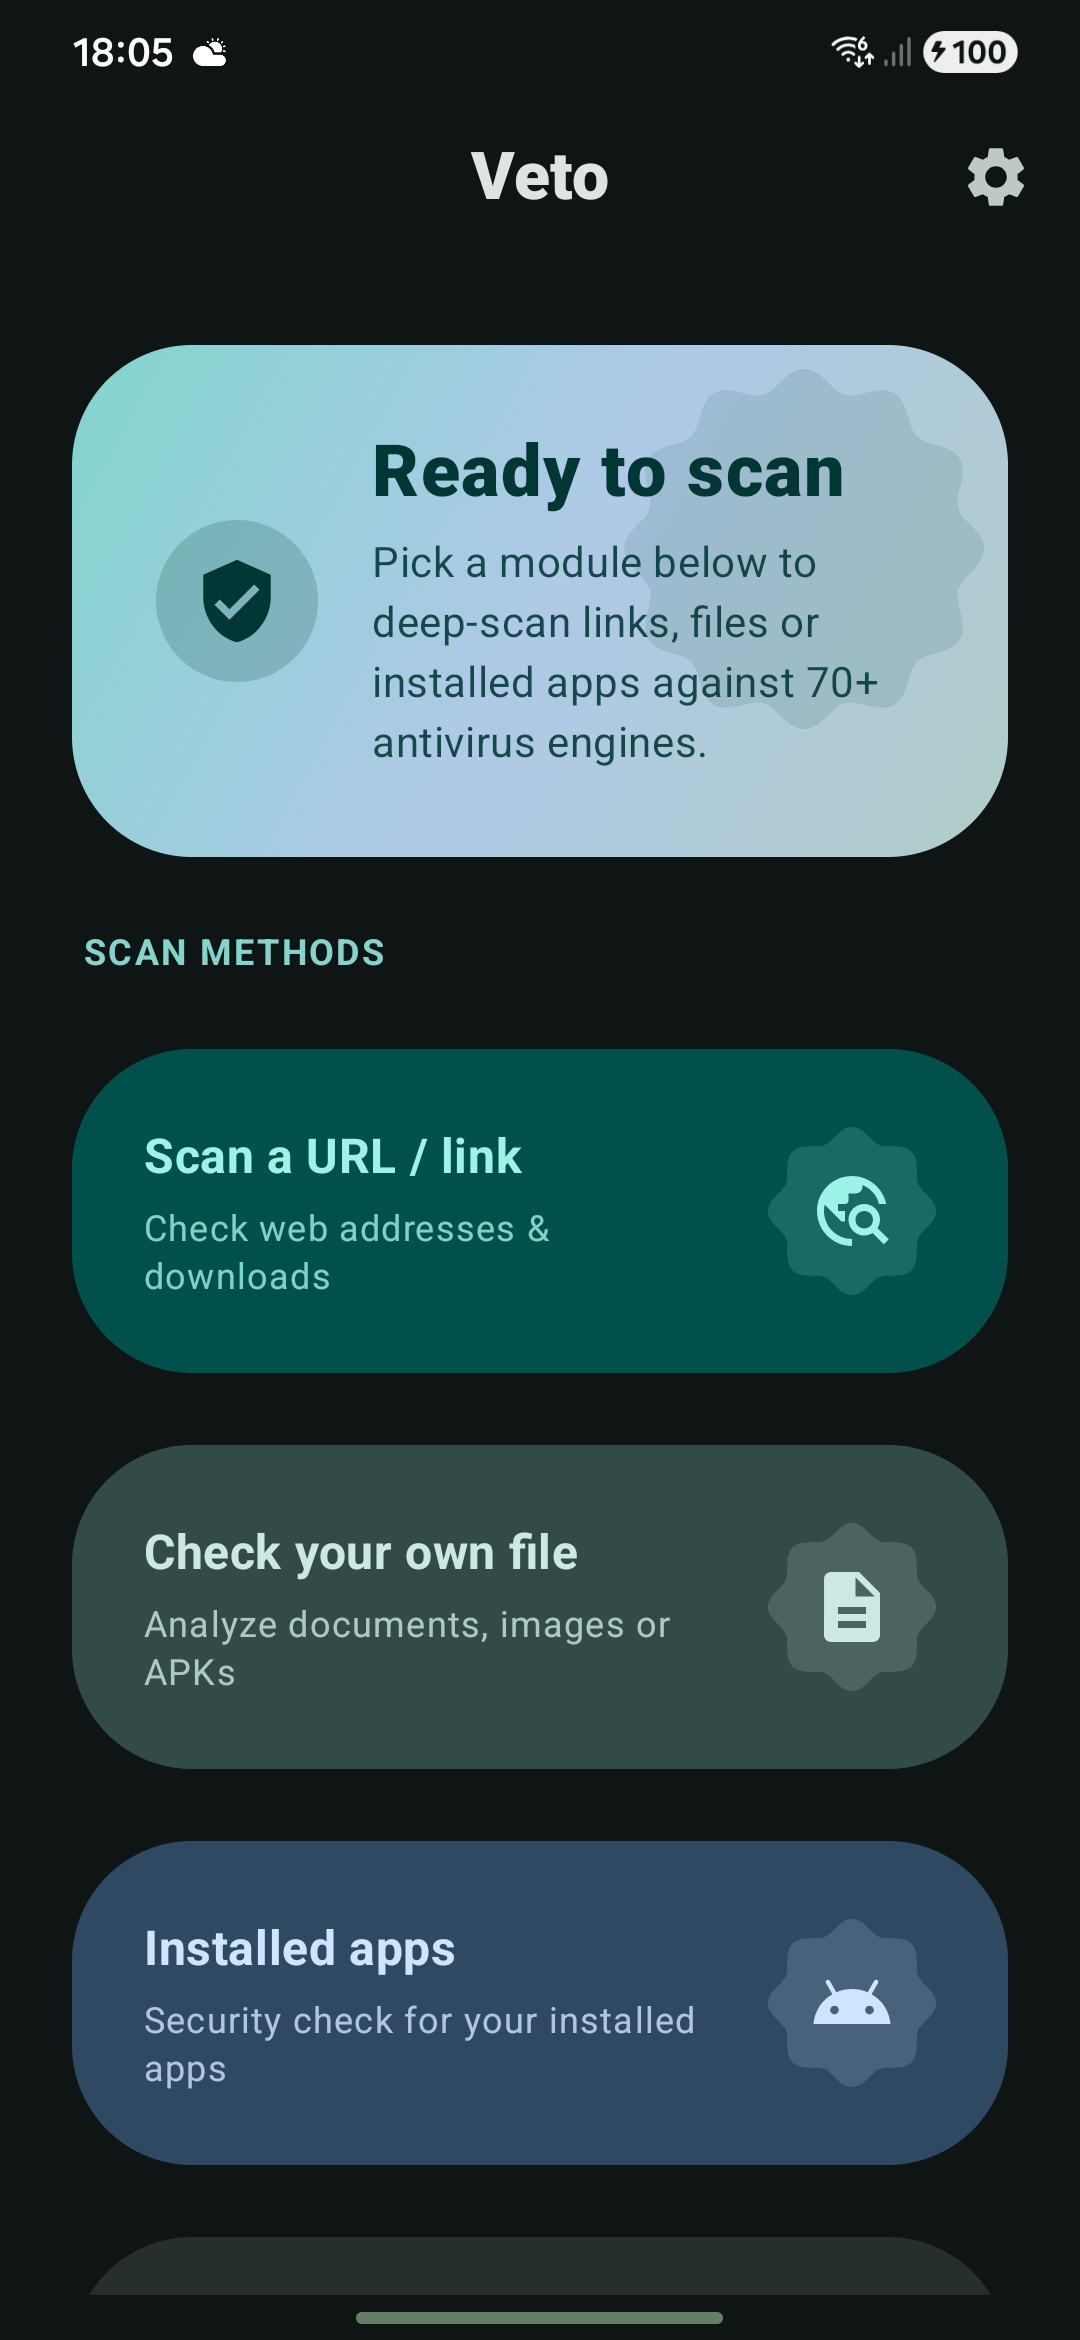 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
 rjsudlow/proxynotshell-ioc-checker
Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
 paloaltonetworks/unit42-threat-intelligence-article-information
This is the repository for indicators of compromise (IOCs) and other data for threat intelligence articles posted on the Palo Alto Networks Unit 42…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…