cpanel-cve-41940-detector
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
digital-forensicsforensicsincident-response+6
limo57640-crypto/cpanel-cve-41940-detectorRead-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
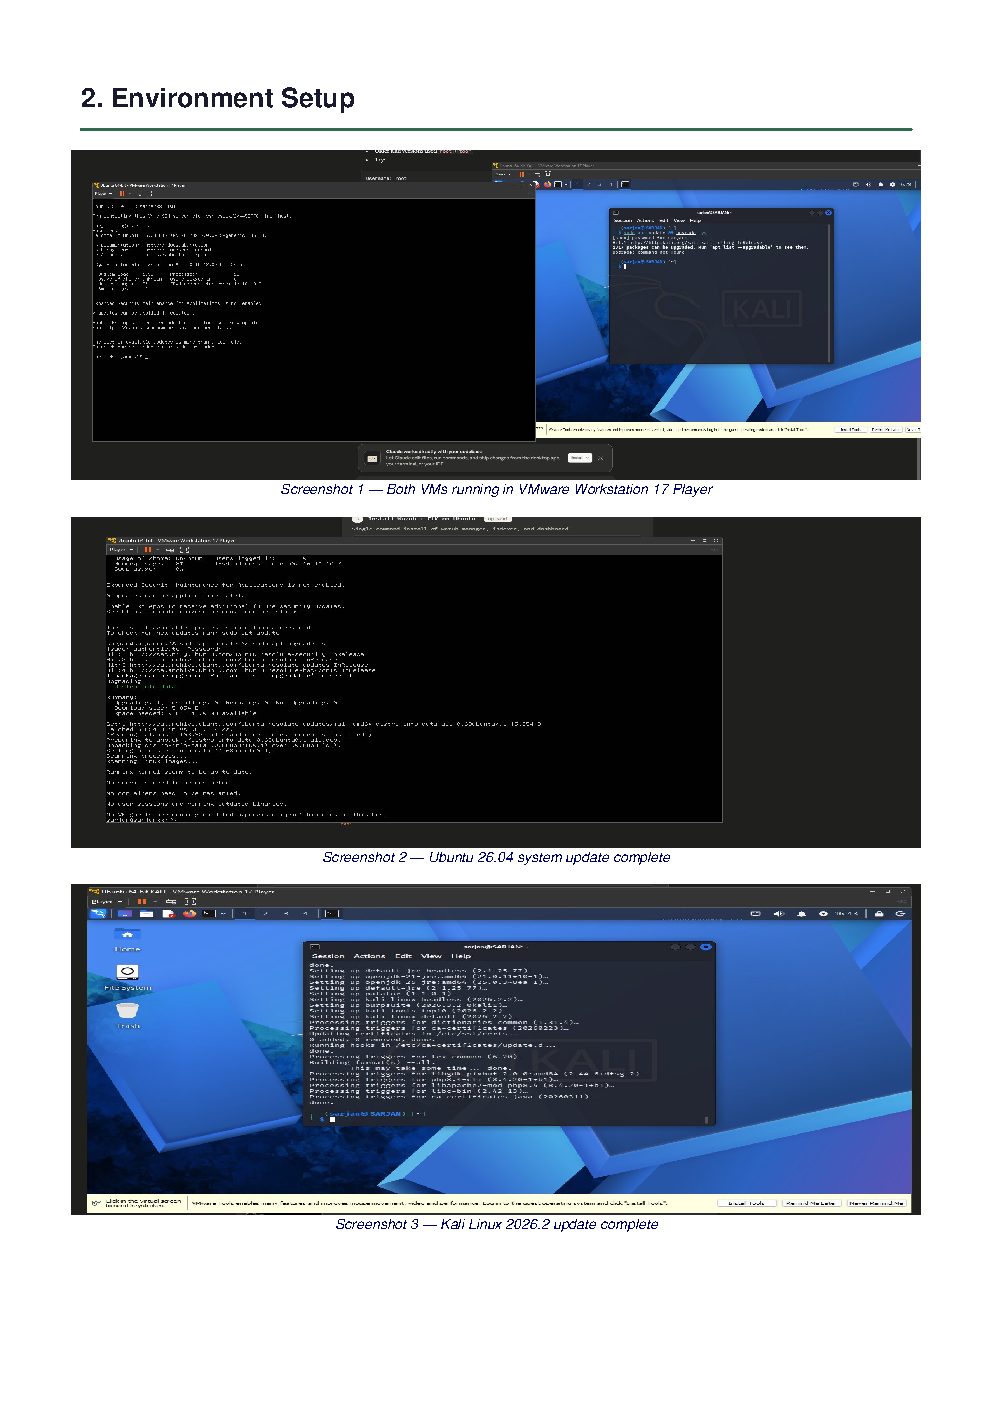 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
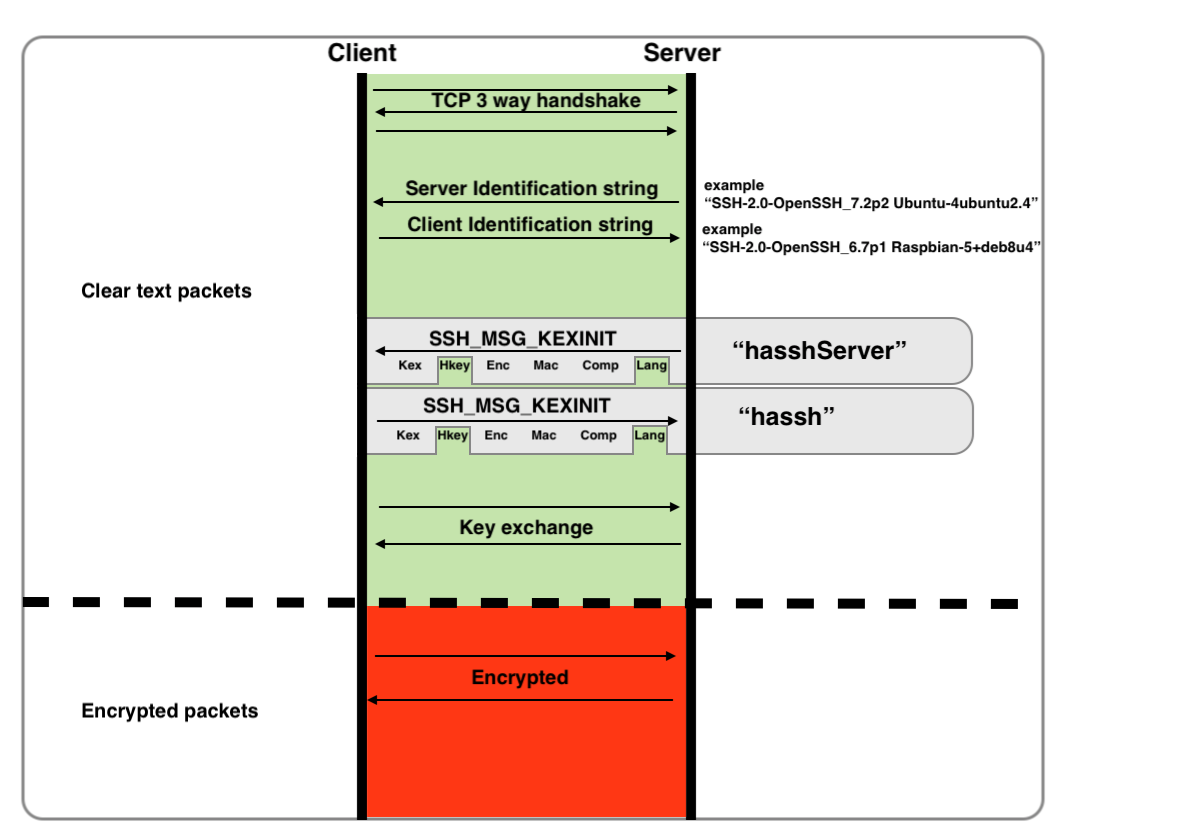 corelight/hassh
Fingerprint SSH clients and servers.
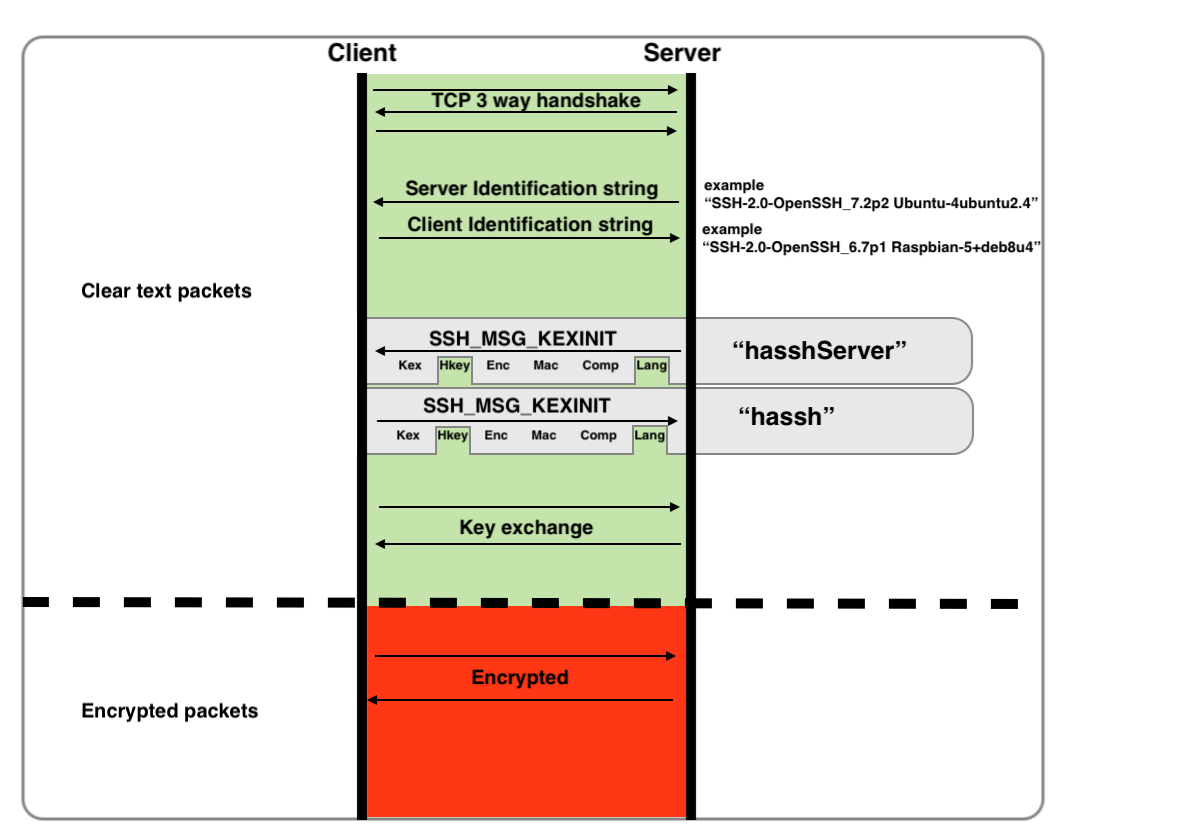 salesforce/hassh
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
 secdev02/cyber-decoy
Experimental Decoy Broker
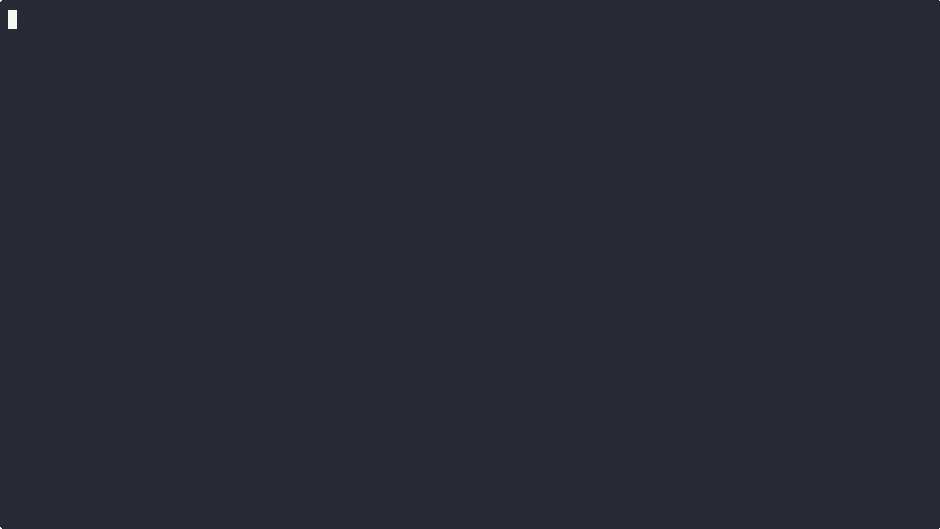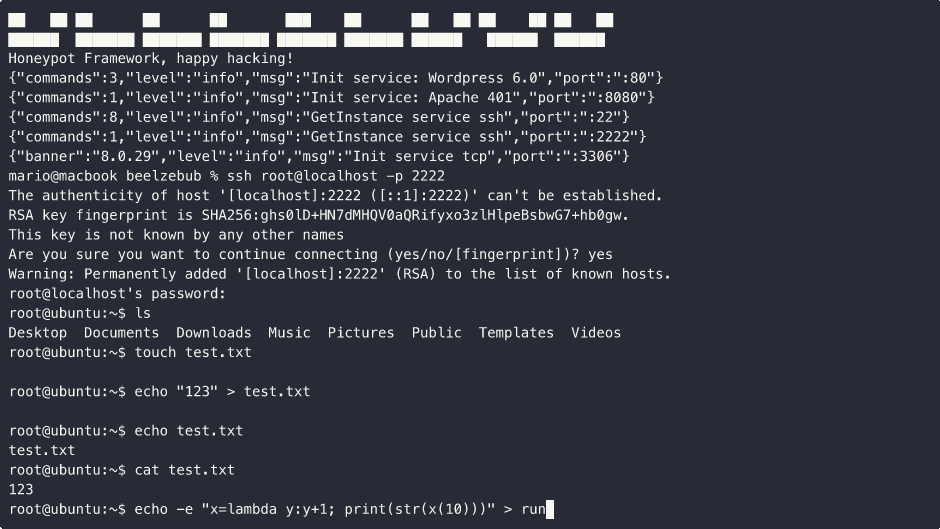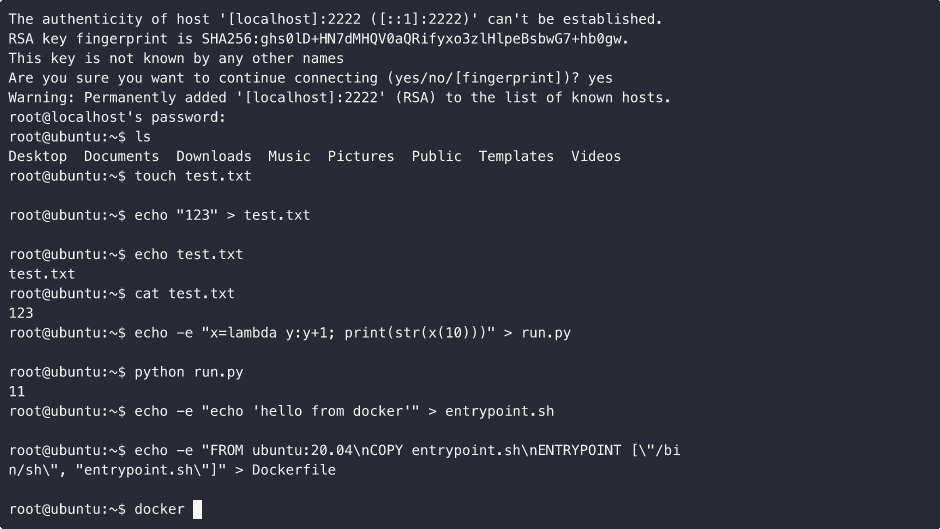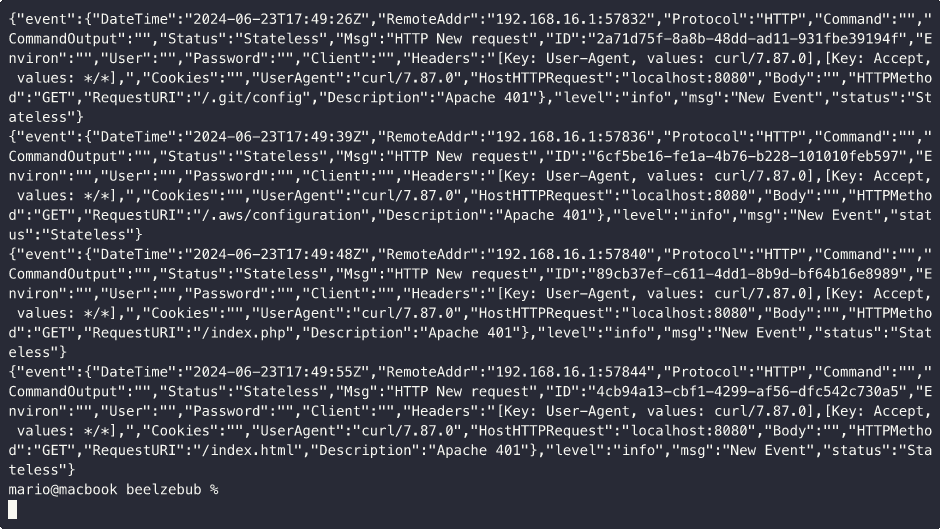 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
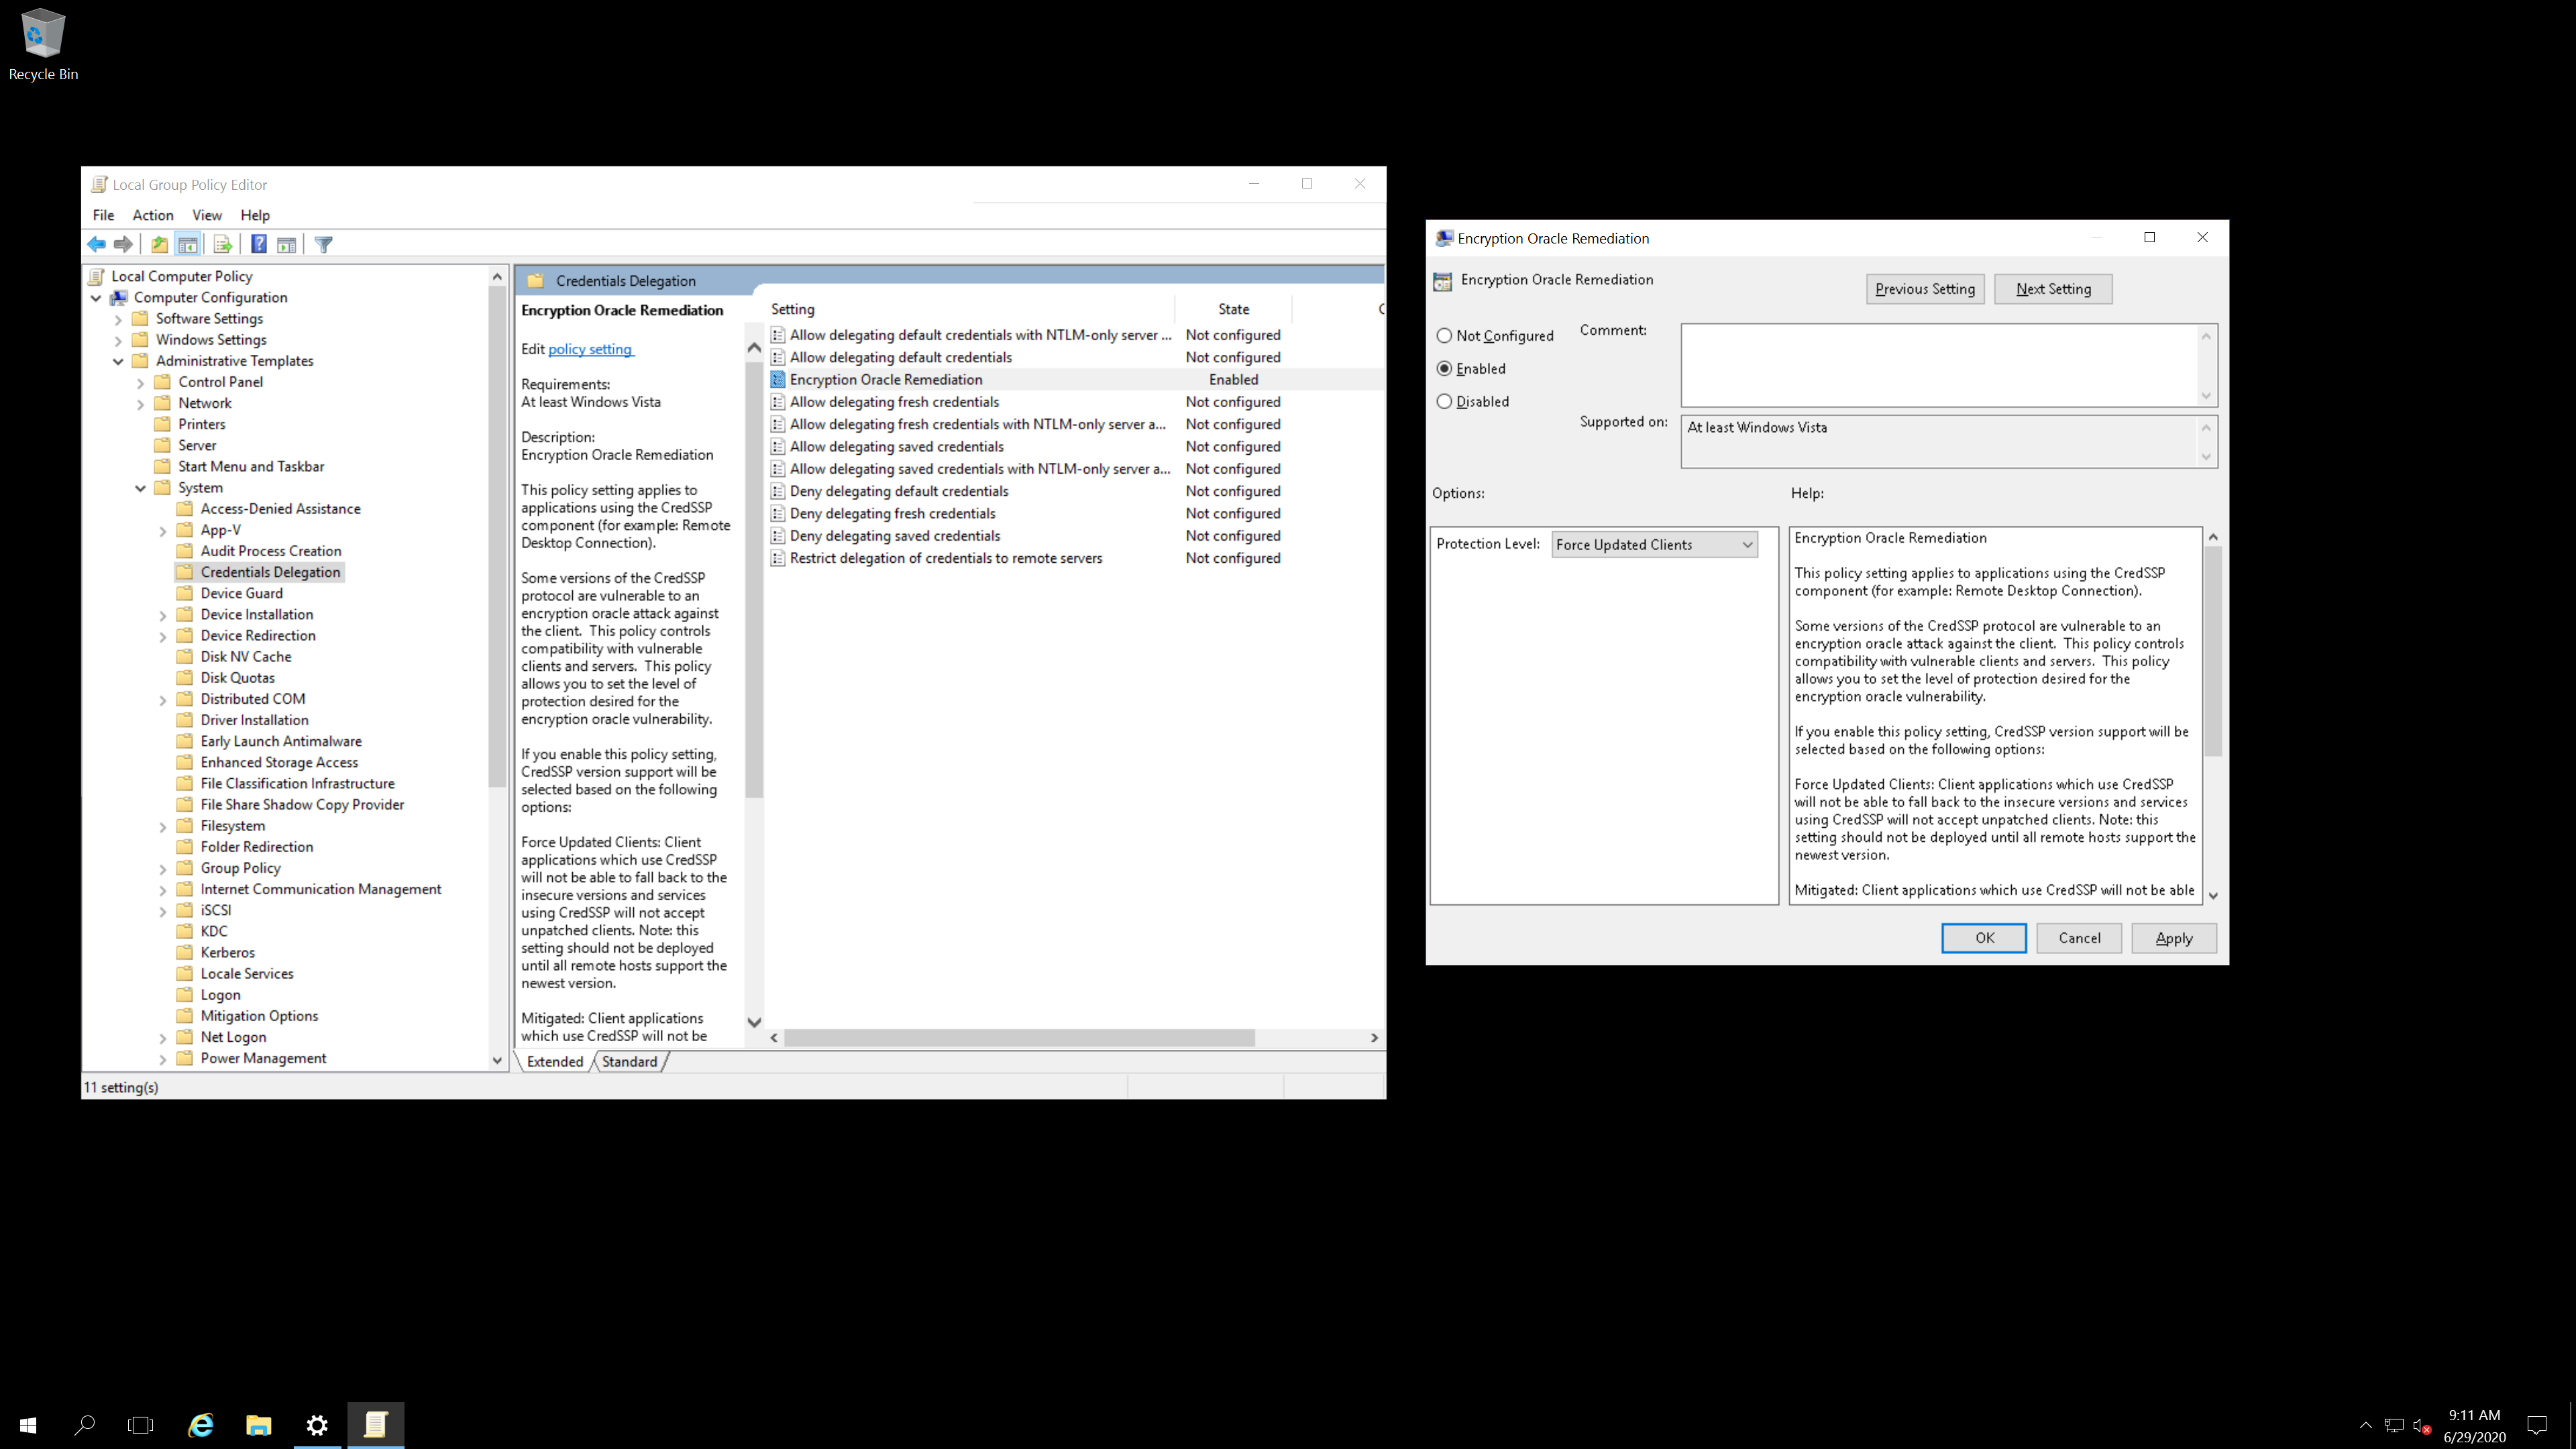 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
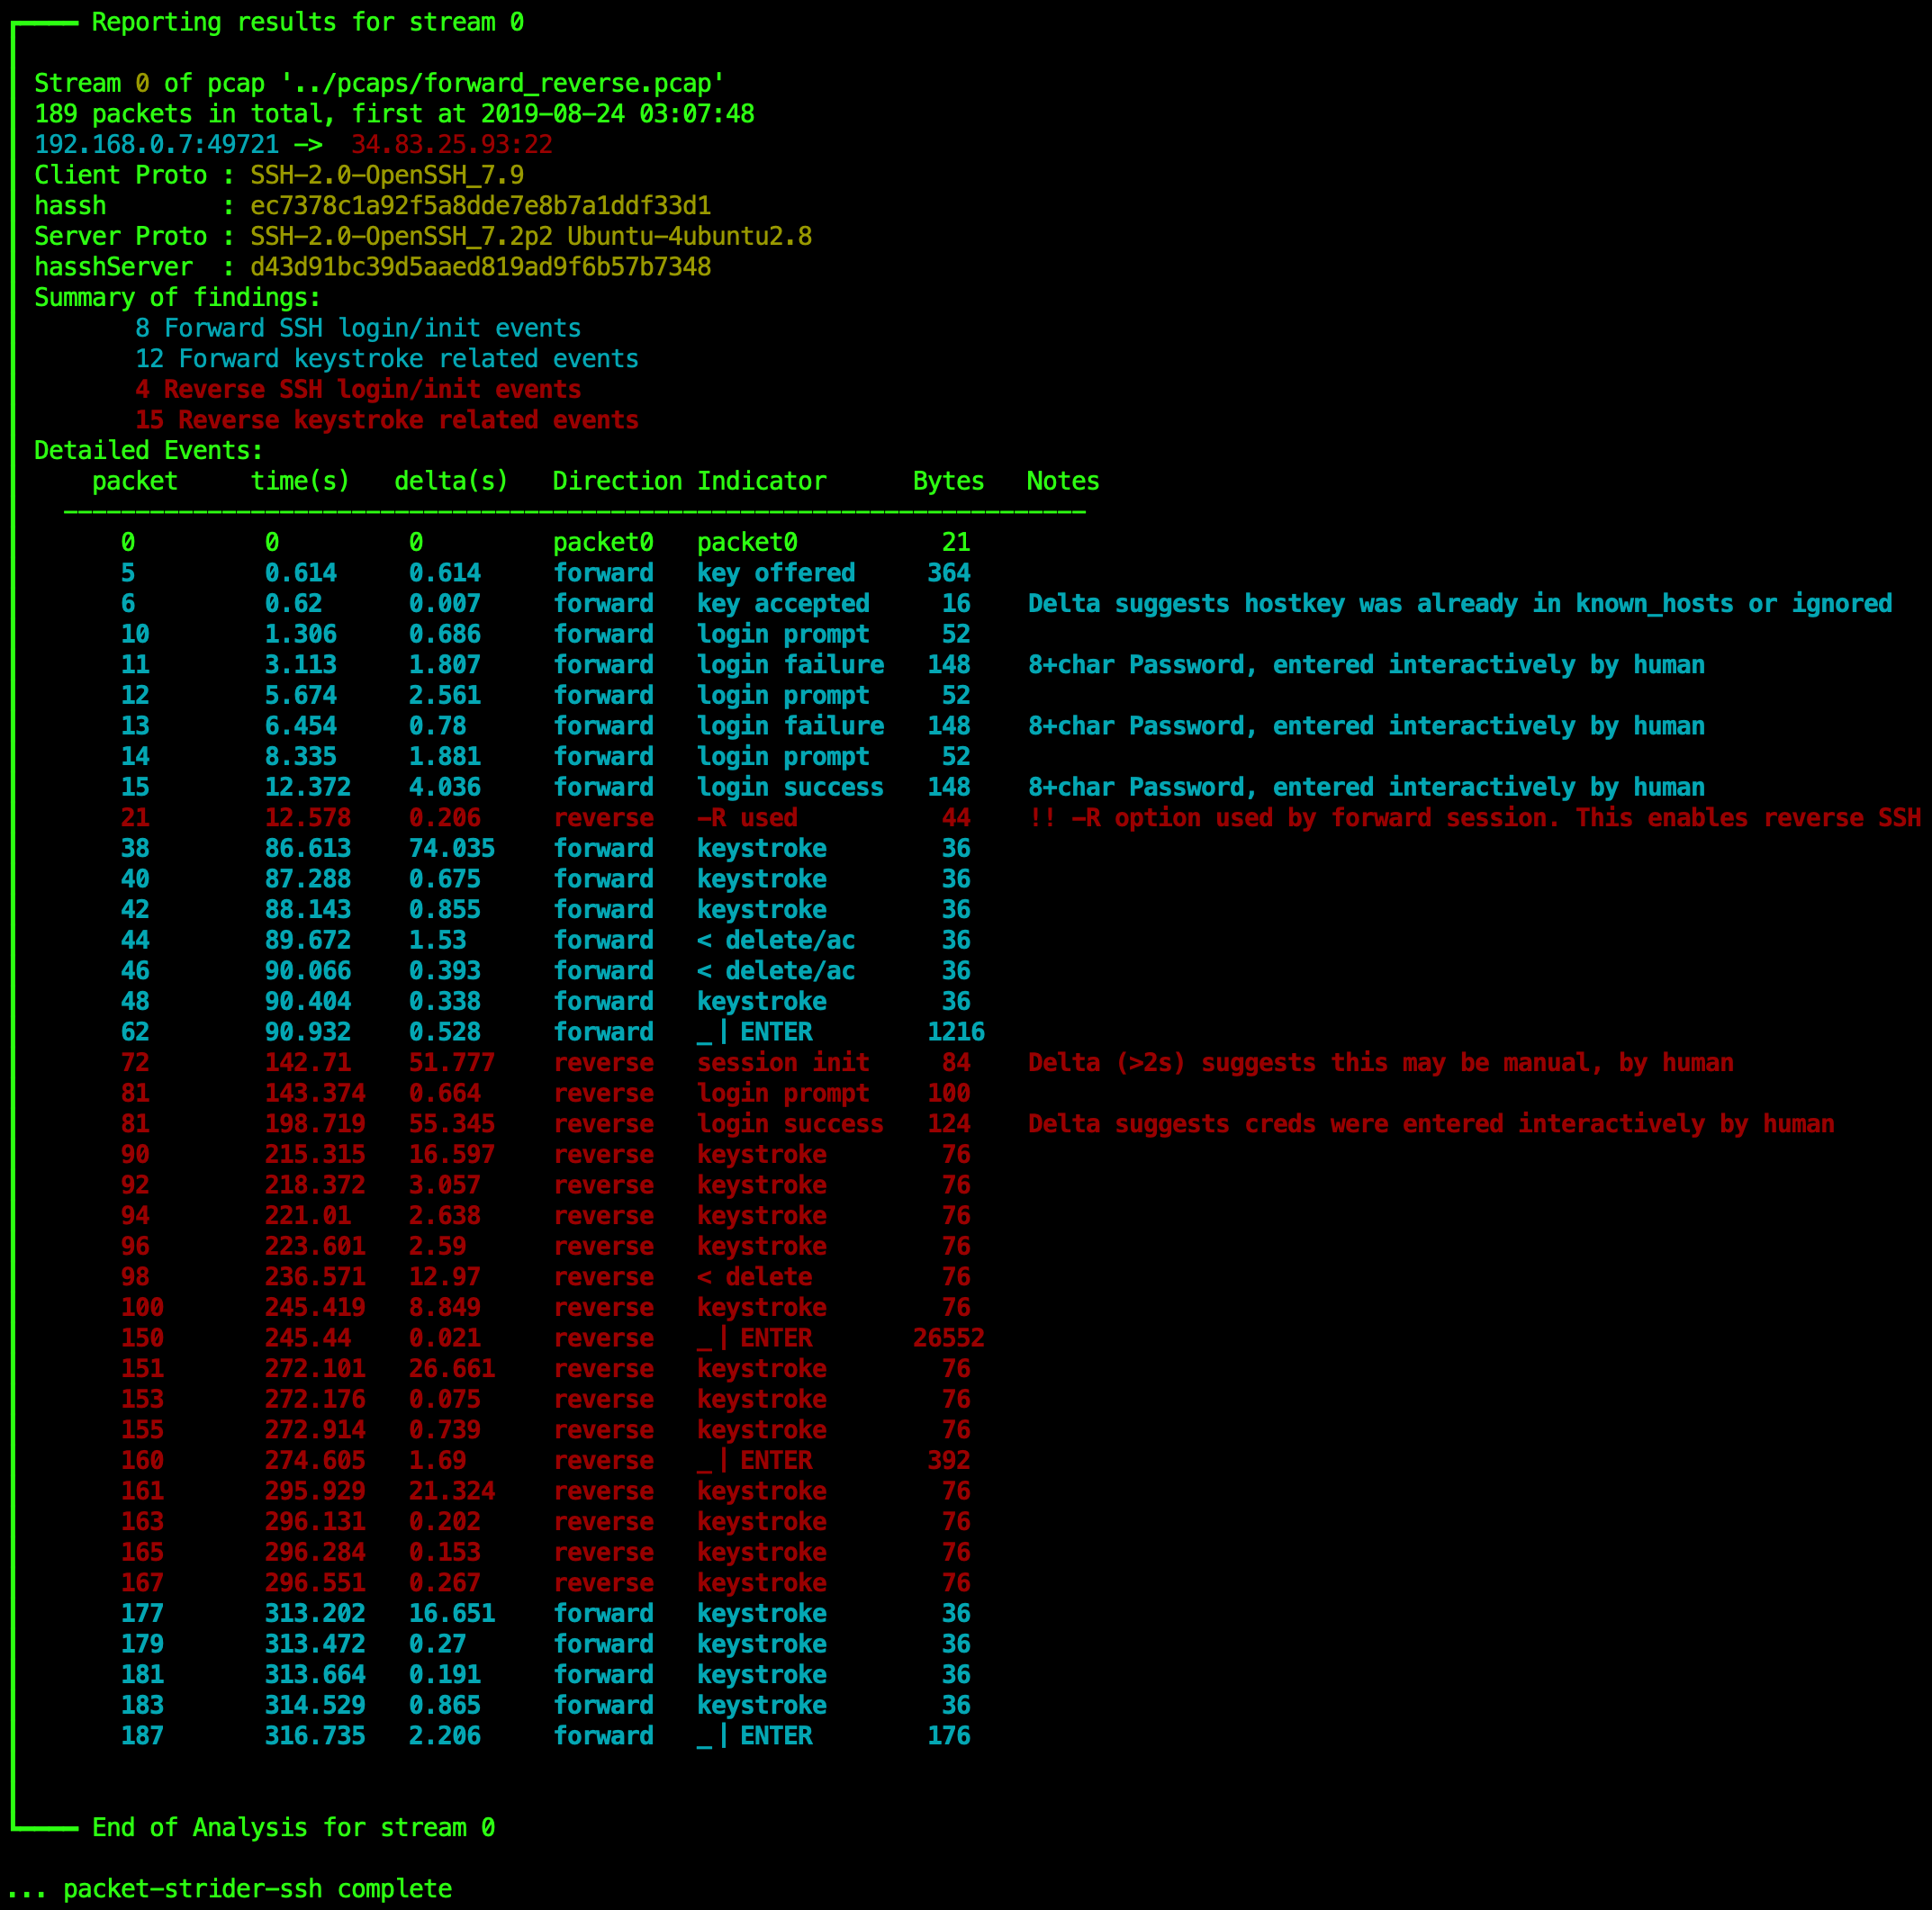 benjeems/packetstrider
A network packet forensics tool for SSH
 ohmyadd/wetland
A high interaction SSH honeypot
 darses/cve-2025-32433
Security research on Erlang/OTP SSH CVE-2025-32433.