
icannTLD
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
dns-analysisinformation-gatheringintrusion-detection+3
8
corelight/icanntldZeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
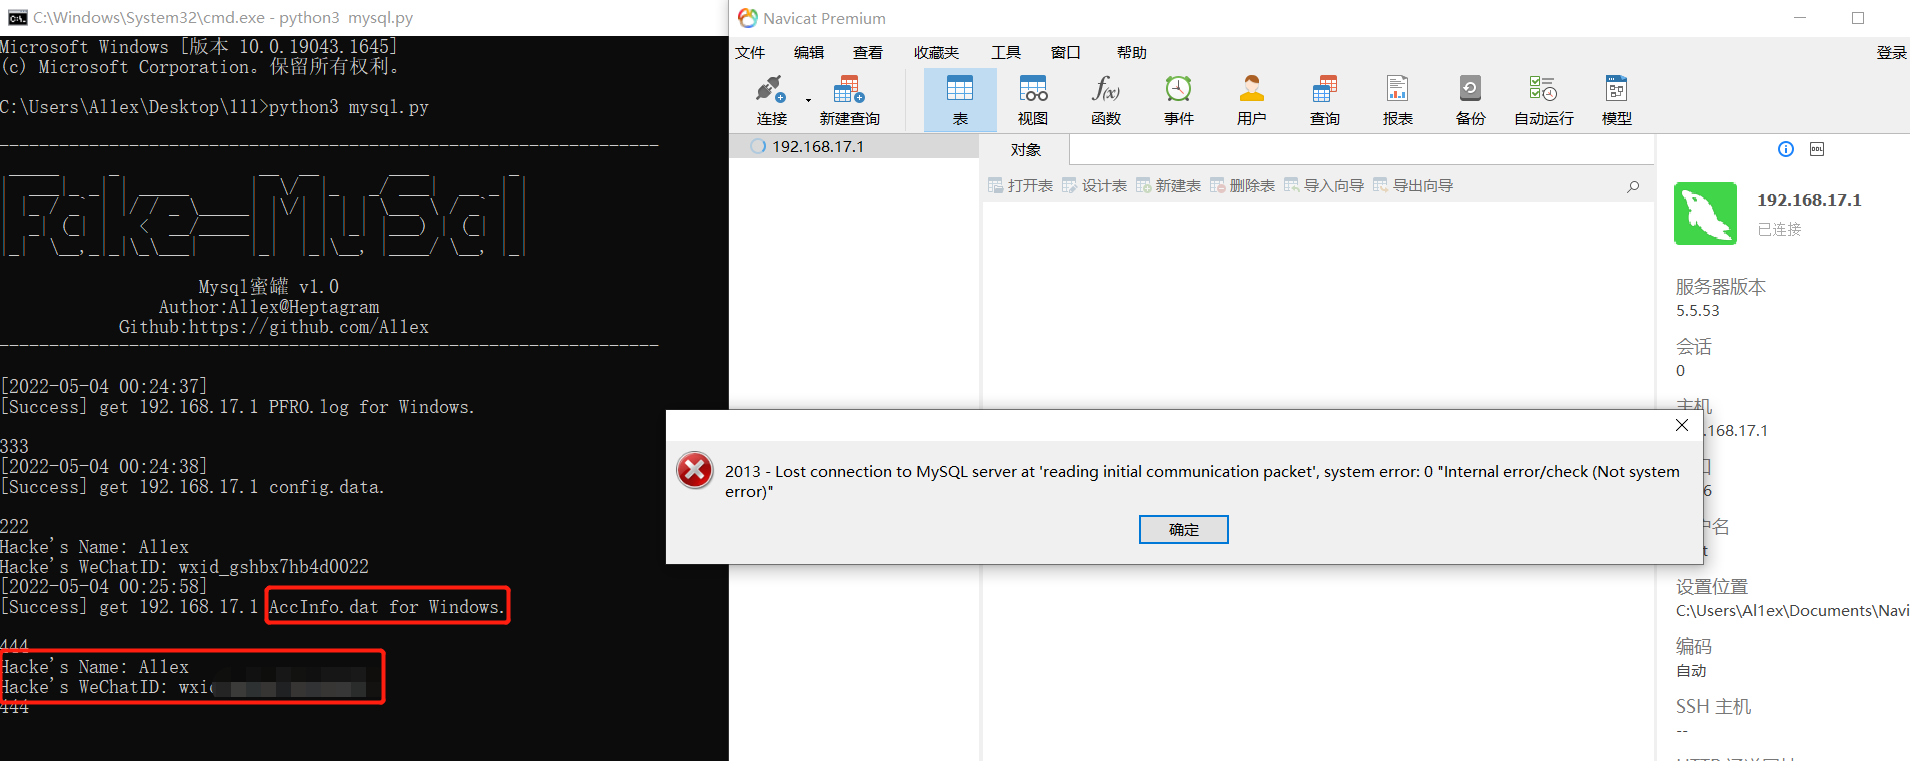 al1ex/mysqlhoneypot
MysqlHoneypot
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 kismetwireless/kismet
Github mirror of official Kismet repository
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 gbrindisi/wordpot
A Wordpress Honeypot
 stamparm/tsusen
Network traffic sensor
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 randomuserid/tylium
Primary data pipelines for intrusion detection, security analytics and threat hunting
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit