Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/al1ex/mysqlhoneypot
Defensive ToolsOSINT (Open Source Intelligence)ReconnaissanceInformation GatheringIntrusion Detection
GitHubal1ex/mysqlhoneypot

MysqlHoneypot

MysqlHoneypot

View Repository
253344 years agoReviewed by Kitploit
Share

Introduction

MysqlHoneypot is a Mysql honeypot project, which mainly uses load data local infile to obtain the user name of the attacker's host (Windows platform), and further obtains the WeChat ID according to the user name, and then obtains the user's mobile phone number, login address and other information according to the WeChat ID. The main files read are as follows:

A、Via C: / Windows / pfro Log to get attacker's name
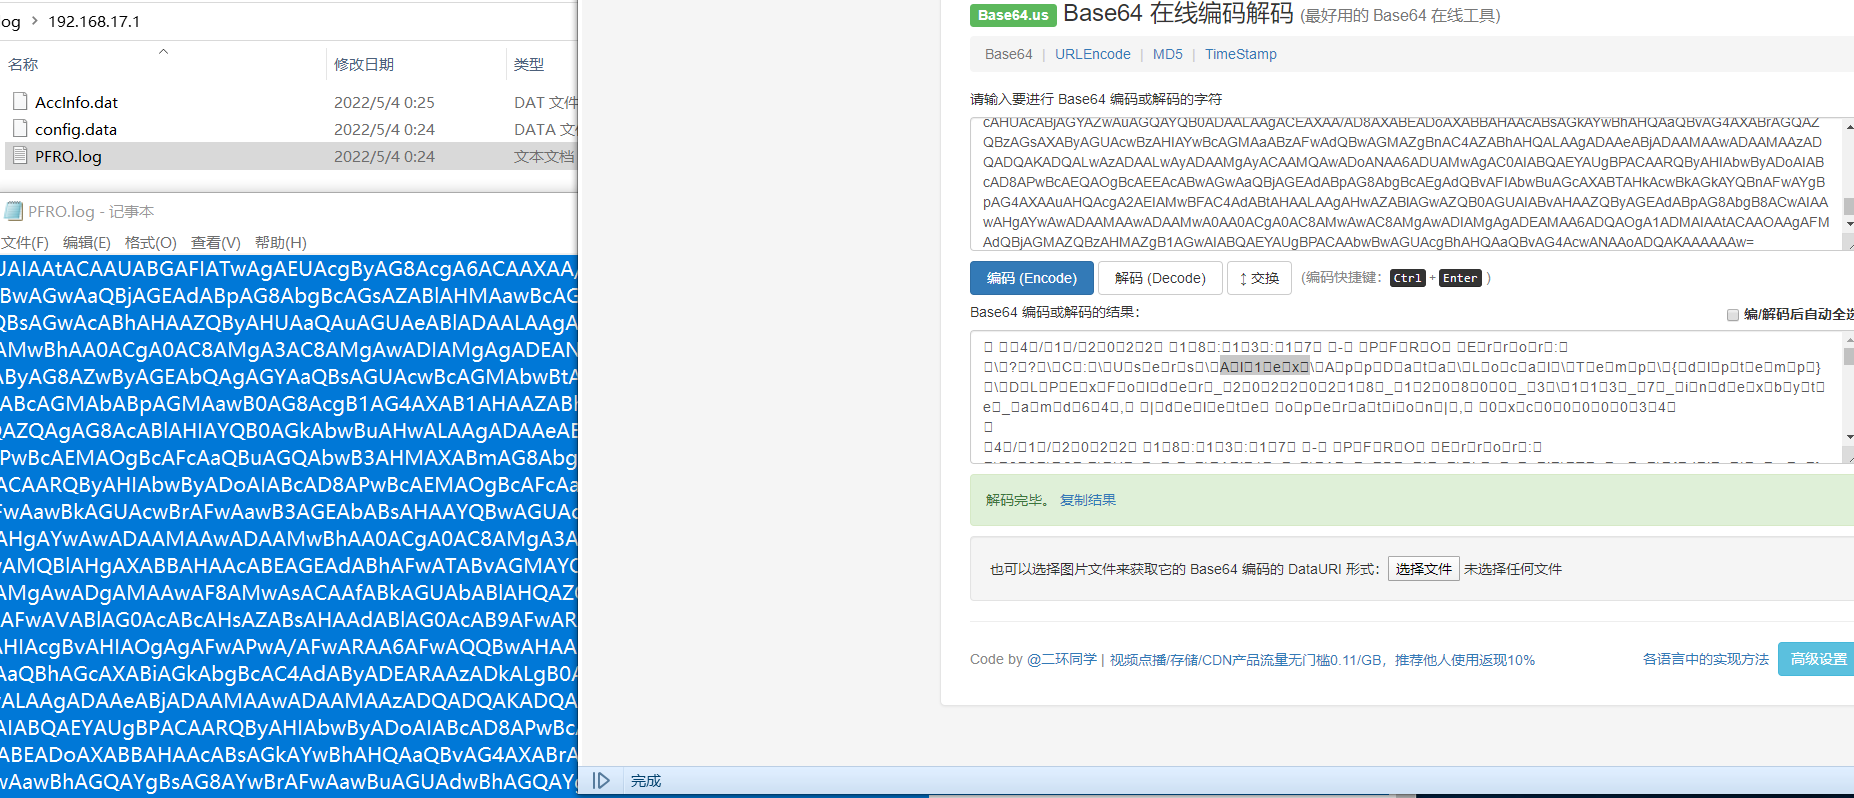
username

B、Via C:/Users/UserName/Documents/WeChat Files/All Users/config/config.data get attacker's wxid
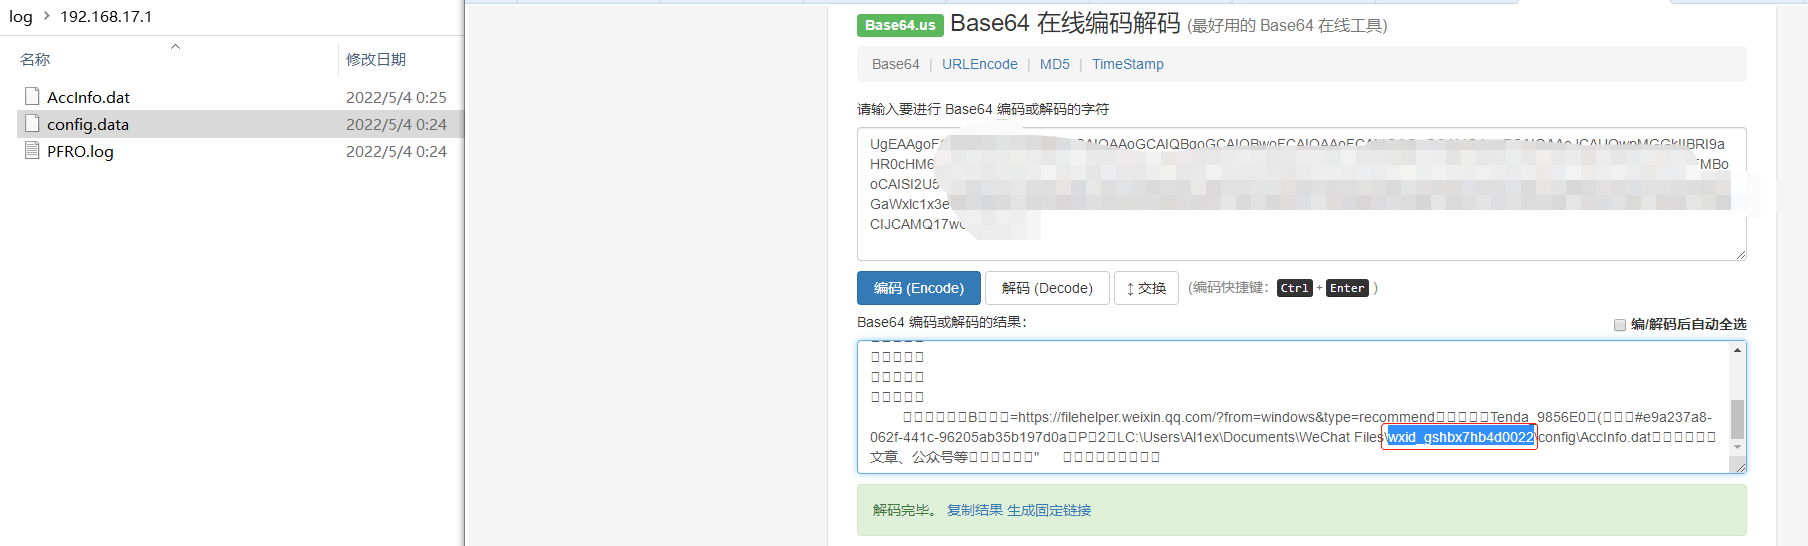
wechat

C、Via C:/Users/UserName/Documents/WeChat Files/wx_id/config/AccInfo.dat get address、wechatID、Telephone
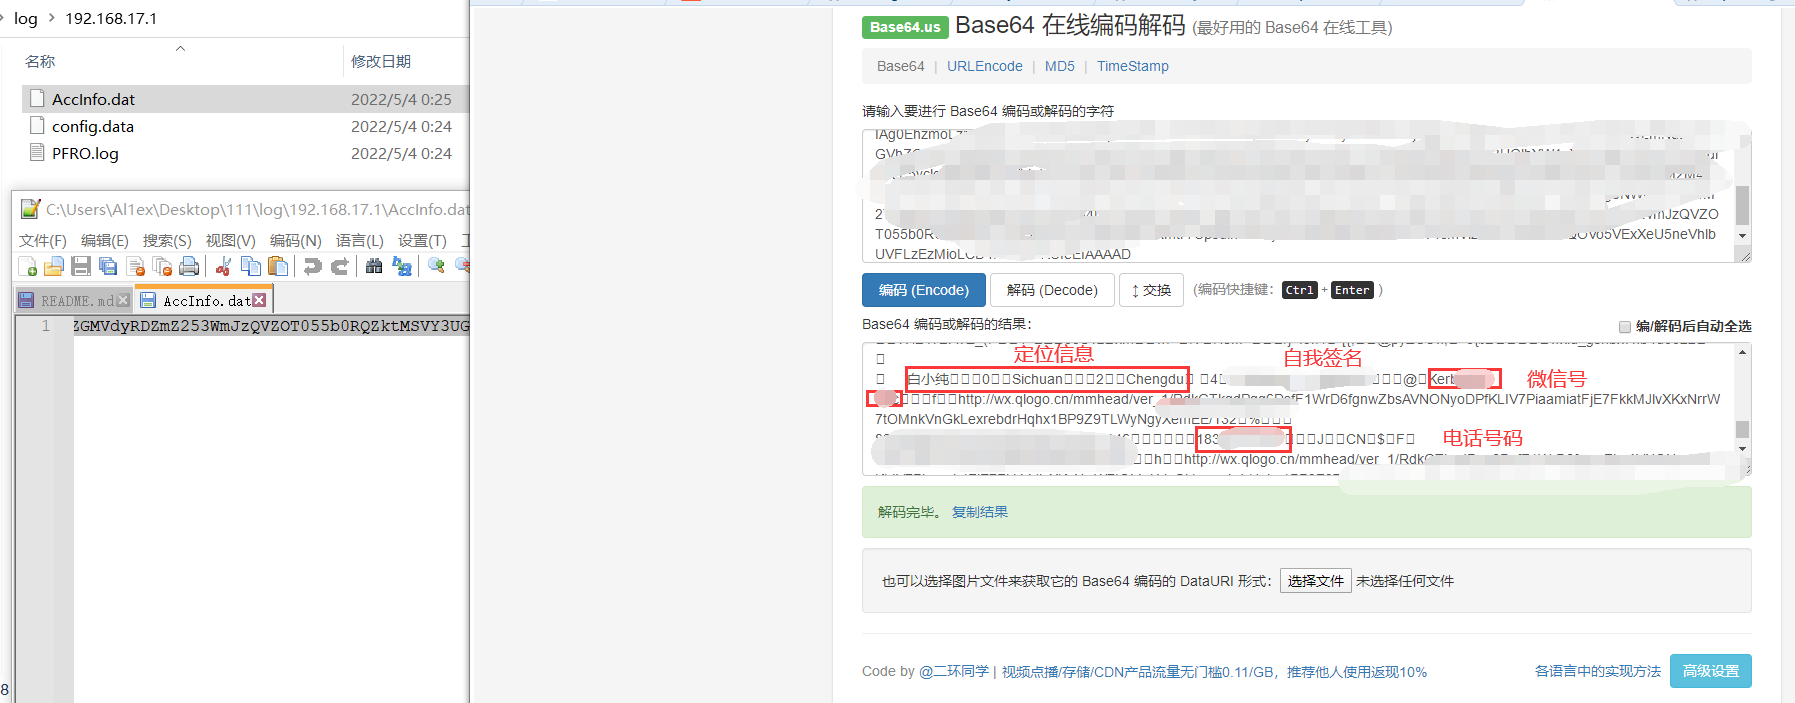
acc2

Function

Capture the attacker's PC WeChat account information

Usage examples

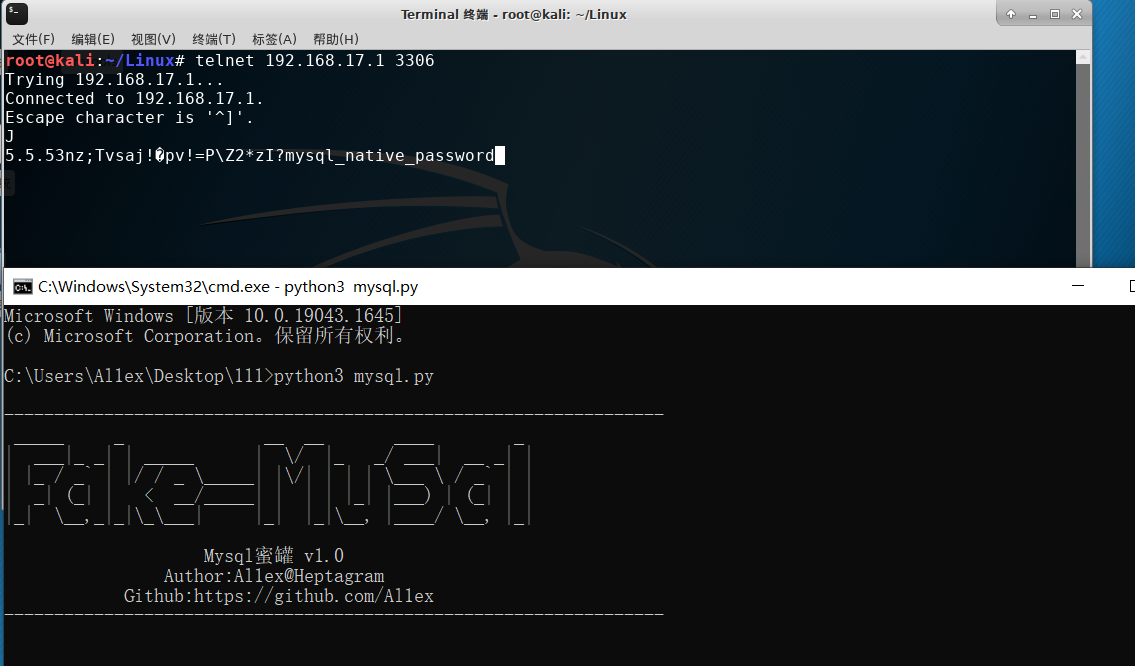
Step 1:The attacker's extranet scans the assets and guesses violently.

crake

Step 2:The local PC of the attacker directly reads PFRO.log and config.data files for the first time when WeChat is installed.
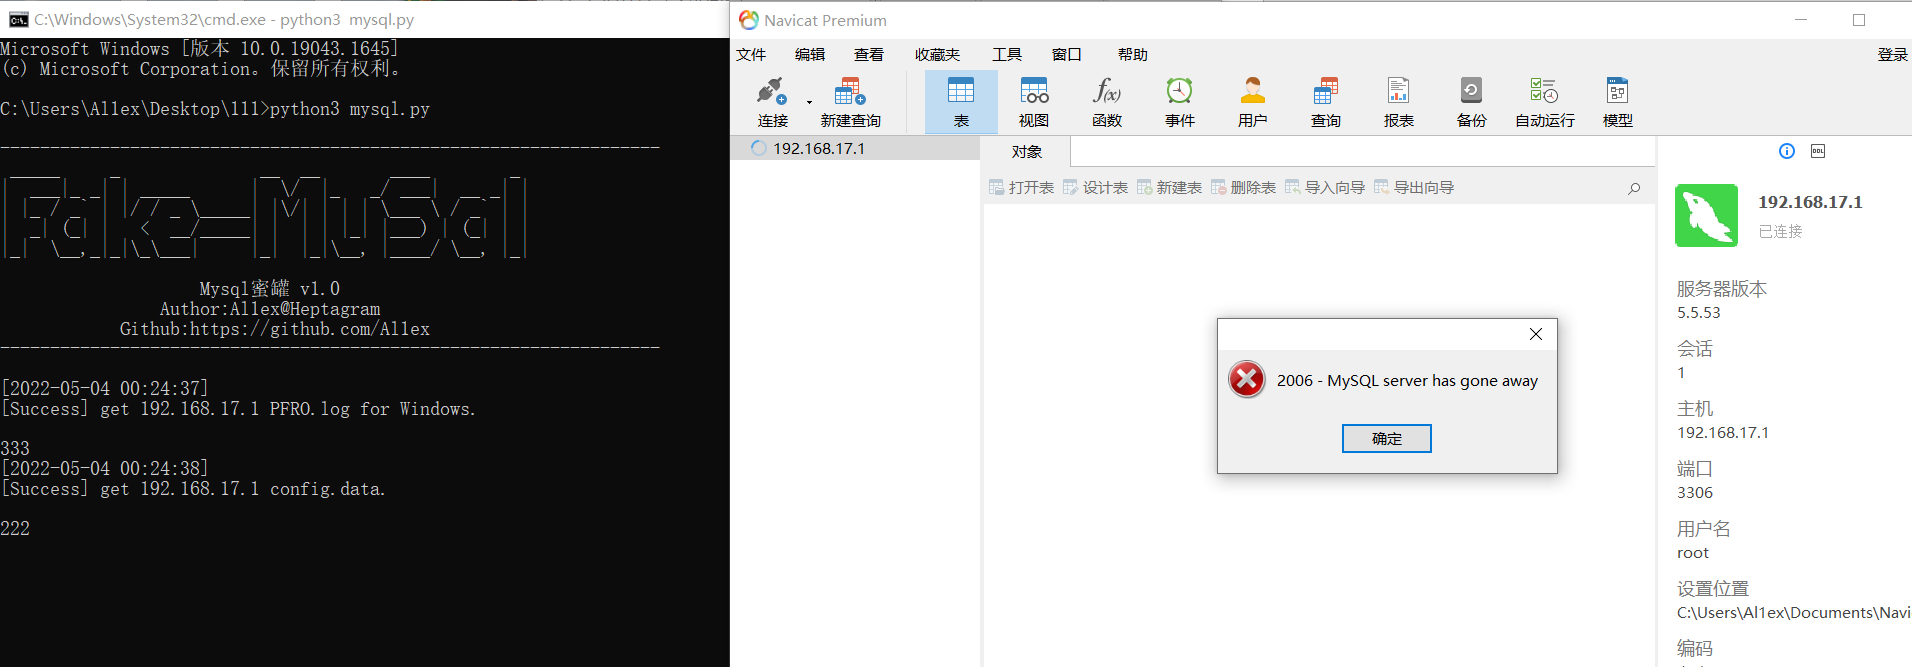
config

Step 3:The attacker obtains AccInfo.dat information when trying again.
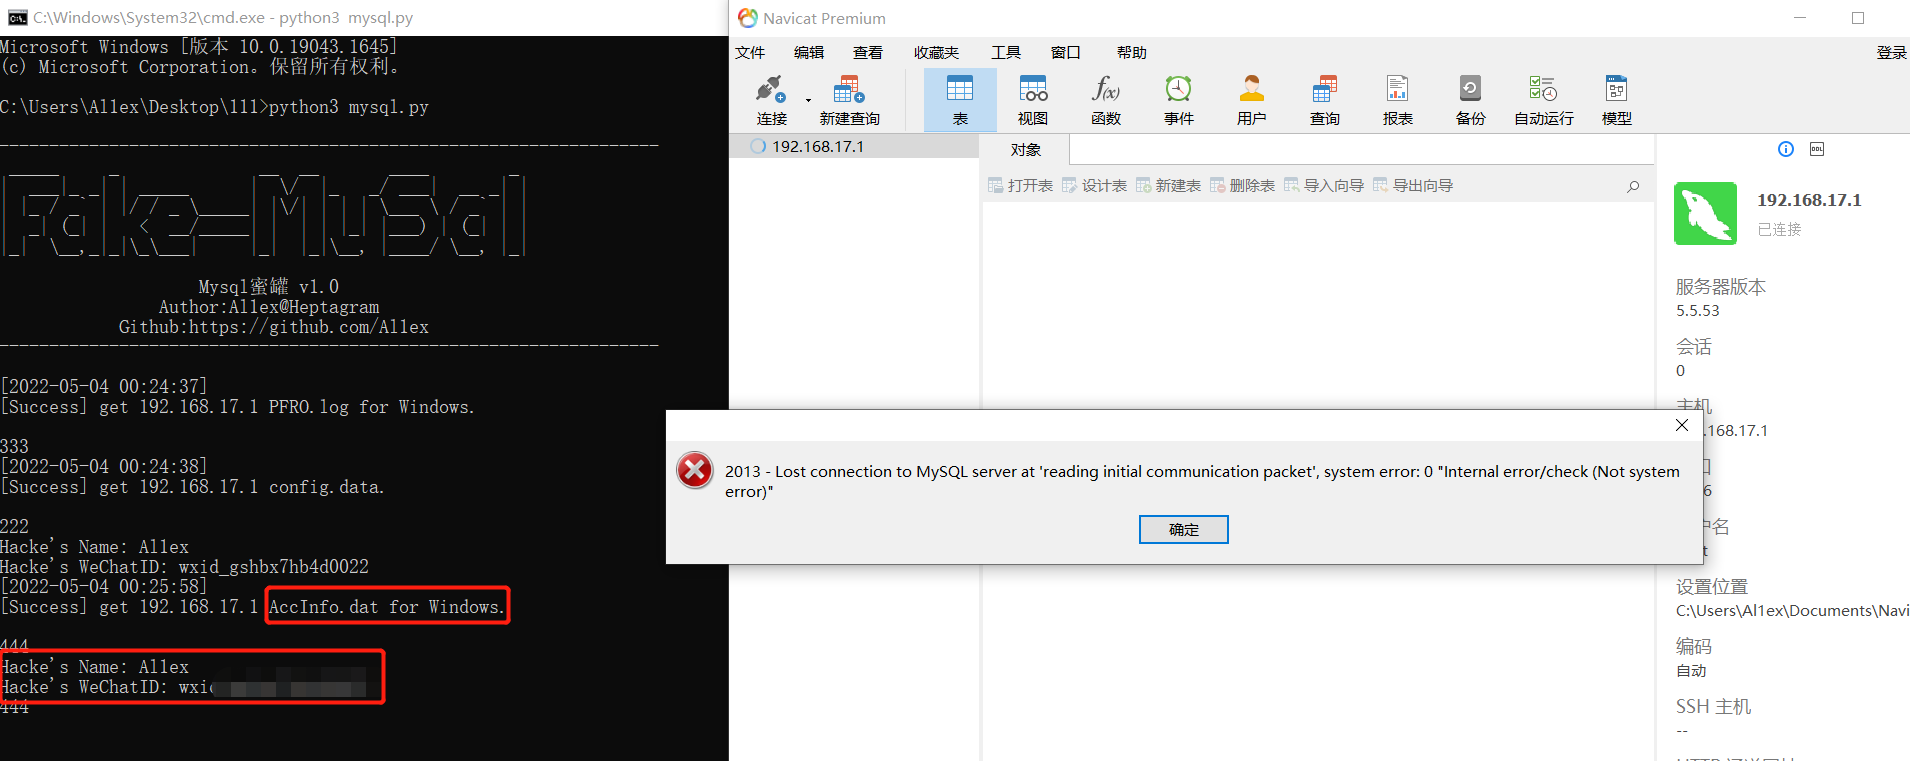
acc

Supplementary expansion:

  • Windows will not get information when it is not connected to the system. If necessary, you can change what you want to read in the file.

linux

  • The attacker only reads PFRO.log when WeChat is not installed locally.

log

Shortcomings

When an attacker uses the brute force guessing tool to successfully explode (fake) and log in remotely, he will get the contents of PFRO.log and config.data files for the first time. If he wants to get more delicate contents, he needs to try to connect again (usually). Please change this later when you have time.

Reference

https://github.com/qigpig/MysqlHoneypot

https://github.com/heikanet/MysqlHoneypot

https://mp.weixin.qq.com/s/rQ9BpavBeMnS6xUOidZ5OA

https://mp.weixin.qq.com/s/m4I_YDn98K_A2yGAhv67Gg

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →