

artillery
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
anomaly-detectiondefensive-toolshardware-iot-security+5
338
trustedsec/artilleryOpen-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 yjesus/patriot-linux
Host IDS for desktop users
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 neo23x0/auditd
Best Practice Auditd Configuration
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 rnehra01/arp-validator
Security Tool to detect arp poisoning attacks
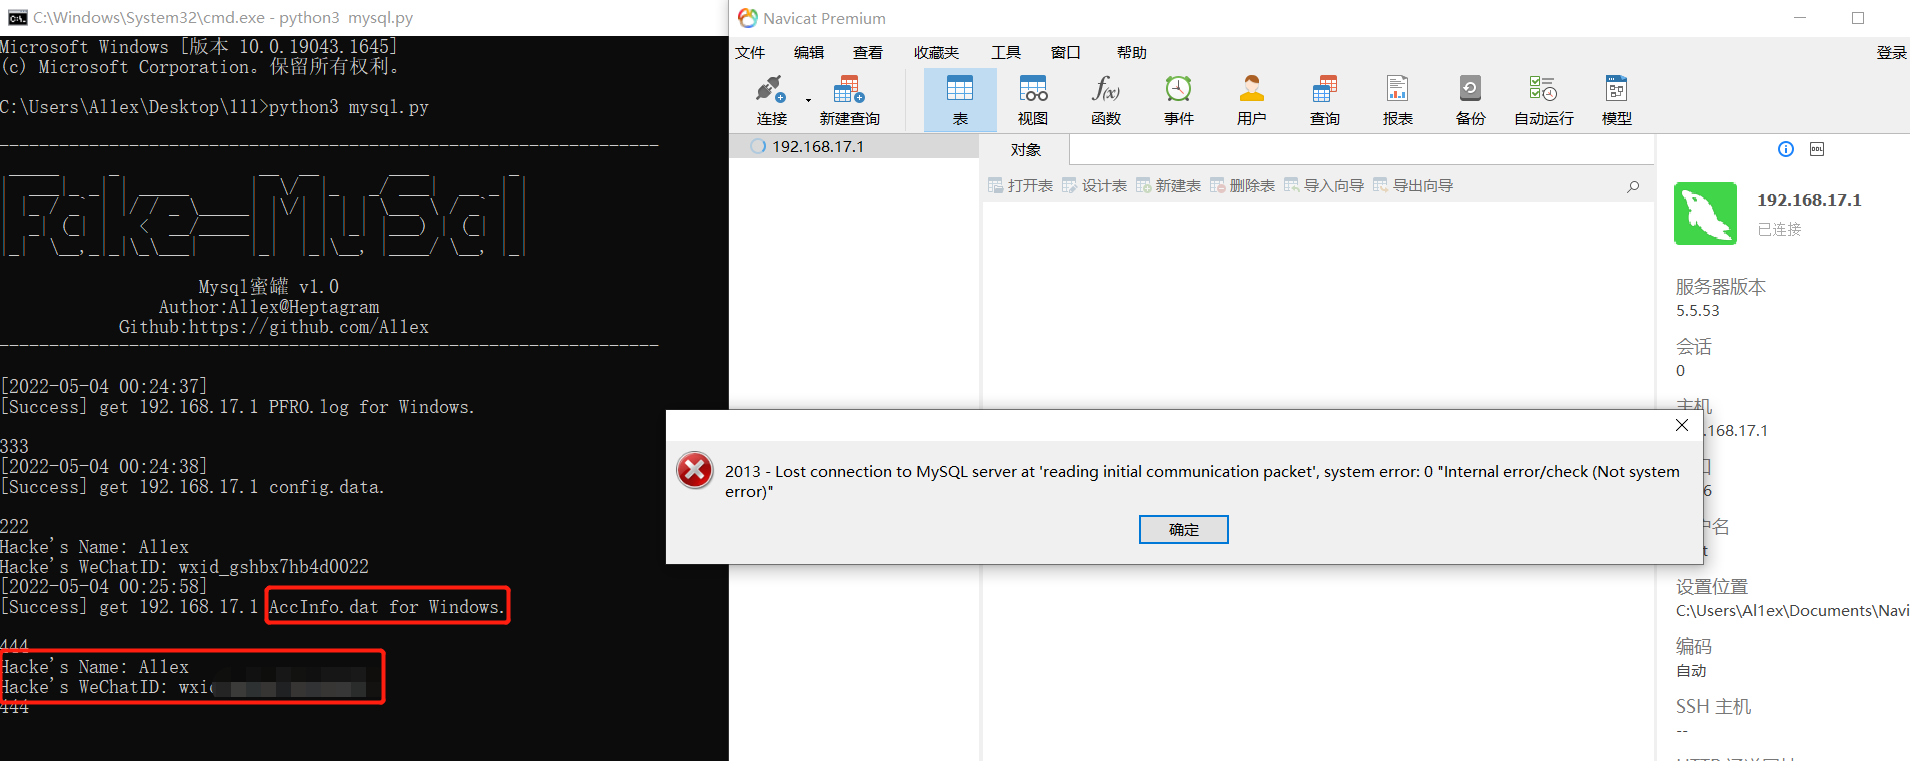 al1ex/mysqlhoneypot
MysqlHoneypot
 lp008/cve-2020-13942
Exploit for Apache Unomi pre-auth RCE (CVE-2020-13942) with a Suricata detection rule for identifying exploitation attempts.
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 nerium-security/cve-2025-55182
Host-based detection rules for the RCE vulnerability in the React JavaScript framework.