

iMonitor
 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
forensicsintrusion-detectionmalware-analysis+1
835
wecooperate/imonitorEndpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
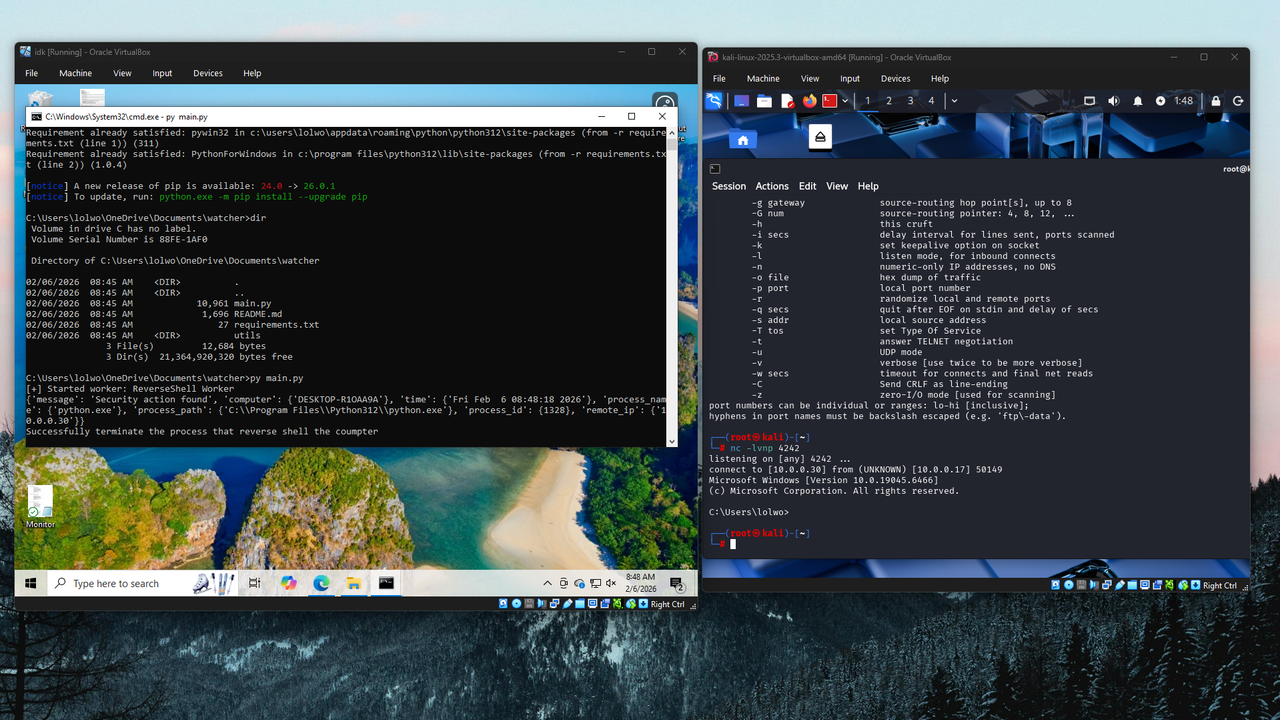 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 elastic/protections-artifacts
Elastic Security detection content for Endpoint
 withsecurelabs/doublepulsar-detection-script
A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
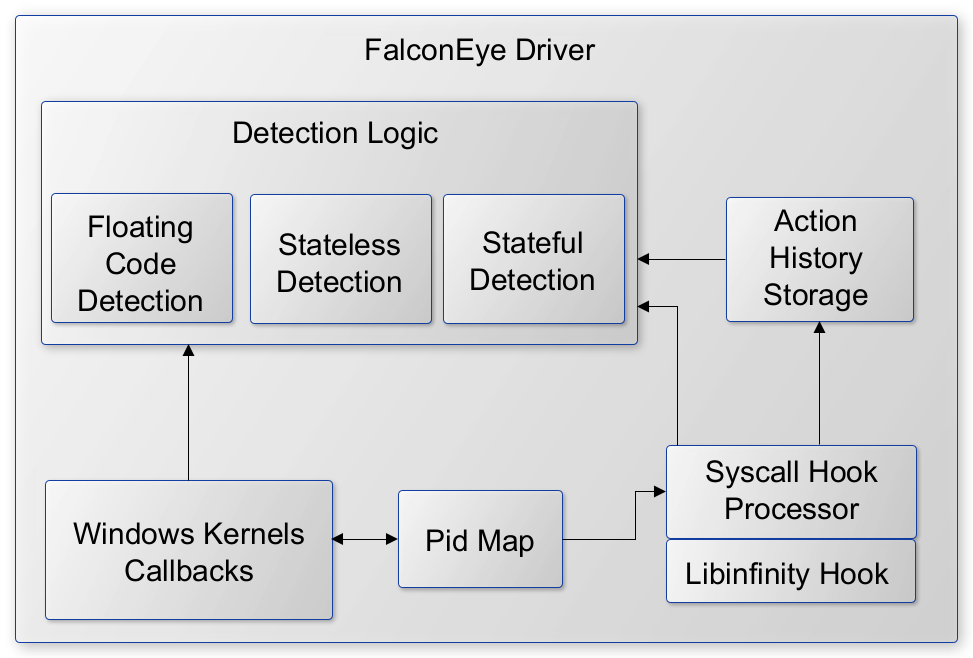 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
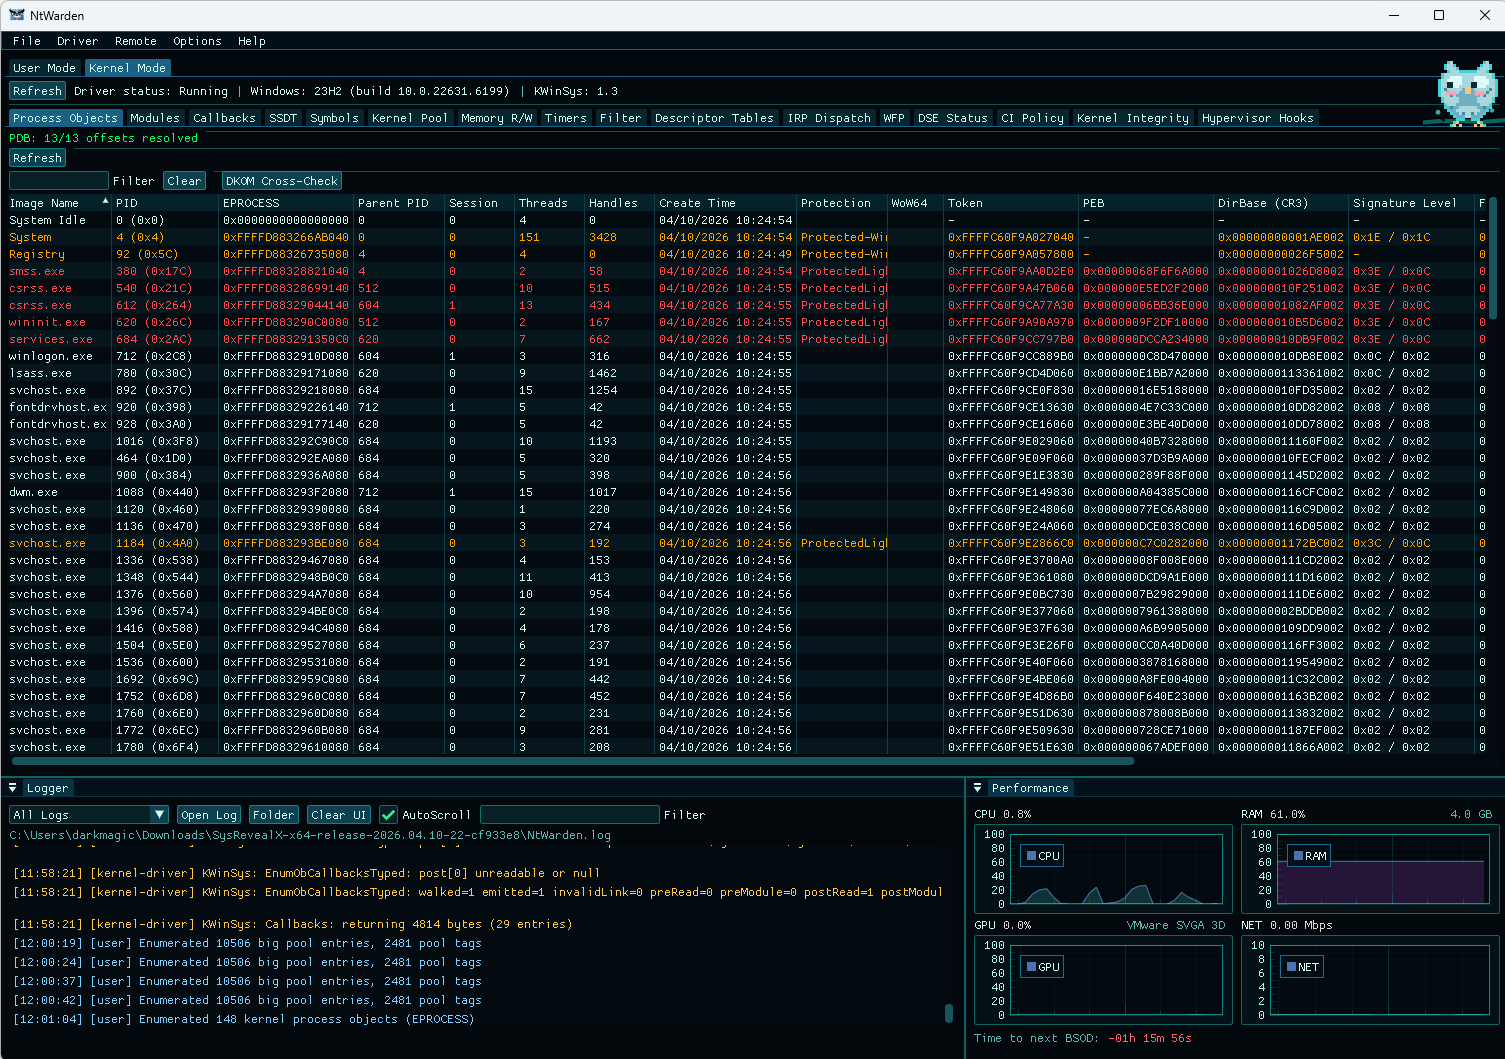 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
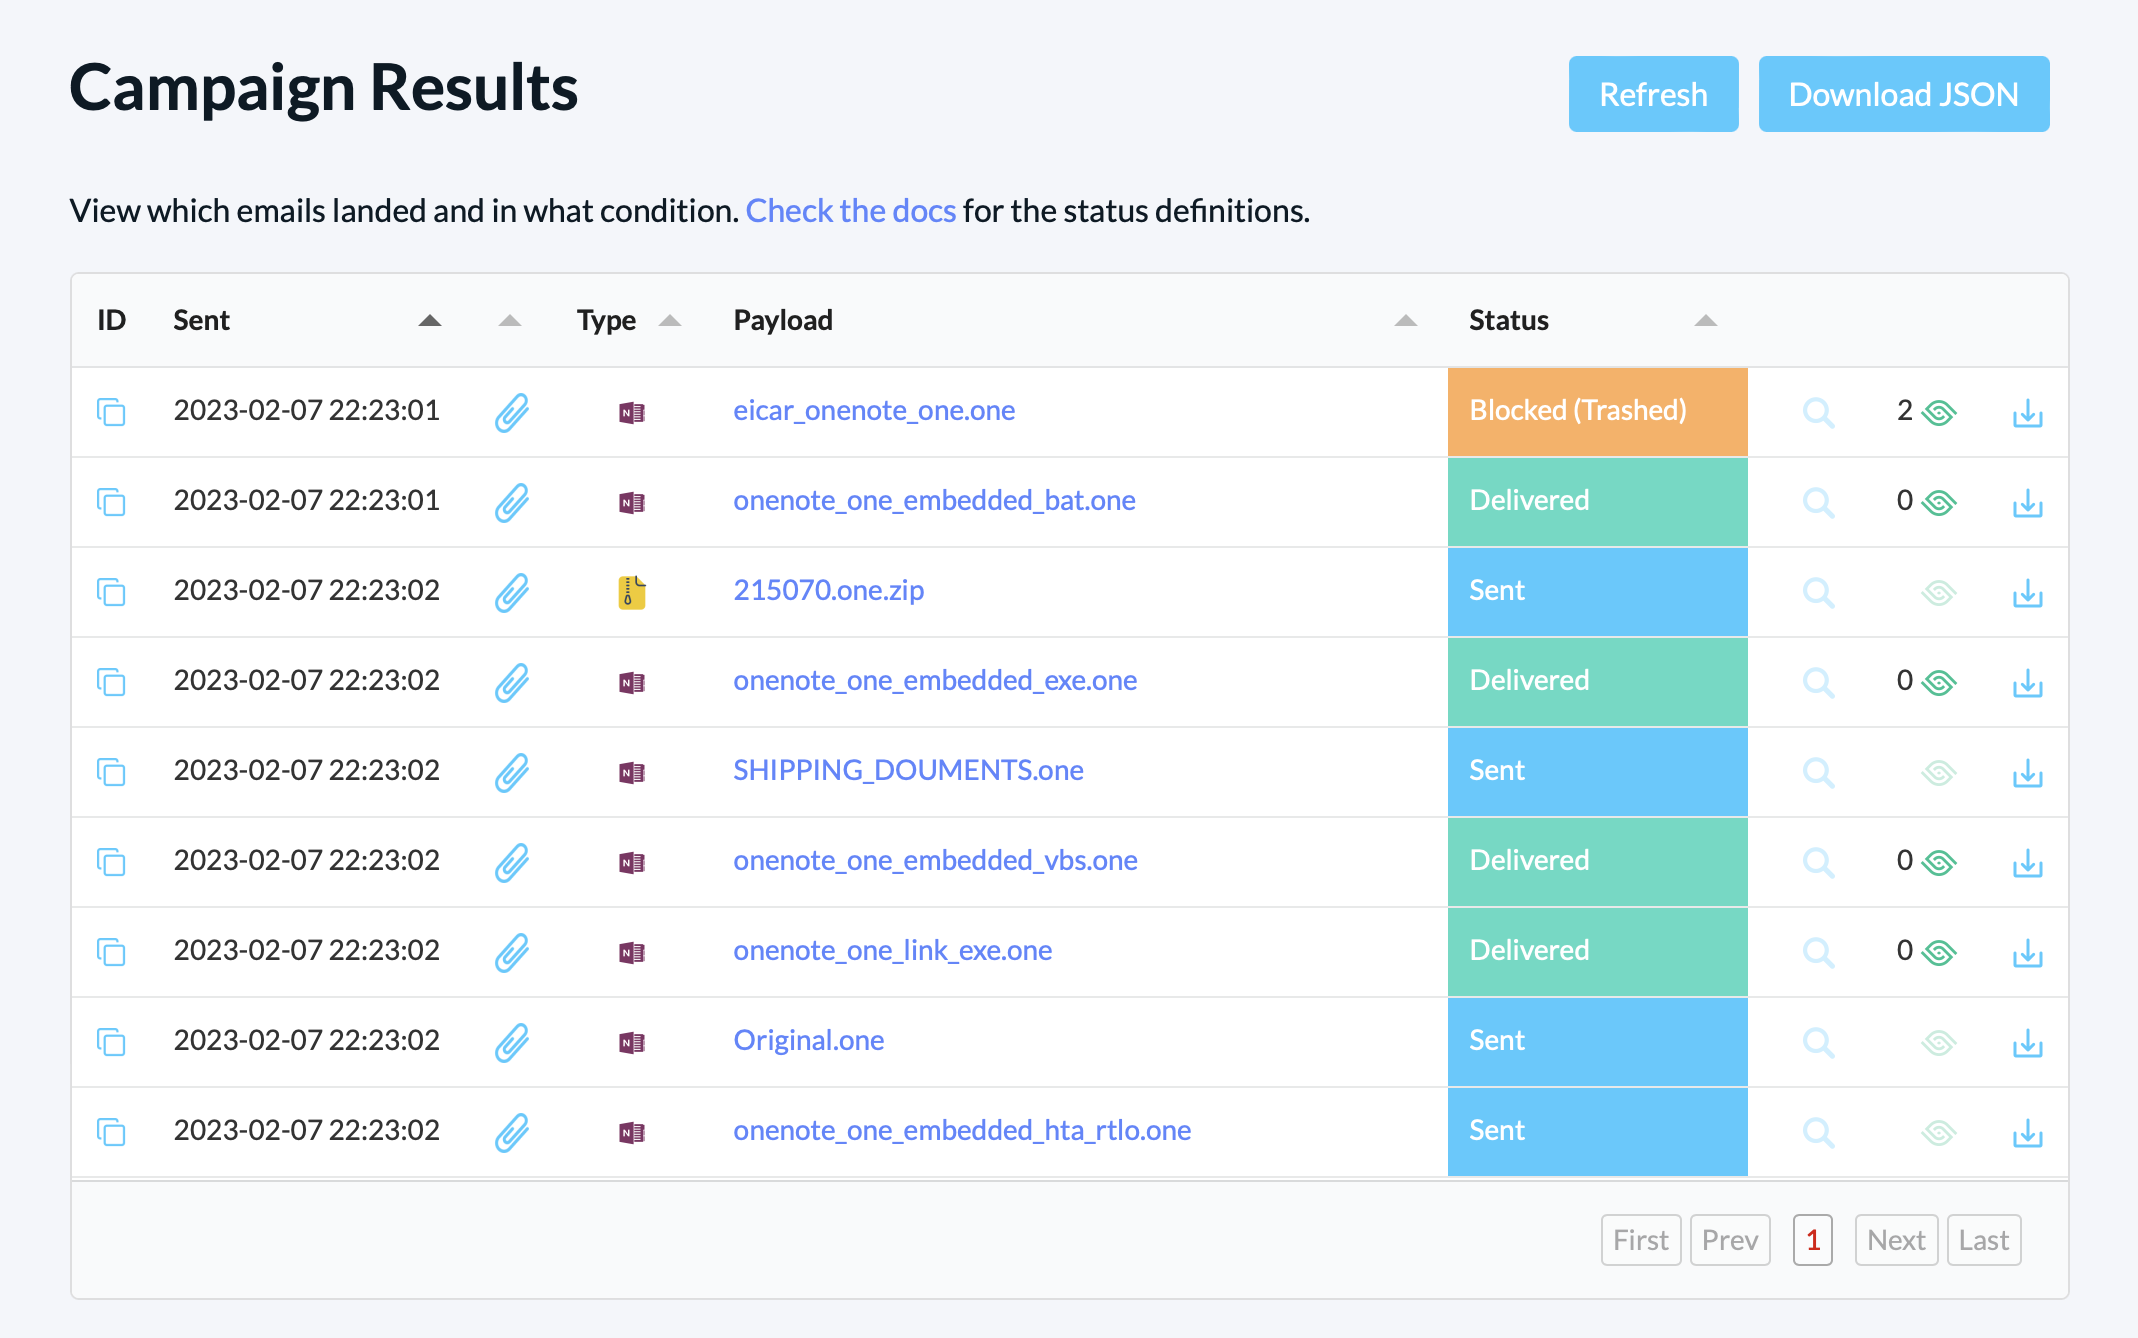 delivr-to/detections
A home for detection content developed by the delivr.to team

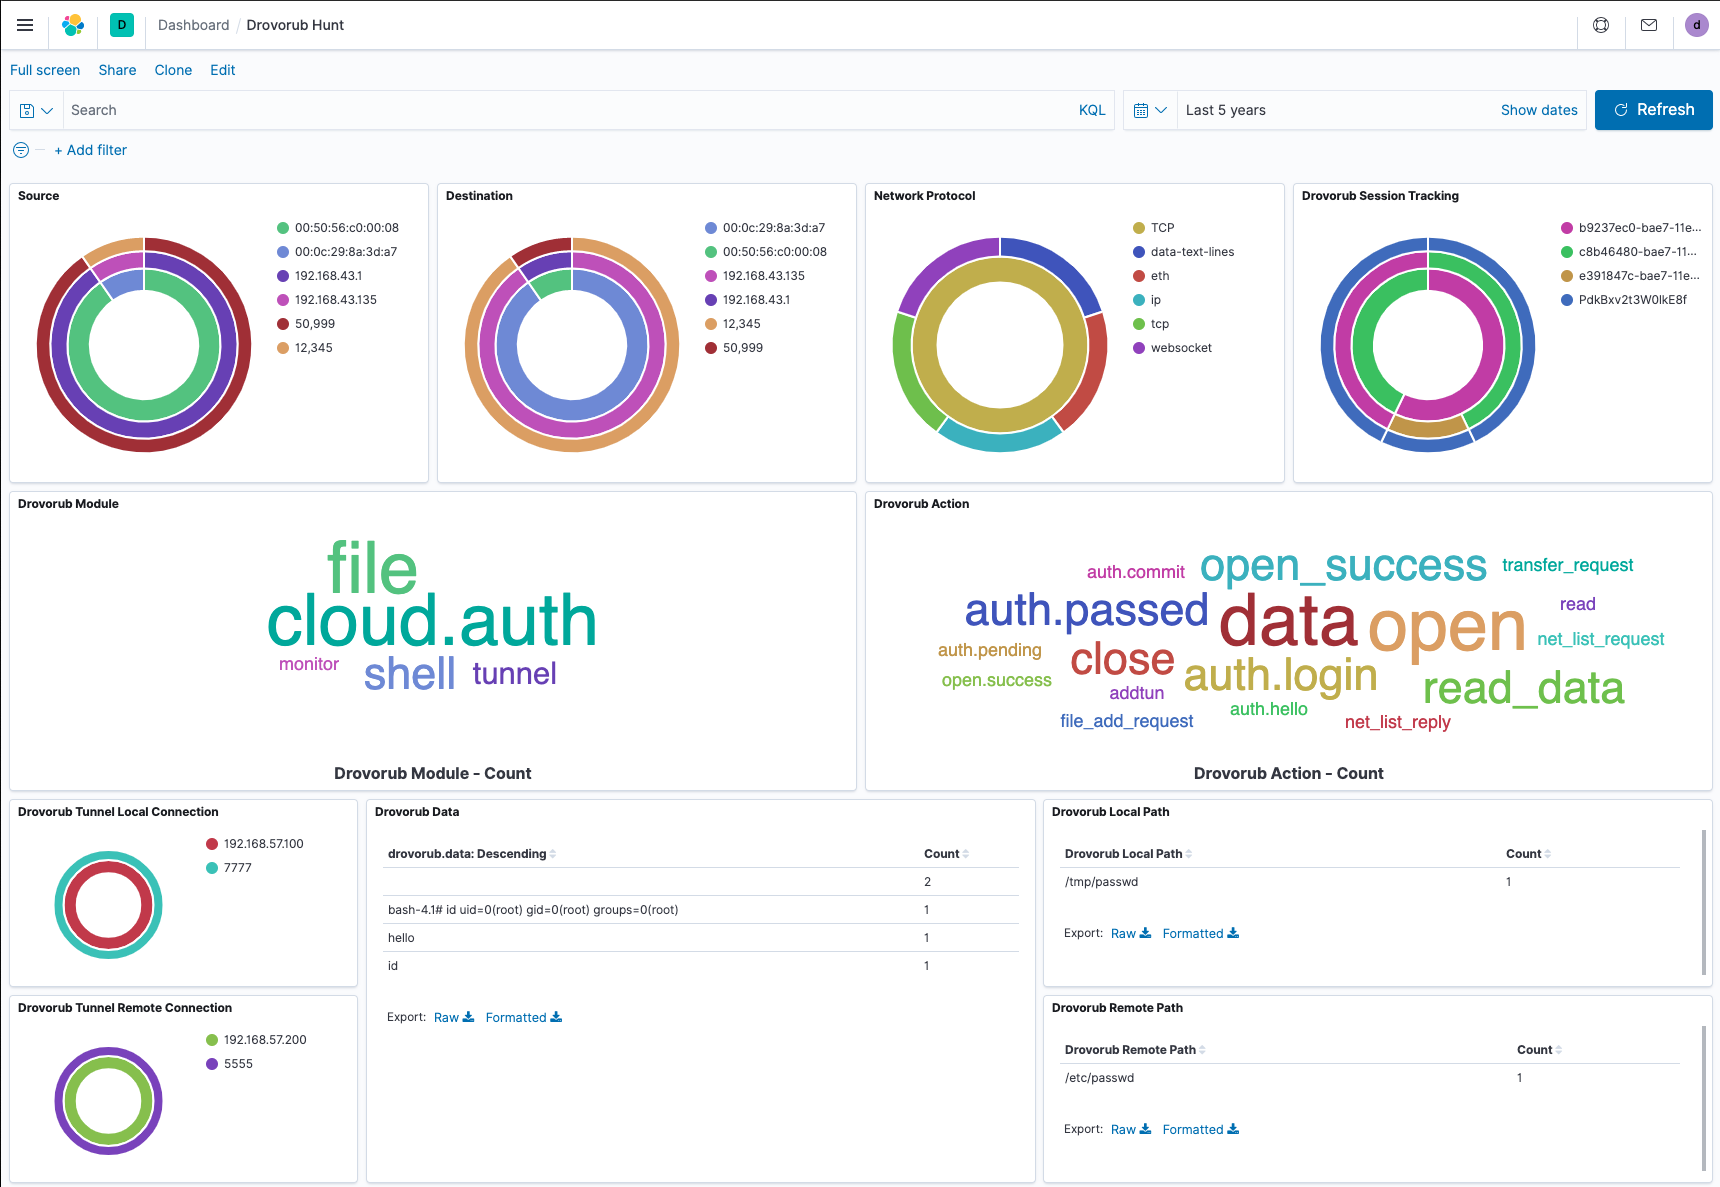 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 corelight/detect-ransomware-filenames
Zeek script that monitors SMB traffic and alerts on known ransomware filenames using the Anti-Ransomware File System Resource Manager list.