wp2shell-Hestia-Scanner

Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…

Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…

A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…

A curated list of resources related to Industrial Control System (ICS) security.

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

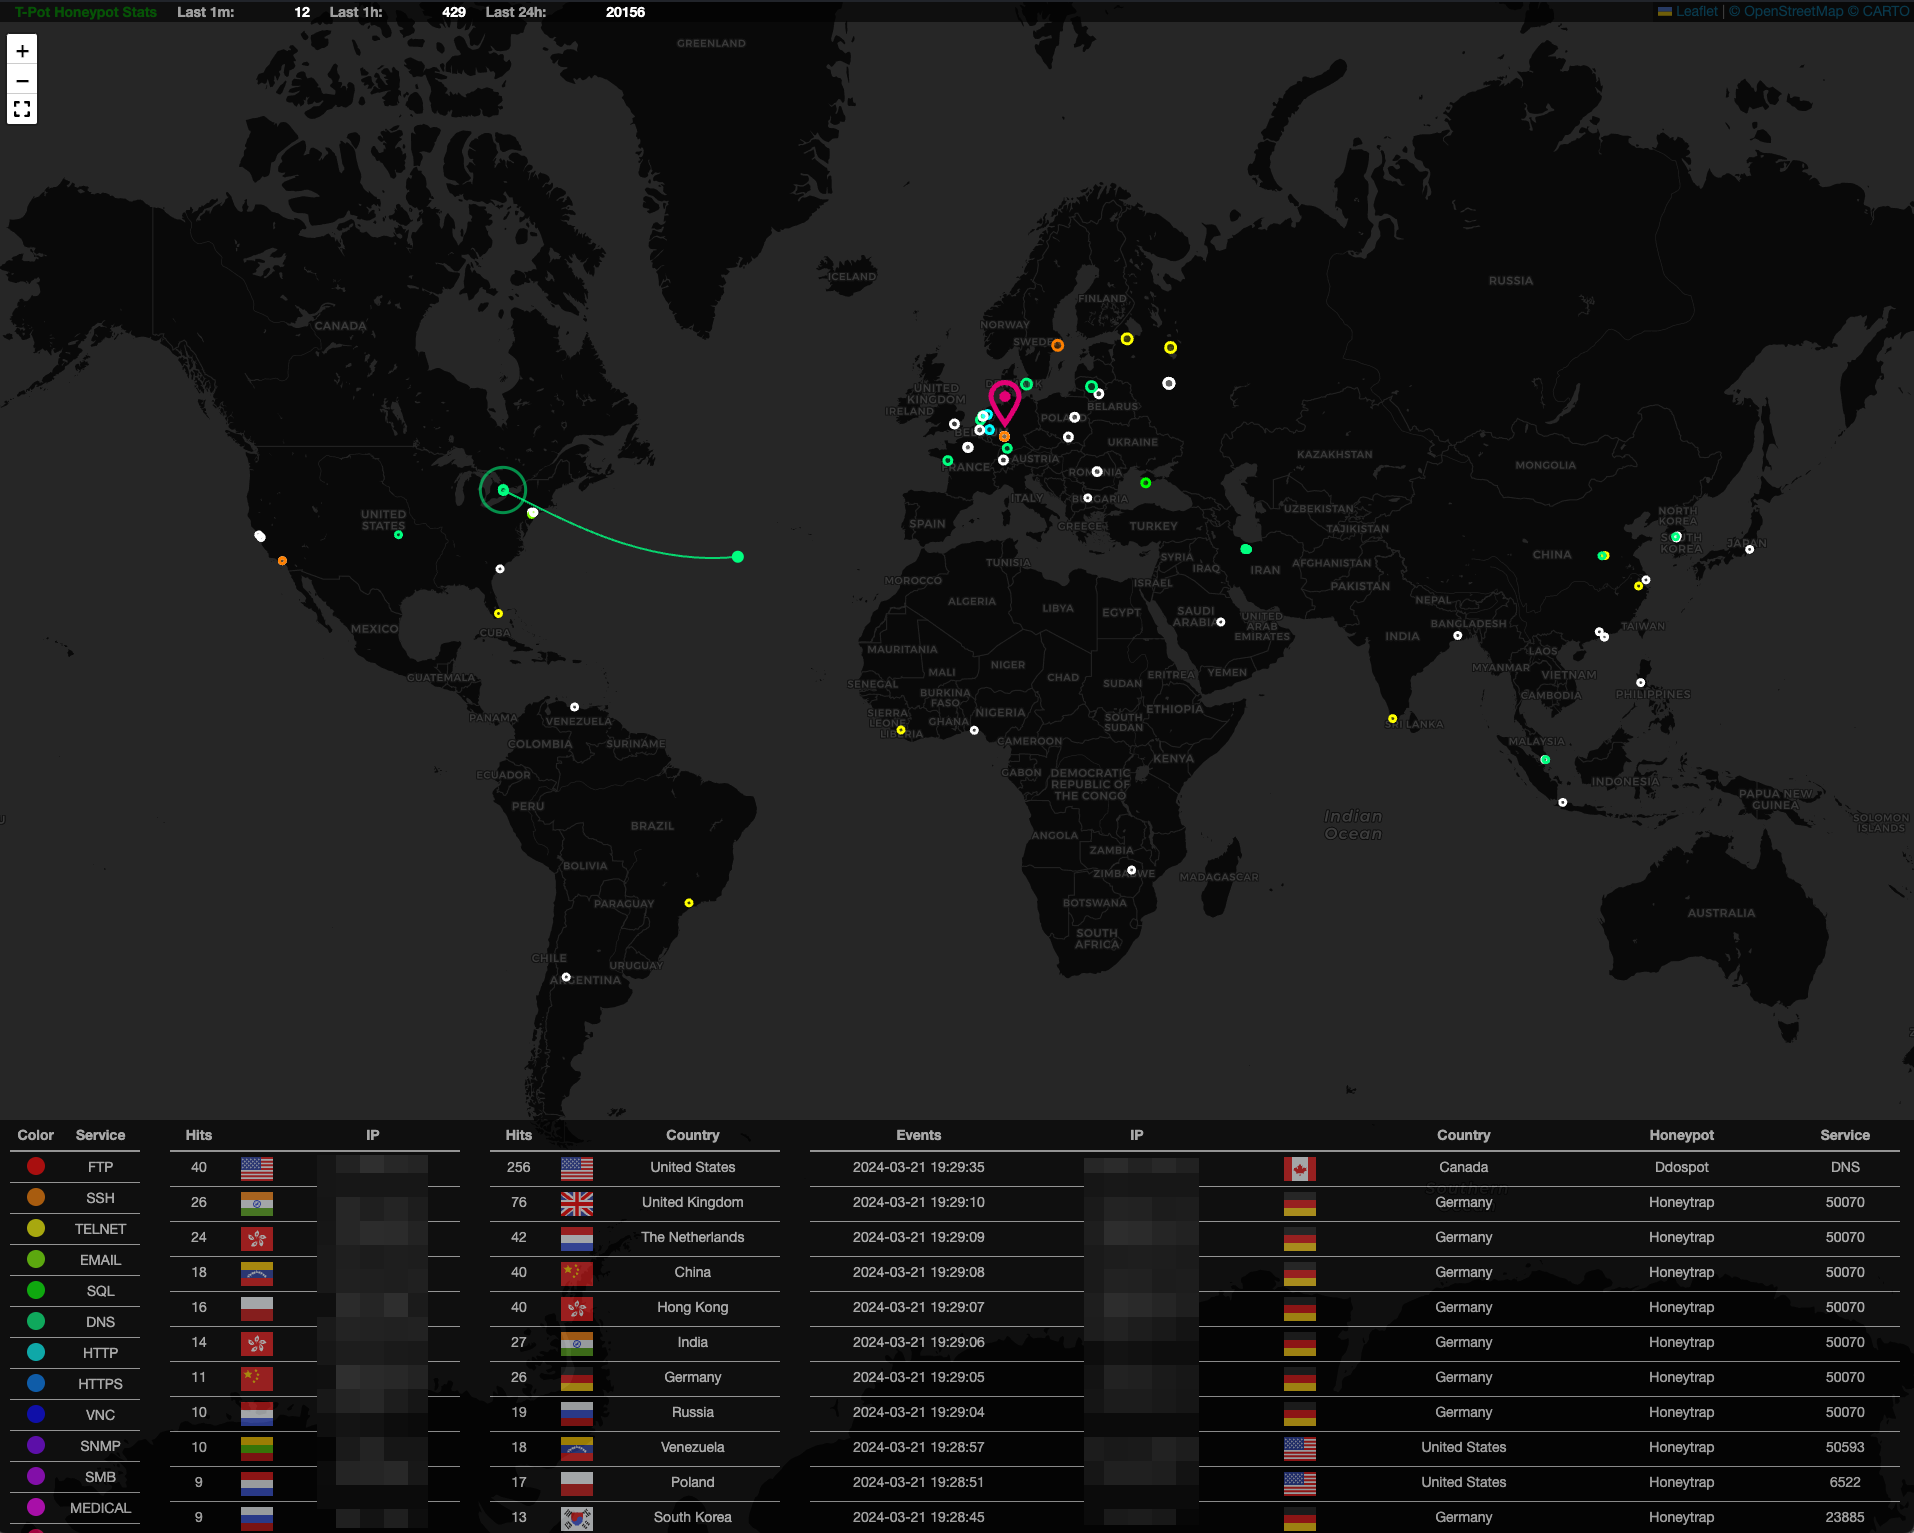
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.

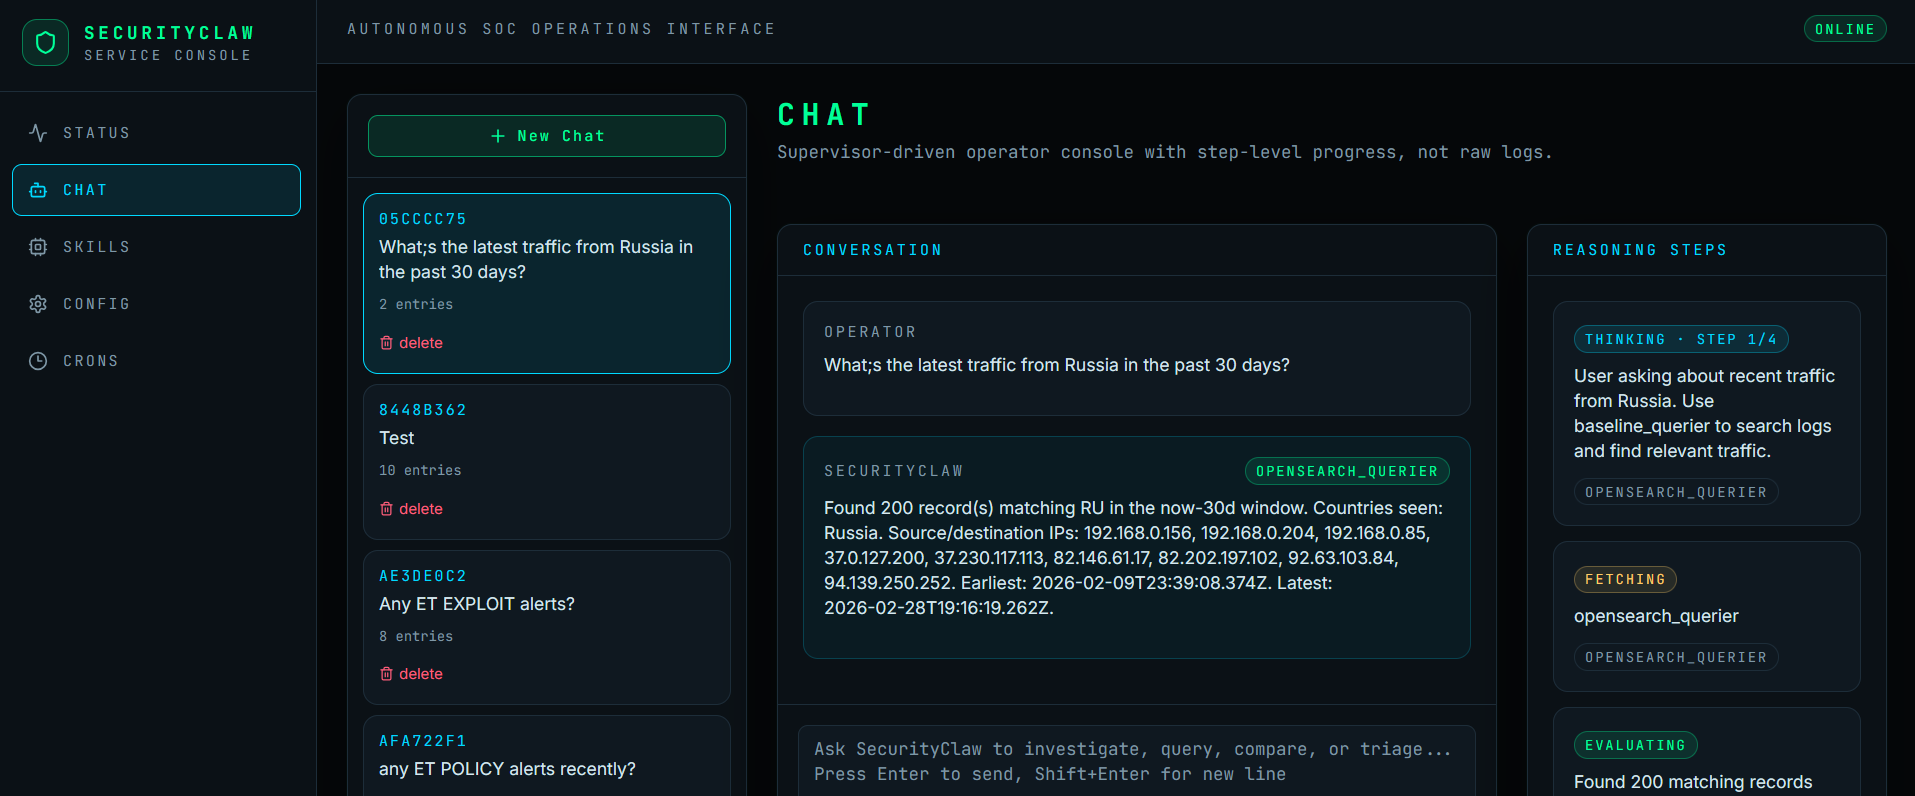
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…

Primary data pipelines for intrusion detection, security analytics and threat hunting

Sigma detection rules for AI agent security monitoring

Automated Network Security with Rust: Detecting and Blocking Port Scanners

Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…

IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.

SQL powered operating system instrumentation, monitoring, and analytics.

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

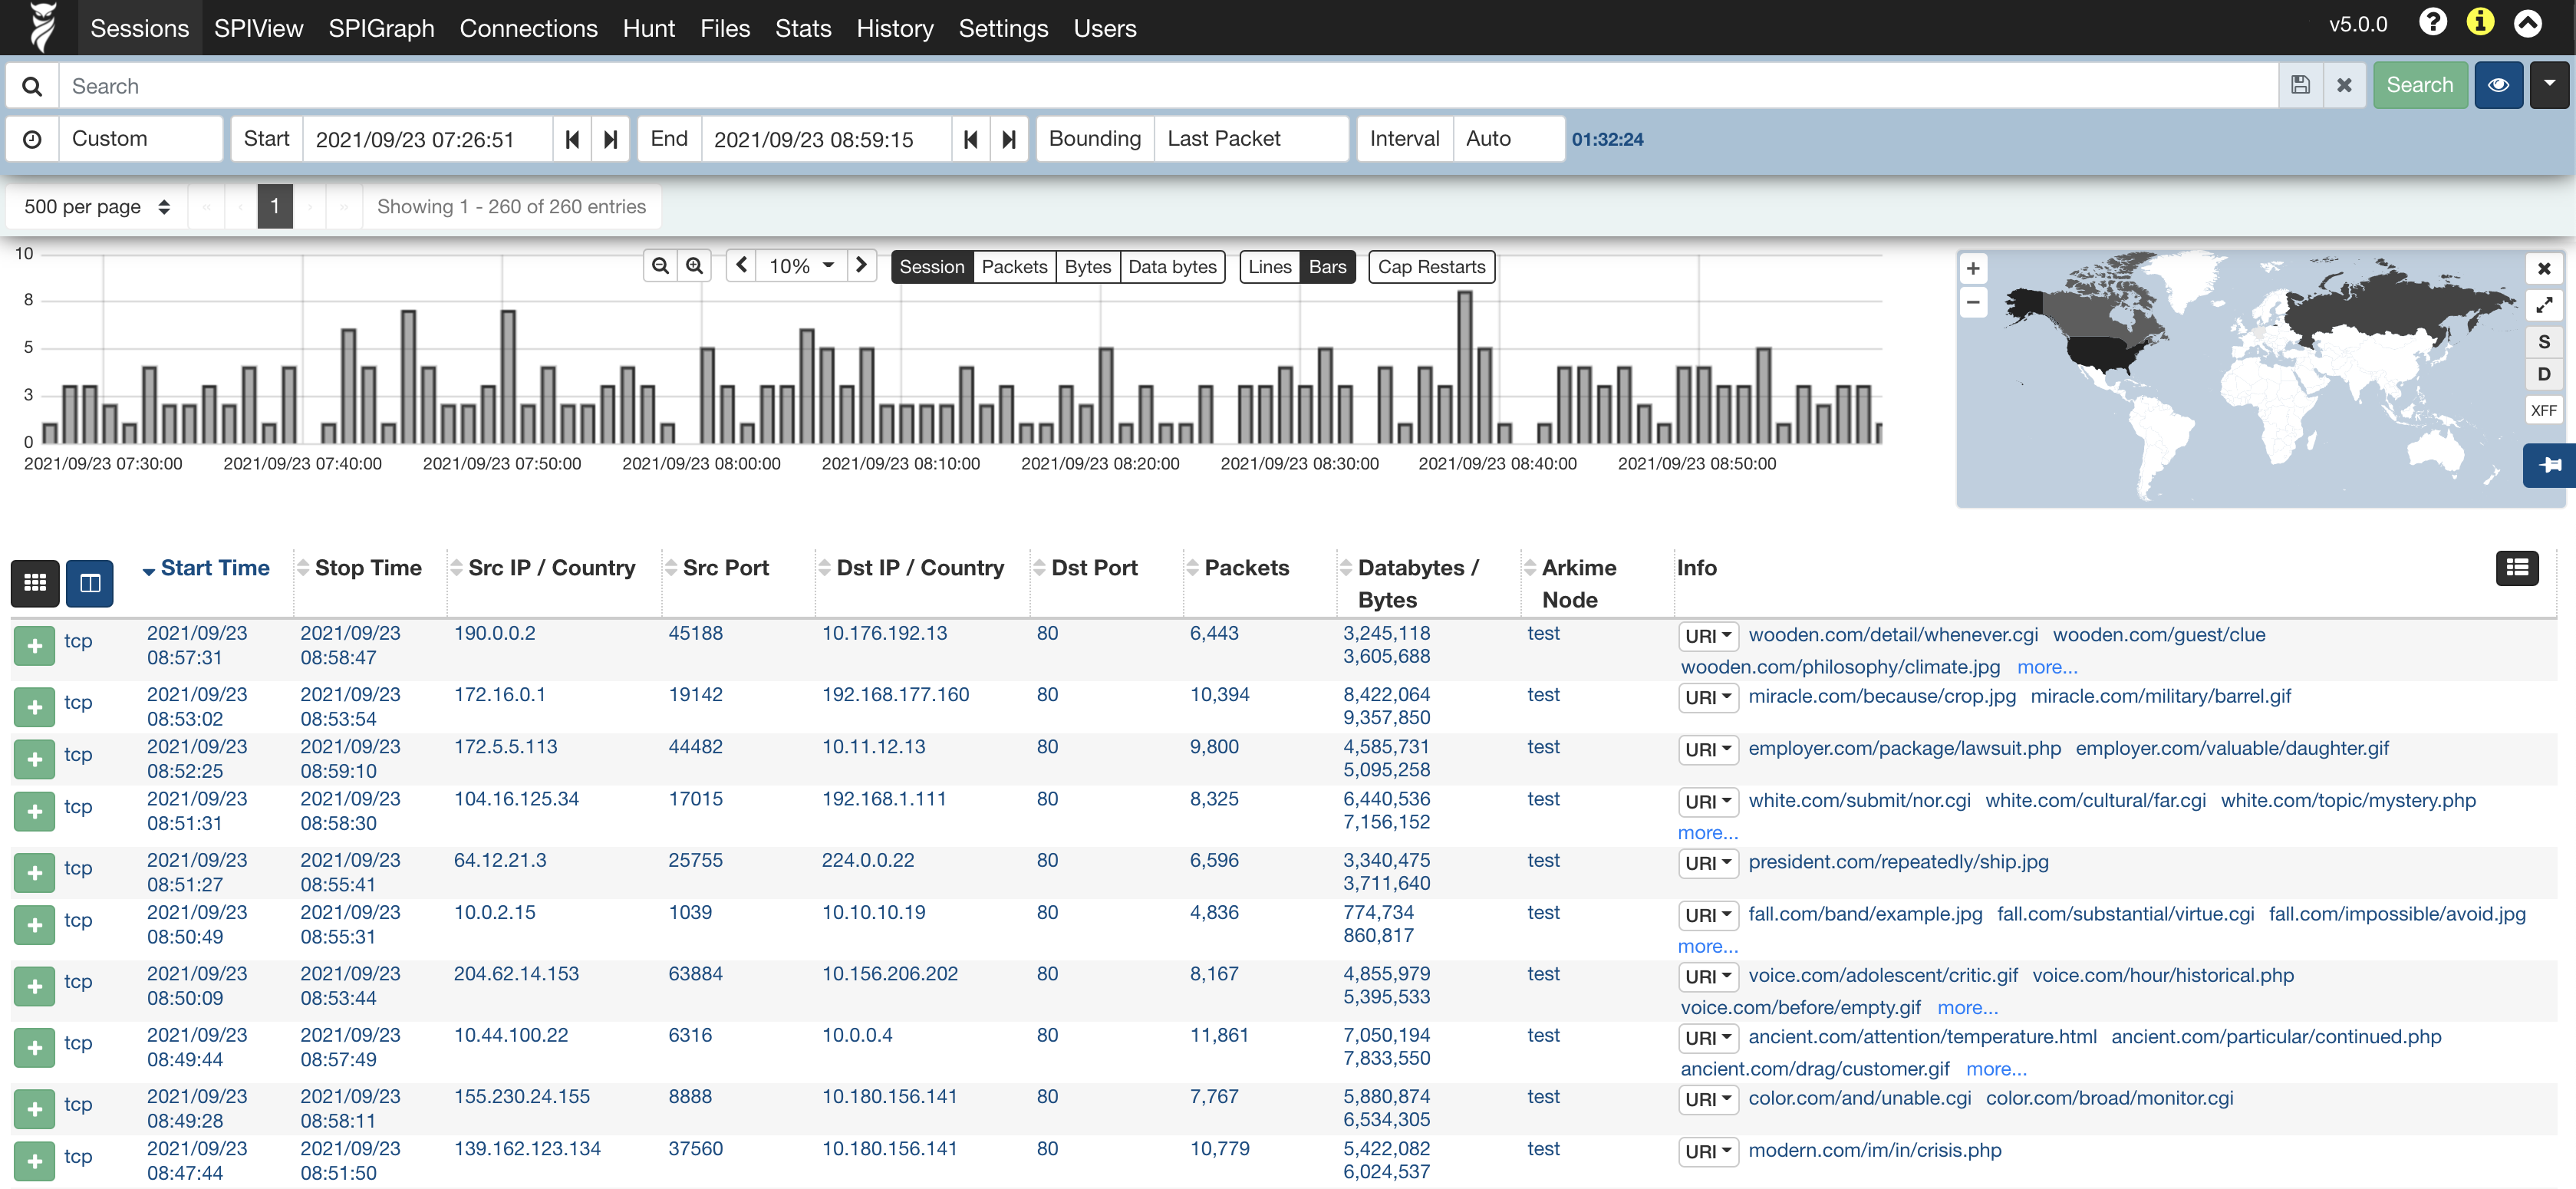
Arkime is an open source, large scale, full packet capturing, indexing, and database system.

Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.

An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.