logdata-anomaly-miner

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

A tool to generate Snort rules based on public IP reputation data

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

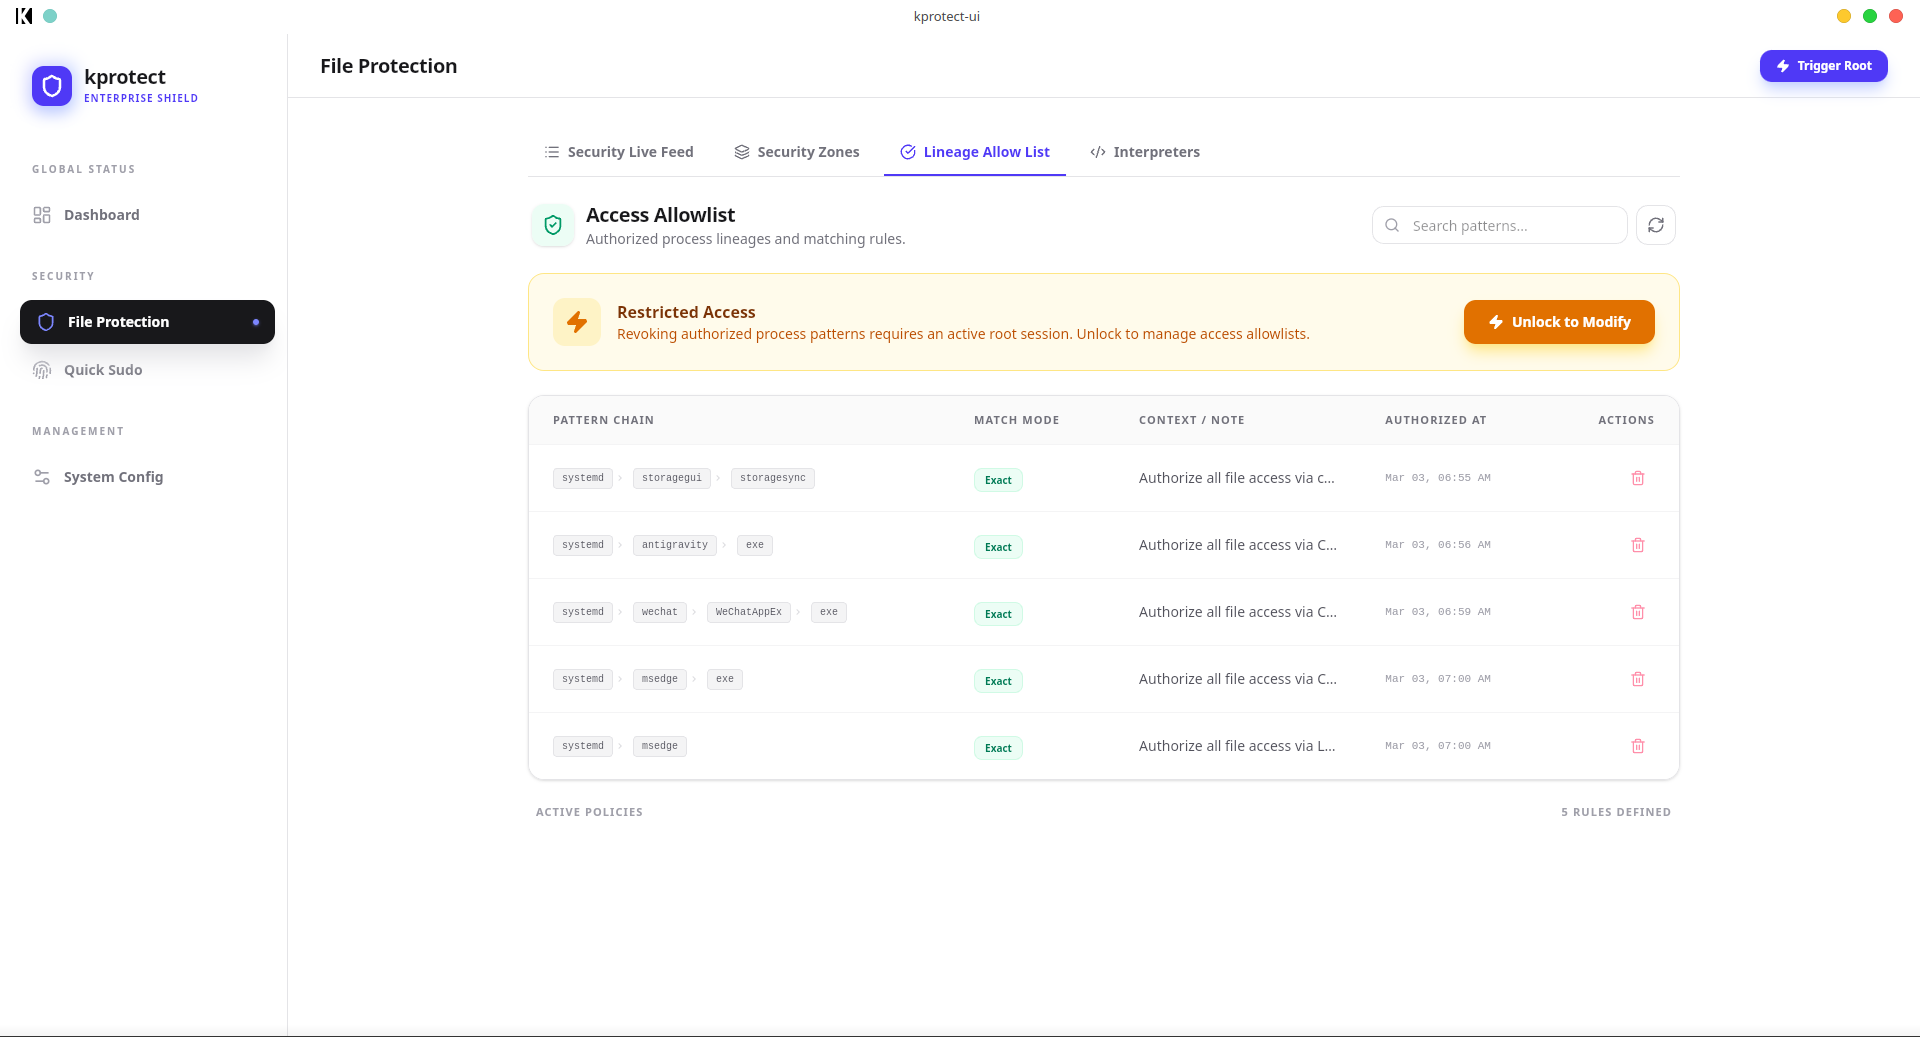
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…

Python-based exploit tool targeting CVE-2016-7144 for penetration testing and vulnerability validation against affected systems.

Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…

JA4+ is a suite of network fingerprinting standards

Deep Learning models for network traffic classification

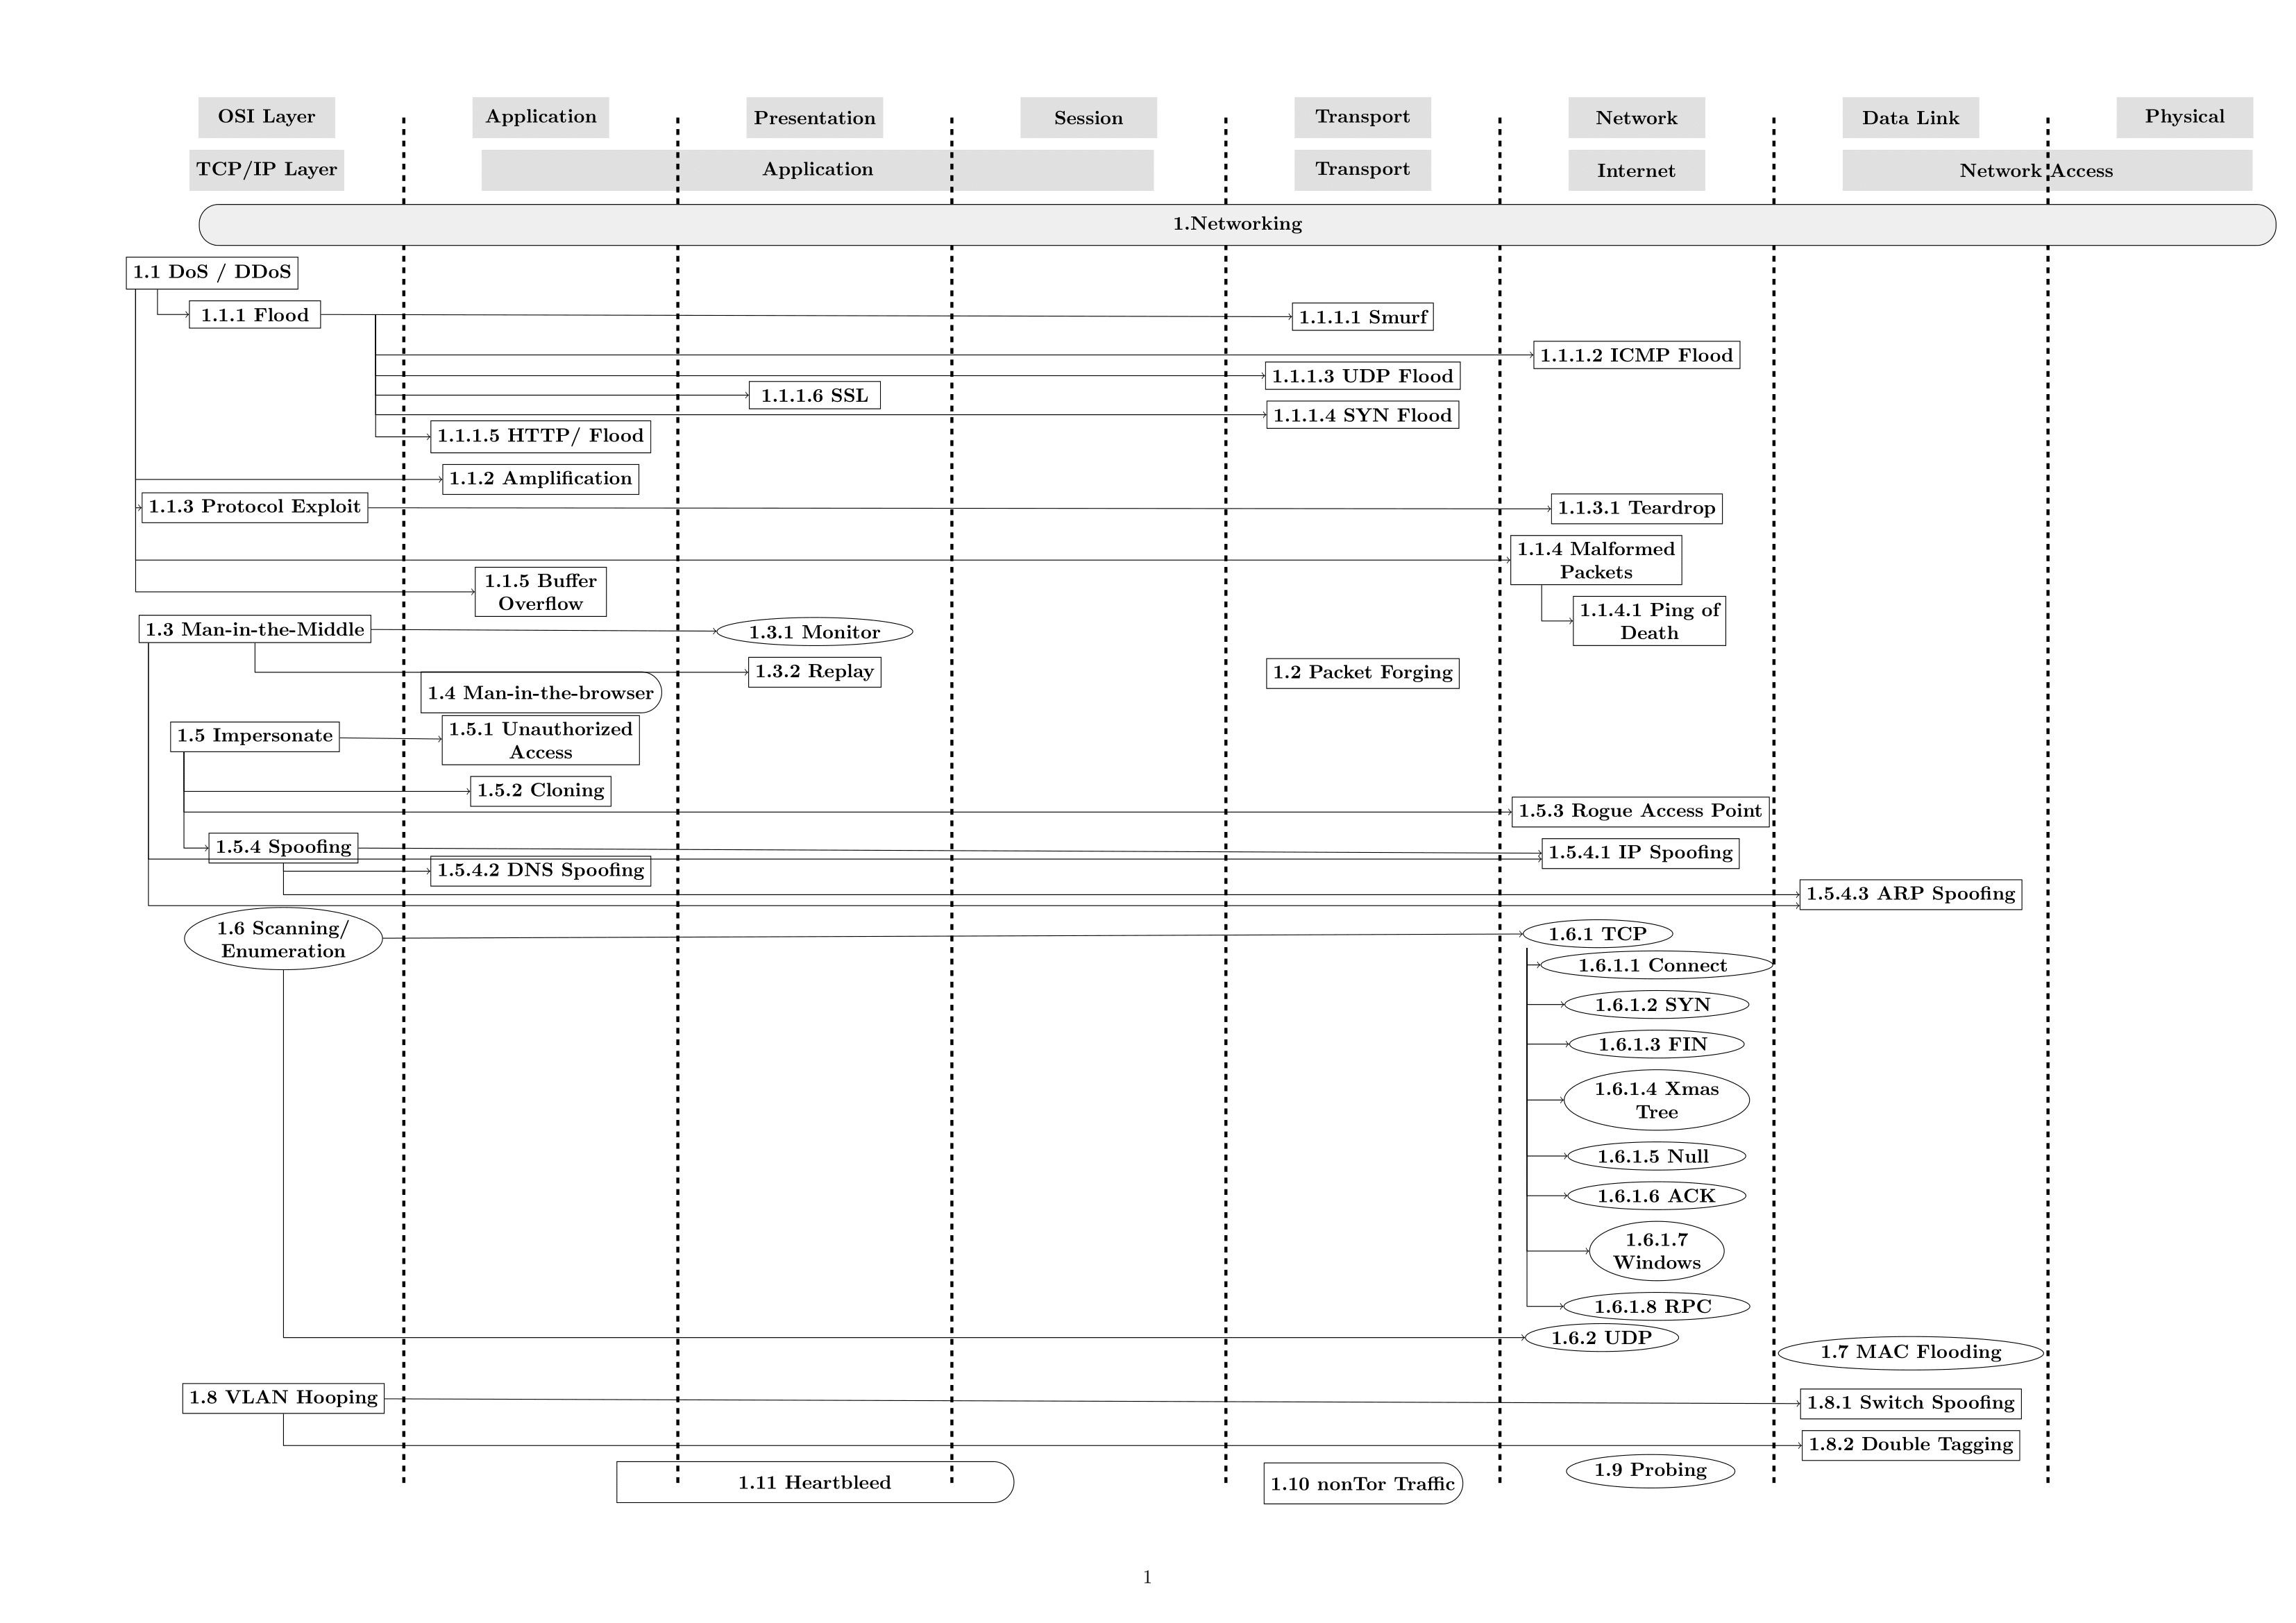
Machine Learning based Intrusion Detection Systems are difficult to evaluate due to a shortage of datasets representing accurately network traffic…

Rust tool to detect cell site simulators on an orbic mobile hotspot

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…

Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.

A network packet forensics tool for SSH

Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)

A tool for malicious behavior detection in IoT devices

Conveigh is a Windows PowerShell LLMNR/NBNS spoofer detection tool