
Azure-Sentinel
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
cloud-securitycurated-resourcesdefensive-tools+5
6.1k
azure/azure-sentinelCloud-native SIEM for intelligent security analytics for your entire enterprise.
 thinkst/canarytokens
Canarytokens helps track activity and actions on your network
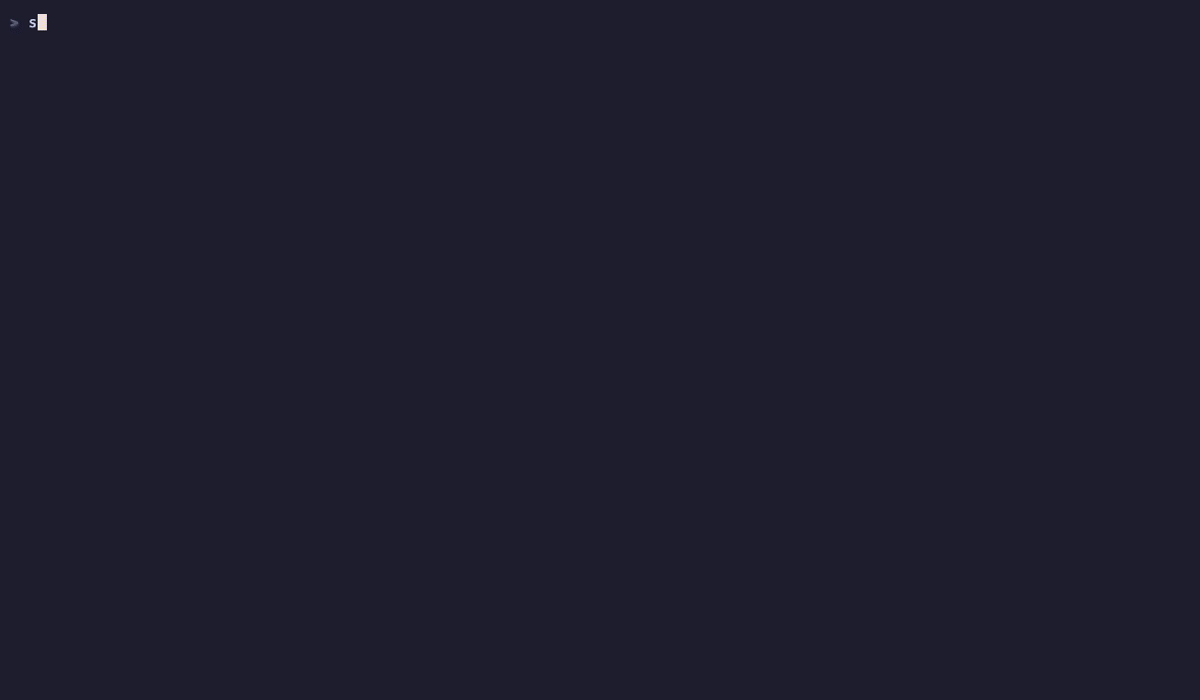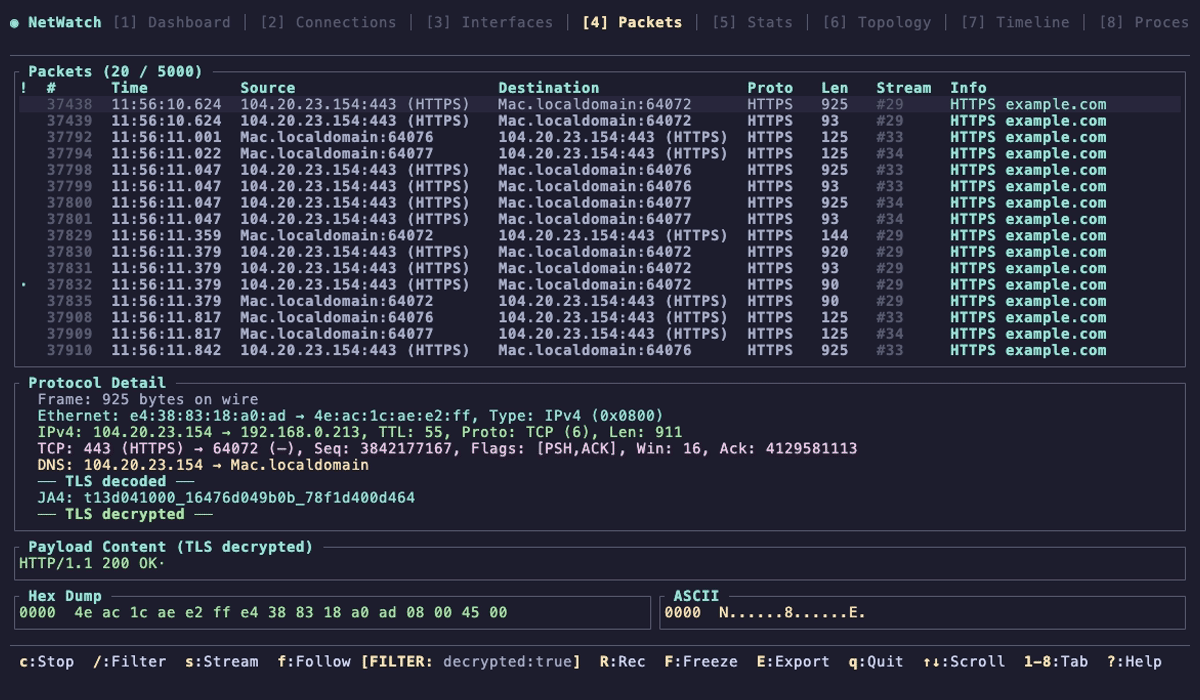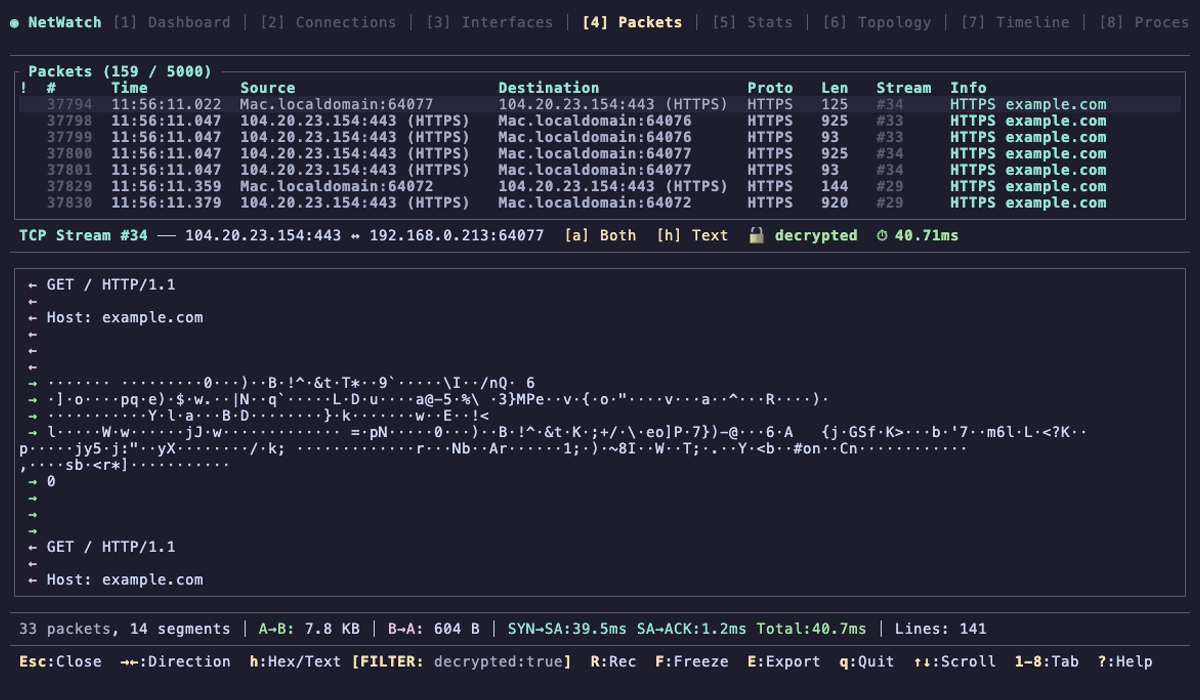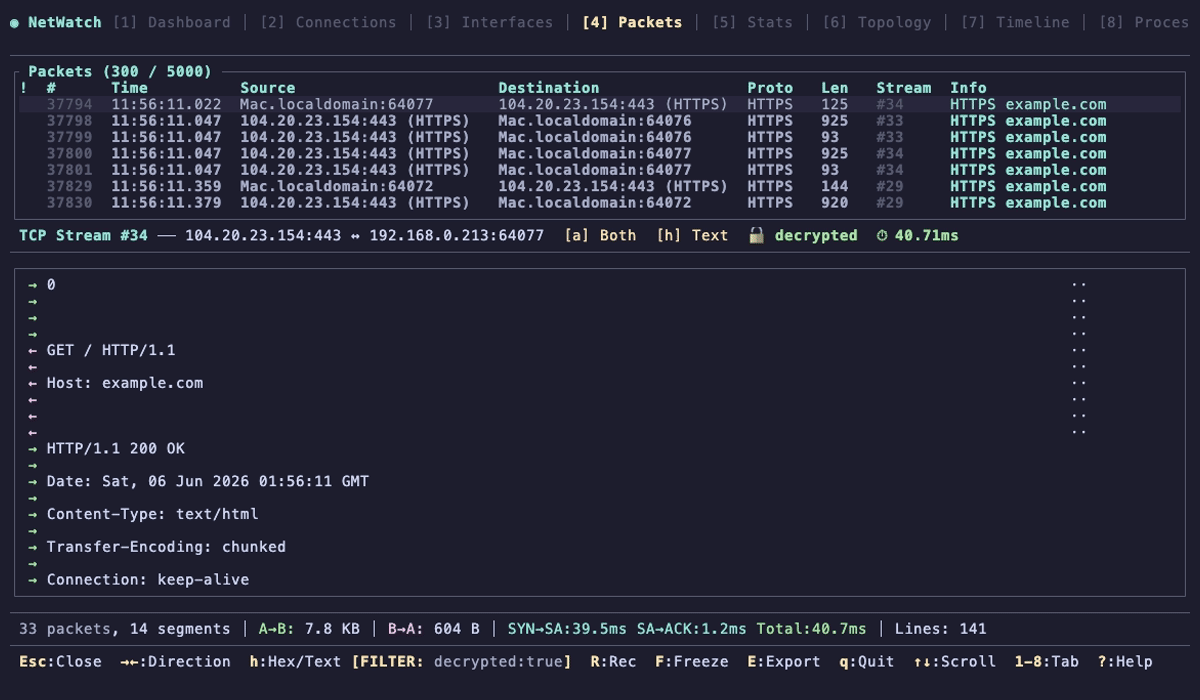 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 thinkst/canarytokens-docker
Docker configuration to quickly setup your own Canarytokens.
 back2root/log4shell-rex
PCRE RegEx matching Log4Shell CVE-2021-44228 IOC in your logs
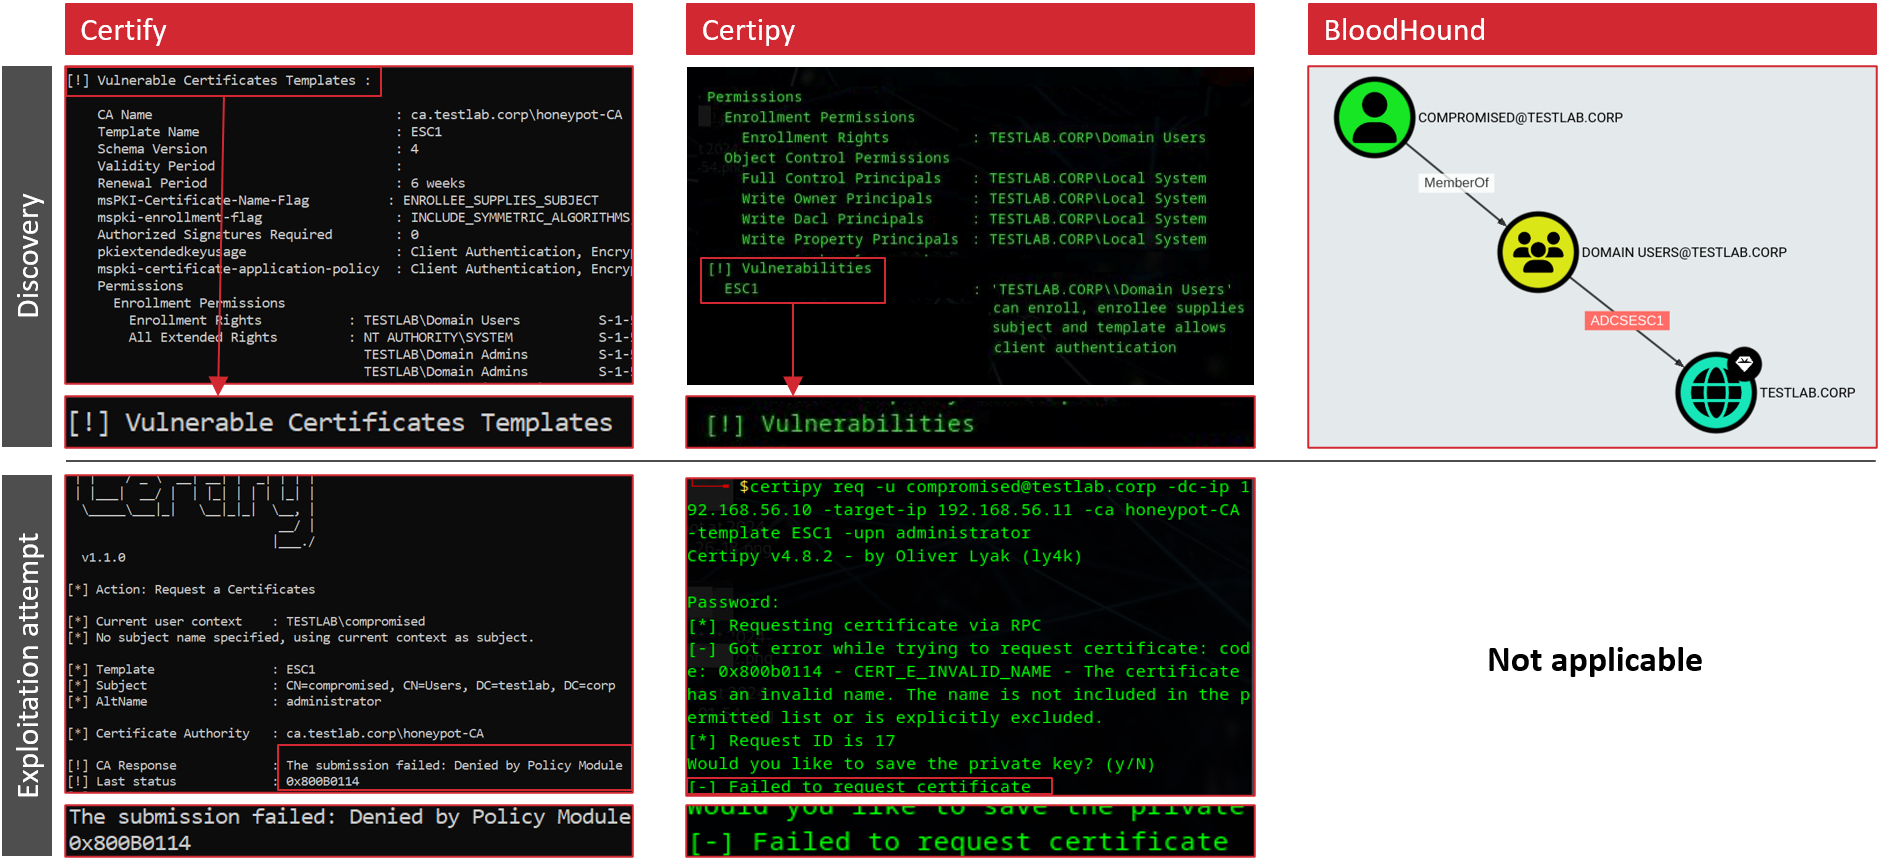 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.
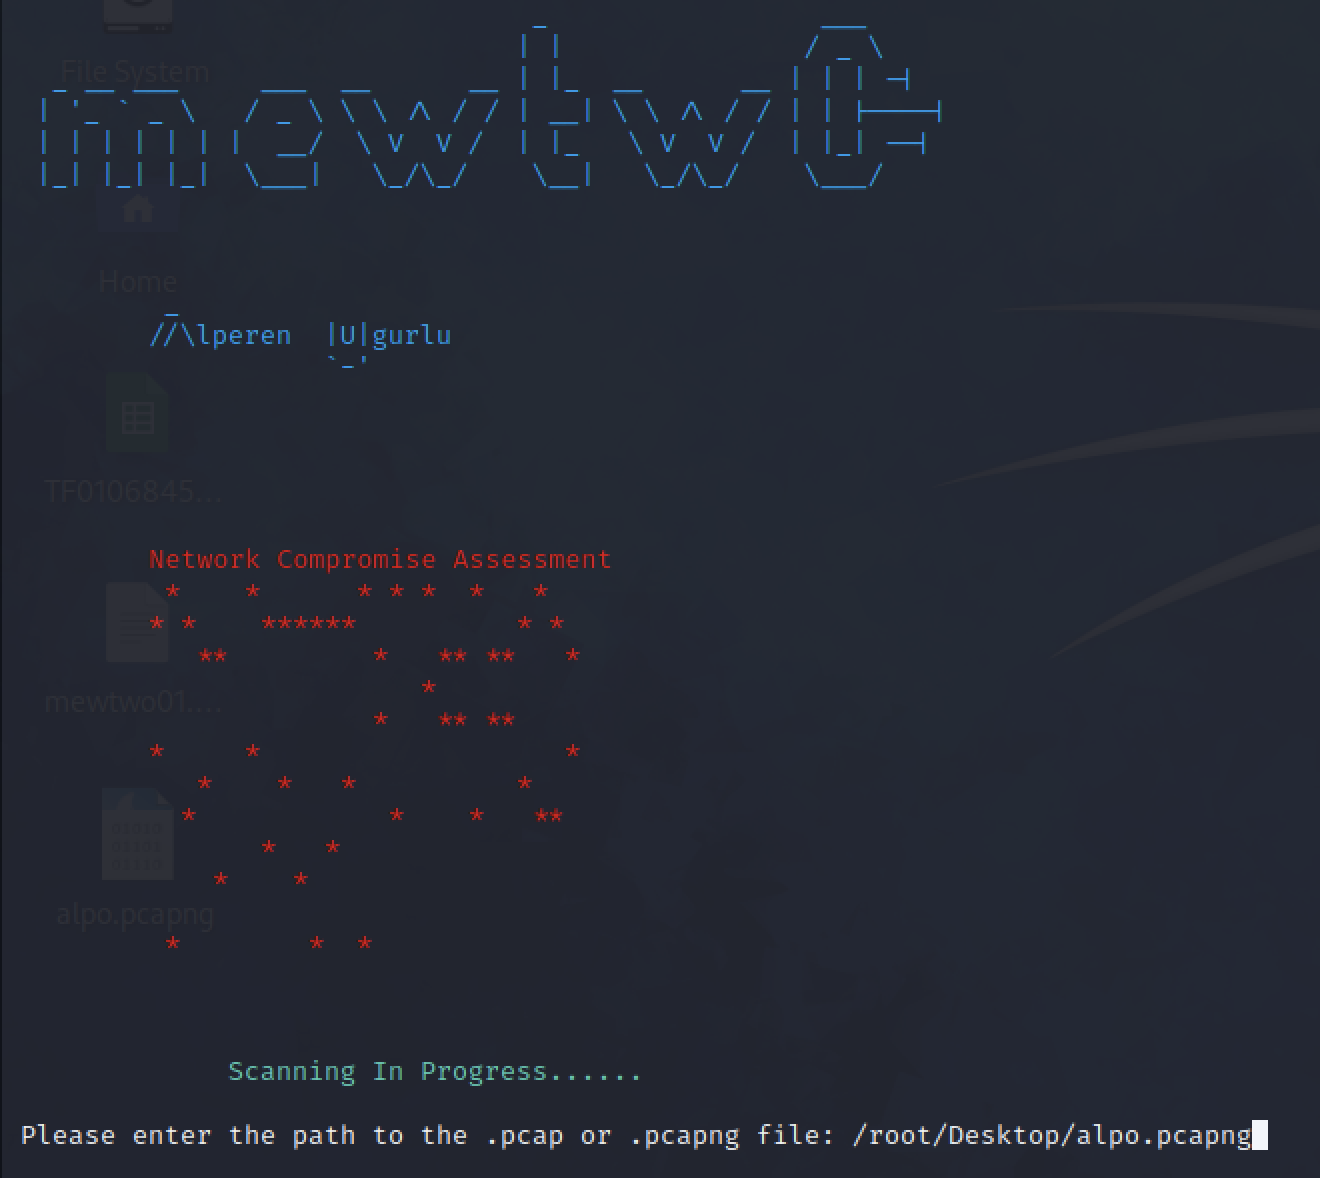 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 binarydefense/log4j-honeypot-flask
Internal network honeypot for detecting if an attacker or insider threat scans your network for log4j CVE-2021-44228
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
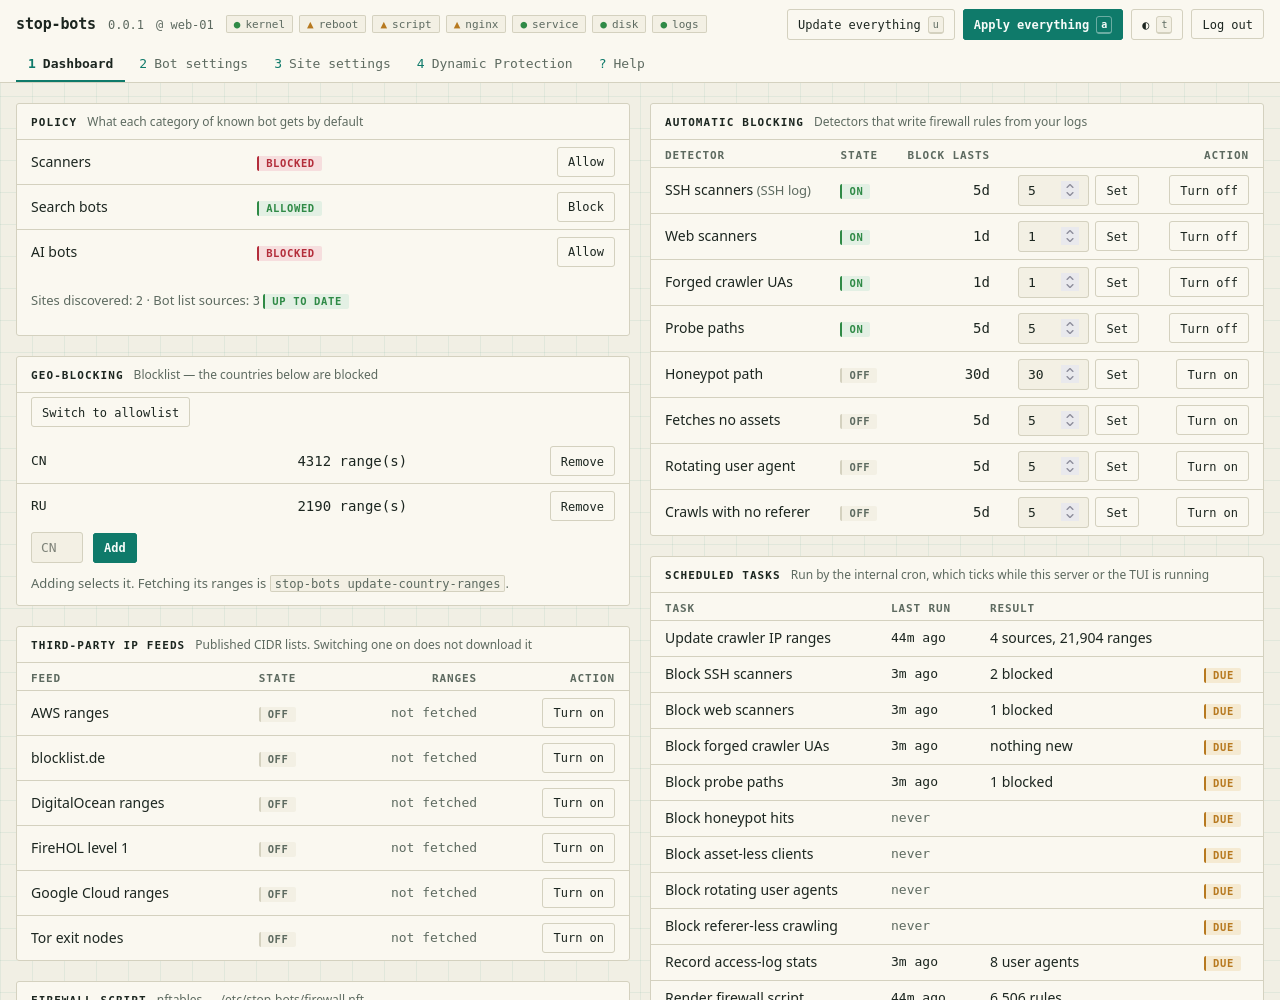 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
 d0n601/wp-mhn
Integrates your Modern Honeypot Network Server and Wordpress Blog via MHN's REST API and WP's shortcodes
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 gossithedog/threathunting
Tools for hunting for threats.
 metlo-labs/metlo
Metlo is an open-source API security platform.