

ehids-agent
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
container-escapedefensive-toolsdns-analysis+5
457
gojue/ehids-agentA Linux Host-based Intrusion Detection System based on eBPF.
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
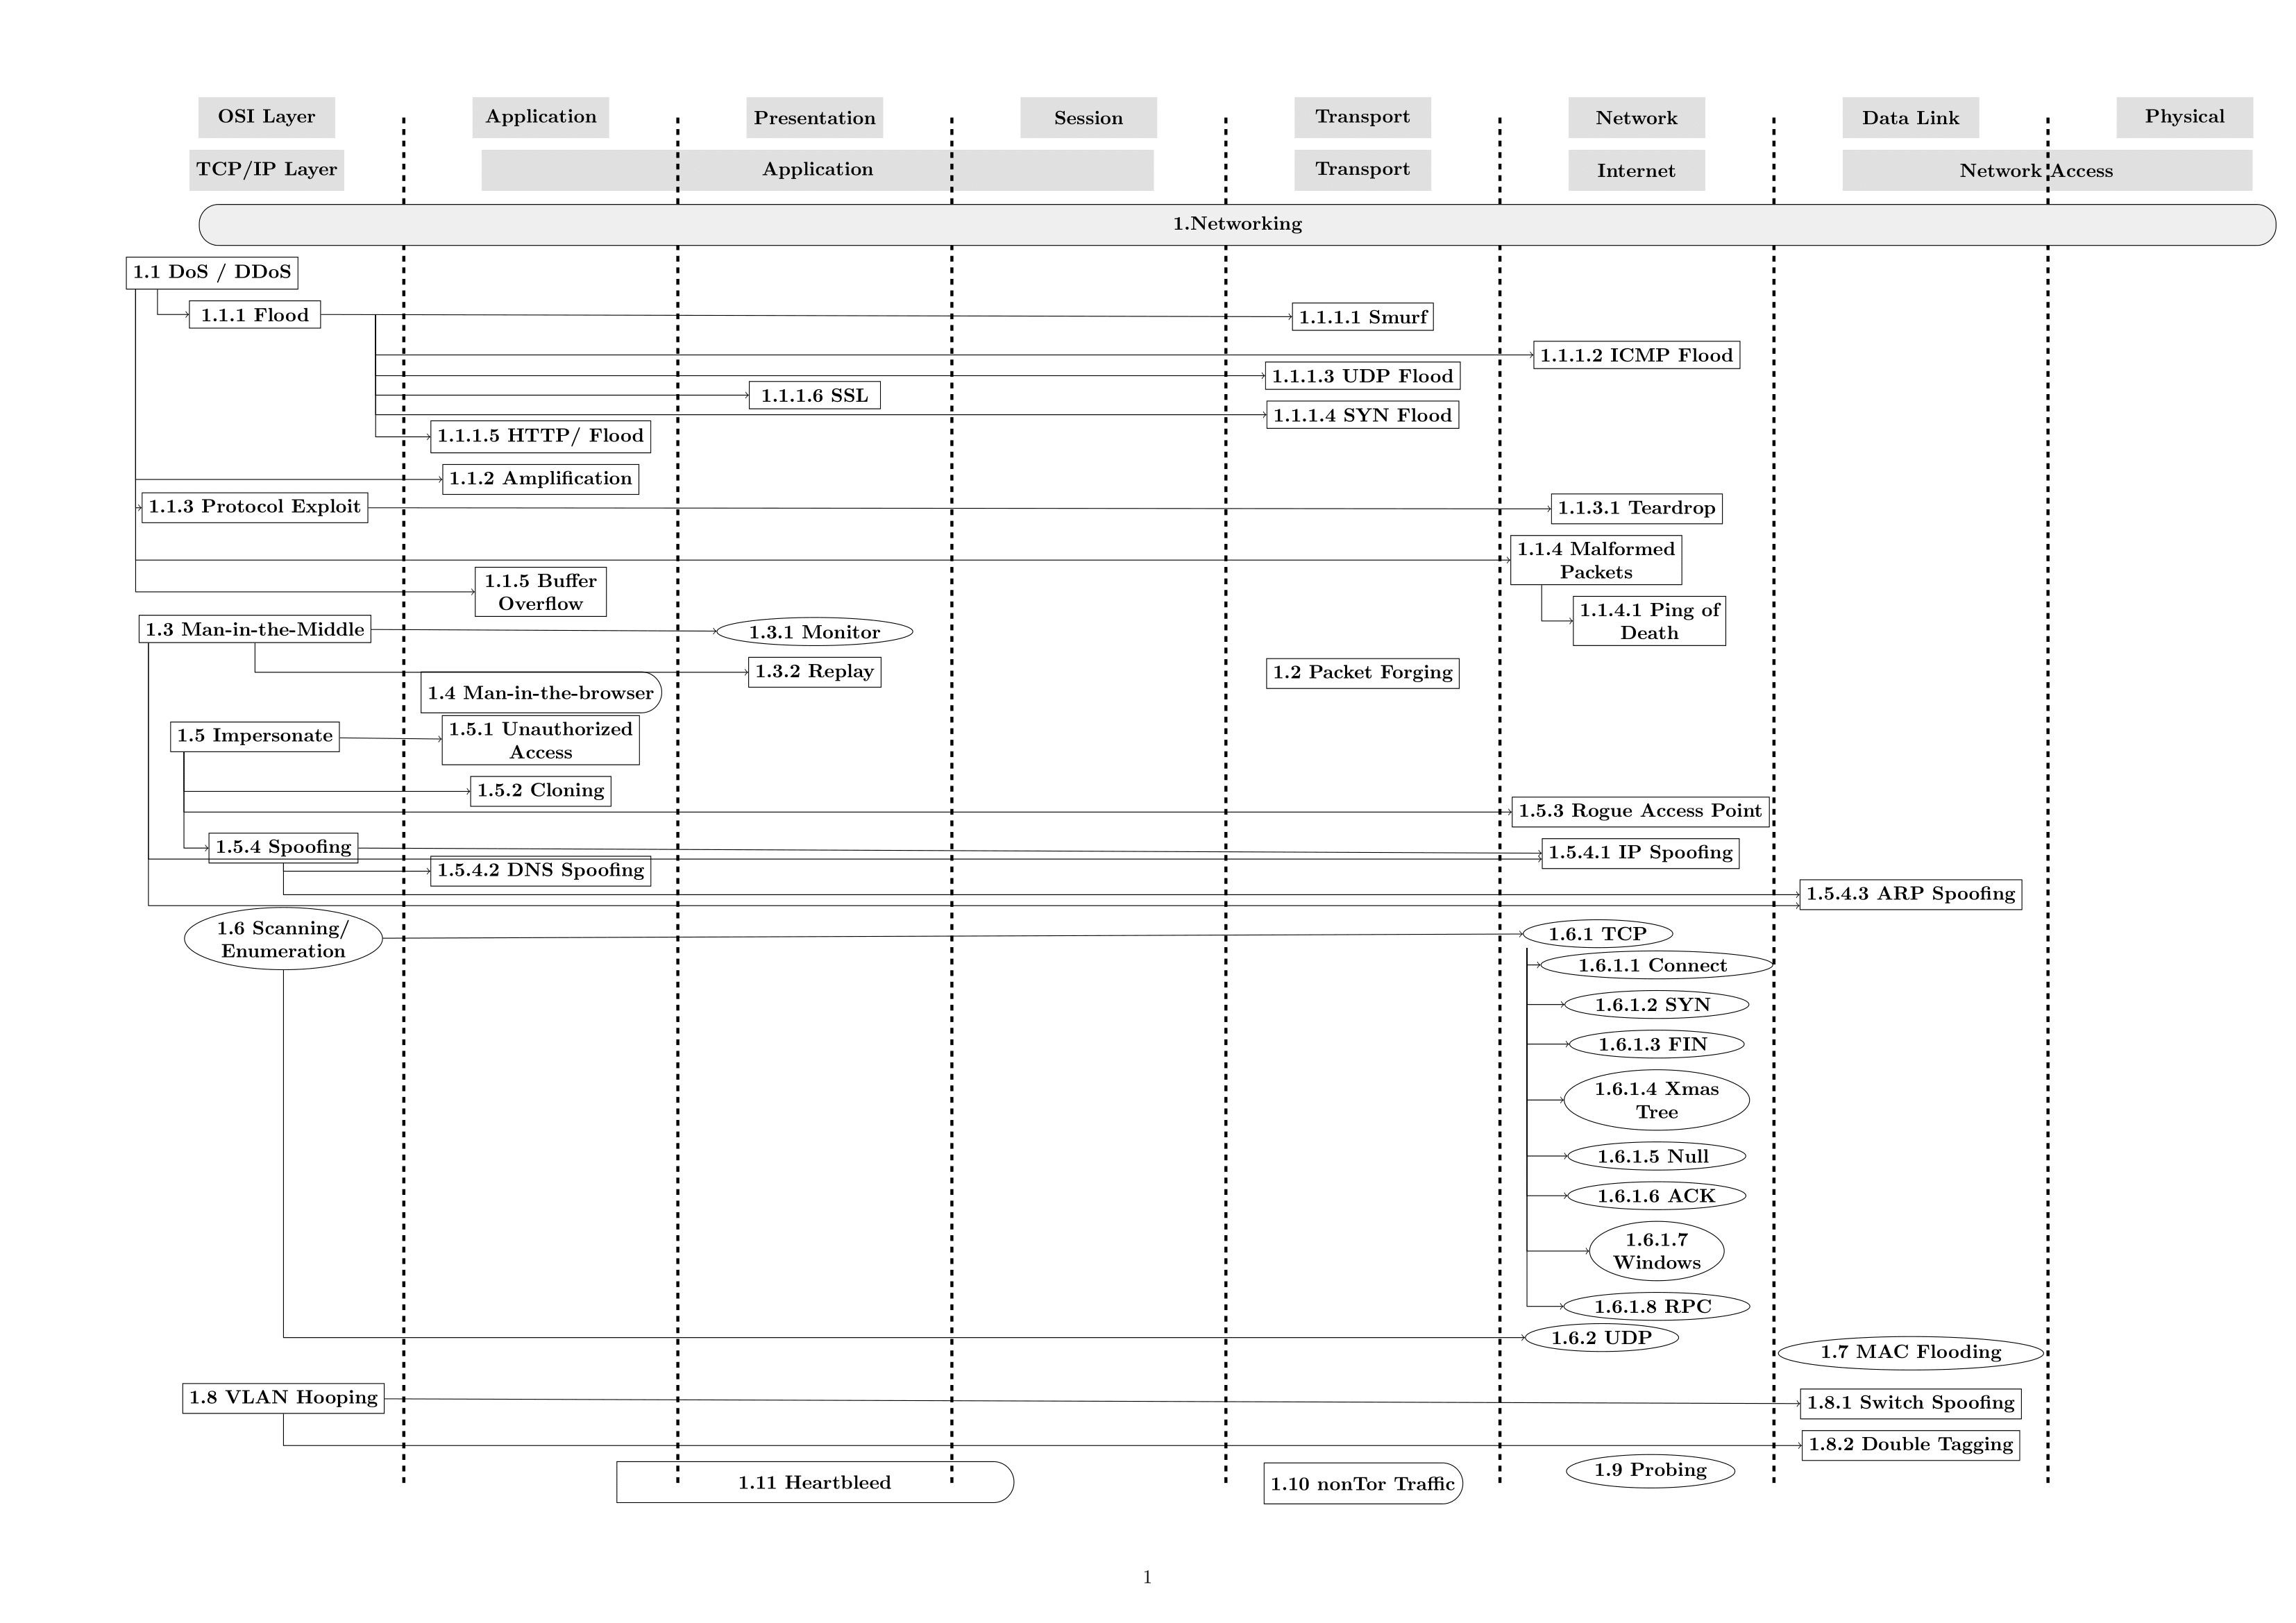 abertaymachinelearninggroup/network-threats-taxonomy
Machine Learning based Intrusion Detection Systems are difficult to evaluate due to a shortage of datasets representing accurately network traffic…
 fksvs/siper
XDP Based Lightweight and Fast Firewall
 nccgroup/ip-reputation-snort-rule-generator
A tool to generate Snort rules based on public IP reputation data
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
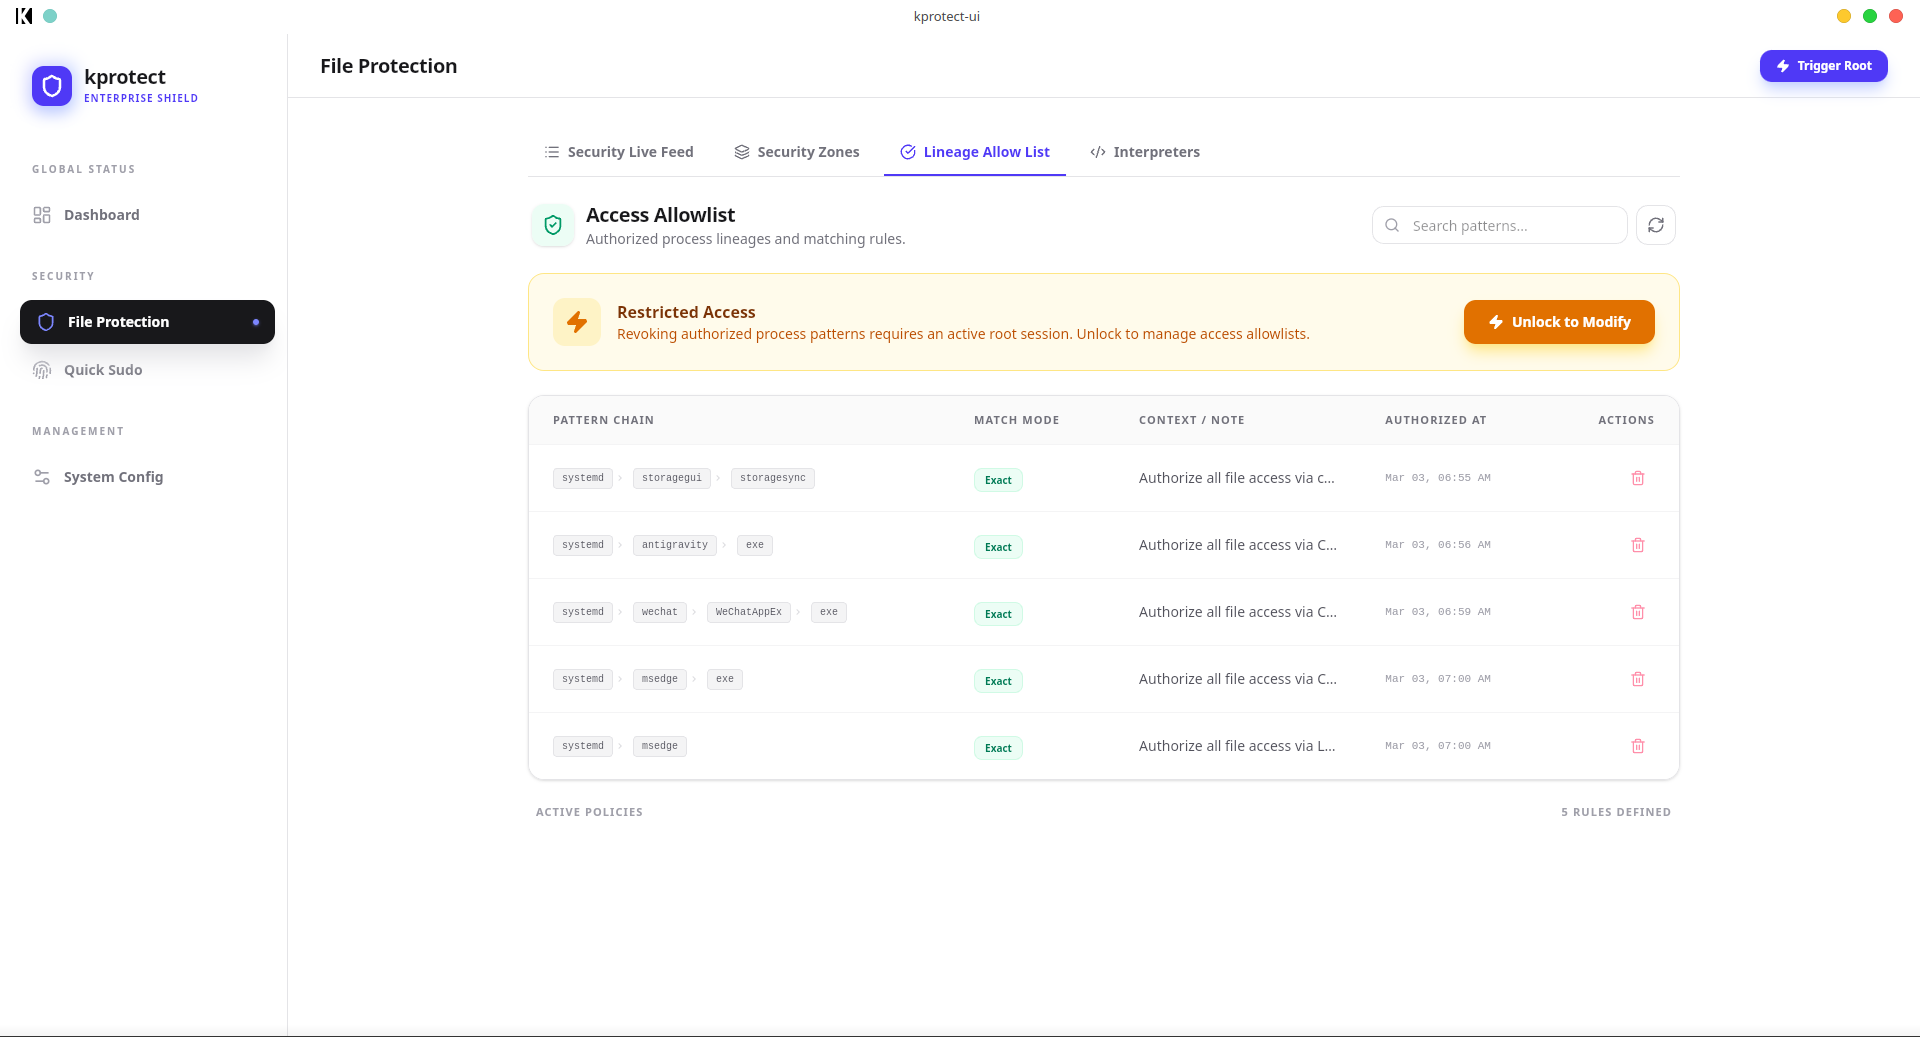 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 corelight/zeek-spicy-openvpn
A Zeek OpenVPN protocol analyzer, based on Spicy.
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.

 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
 corelight/zeek-strrat-detector
A Zeek based STRRAT malware detector.
 corelight/zeek-agenttesla-detector
A Zeek based Agent Tesla malware C2 detector.
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 corelight/zeek-gozi-detector
A Zeek based Gozi banking malware detector.