CVE-2025-68616-Detecting-and-Patching-an-SSRF-in-WeasyPrint-with-Wazuh

Hands-on vulnerability management case study: how Wazuh flagged a real SSRF (CVE-2025-68616) in WeasyPrint, and how I reproduced and patched it.

Hands-on vulnerability management case study: how Wazuh flagged a real SSRF (CVE-2025-68616) in WeasyPrint, and how I reproduced and patched it.

Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…

Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…

A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.

eBPF Security Monitoring and Sandboxing Agent Based on Aya

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.

Daemon to ban hosts that cause multiple authentication errors

Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…

Interactive GNU/Linux application firewall that filters outbound connections, blocks ads and malware domains, manages system firewall rules via GUI,…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

Purpleteam scripts simulation & Detection - trigger events for SOC detections

Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis

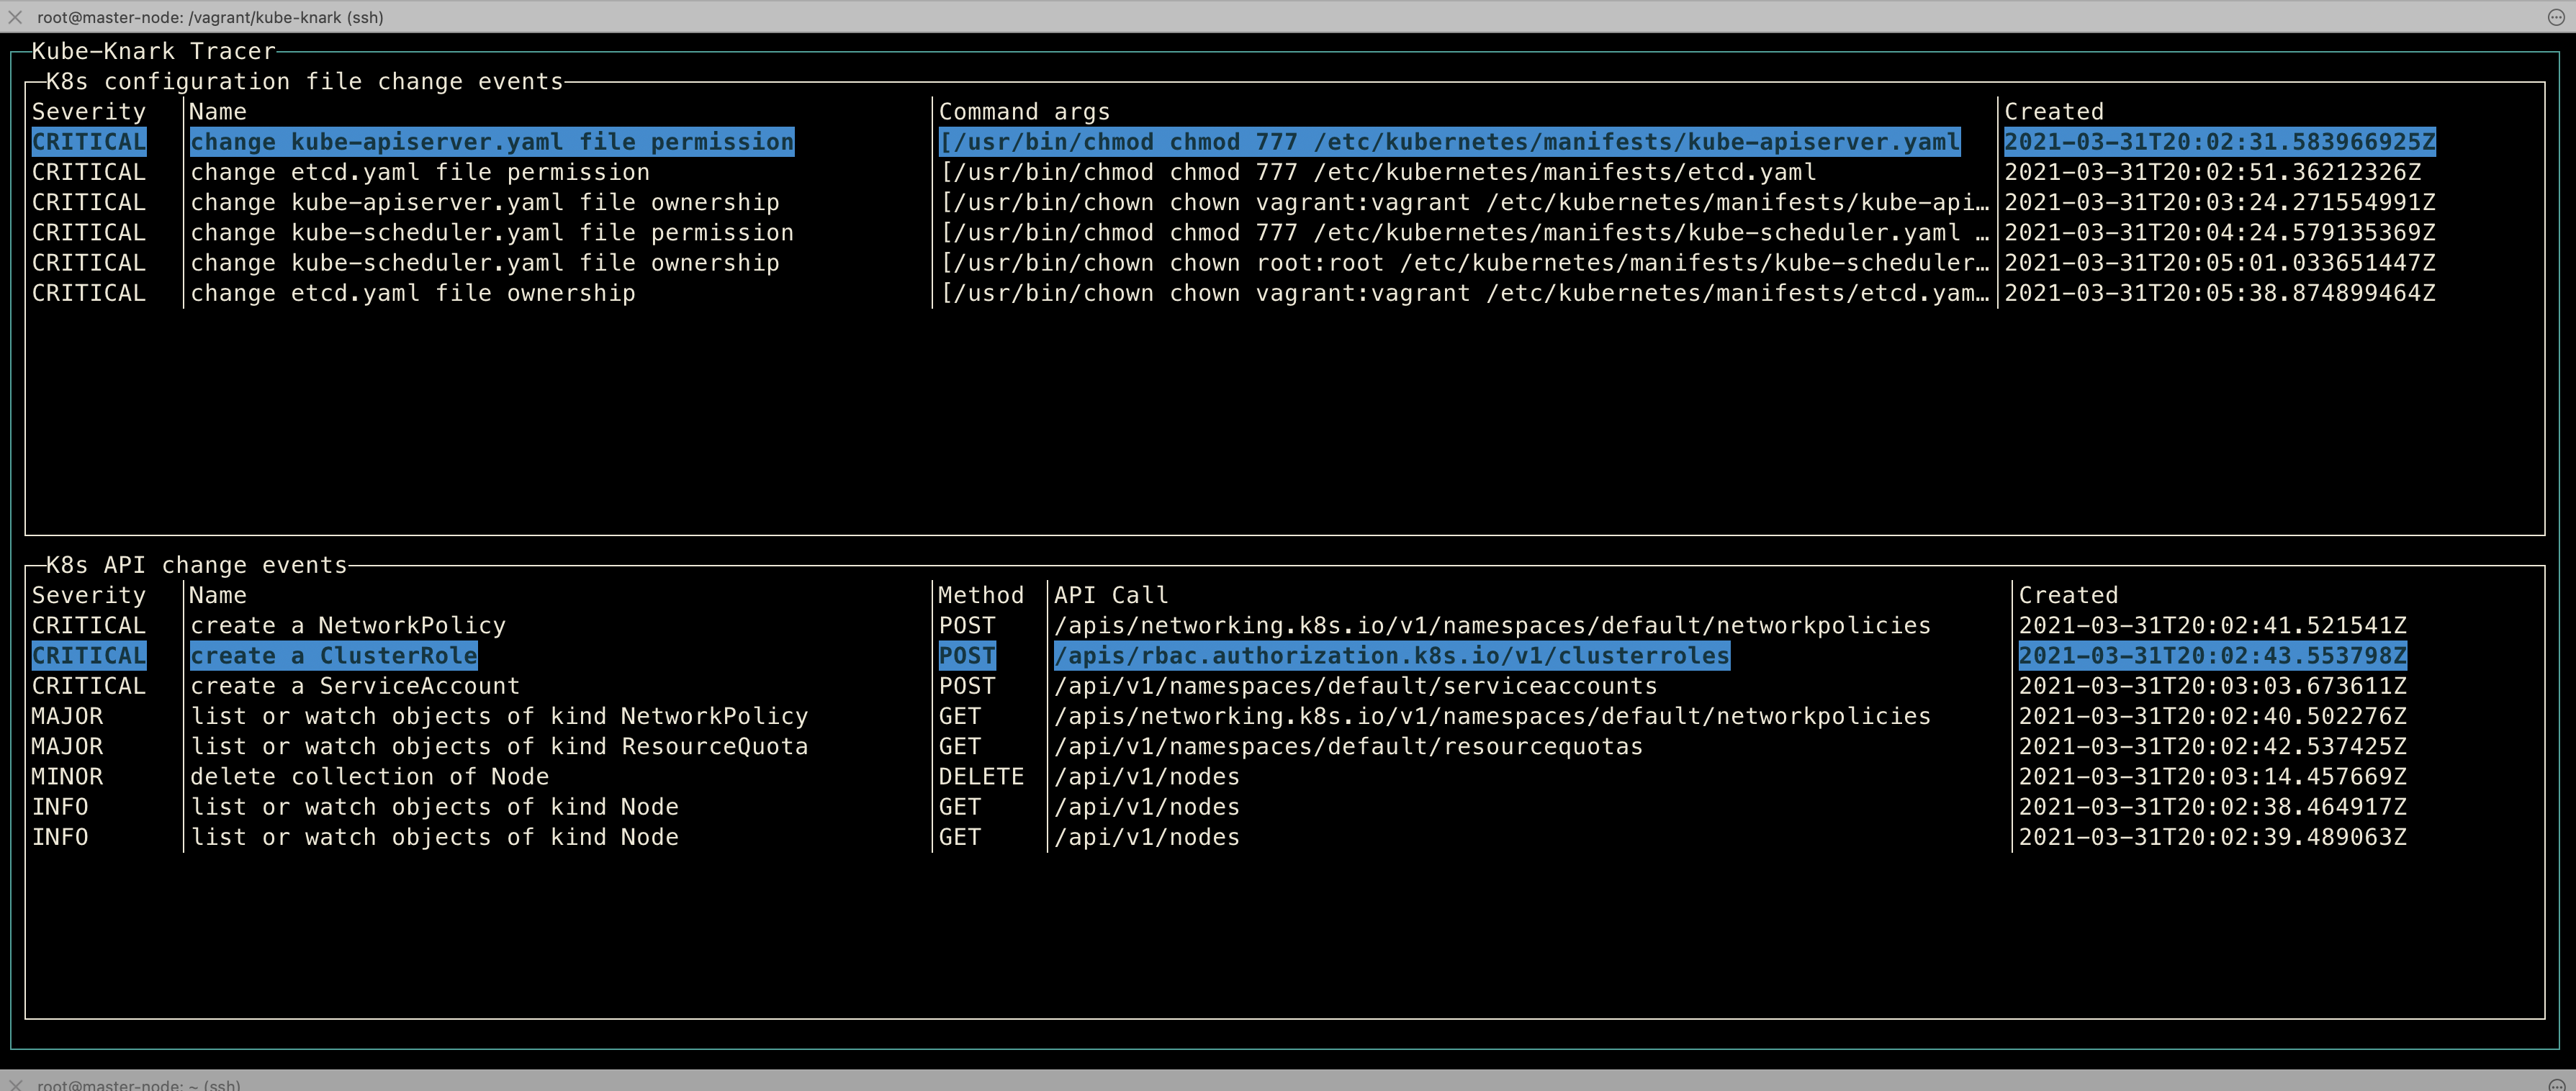
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…

SQL powered operating system instrumentation, monitoring, and analytics.

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

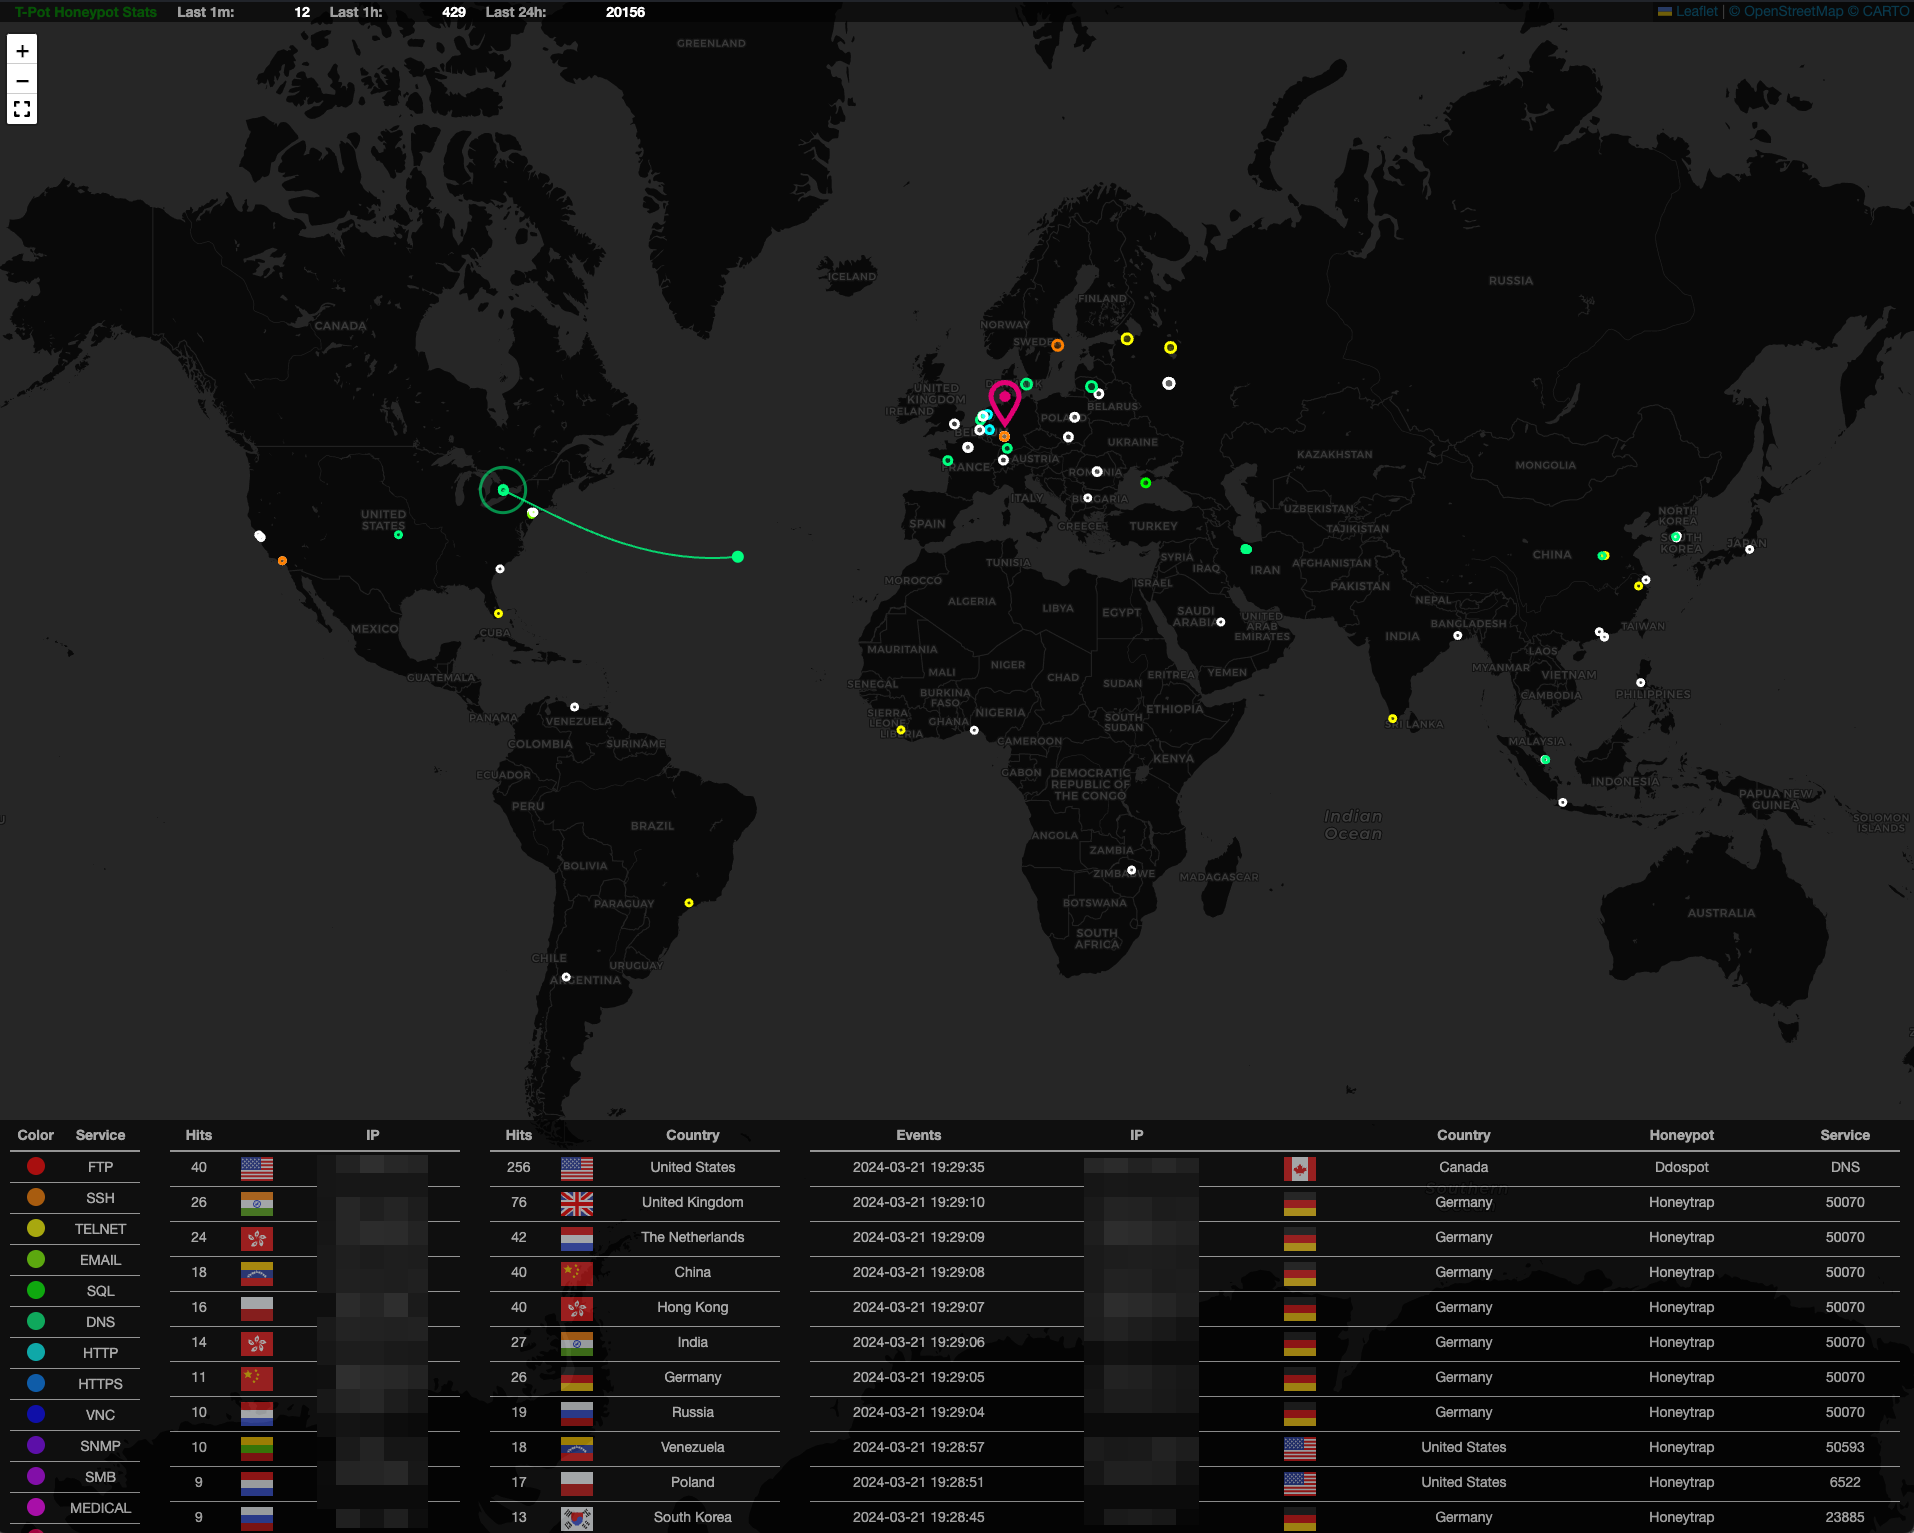
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝