
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
583 results
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
481
26 days ago
dionaea preview

dionaea

GitHubdinotools/dionaea

Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.

defensive-toolsintrusion-detectionmalware-analysis+2
8192 years ago
ioc preview

ioc

GitHubgendigitalinc/ioc

Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.

defensive-toolsintrusion-detectionioc-management+3
4593 months ago
threat-intel preview

threat-intel

GitHubvolexity/threat-intel

Signatures and IoCs from public Volexity blog posts.
defensive-toolsintrusion-detectionioc-management+4
37211 days ago
EnableWindowsLogSettings preview

EnableWindowsLogSettings

GitHubyamato-security/enablewindowslogsettings

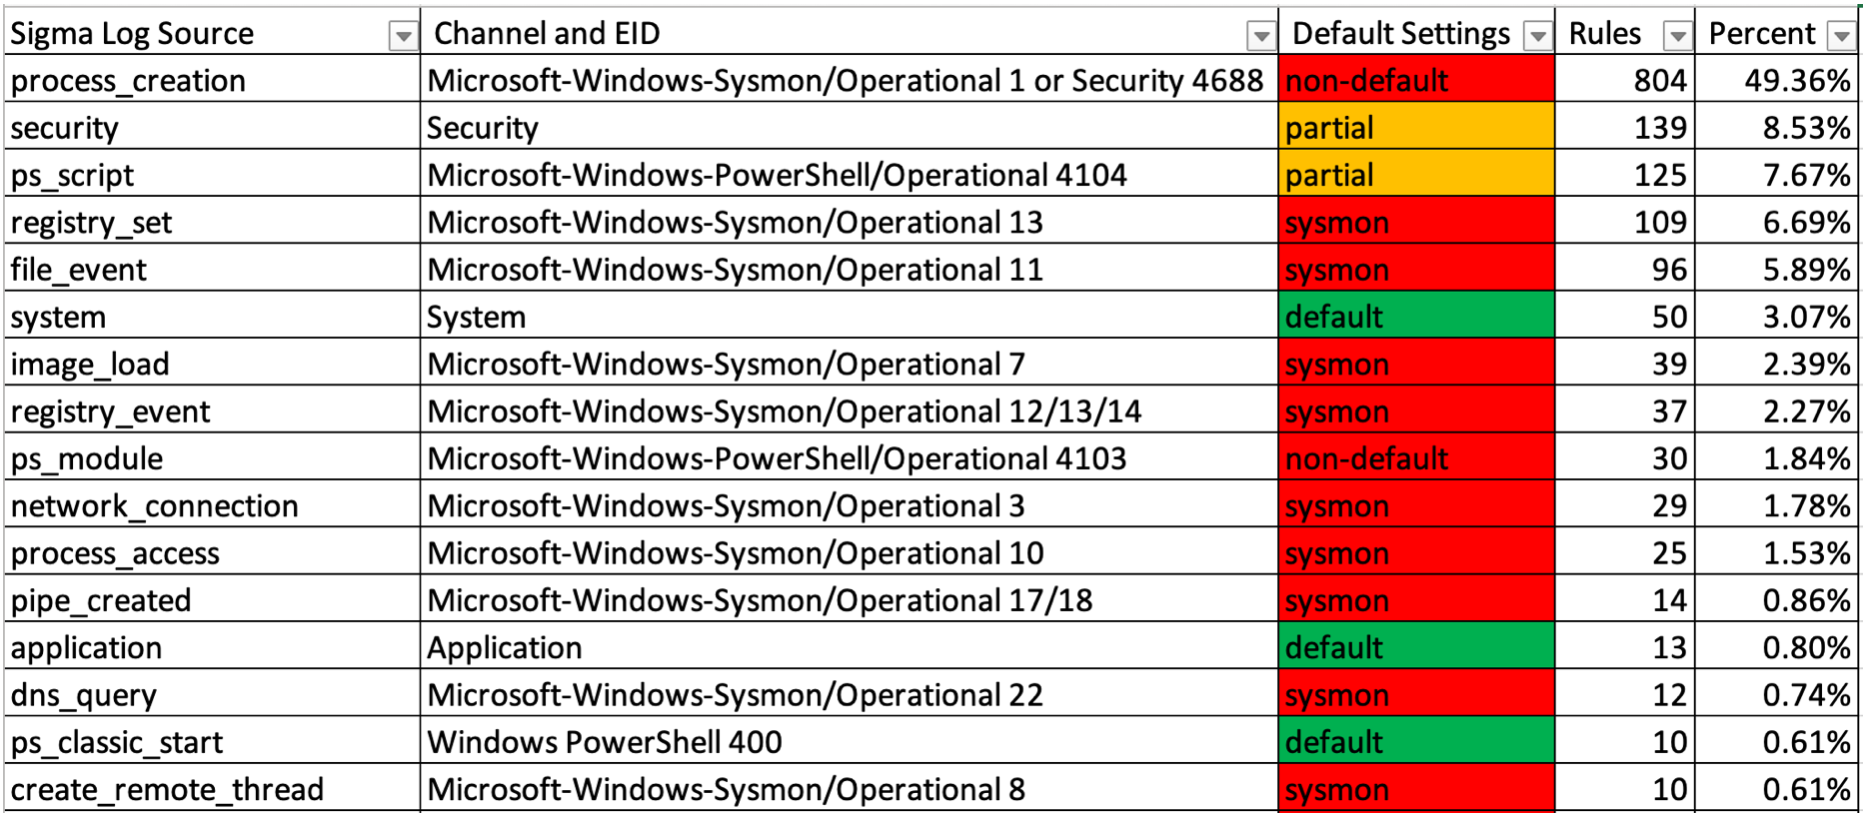
Documentation and scripts to properly enable Windows event logs.

configuration-auditingdefensive-toolsdigital-forensics+3
71911 months ago
so-crates preview

so-crates

GitHubdougburks/so-crates

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
container-securitydigital-forensicseducation+8
60526 days ago
scirius preview

scirius

GitHubstamusnetworks/scirius

Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…

defensive-toolsintrusion-detectionnetwork-security+3
6861 year ago
iMonitor preview

iMonitor

GitHubwecooperate/imonitor

Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…

forensicsintrusion-detectionmalware-analysis+1
8361 year ago
S1EM preview

S1EM

GitHubv1d1an/s1em

This project is a SIEM with SIRP and Threat Intel, all in one.
educationforensicsincident-response+6
4621 year ago
FalconEye preview

FalconEye

GitHubrajiv2790/falconeye

Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…

binary-analysisdefensive-toolsintrusion-detection+1
3105 years ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
6413 months ago
NtWarden preview

NtWarden

GitHubmrt4ntr4/ntwarden

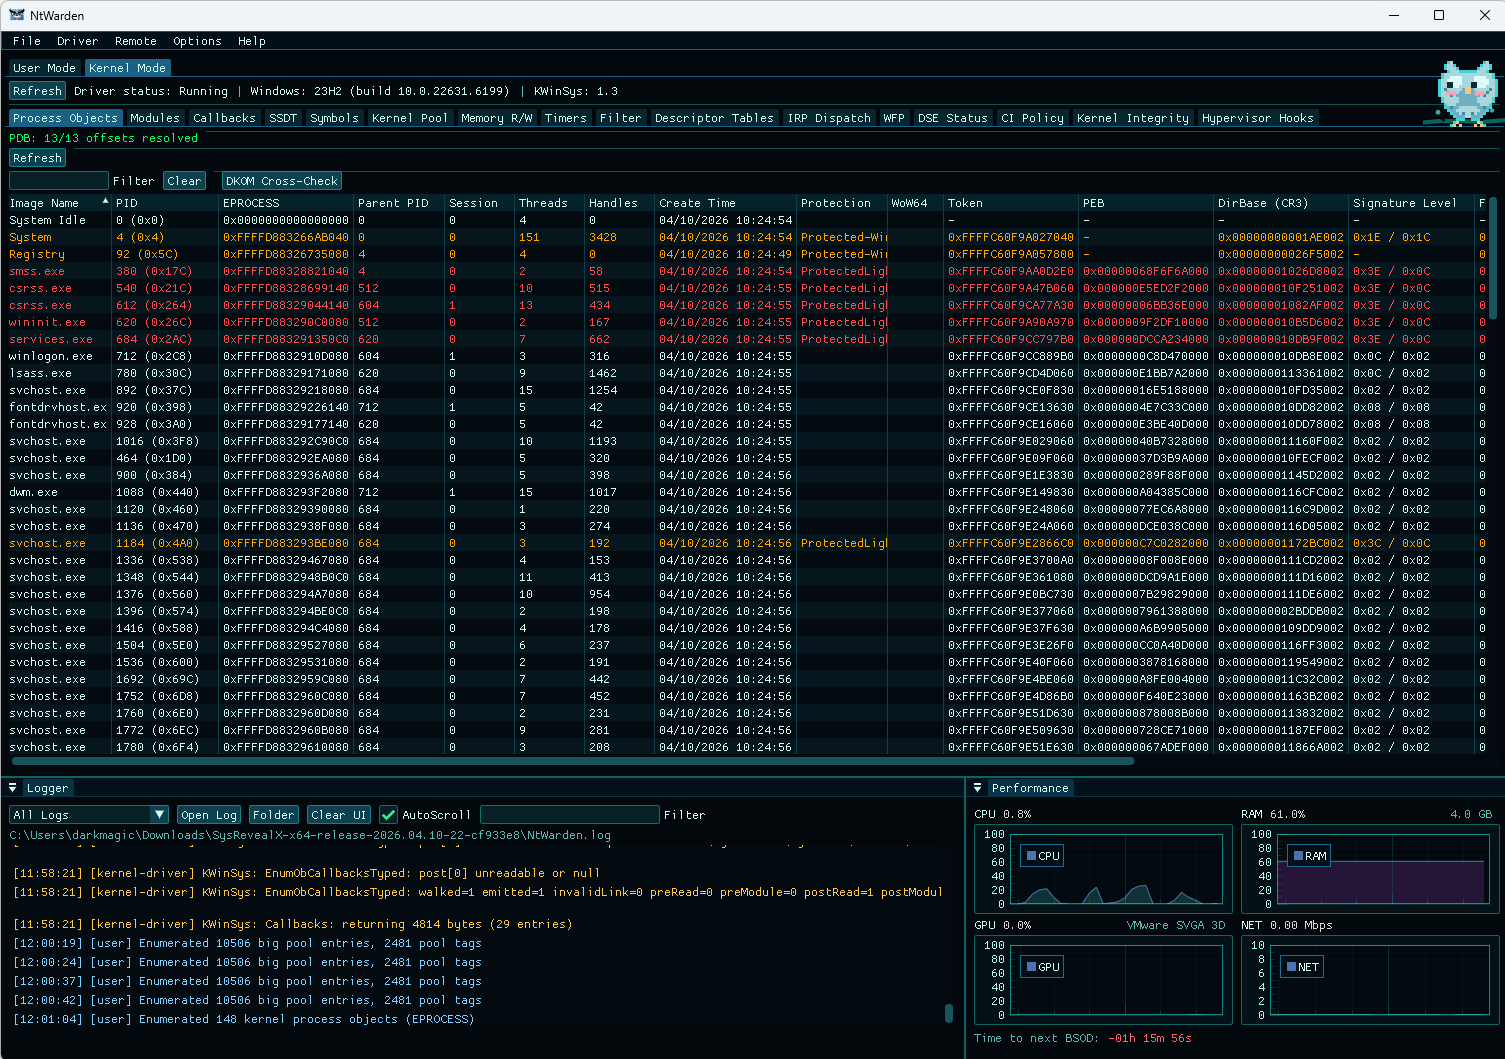
Windows Analysis and Research Toolkit
binary-analysisdefensive-toolsdigital-forensics+4
6914 months ago
pulledpork preview

pulledpork

GitHubshirkdog/pulledpork

Pulled Pork for Snort and Suricata rule management (from Google code)

configuration-auditingintrusion-detectionnetwork-security+2
4445 years ago
Honeypot-Project preview

Honeypot-Project

GitHubowasp/honeypot-project

Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
defensive-toolseducationincident-response+5
10821 days ago
SecurityClaw preview

SecurityClaw

GitHubsecurityclaw/securityclaw

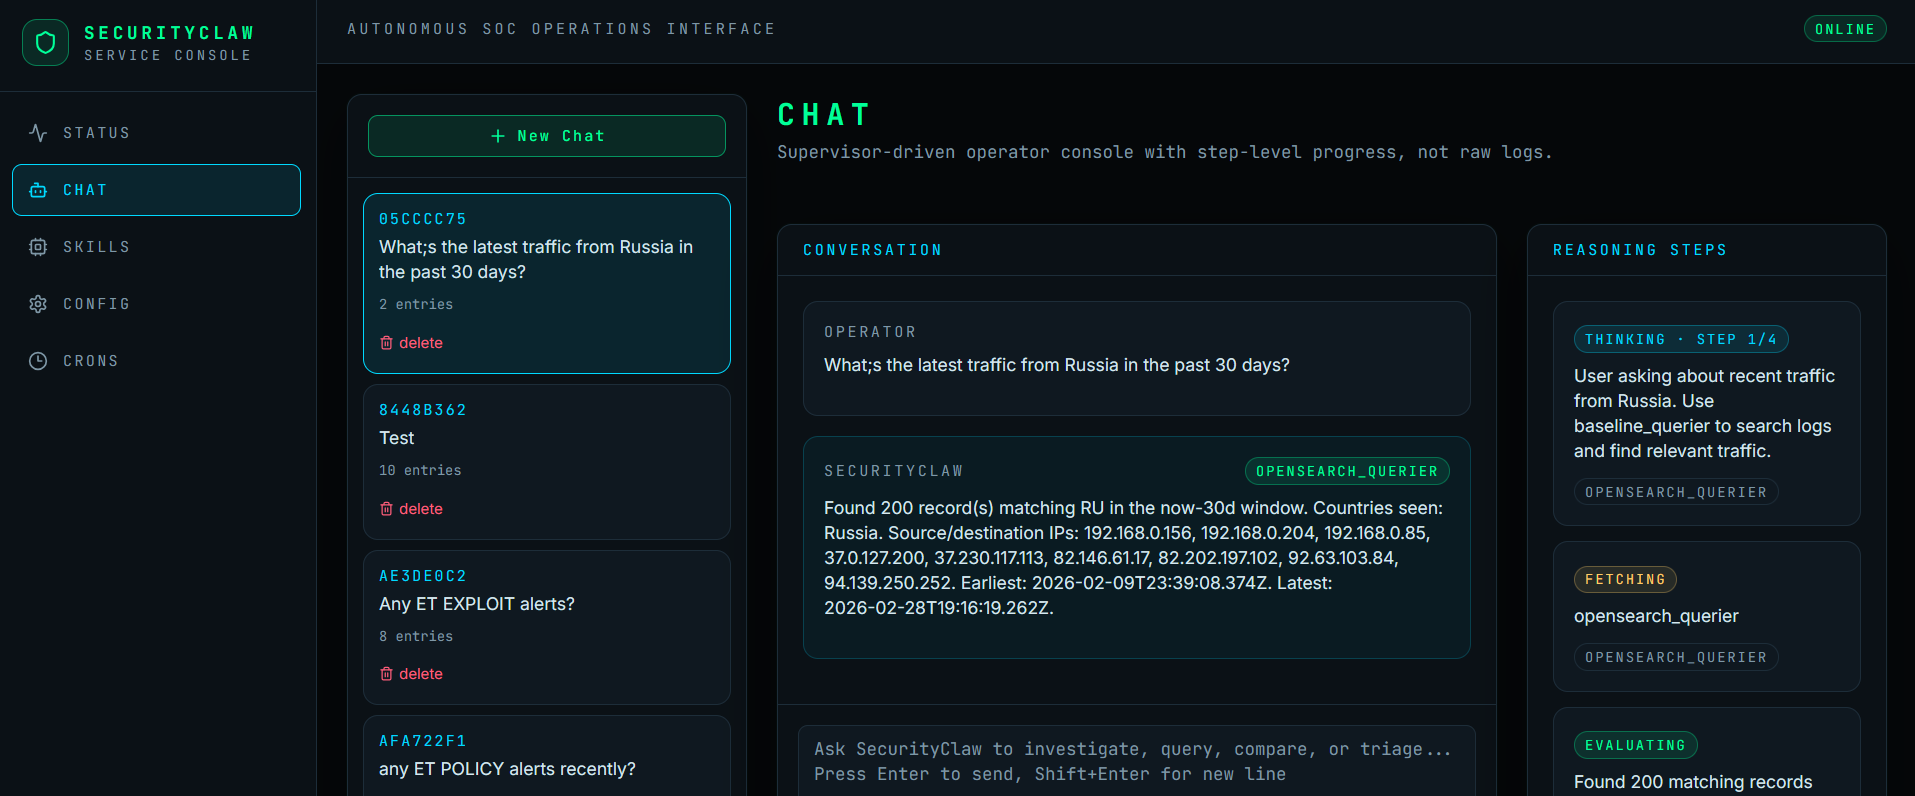
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
ai-securityanomaly-detectionforensics+8
2722 months ago
syswarden preview

syswarden

GitHubduggytuxy/syswarden

Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…

cloud-securityconfiguration-auditingdefensive-tools+4
3356 days ago
psad preview

psad

GitHubmrash/psad

psad: Intrusion Detection and Log Analysis with iptables

forensicsids-ips-evasionintrusion-detection+4
4287 years ago
CVE-2020-16898 preview

CVE-2020-16898

GitHubadvanced-threat-research/cve-2020-16898

CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule

exploitationintrusion-detectionnetwork-security+1
2095 years ago
Previous1…345…33Next