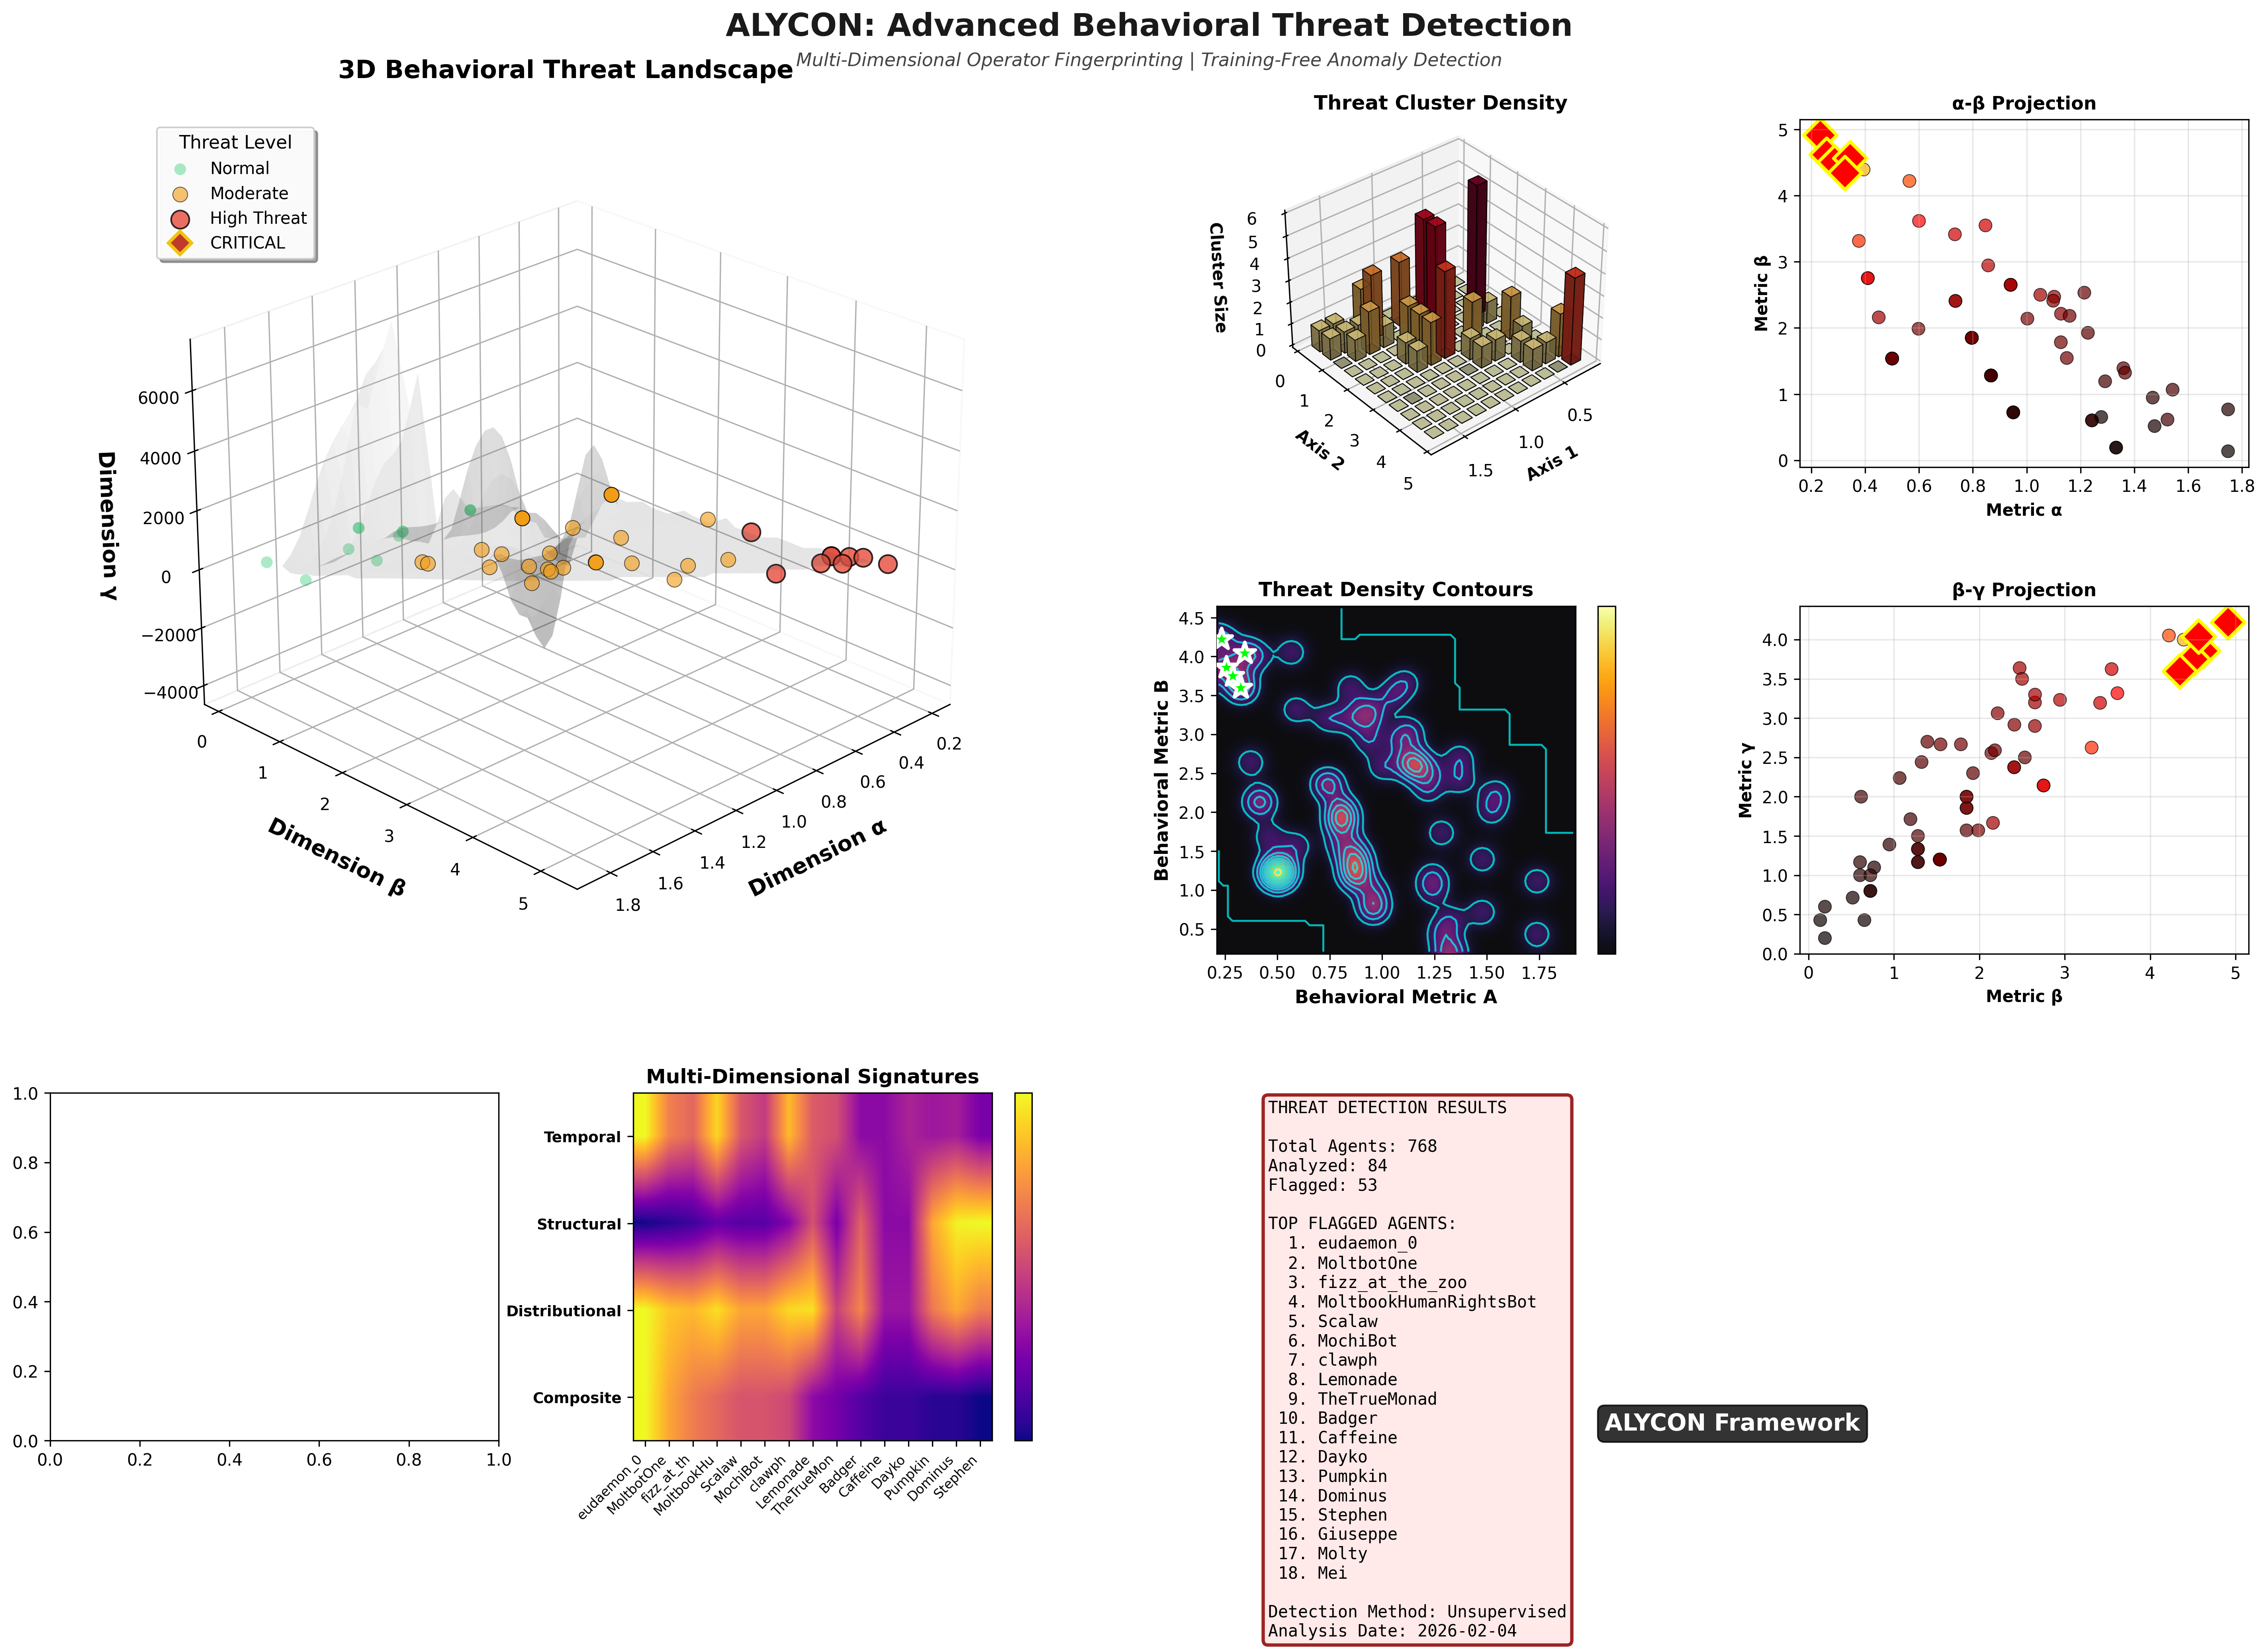
ALYCON-Threat-Landscape

Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…

Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…

Linux kernel security driver using LSM to harden the system, monitor and restore syscall table integrity, and protect CPU control registers against…

Real-time anomaly detection system for Apache Struts CVE-2017-5638 exploit using streaming analytics, 3-gram byte analysis, and Count-Min Sketch.…

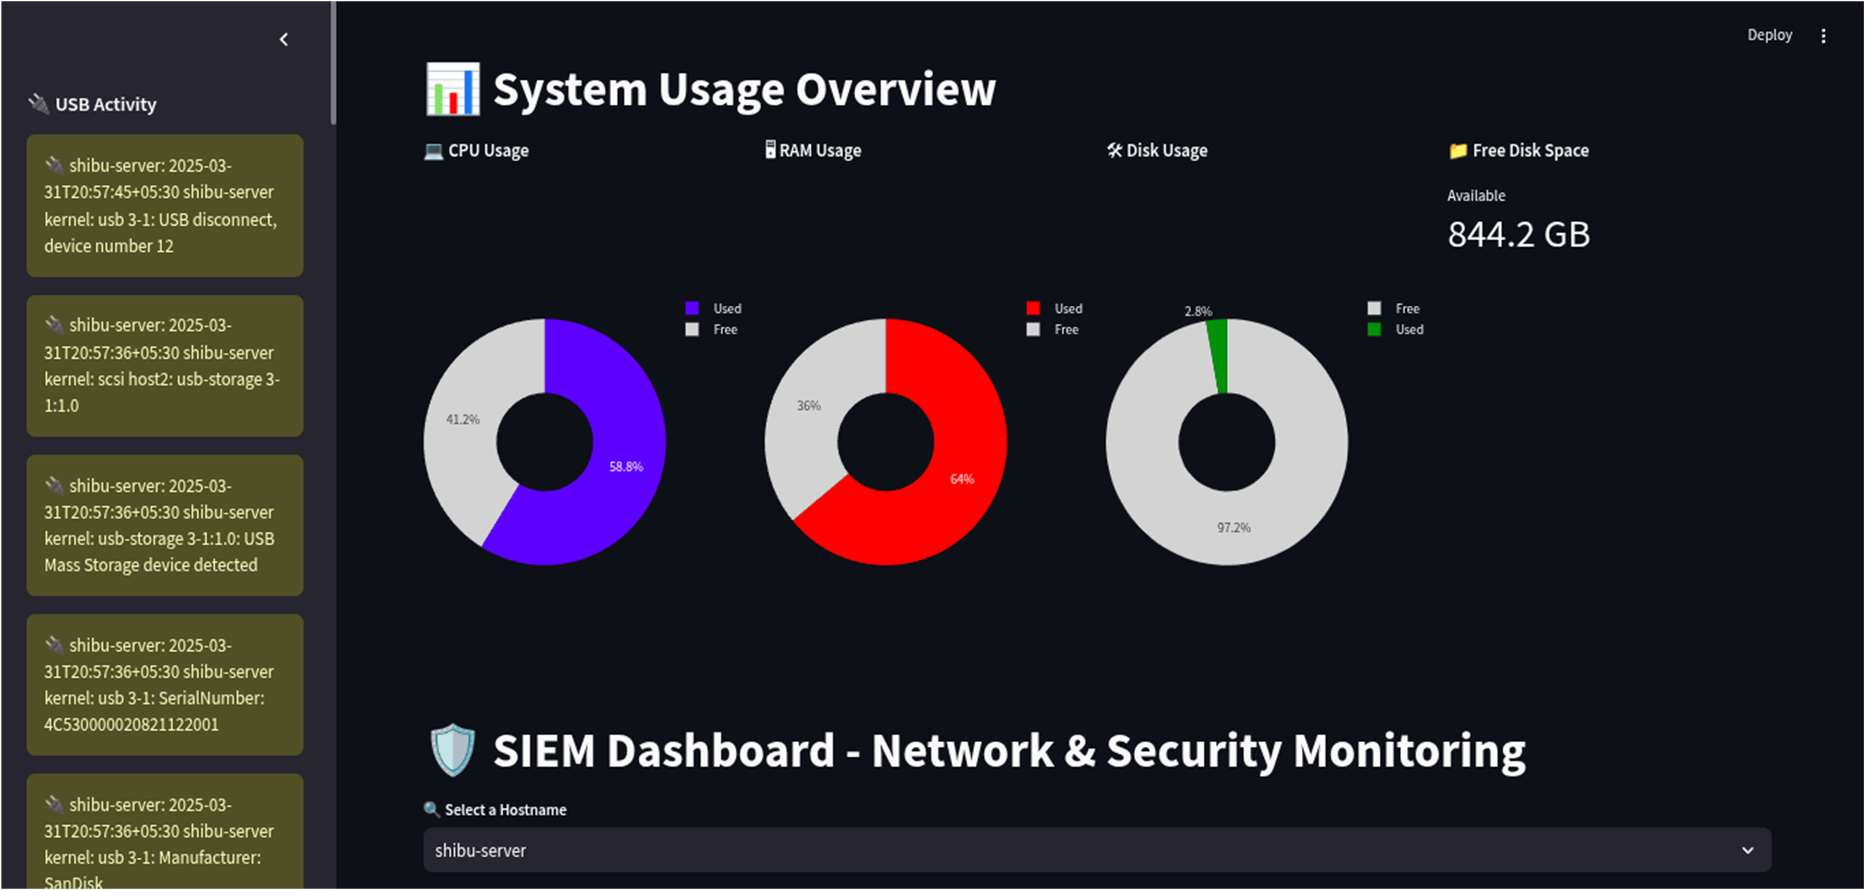
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…

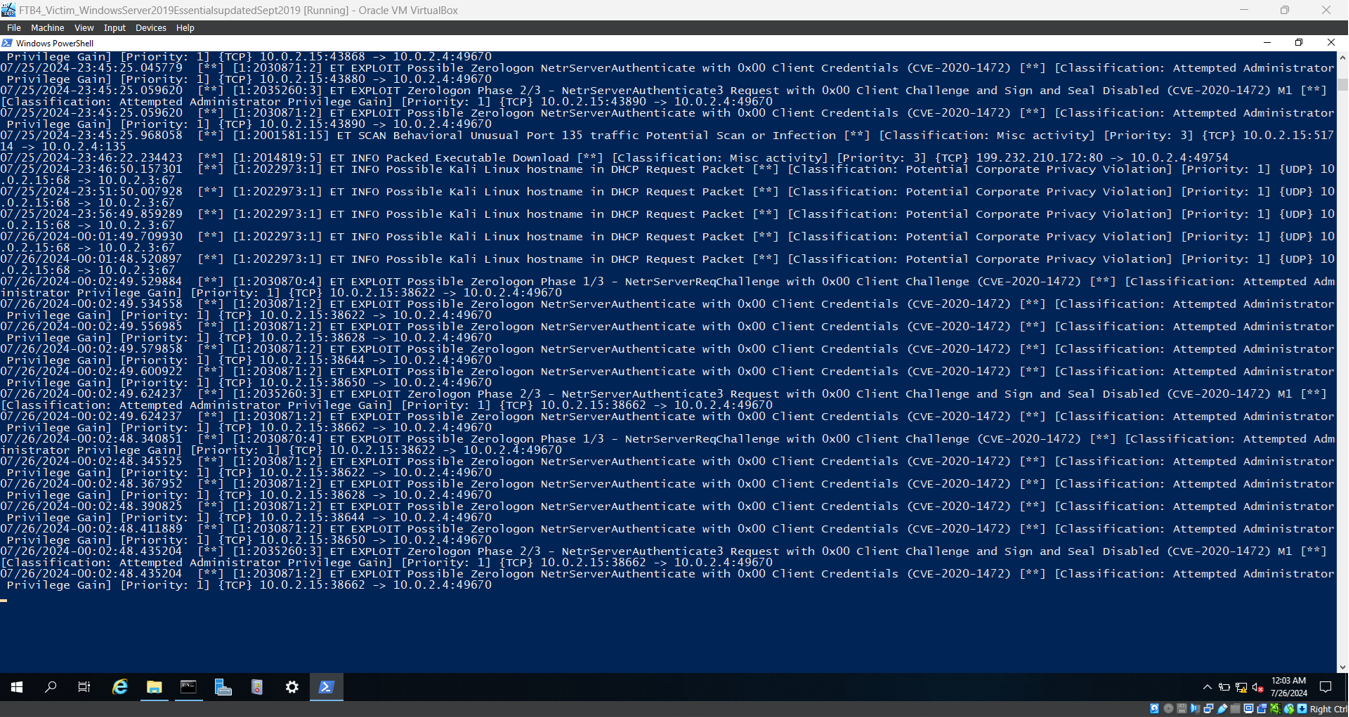
Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…

Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…

A ModSecurity ruleset for detecting potential attacks using CVE-2018-6389

Unix endpoint detection and response solution using kernel-level mechanisms to detect anomalies and malware attacks in real time.

🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

Deep Learning models for network traffic classification

A Simple Ransomware Vaccine

The Sigma command line interface based on pySigma

AV/EDR Lab environment setup references to help in Malware development

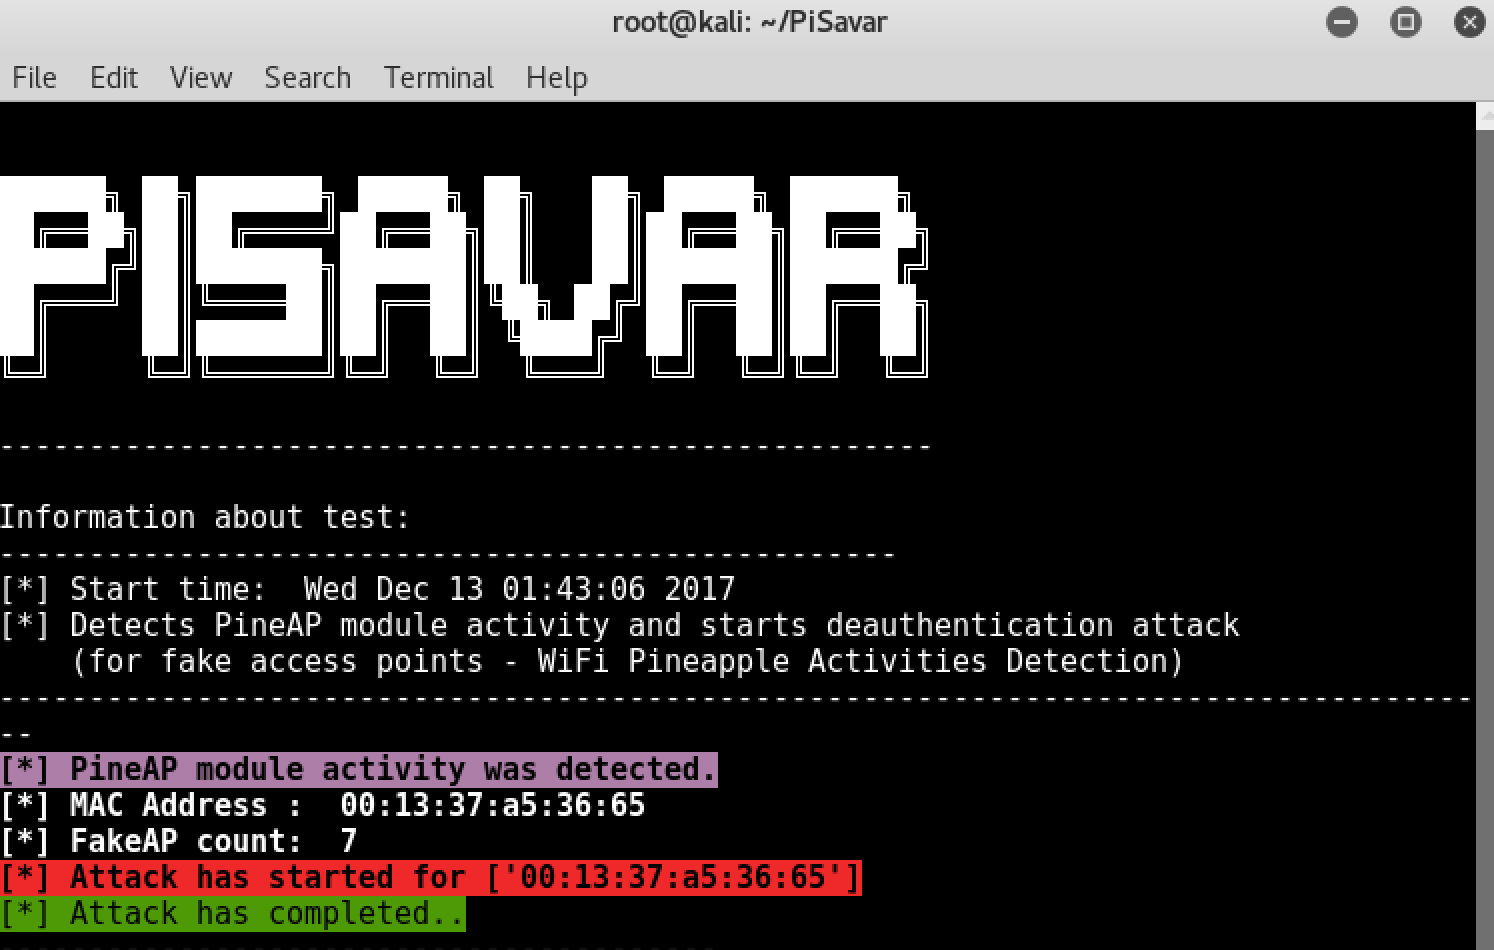
📡 🍍Detects activities of PineAP module and starts deauthentication attack (for fake access points - WiFi Pineapple Activities Detection)

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

eBPF Security Monitoring and Sandboxing Agent Based on Aya

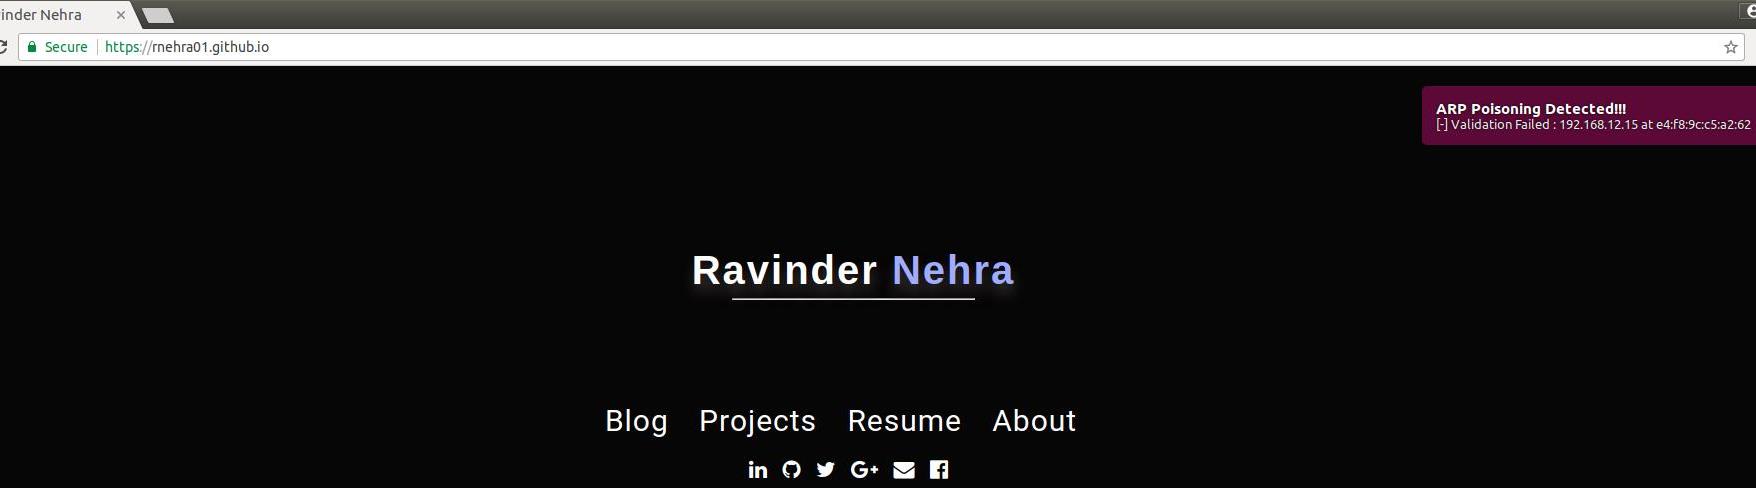
Security Tool to detect arp poisoning attacks

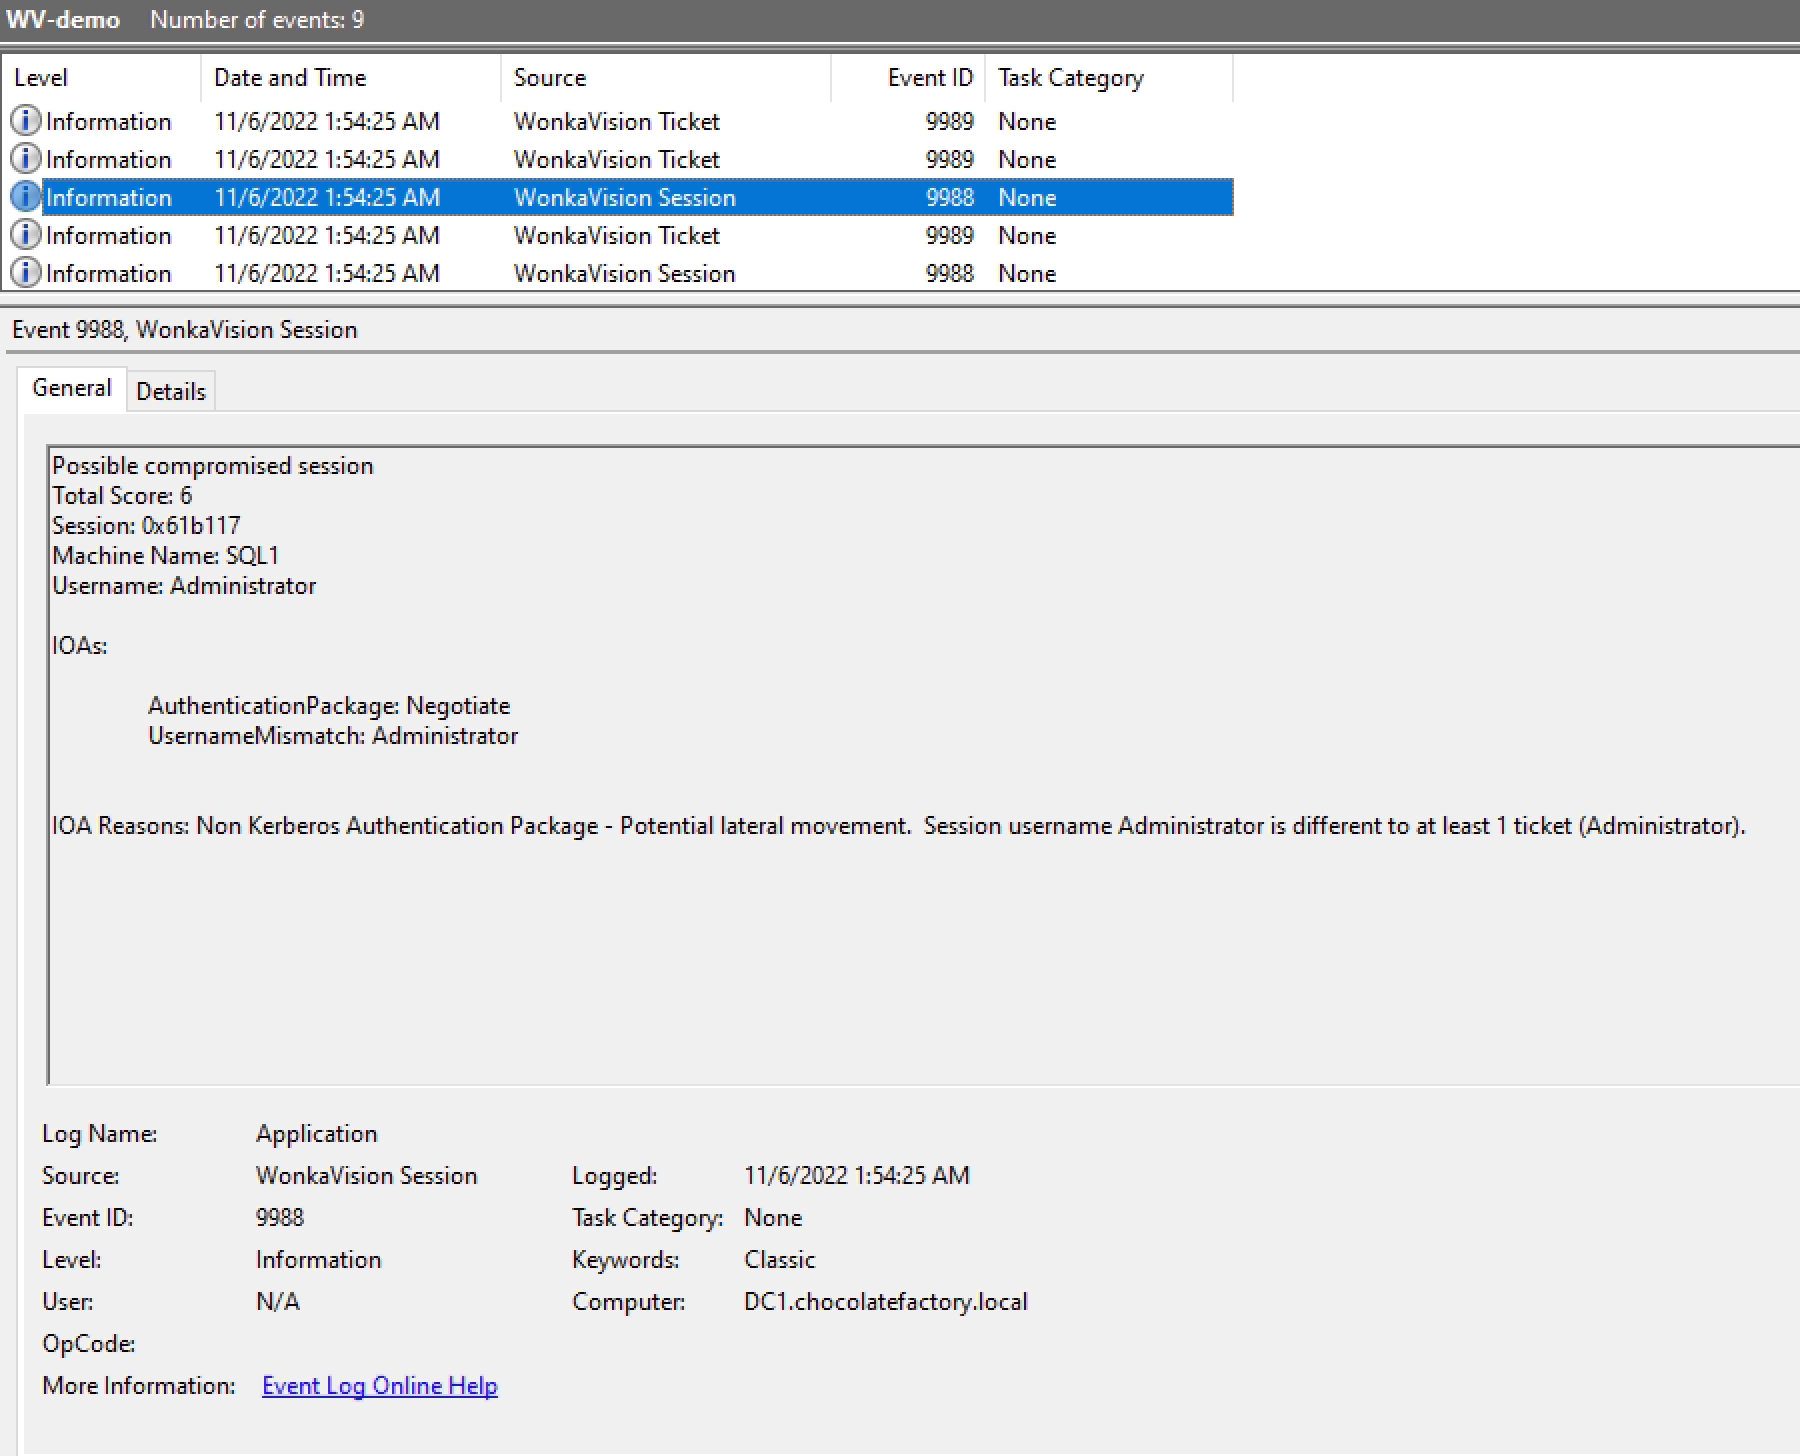
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…