
IPBan
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
defensive-toolsintrusion-detectionlog-analysis+1
2.2k
digitalruby/ipbanAutomated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 joesecurity/sigma-rules
Sigma rules from Joe Security
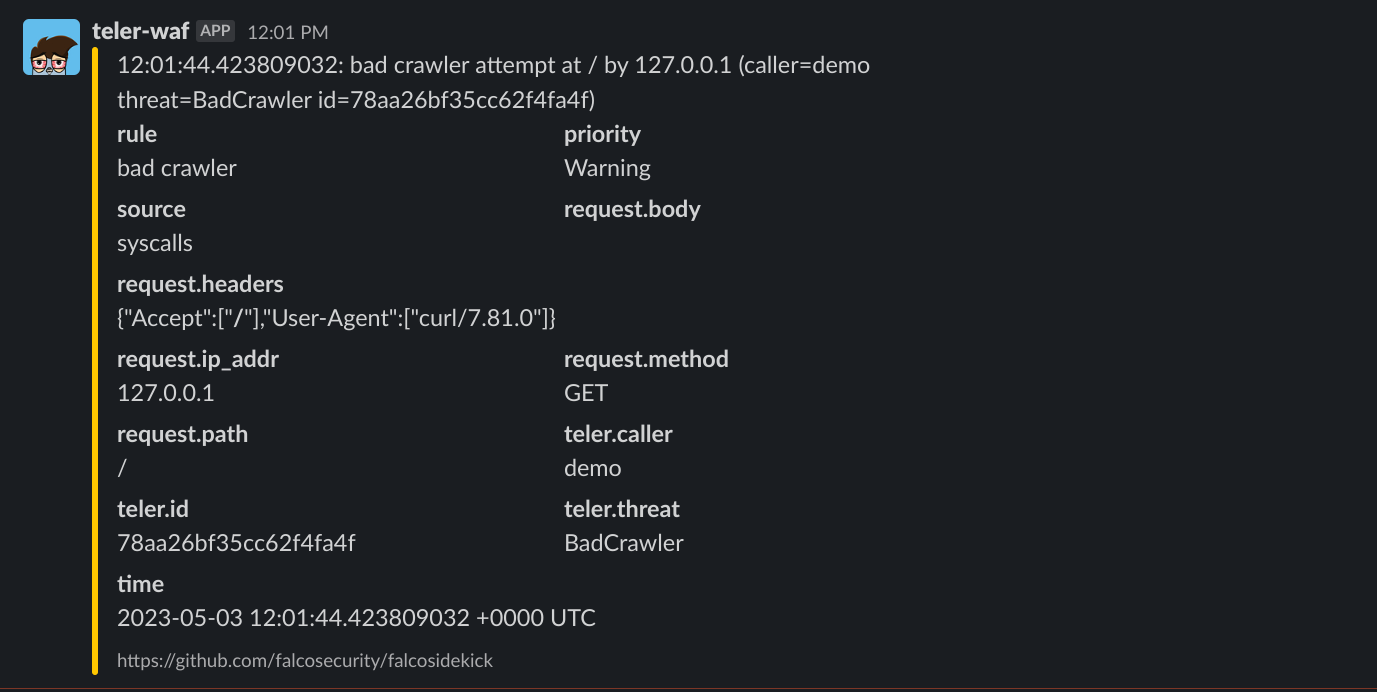 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
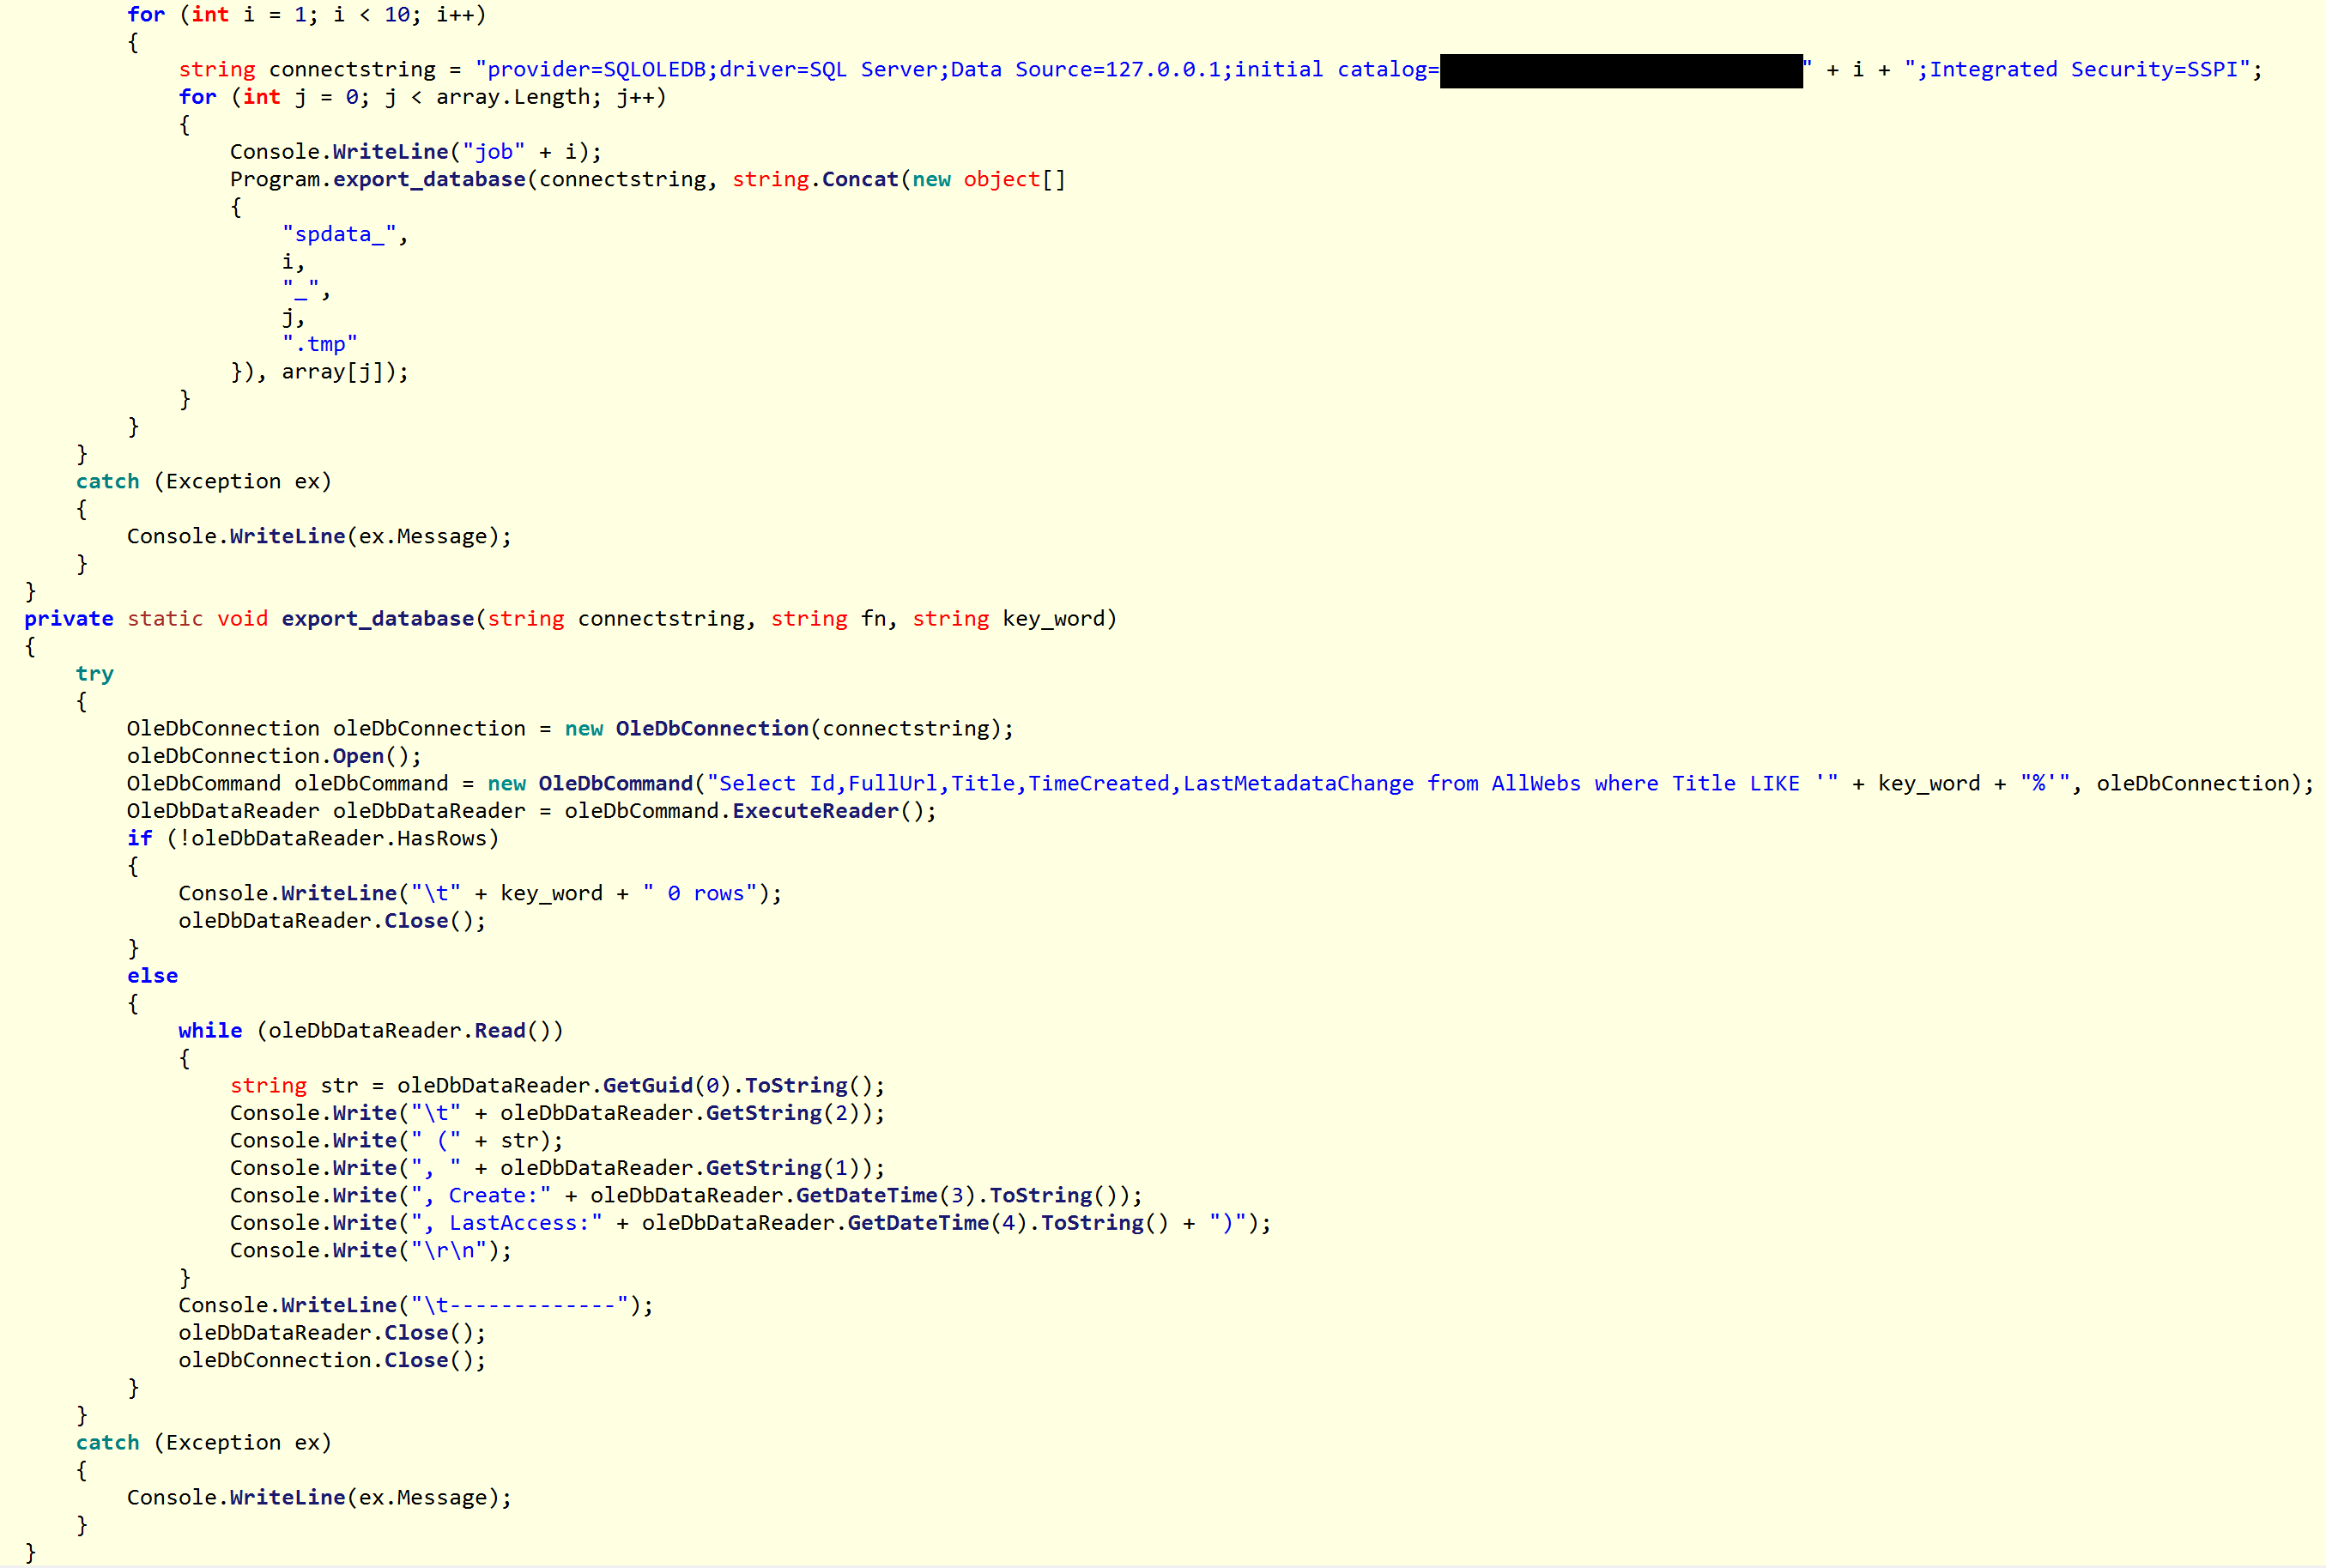 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 nccgroup/mimikatz-detector-condrv
The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…
 yardenshafir/conference_talks
Slides from various conference talks
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
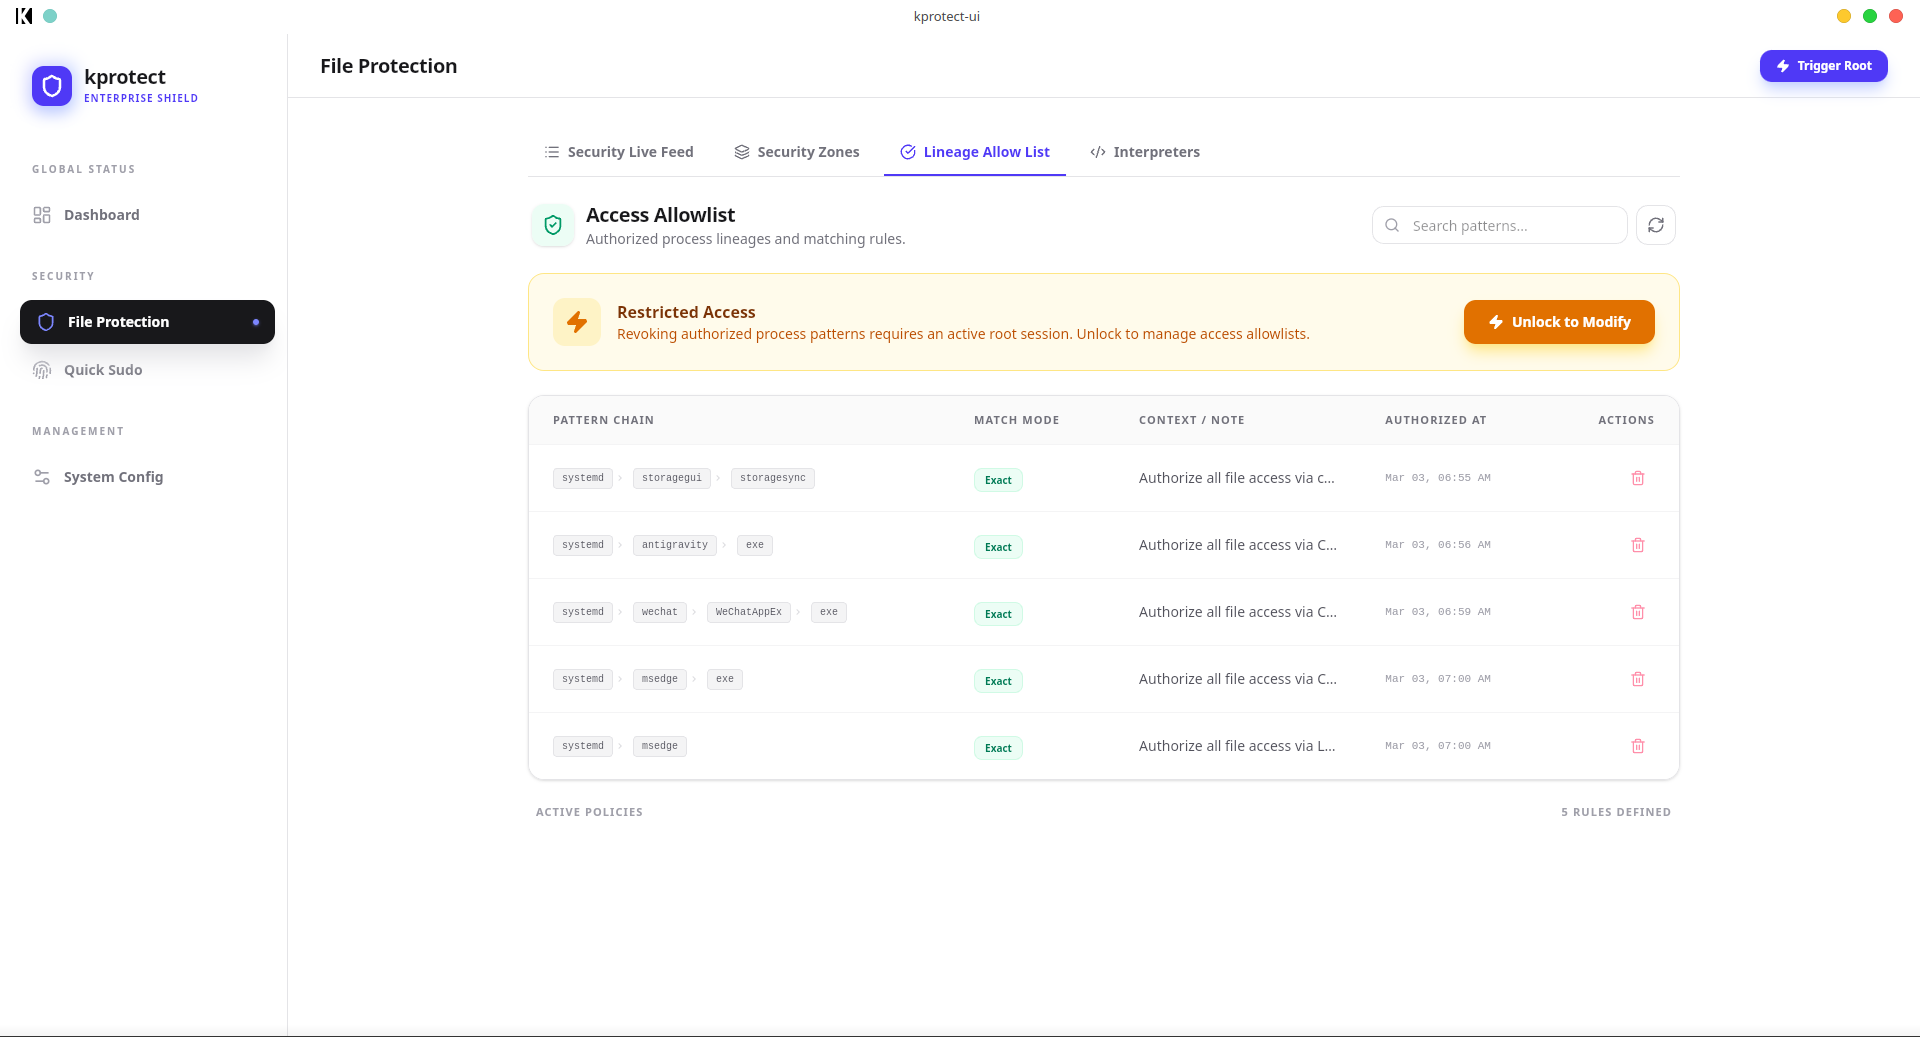 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 nccgroup/yaml2yara
Generate bulk YARA rules from YAML input
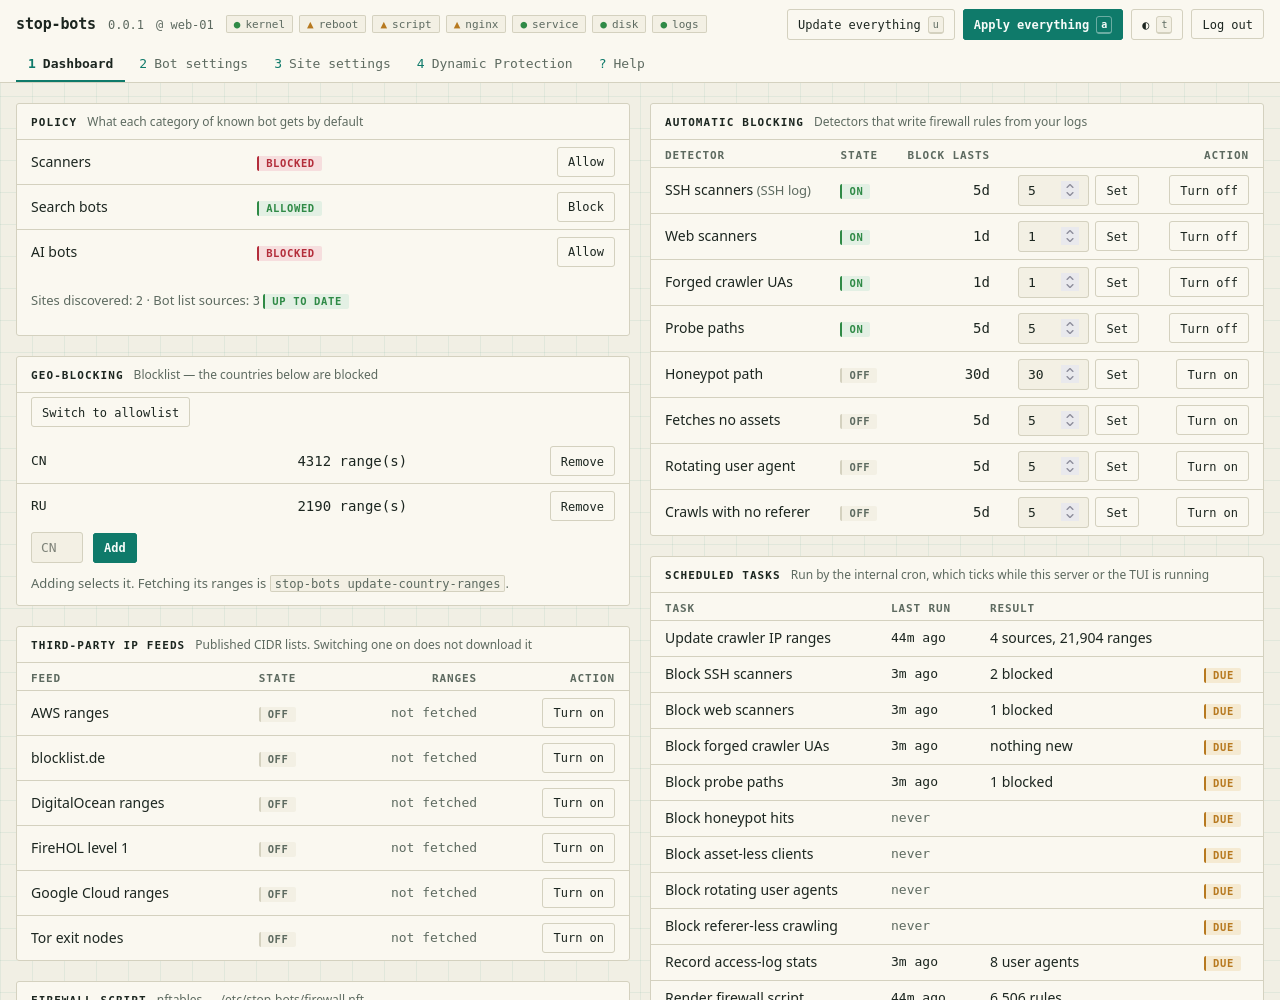 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
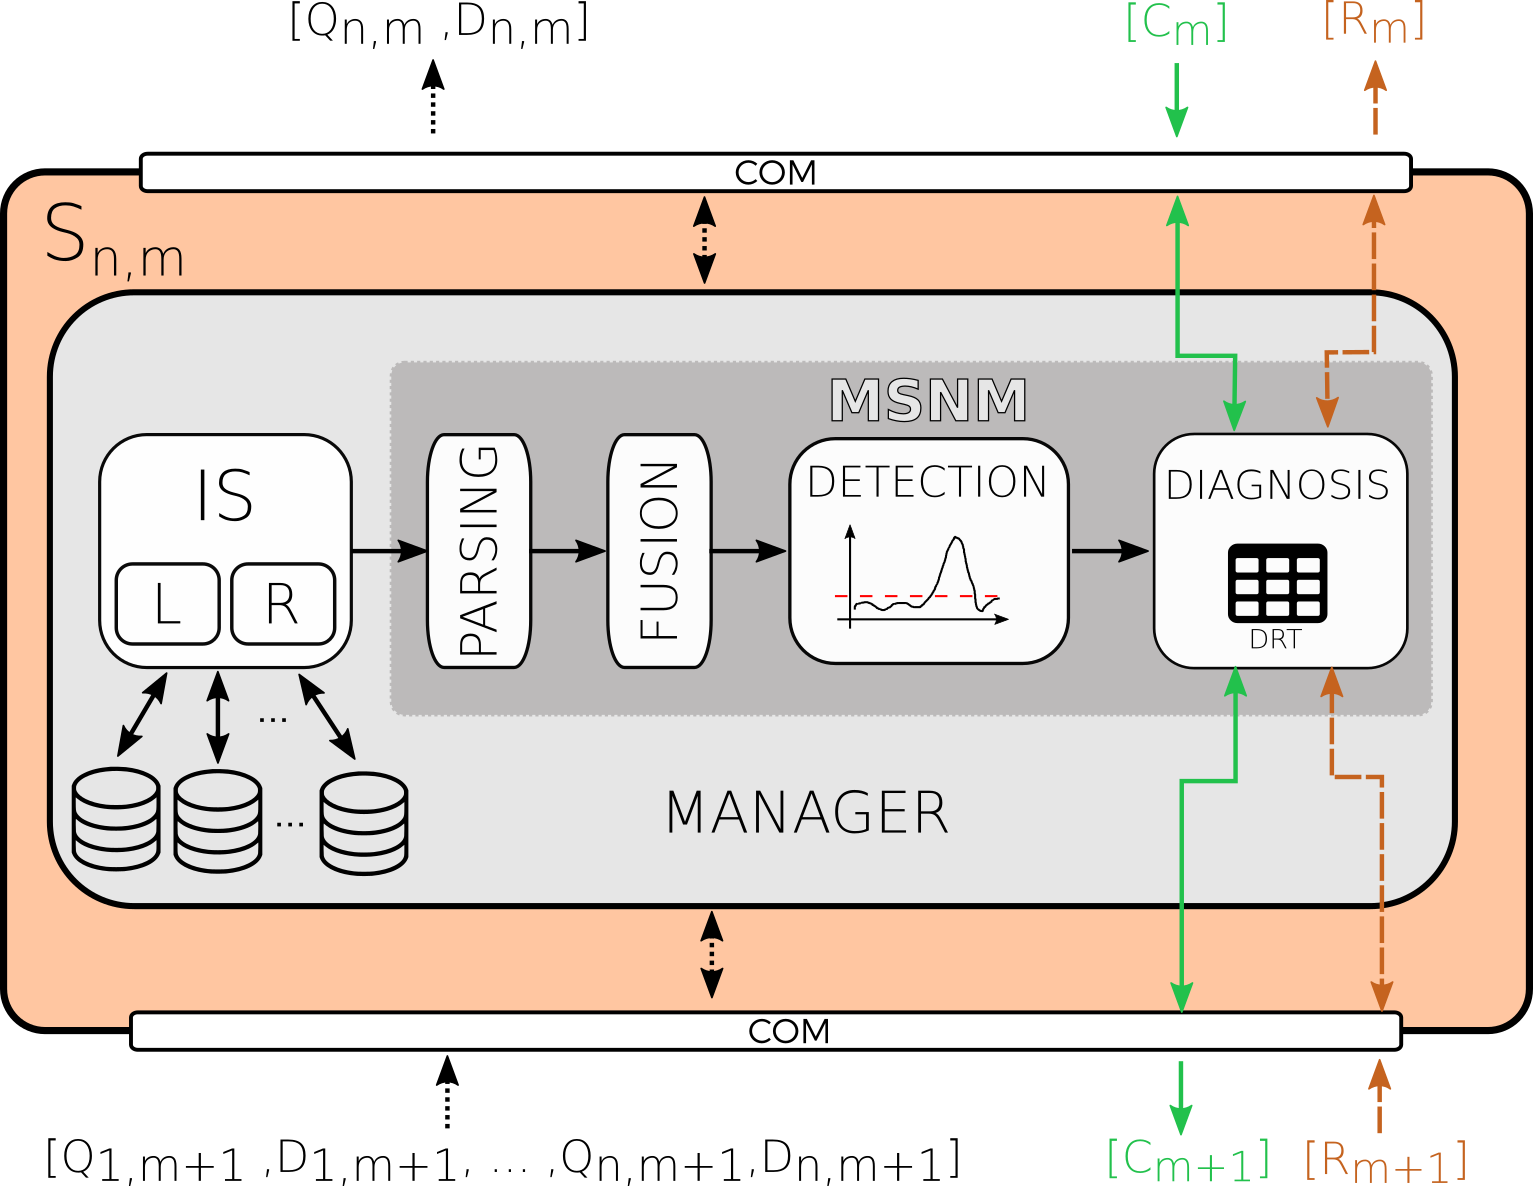 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…