
DetectionLabELK
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
configuration-auditingdefensive-toolsdigital-forensics+7
578
cyberdefenders/detectionlabelkDetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
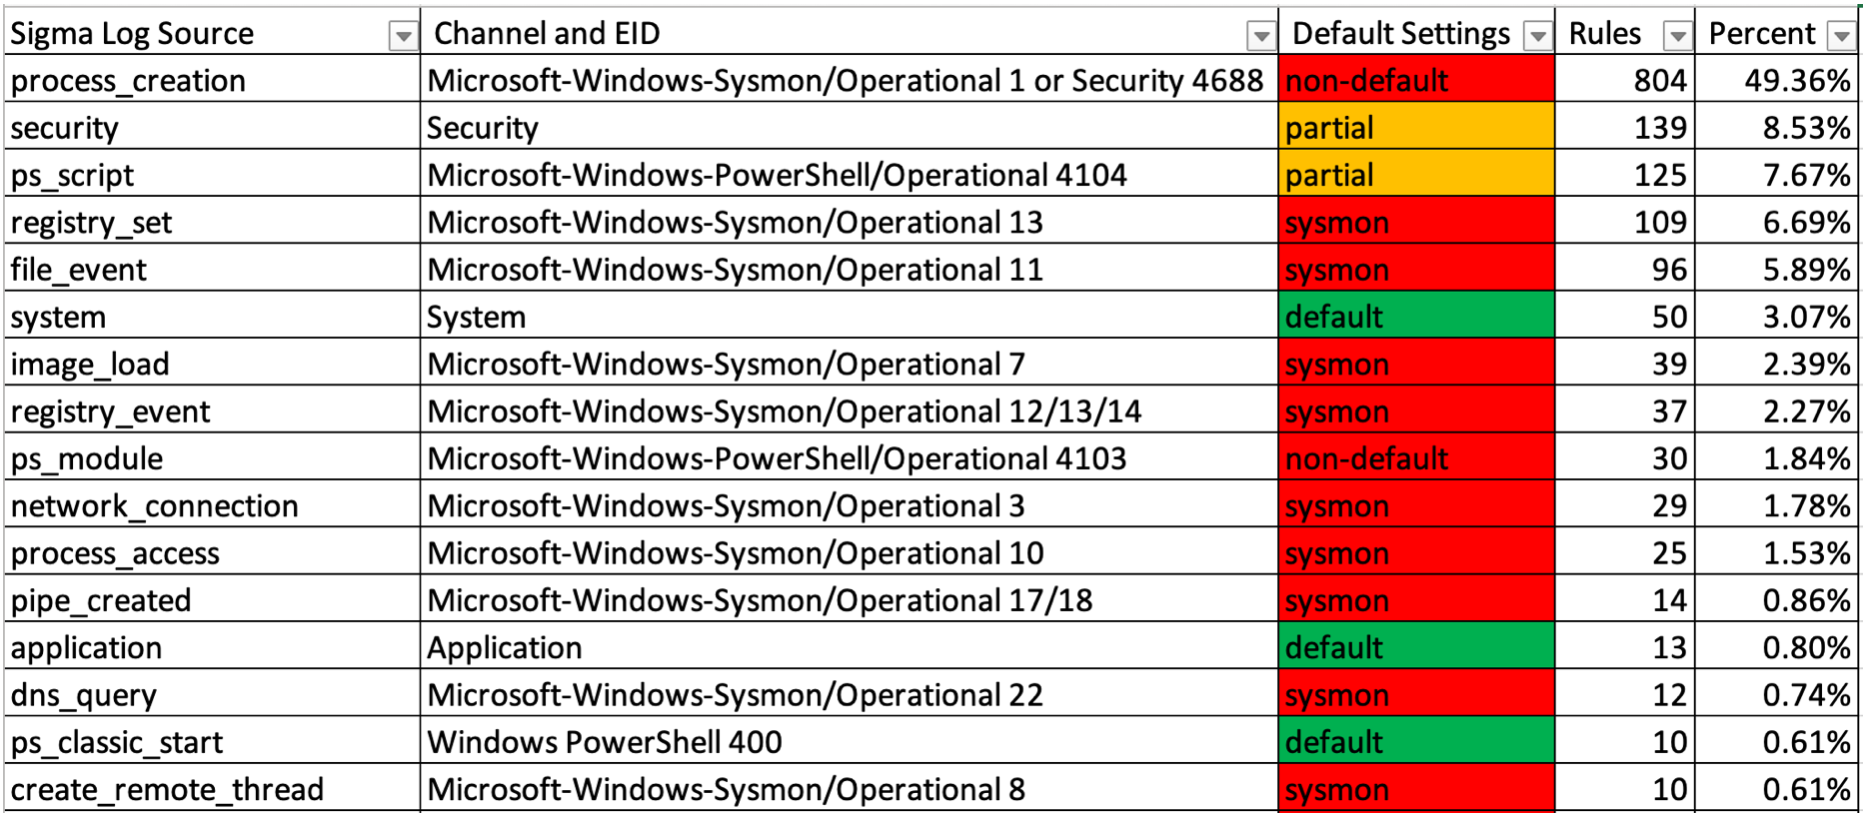 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 chainguard-dev/osquery-defense-kit
Production-ready detection & response queries for osquery
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
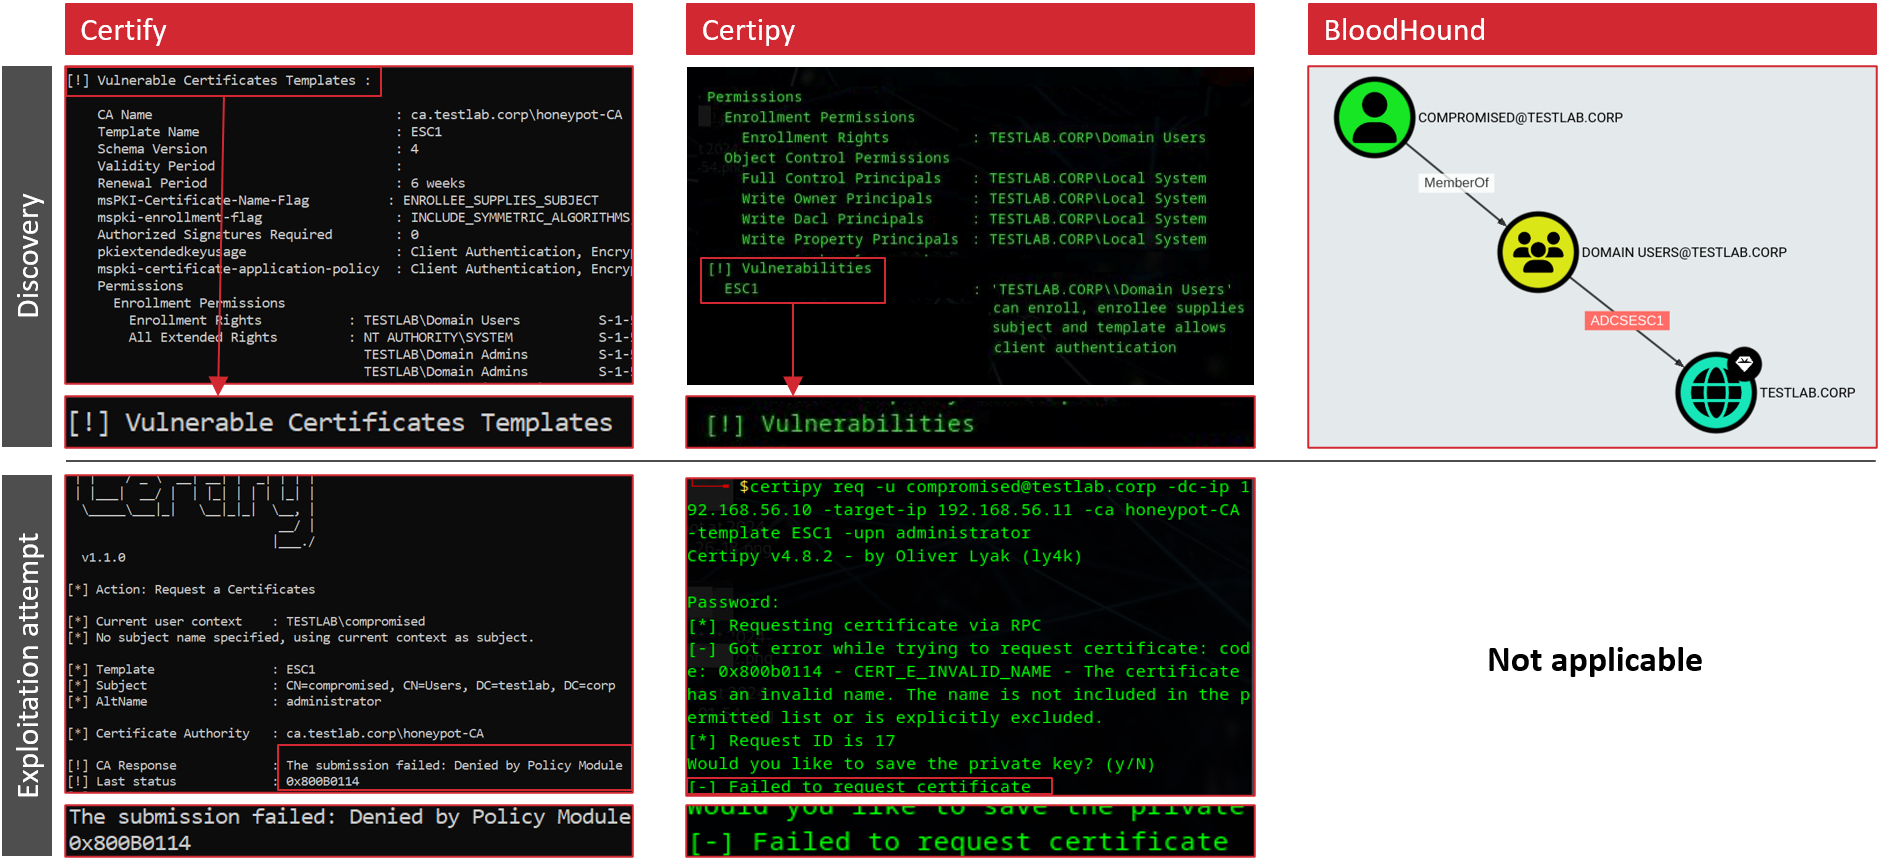 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 stintel/vallumd
Centralize or distribute IPset blacklists
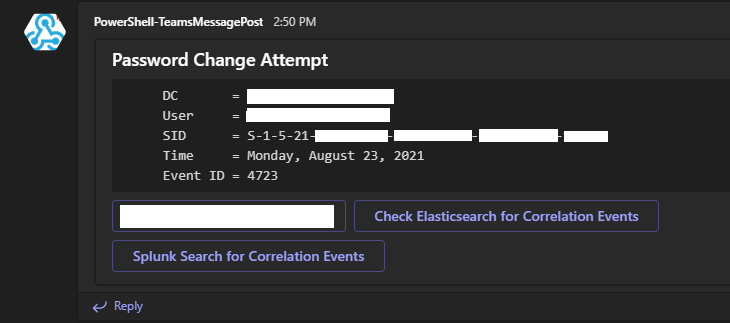 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 connectedlucy/plague
Default Detections for EDR
 fksvs/siper
XDP Based Lightweight and Fast Firewall
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 corelight/corelight-ansible-roles
Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)