

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
64 results
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
21h 12m ago
suricata_exporter preview

suricata_exporter

GitHubcorelight/suricata_exporter

A Prometheus Exporter for Suricata

defensive-toolsintrusion-detectionlog-analysis+1
273 days ago
SSHintel preview

SSHintel

GitHubsonitbahl/sshintel

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

incident-responseintrusion-detectionlog-analysis+2
33 days ago
tpotce preview

tpotce

GitHubtelekom-security/tpotce

🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
9.6k3 days ago
ecs-logstash-mappings preview

ecs-logstash-mappings

GitHubcorelight/ecs-logstash-mappings

Mapping Corelight or Zeek data to Elastic Common Schema logs
incident-responseintrusion-detectionlog-analysis+2
126 days ago
owLSM preview

owLSM

GitHubcybereason-public/owlsm

Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
cloud-securitycontainer-securitydefensive-tools+4
2806 days ago
Threat-Hunting preview

Threat-Hunting

GitHuba2awais/threat-hunting

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

educationincident-responseinformation-gathering+4
866 days ago
bombini preview

bombini

GitHubbombinisecurity/bombini

eBPF Security Monitoring and Sandboxing Agent Based on Aya

container-securitydefensive-toolsintrusion-detection
768 days ago
AIP preview

AIP

GitHubstratosphereips/aip

Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…

information-gatheringintrusion-detectioniot-security+3
328 days ago
ddos-reduction-system preview

ddos-reduction-system

GitHubdevinblack001/ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

anomaly-detectiondefensive-toolsincident-response+6
29 days ago
pvbrf-id preview

pvbrf-id

GitHubnawaralseelawi/pvbrf-id

Simulation code and results for a private, verifiable, Byzantine-robust federated intrusion detection protocol using secret sharing, Merkle audits…
anomaly-detectioncryptographydefensive-tools+5
12 days ago
sigma-cli preview

sigma-cli

GitHubsigmahq/sigma-cli

The Sigma command line interface based on pySigma

defensive-toolsintrusion-detectionlog-analysis+2
21916 days ago
dns_watchdog_windows2 preview

dns_watchdog_windows2

GitHubmicrolaser/dns_watchdog_windows2

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
anomaly-detectiondefensive-toolsdns-analysis+5
1 month ago
go-zeek-broker-ws preview

go-zeek-broker-ws

GitHubcorelight/go-zeek-broker-ws

A Go library for using zeek broker's websocket API
authentication-authorizationintrusion-detectionnetwork-security+1
51 month ago
KOOBE-Guard preview

KOOBE-Guard

GitHubvedantk6403/koobe-guard

Linux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
anomaly-detectiondefensive-toolsintrusion-detection+1
2 months ago
PhantomFS preview

PhantomFS

GitHuballoysecuregroup/phantomfs

Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
defensive-toolsincident-responseintrusion-detection
712 months ago
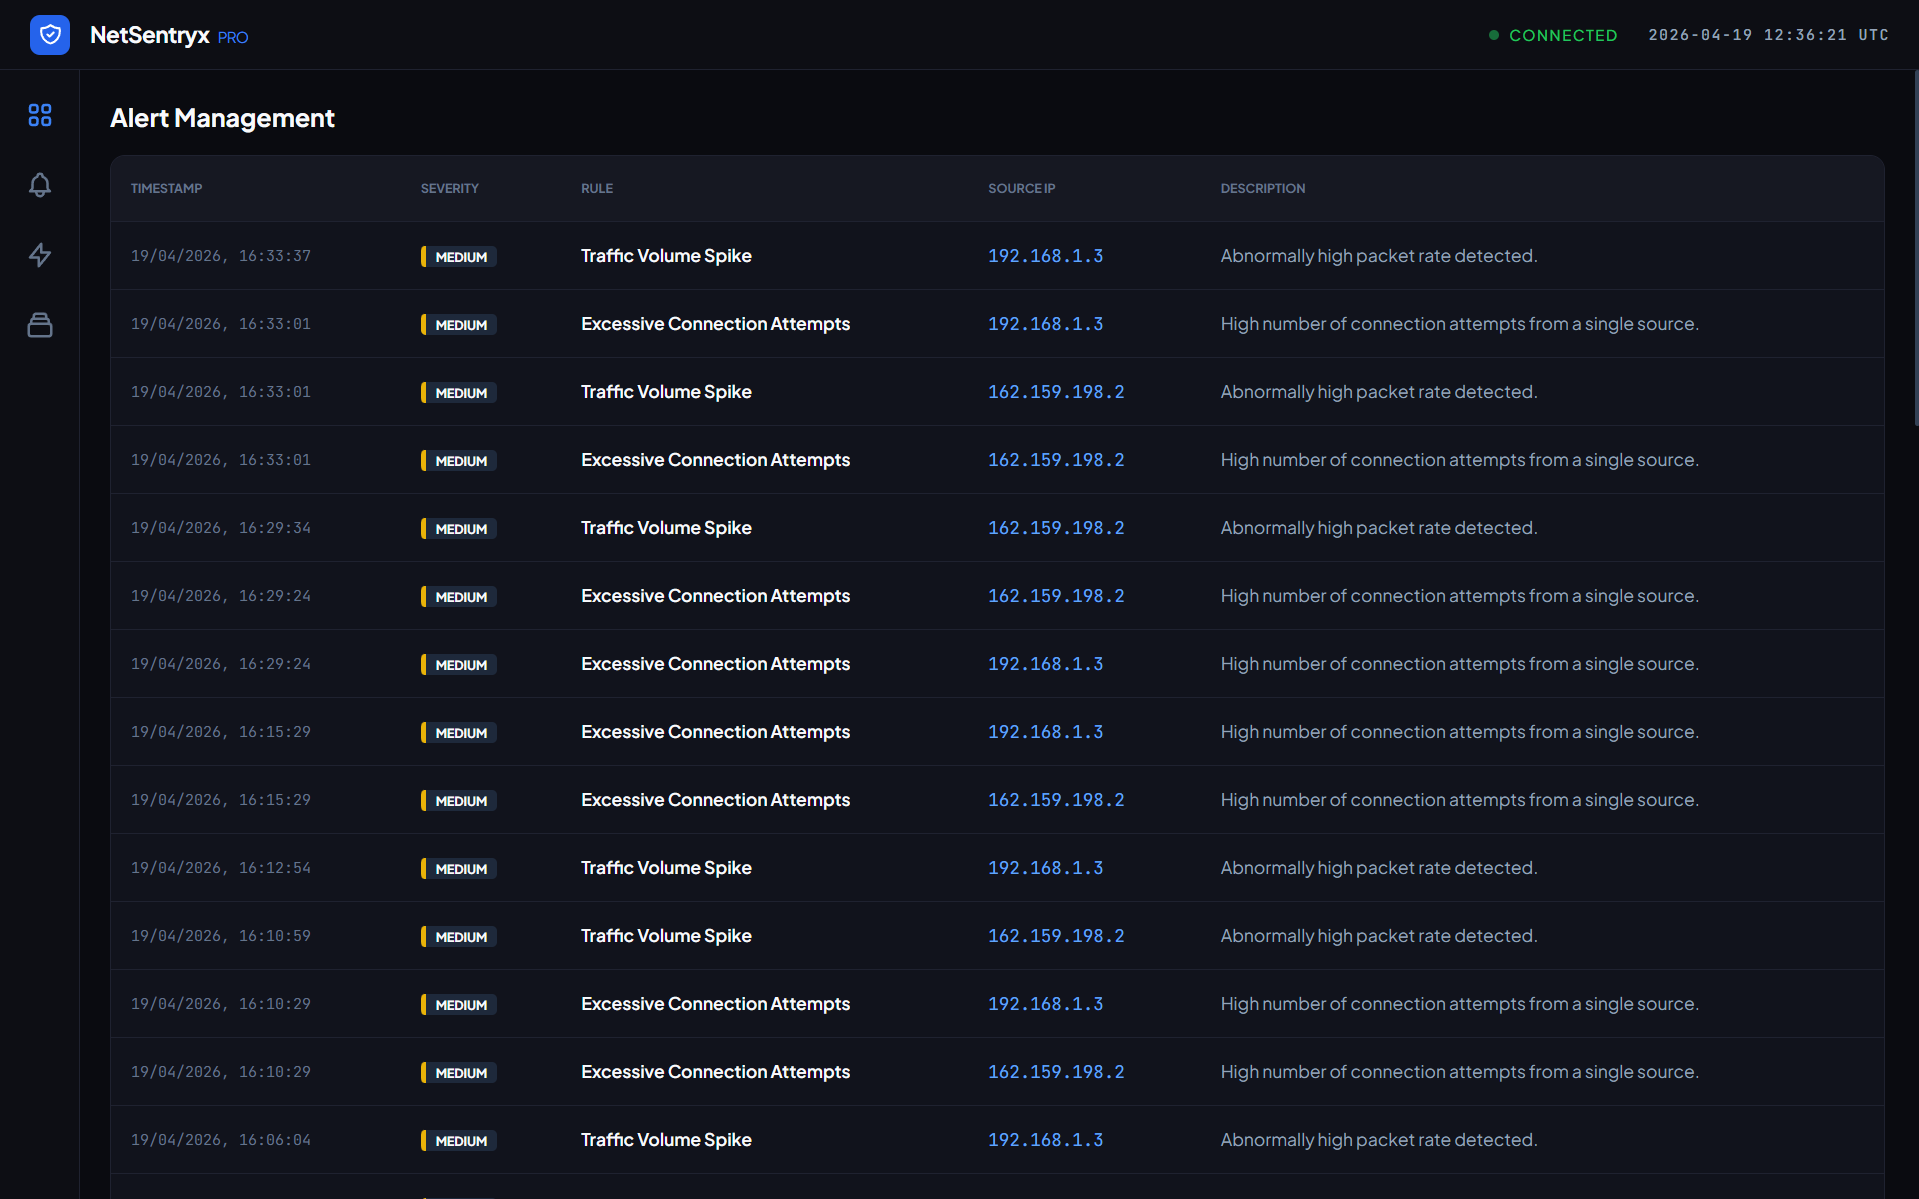
netsentryx preview

netsentryx

GitHubaman-sharma-dev/netsentryx

An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
anomaly-detectioncloud-securitydefensive-tools+6
2 months ago
printnightmare-detection-lab preview

printnightmare-detection-lab

GitHubjoertx07/printnightmare-detection-lab

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

adversarial-attackeducationexploitation+6
2 months ago
Previous1234Next